

zaproxy
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
android-securityapi-securityapi-security-testing+15
16.0k
zaproxy/zaproxyOpen-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 commando-x/vuln-bank
Intentionally vulnerable banking platform for practicing web application, API, and AI/LLM security testing, secure code review, and DevSecOps…
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
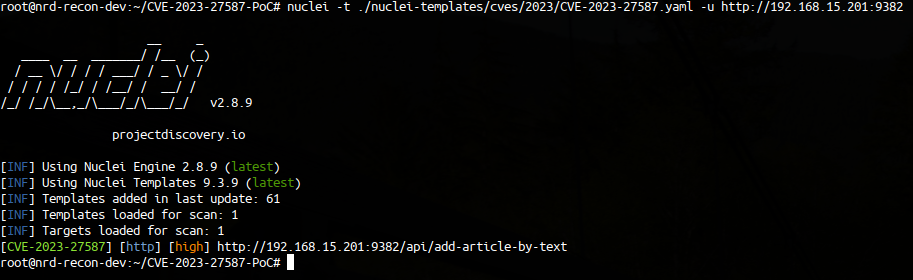 vagnerd/cve-2023-27587-poc
The simple PoC of CVE-2023-27587
 rbidou/pyrasp
Runtime Application Self Protection for Python web servers, serverless functions and MCP servers, detecting attacks, prompt injection and data leaks…
 owasp/asvs
Application Security Verification Standard
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 vicanso/pingap
A reverse proxy like nginx, built on pingora, simple and efficient.
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
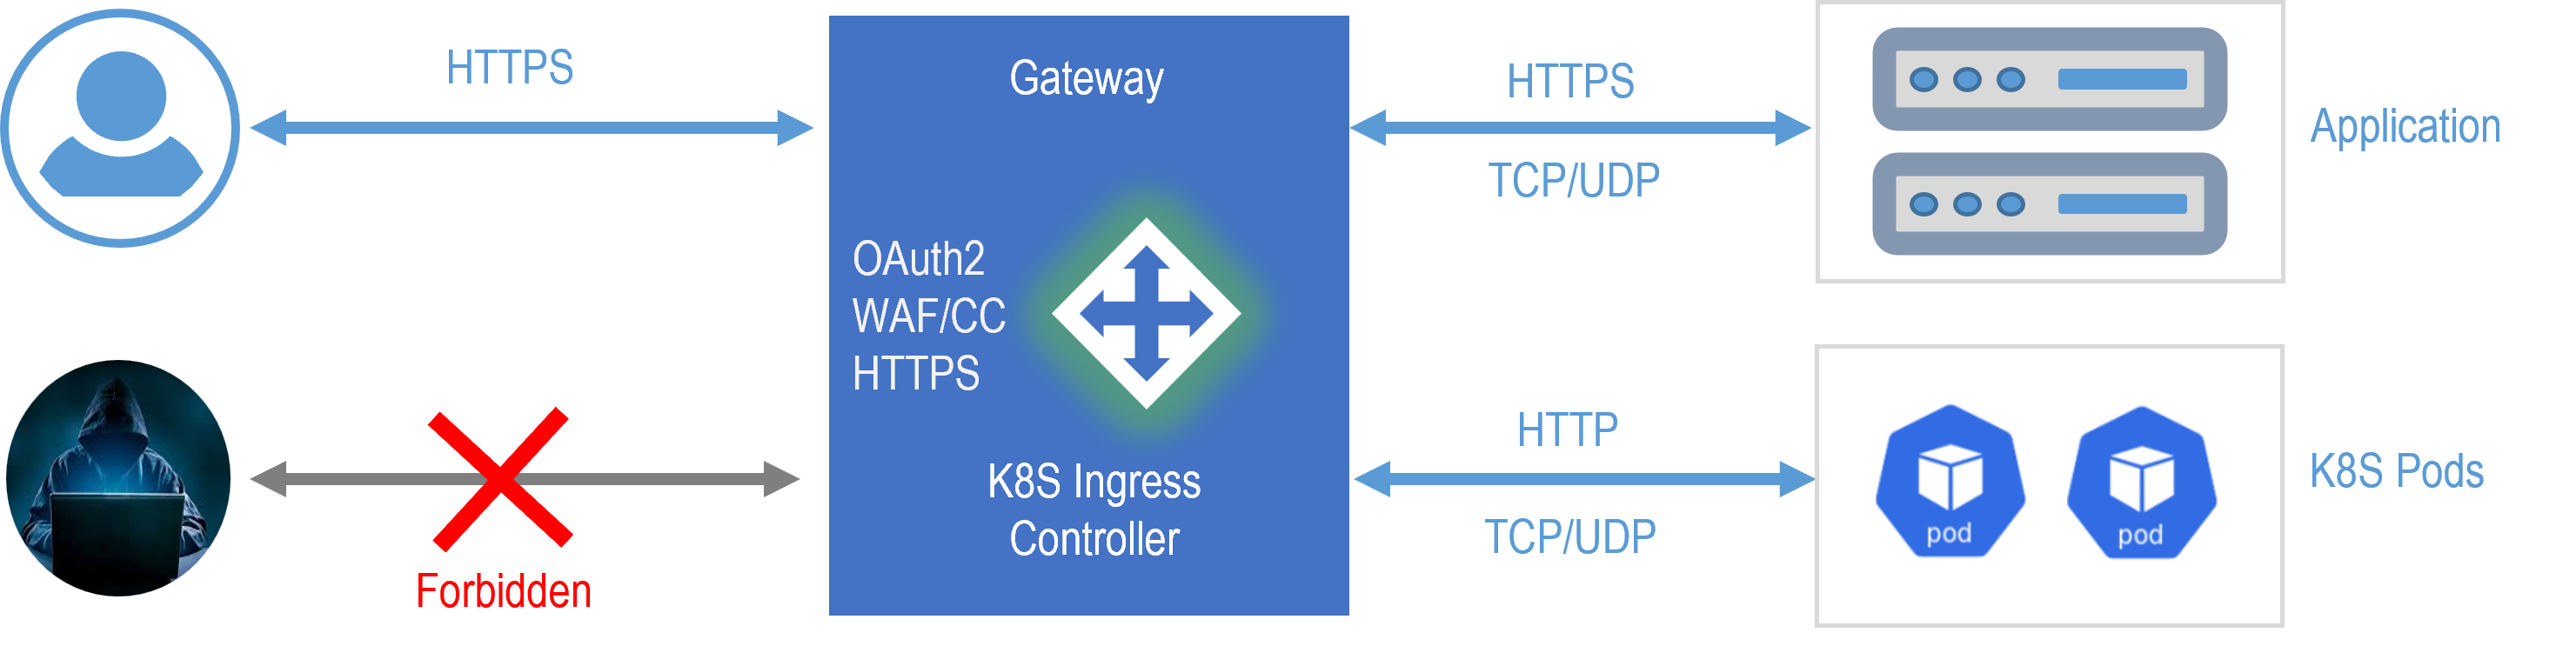 janusec/janusec
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
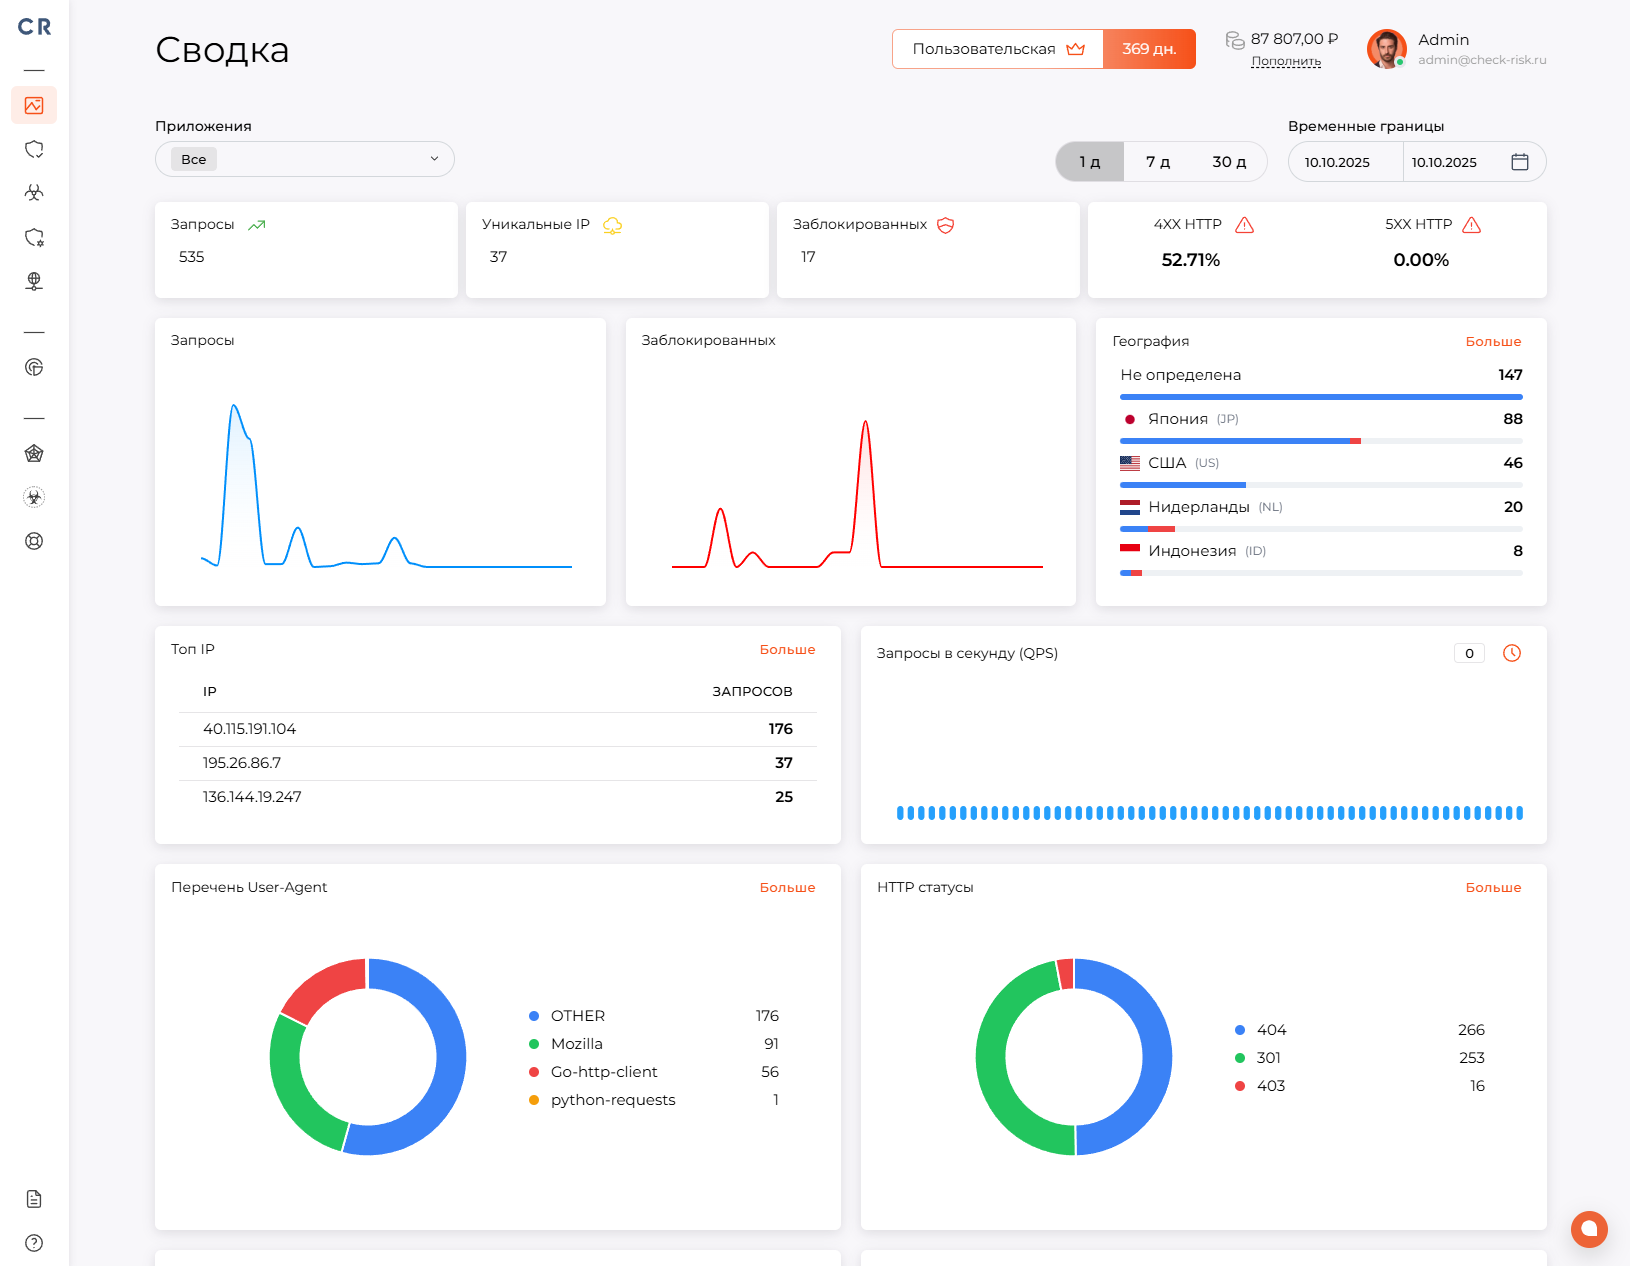
 check-risk-waf/check-risk-waf
Cloud-based Web Application Firewall (WAF) providing L3/L7 protection against SQLi, XSS, DDoS, and bot attacks. Features AI assistant, anti-bot…
 owasp/threat-dragon
An open source threat modeling tool from OWASP
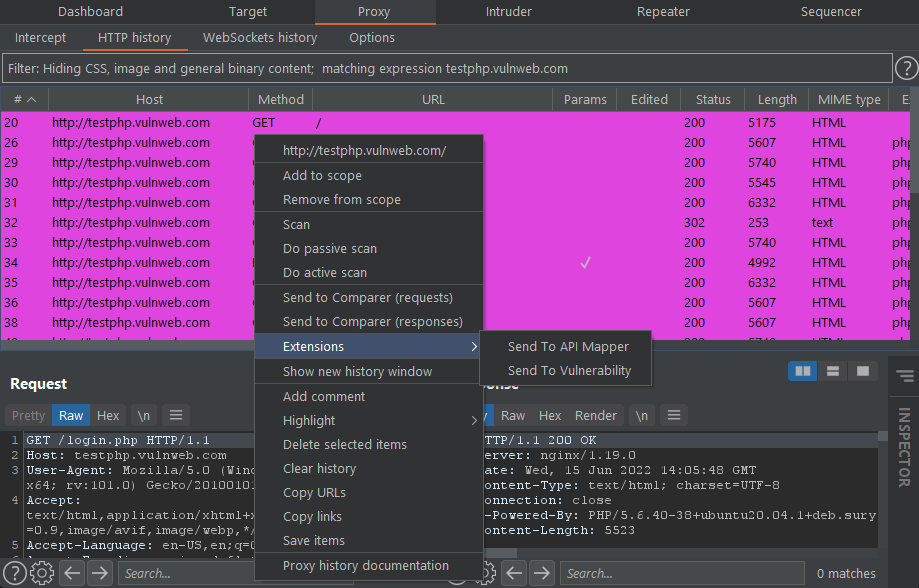 portswigger/pentest-mapper
A Burp Suite Extension for Application Penetration Testing to map flows and vulnerabilities
 uziii2208/cve-2026-86259
OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass