
CVE-2026-31283
 saykino/cve-2026-31283
Documentation of CVE-2026-31283: an email bombing vulnerability in Totara LMS's forgot password API due to missing rate limiting, allowing…
api-securityeducationemail-security+3
saykino/cve-2026-31283Documentation of CVE-2026-31283: an email bombing vulnerability in Totara LMS's forgot password API due to missing rate limiting, allowing…
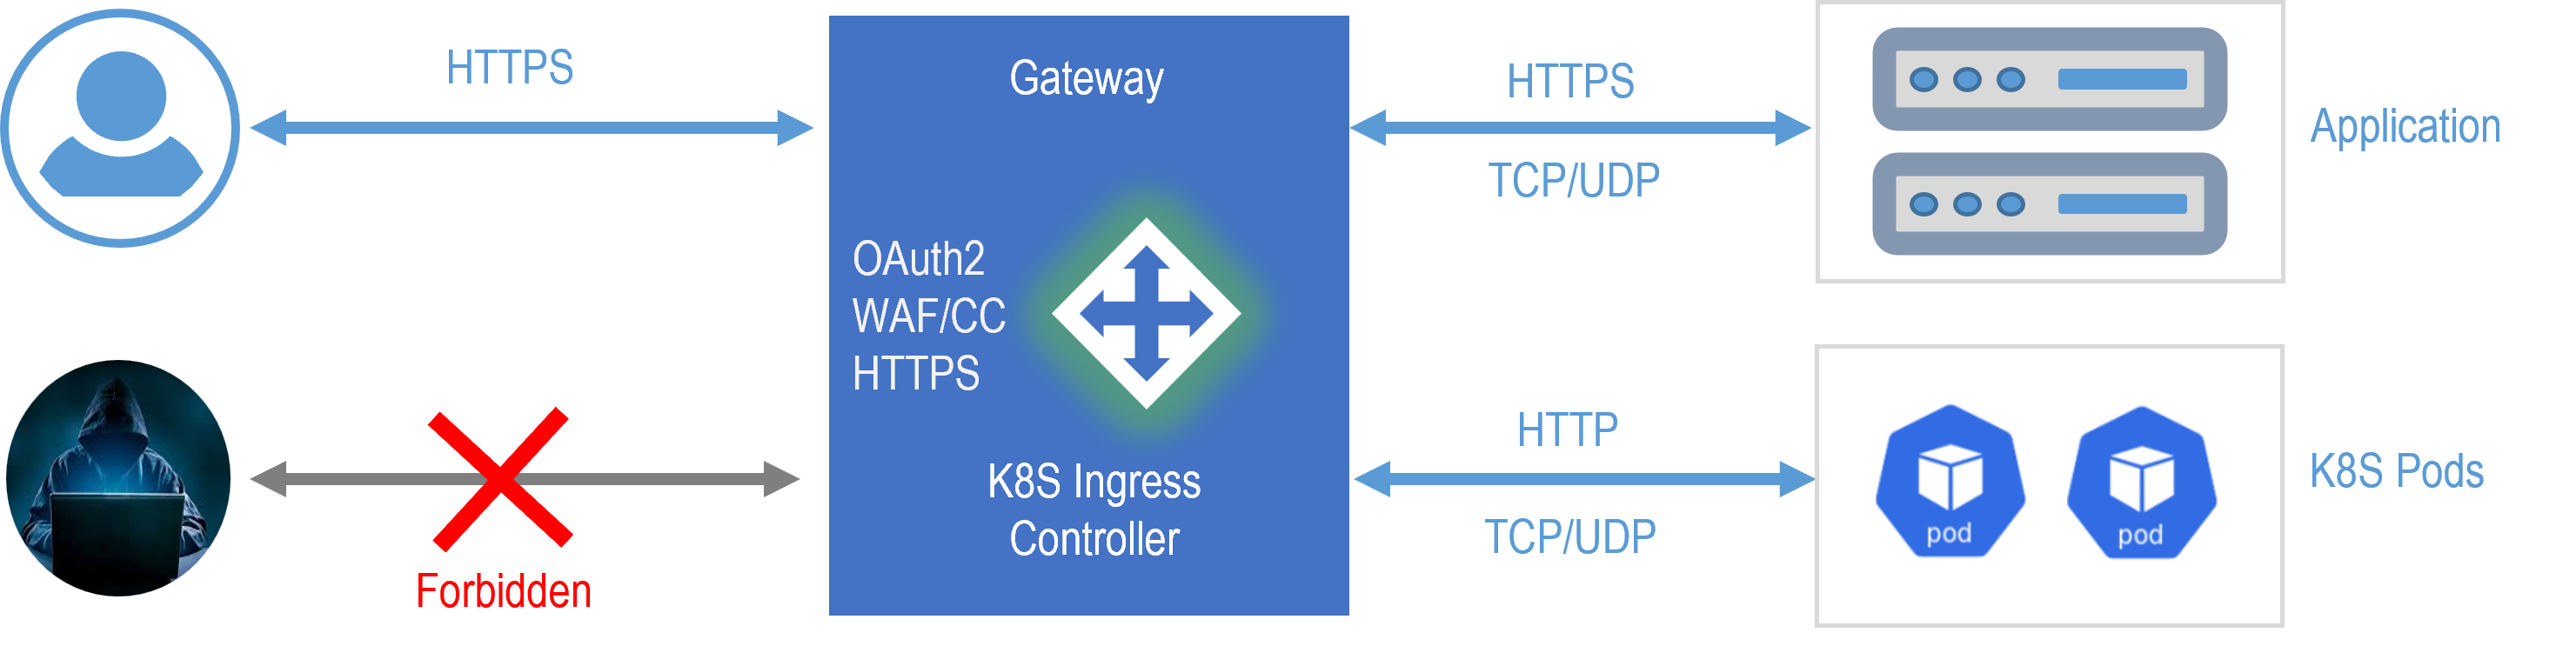 janusec/janusec
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
 sublime-security/ics-phishing-toolkit
Open source tooling to stop ICS phishing (malicious calendar invites)
 jenish-sojitra/jsanalyzer
Burp Suite extension for JavaScript static analysis: extracts API endpoints, URLs, secrets, and emails with noise filtering for web security testing.
 derrickschoen/laravel-framework
Fork of laravel/framework 10.50.2 with CVE-2026-48019 (CRLF injection in default email rule) backported into ValidatesAttributes::validateEmail.…
 saykino/cve-2025-54320
Proof-of-concept for CVE-2025-54320: an email bombing vulnerability in Ascertia SigningHub's Invite User API due to missing rate limiting, allowing…
 at0mxploit/cve-2025-59843-cve-2025-59932
CVE on FlagForge on versions 2.0.0 to 2.3.0. Upgrade to version 2.3.1 to fix the issue.
 yuxblank/cve-2022-2466---request-context-not-terminated-with-graphql
Proof-of-concept for CVE-2022-2466 demonstrating unauthenticated GraphQL request context termination in Quarkus/SmallRye, bypassing authorization…
 afine-com/cve-2018-25031
.json and .yaml files used to exploit CVE-2018-25031