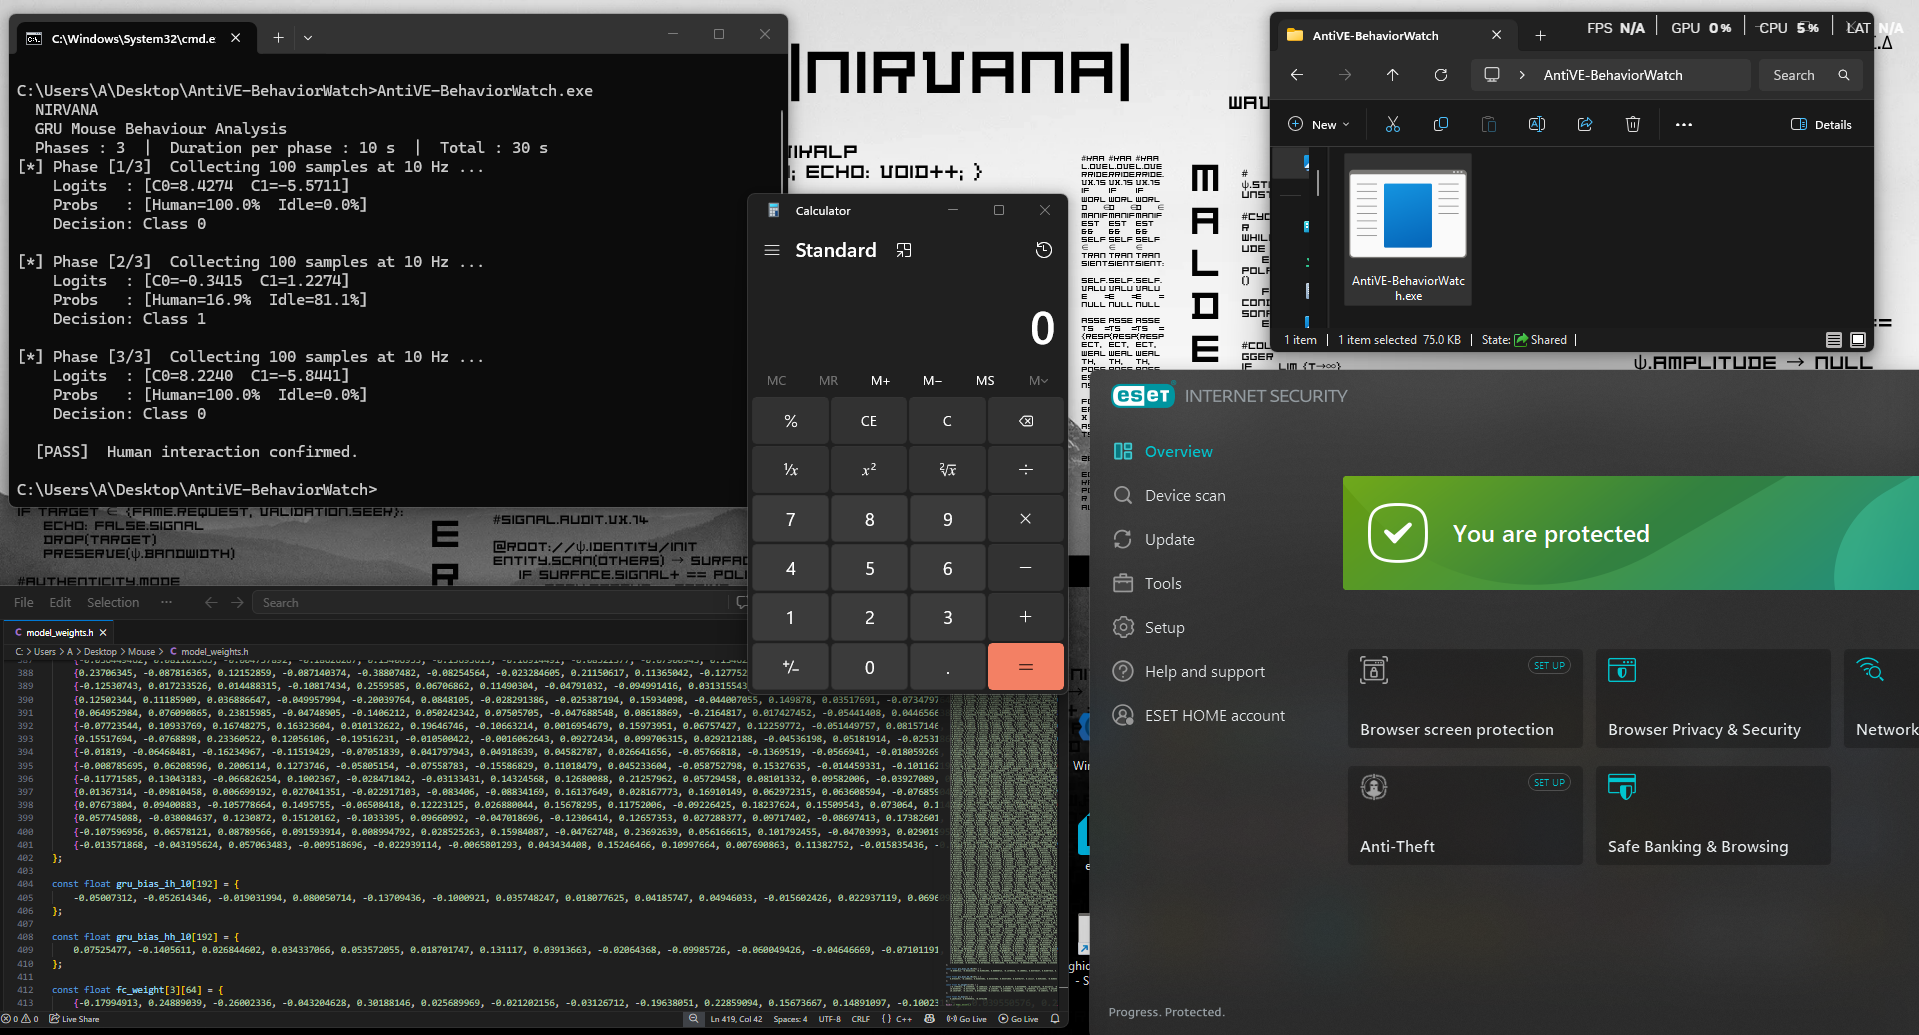
AntiVE-BehaviorWatch

Embedded GRU neural network for real-time human behavior verification via mouse movement analysis, detecting automated analysis systems, sandboxes,…

Embedded GRU neural network for real-time human behavior verification via mouse movement analysis, detecting automated analysis systems, sandboxes,…

C++ tool for detecting AnyRun sandbox environments, enabling malware to evade dynamic analysis and automated sandboxing systems.

Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…

Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…

ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…

Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.

Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…

Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…

Multi-threaded network intrusion detection and prevention system with rule-based detection, protocol-aware inspection, and pcap analysis for…

Windows kernel driver that hooks Nt* SSDT functions to hide debuggers and processes from anti-debug checks, with an x64dbg plugin for stealth…

A PowerShell script that attempts to help malware analysts hide their Windows VirtualBox Windows VM's from malware that may be trying to evade…

Evade behavioral analysis by executing malicious code within trusted Microsoft call stacks, patchless hooking library IAT/EAT.

C++ tool that patches Windows API calls to bypass sandbox RAM size checks, enabling malware to evade detection in isolated analysis environments.

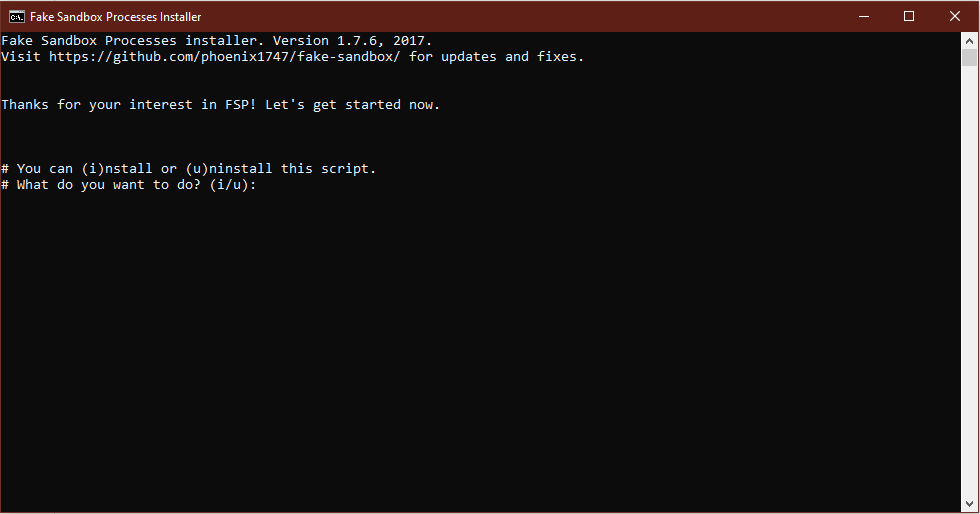
👁🗨 This script will simulate fake processes of analysis sandbox/VM software that some malware will try to avoid.

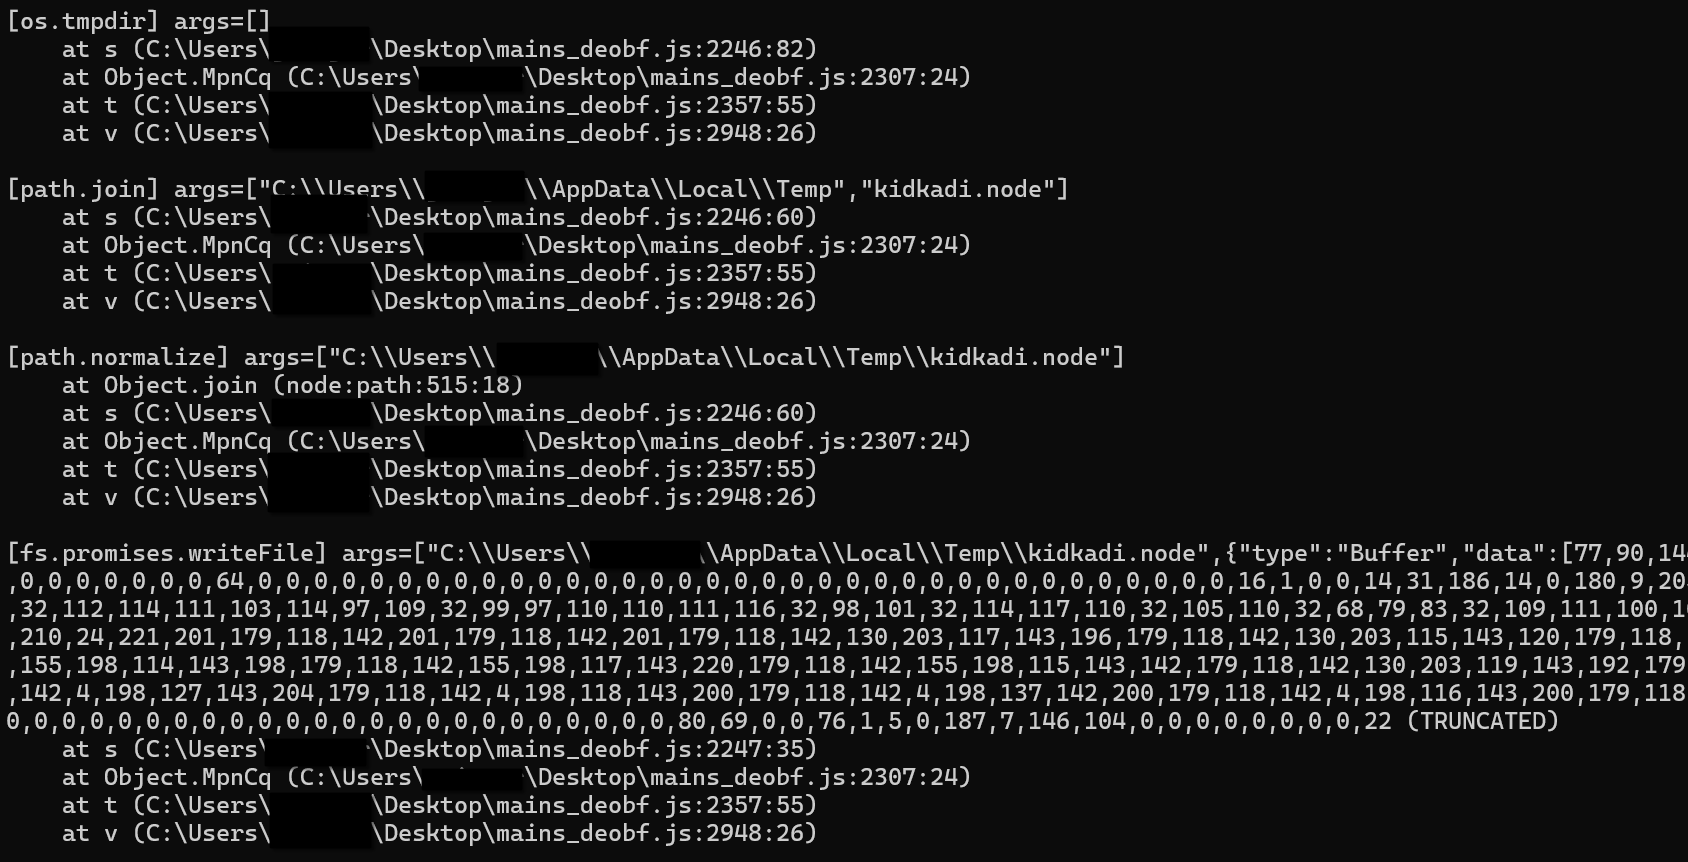
Runtime tracer for Node.js malware analysis that hooks core modules, logs calls, spoofs anti-analysis checks, and captures file writes and HTTP…

Automated detection and tracking of fake engagement on GitHub — daily CI, zero infrastructure

ELF anti-reversing tool that overwrites section headers with nullbytes to prevent static analysis by disassemblers and debuggers, rendering functions…

Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…