
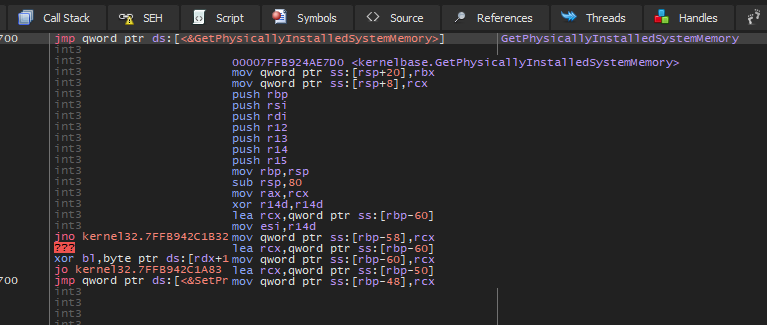
Bypass-Sandbox-Evasion
 zeromemoryex/bypass-sandbox-evasion
C++ tool that patches Windows API calls to bypass sandbox RAM size checks, enabling malware to evade detection in isolated analysis environments.
anti-botbinary-analysisids-ips-evasion+1
zeromemoryex/bypass-sandbox-evasionC++ tool that patches Windows API calls to bypass sandbox RAM size checks, enabling malware to evade detection in isolated analysis environments.
 mephistolist/soviet
A Runtime Crypter in C for Linux ELF binaries.
 theevilbit/shield
An app to protect against process injection and suspicious file links on macOS
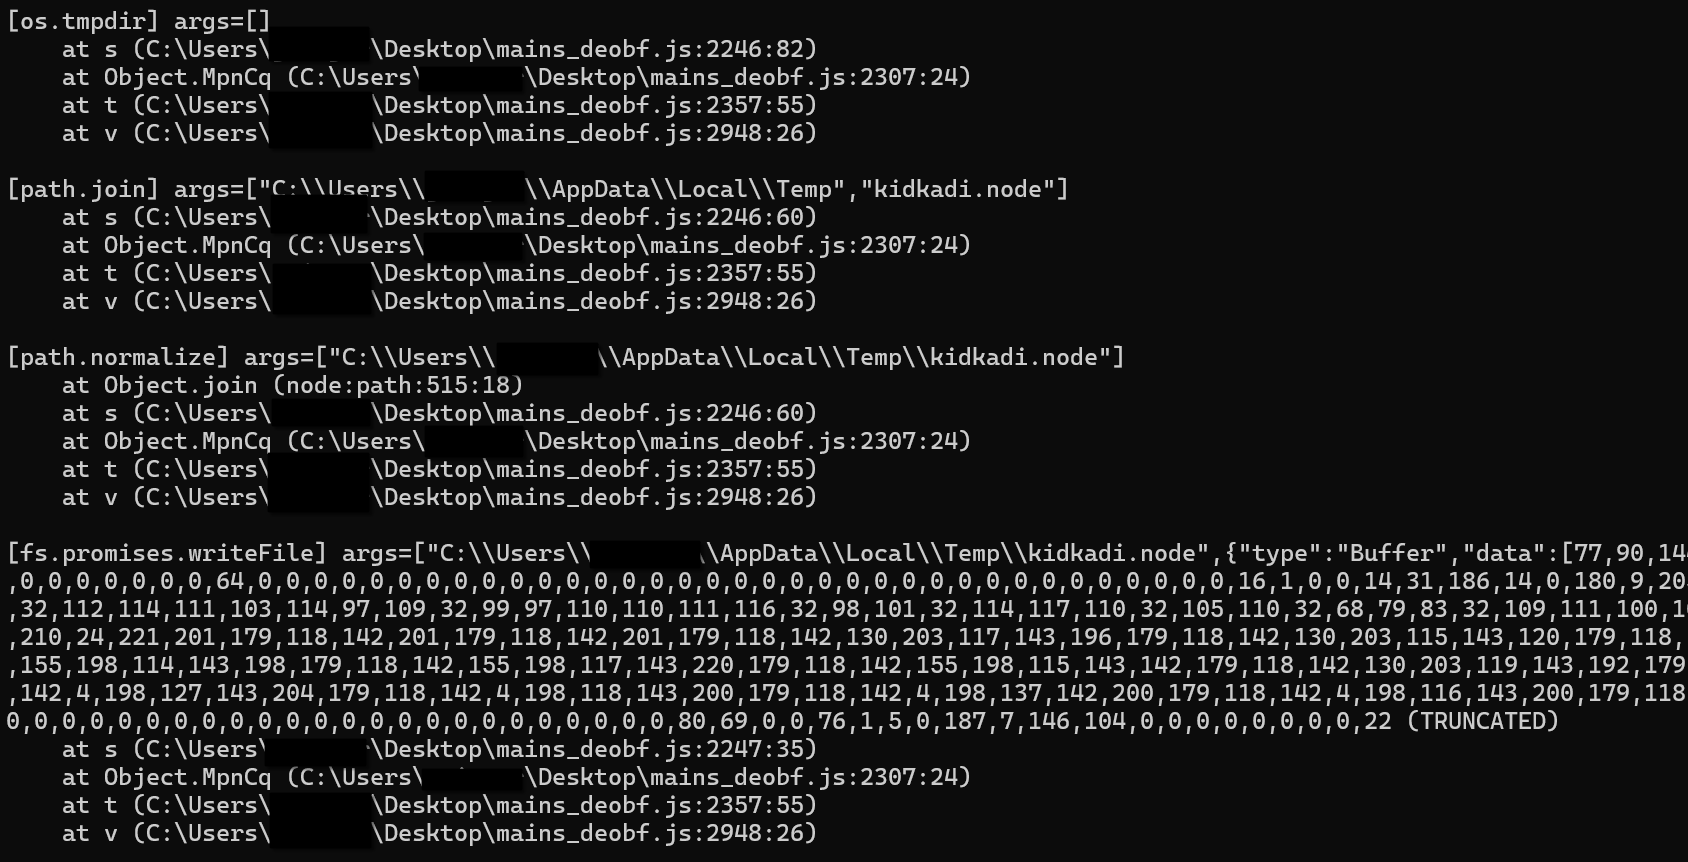 checkpointsw/nodejs-tracer
Runtime tracer for Node.js malware analysis that hooks core modules, logs calls, spoofs anti-analysis checks, and captures file writes and HTTP…
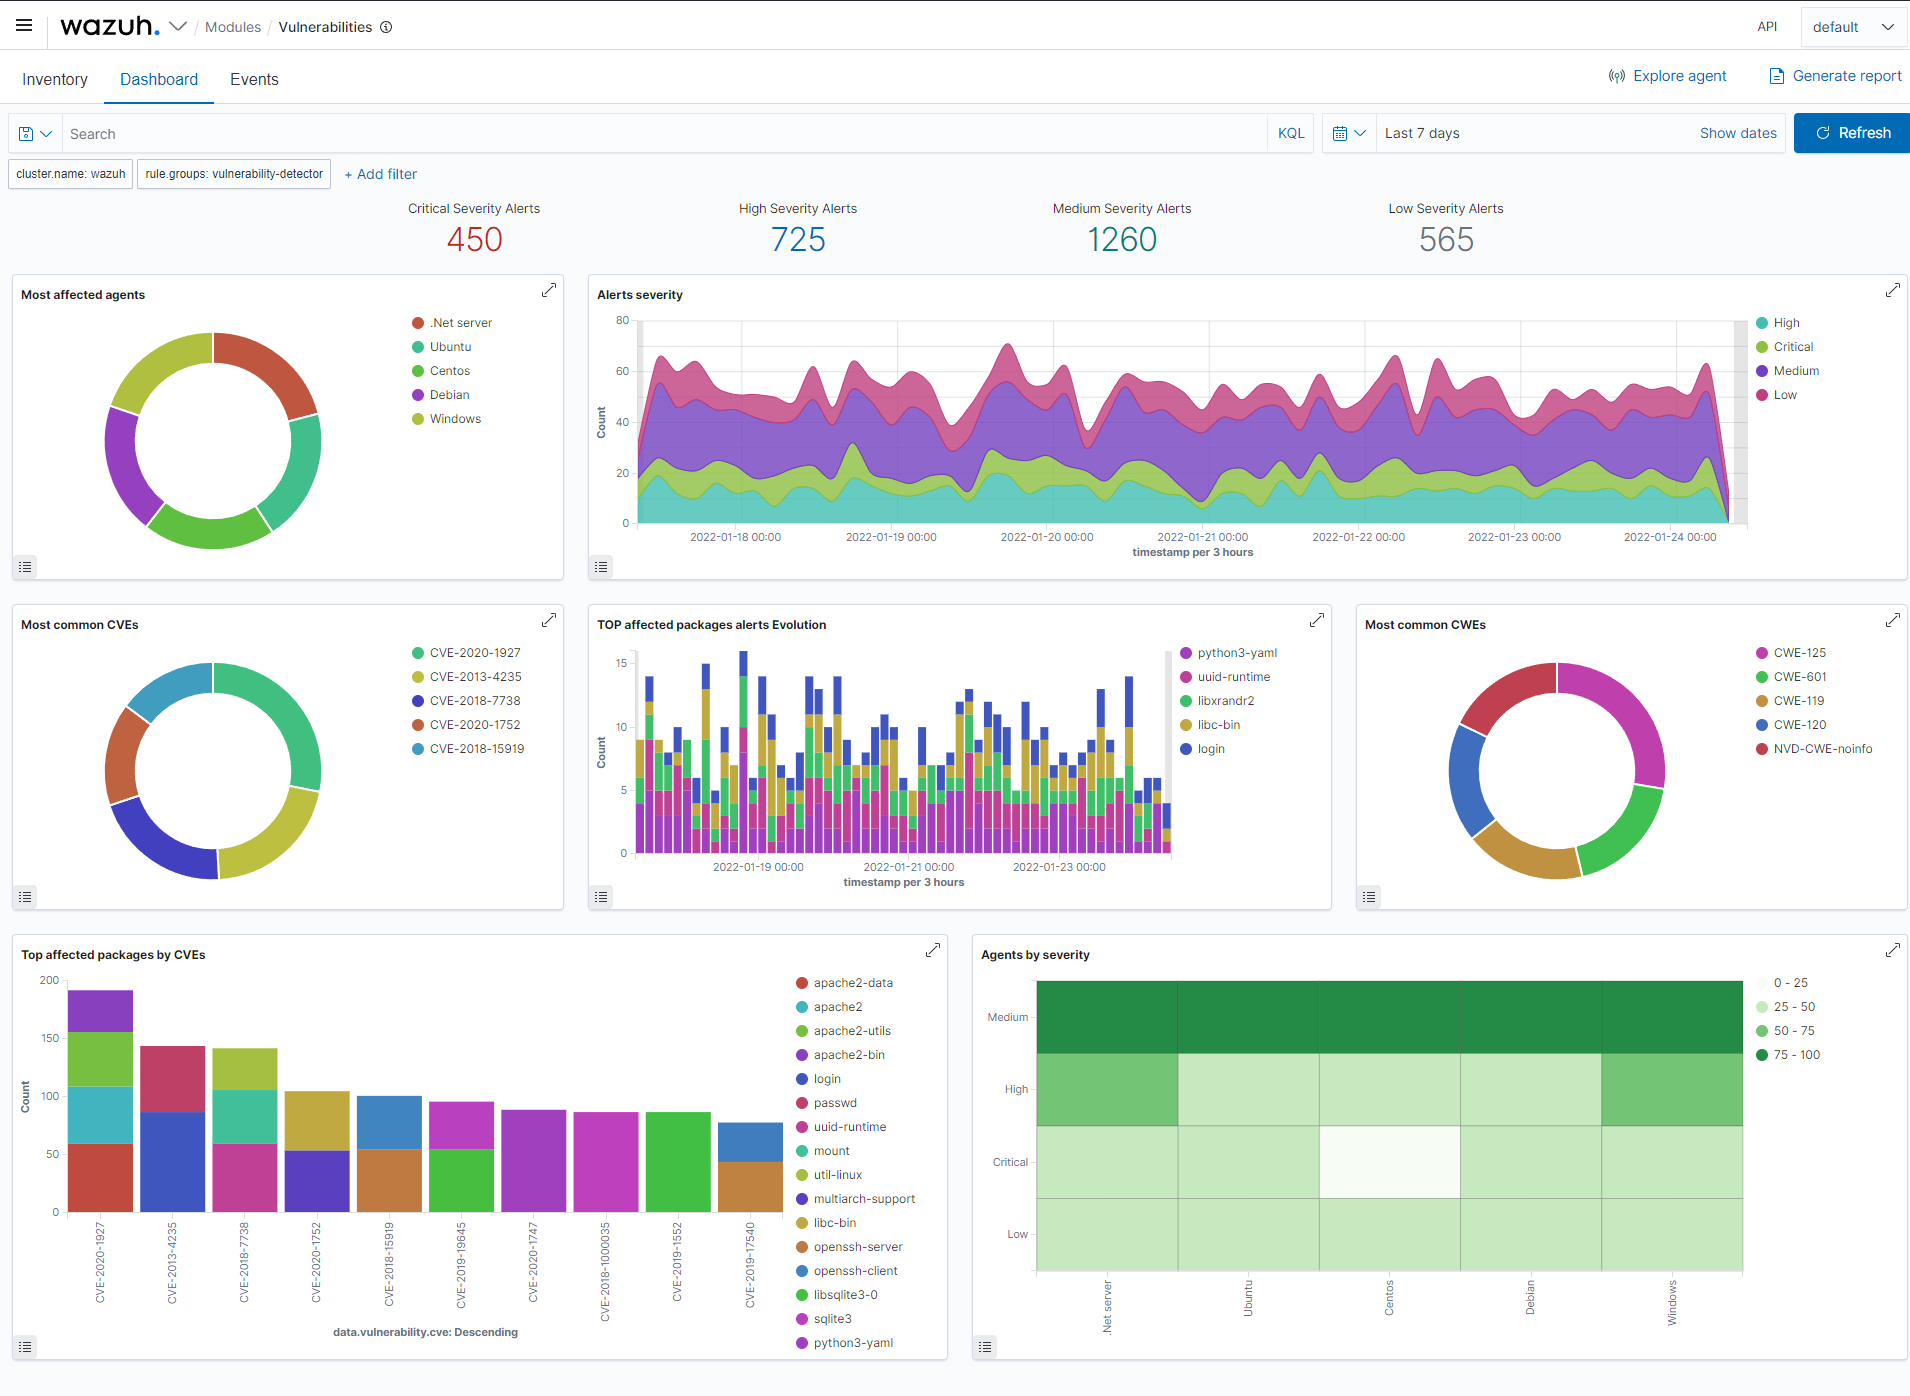 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…