
zeek-quasarrat-detector
 corelight/zeek-quasarrat-detector
Zeek detector for QuasarRat
anomaly-detectionintrusion-detectionmalware-analysis+2
3
corelight/zeek-quasarrat-detectorZeek detector for QuasarRat
 corelight/zeek-asyncrat-detector
A Zeek based AsyncRAT malware detector.
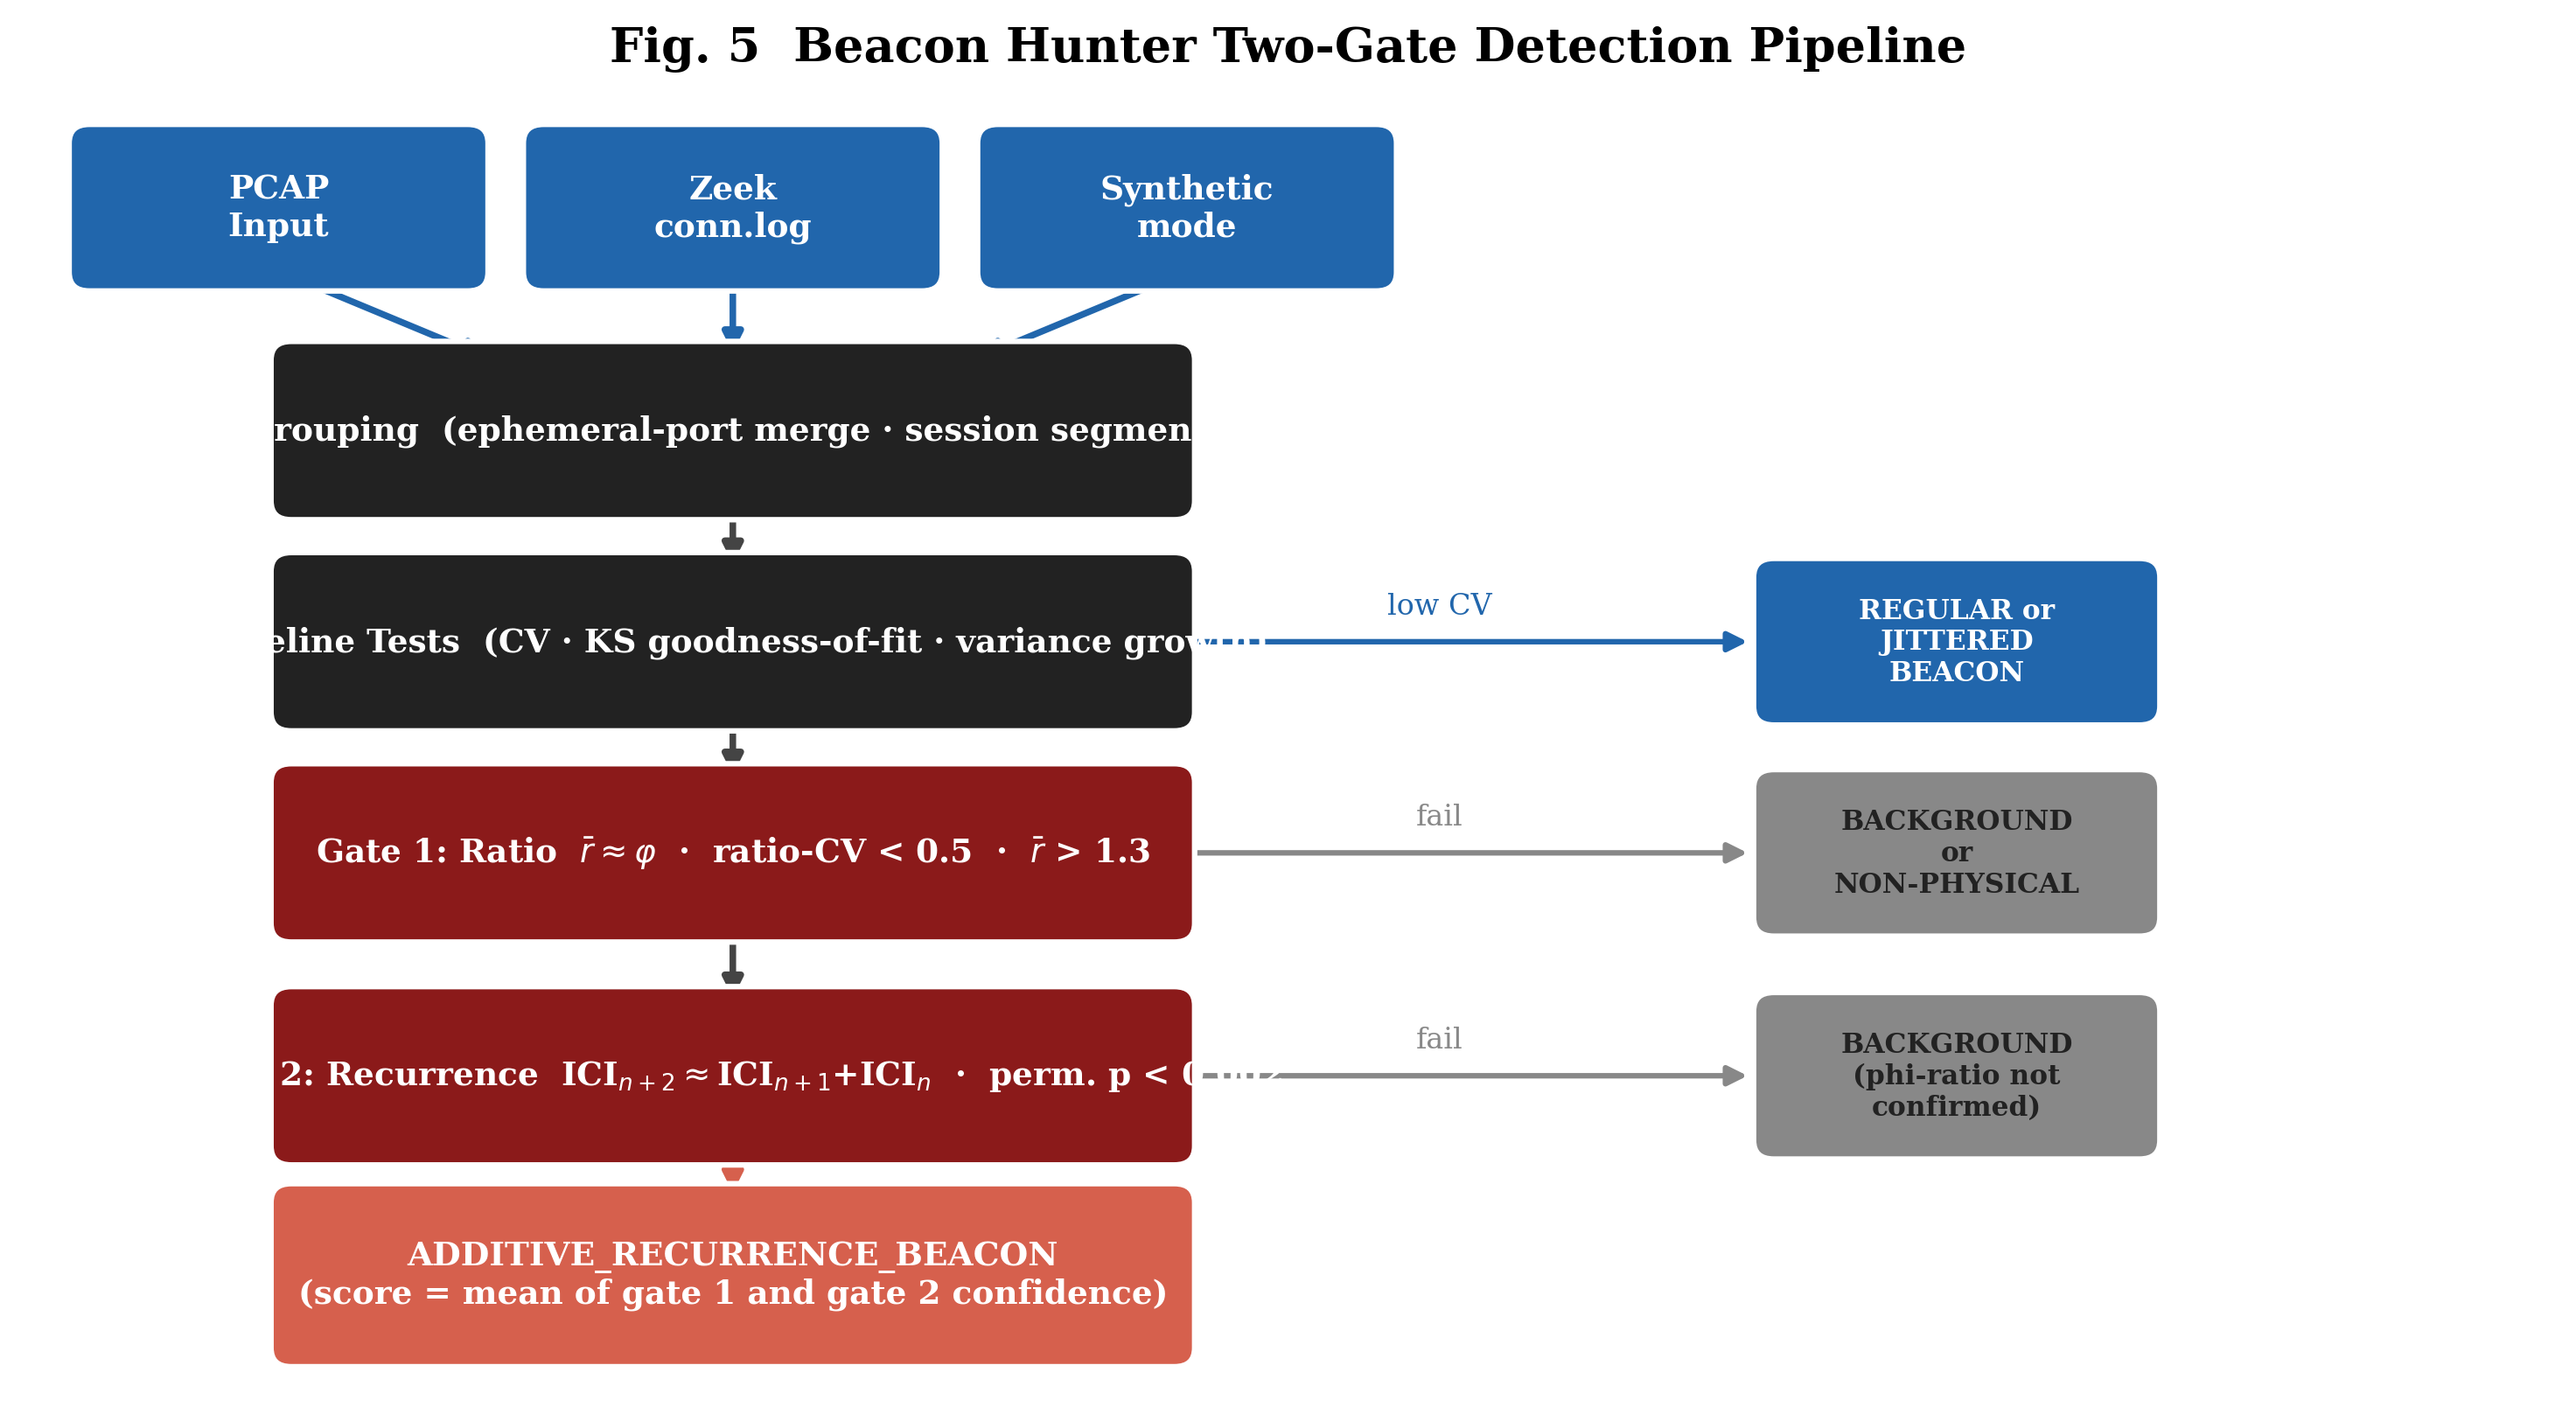 mrcord77/beacon-hunter
Detects phi-structured C2 beacons that evade RITA and standard regularity-based detectors
 activecm/rita
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
 dereeqw/berrysentinel
Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…
 malwaremorghulis/sunburst
Detection for SUNBURST C2 Stage-1 using Shannon Entropy
 oyesanyf/oshoosiclaw
Autonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…
 corelight/zeek-caldera-detector
A Zeek based Mitre Caldera detector.