
columbo
 visma-prodsec/columbo
ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…
anomaly-detectionbinary-analysisdigital-forensics+3
61
visma-prodsec/columboML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…
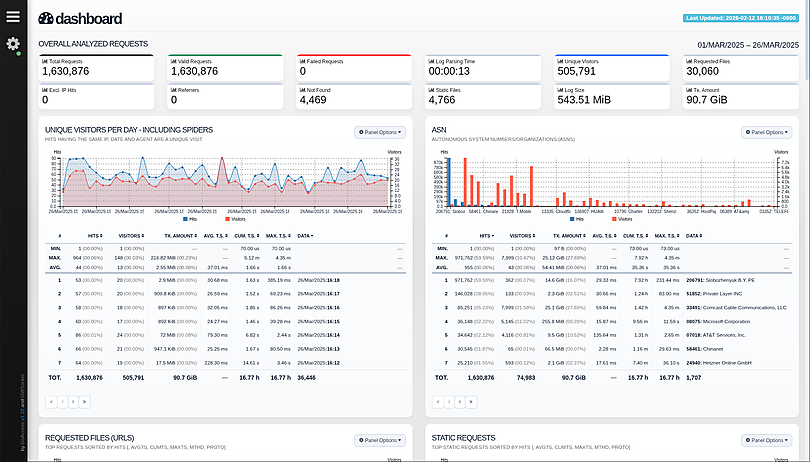 allinurl/goaccess
GoAccess is a real-time web log analyzer and interactive viewer that runs in a terminal in *nix systems or through your browser.
 nccgroup/mimikatz-detector-condrv
The Console Monitor Driver is a KMDF kernel-mode filter driver that captures certain Fast I/O operations (input and output) that is sent to or from…
 kennbroorg/poorskeme
OSINT - Data Visualization - Blockchain - Awareness - Scam
 initconf/cve-2020-16898-bad-neighbor
Zeek detection for CVE-2020-16898-"Bad Neighbor"
 joidiego/detection-struts-cve-2017-5638-detector
Real-time anomaly detection system for Apache Struts CVE-2017-5638 exploit using streaming analytics, 3-gram byte analysis, and Count-Min Sketch.…
 nfstream/nfstream
NFStream: a Flexible Network Data Analysis Framework.
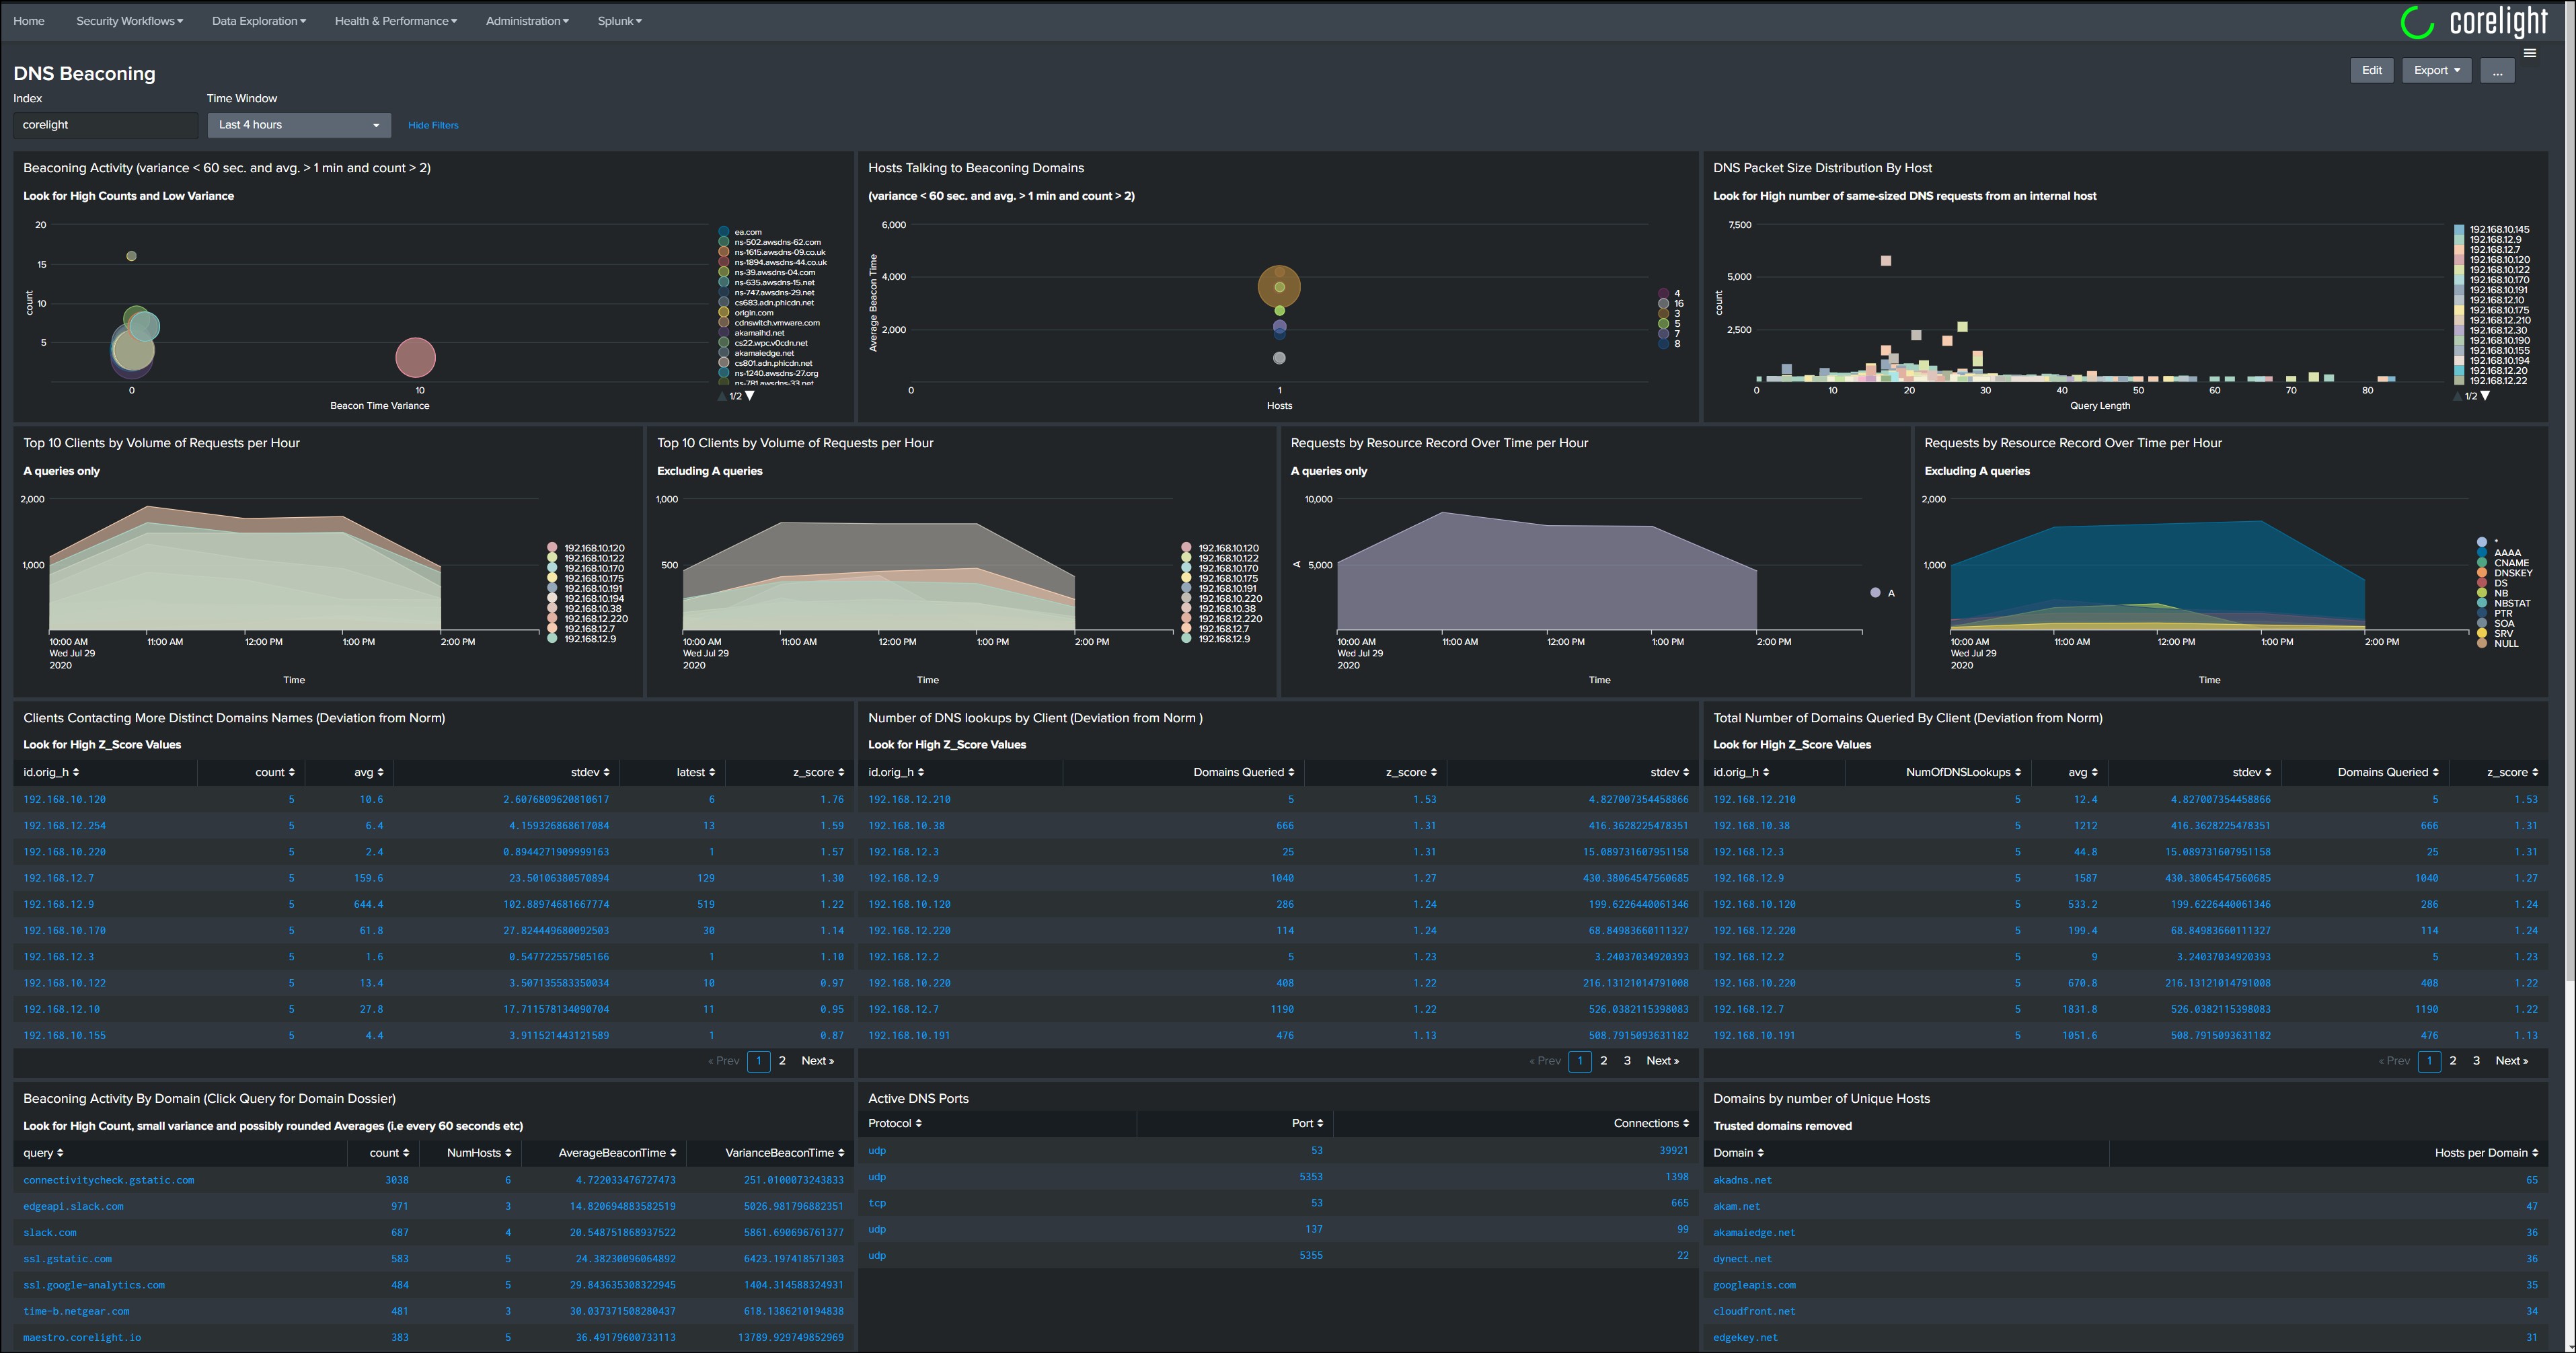 corelight/dashboards-splunk-dns-hunting-beaconing
DNS Dashboard for hunting and identifying beaconing
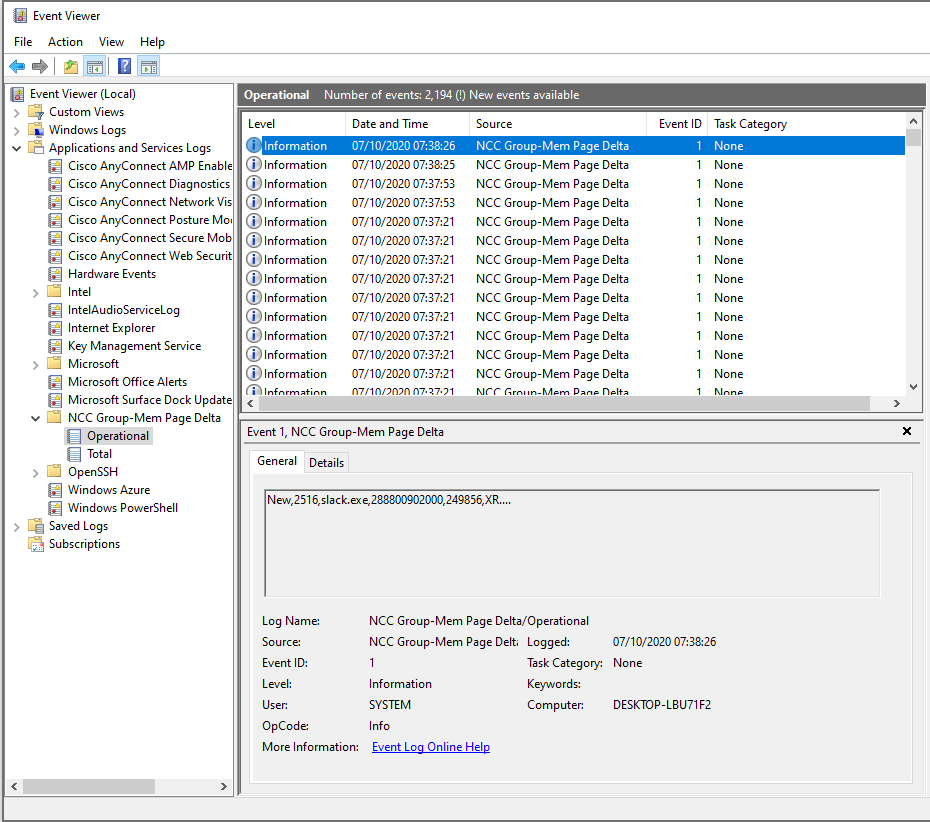 nccgroup/windowsmempagedelta
A Microsoft Windows service to provide telemetry on Windows executable memory page changes to facilitate threat detection
 connectedlucy/plague
Default Detections for EDR
 cisco/joy
A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.
 delvelabs/batea
AI-based, context-driven network device ranking
 corelight/http-stalling-detector
Detect HTTP stalling attacks like slowloris with Bro
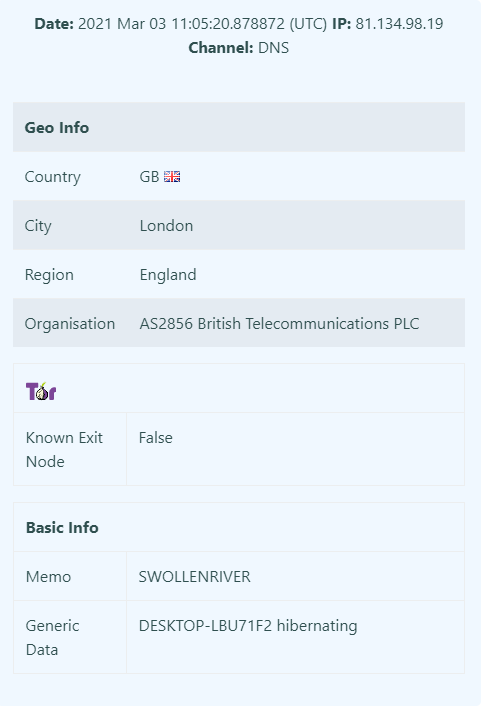 nccgroup/killedprocesscanary
A canary designed to minimize the impact from certain Ransomware actors
 aquibpro/forensix-studio
Forensic intelligence platform that analyzes files, correlates threat indicators, maps behavior to MITRE ATT&CK, and generates actionable security…
 mandiant/silketw
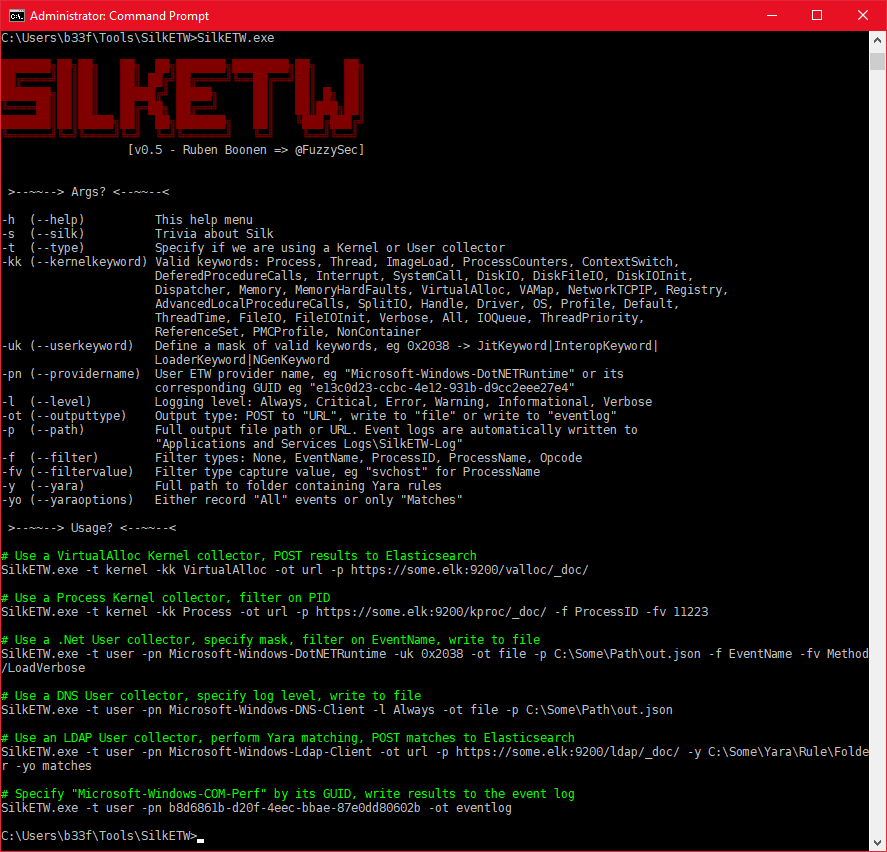
C# wrapper for ETW that serializes kernel and user-mode event data to JSON for threat hunting, malware analysis, and incident response, with Yara…
 uky007/petriage
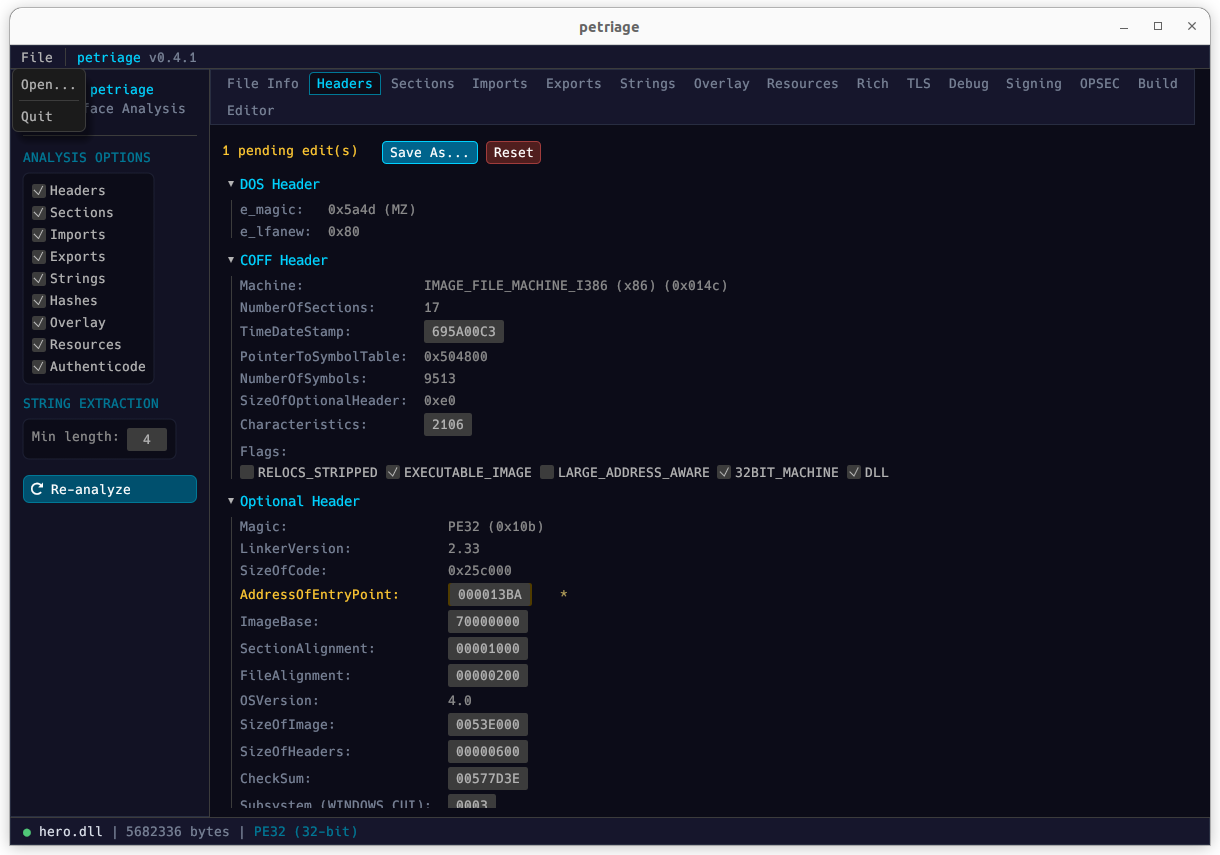
PETriage: A symbol-unified PE file reader for triage, built for multi-platform and multi-interface use.
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…