
plague
 connectedlucy/plague
Default Detections for EDR
anomaly-detectionconfiguration-auditingcurated-resources+4
connectedlucy/plagueDefault Detections for EDR
 ait-aecid/rootkit-detection-ebpf-time-trace
Detection of rootkit file hiding activities through analysis of shifts in kernel function execution times.
 edoardottt/offensive-onos
My experiments in weaponizing ONOS applications (https://github.com/opennetworkinglab/onos)
 c2dc/anomaly-flow
Framework for implementing Network Intrusion Detection Systems (NIDS) aimed at identifying anomalies in network flows using Federated Learning models.
 nccgroup/impossibletravelloganalysis
Basic log analysis tool to detect impossible travel via IP address geographic information
 corelight/zeek-spicy-ospf
A Zeek OSPF packet analyzer based on Spicy.
 bplinux/chackd
Daemon to randomize tcp_challenge_ack_limit to prevent side channel attacks CVE-2016-5696
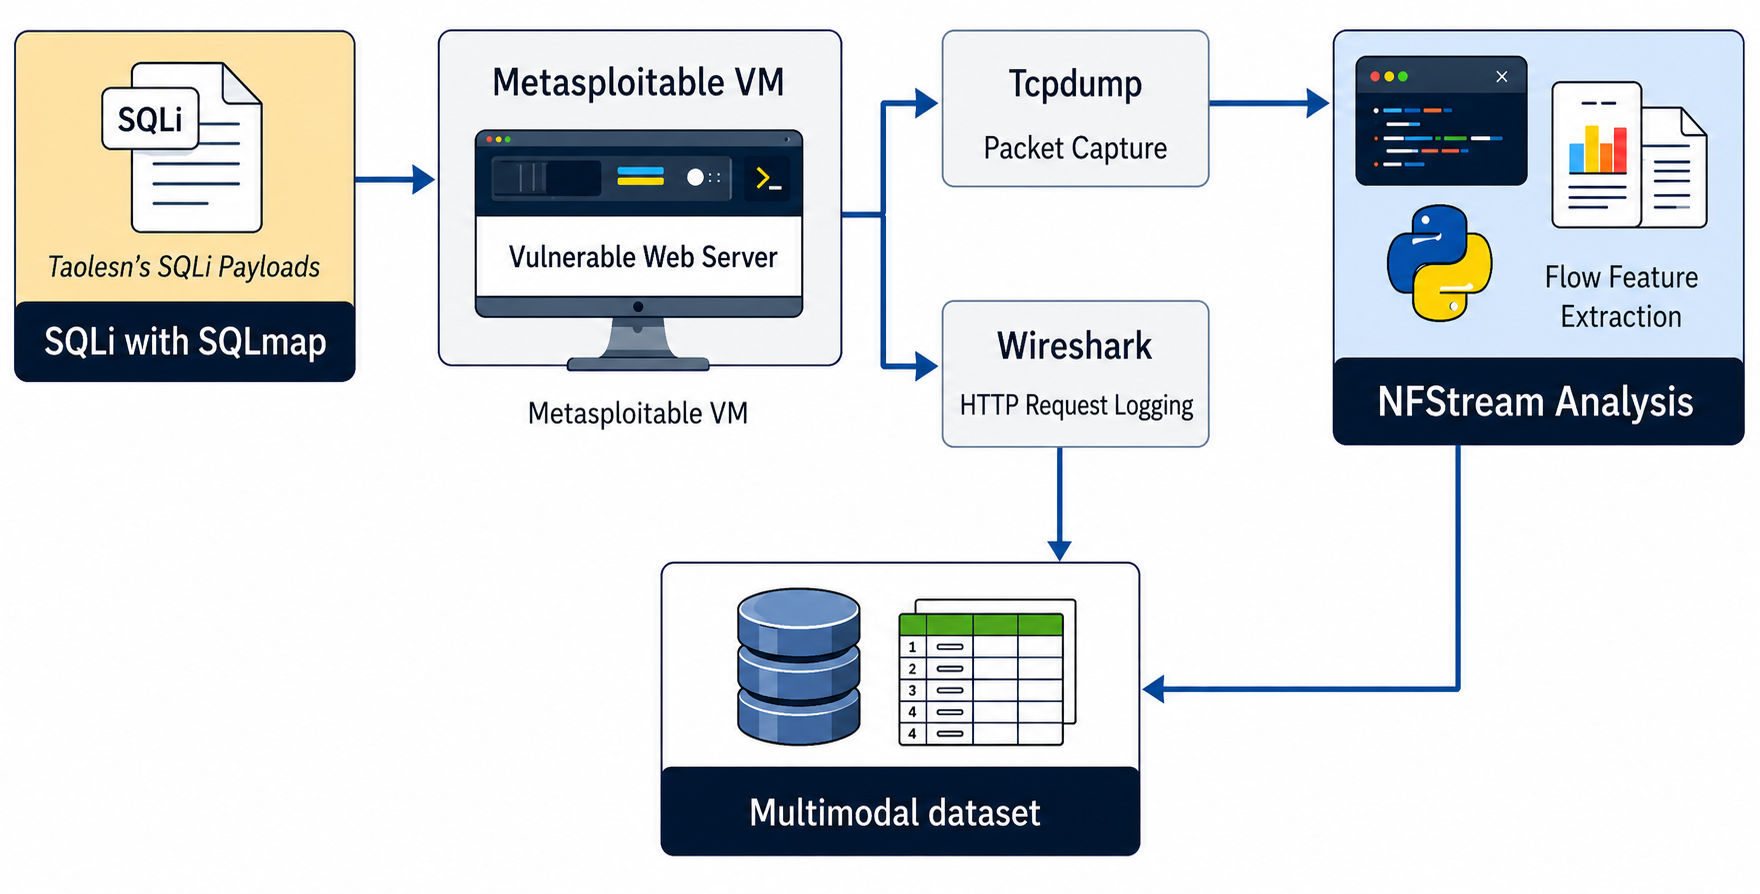 paul12345-cyber/multimodal-web-attack-dataset
This repository hosts a multimodal web attack dataset (MWAD) to advance AI-driven threat detection research.
 leitwacht/leitwacht
Leitwacht control plane — runtime security for GitLab Runner CI/CD: policy authoring, multi-tenancy, audit, GitLab integration
 corelight/zeek-endpoint-enrichment-conn
Enrich the conn.log with EDR data
 cyberdudebivash/cyberdudebivash-5g-core-key-rotation-ghost-admin-auditor
Production-grade tool for detecting & remediating CVE-2026-0622 (Ghost Admin privilege escalation & master key exposure in 5G core software).