
sentrygrid
 kreotic/sentrygrid
ML-driven threat detection and continuous monitoring platform built for federal zero trust architectures.
anomaly-detectioncloud-securitydefensive-tools+3
kreotic/sentrygridML-driven threat detection and continuous monitoring platform built for federal zero trust architectures.
 artur-augustyniak/class_struggle
Autoencoder-based anomaly detection for identifying phishing domains using CERT Polska warning list data, with Jupyter notebooks for research and…
 corelight/corelightforsplunk
Splunk app for integrating and analyzing Corelight network detection data, enabling real-time threat hunting and incident response.
 corelight/petitpotam
Detects NTLM relay attacks via PetitPotam exploit using Zeek, distinguishing successful and unsuccessful attempts by analyzing DCERPC return codes.
 jenderal92/ddos-traffic-monitor
A real-time traffic monitoring tool that detects and displays network traffic volume per IP address to identify potential DDoS attacks.
 reyjesusq/sentinel-mcp
Autonomous AI-powered cyber defense system using MCP, Gemini 2.0 Flash, Dynatrace observability and MongoDB. Google Cloud Hackathon submission.
 yumlembam/insider-threat
Graph-based insider threat detection using GCN-BiLSTM and attention models on CMU CERT datasets. Includes data preprocessing, feature extraction, and…
 aquibpro/forensix-studio
Forensic intelligence platform that analyzes files, correlates threat indicators, maps behavior to MITRE ATT&CK, and generates actionable security…
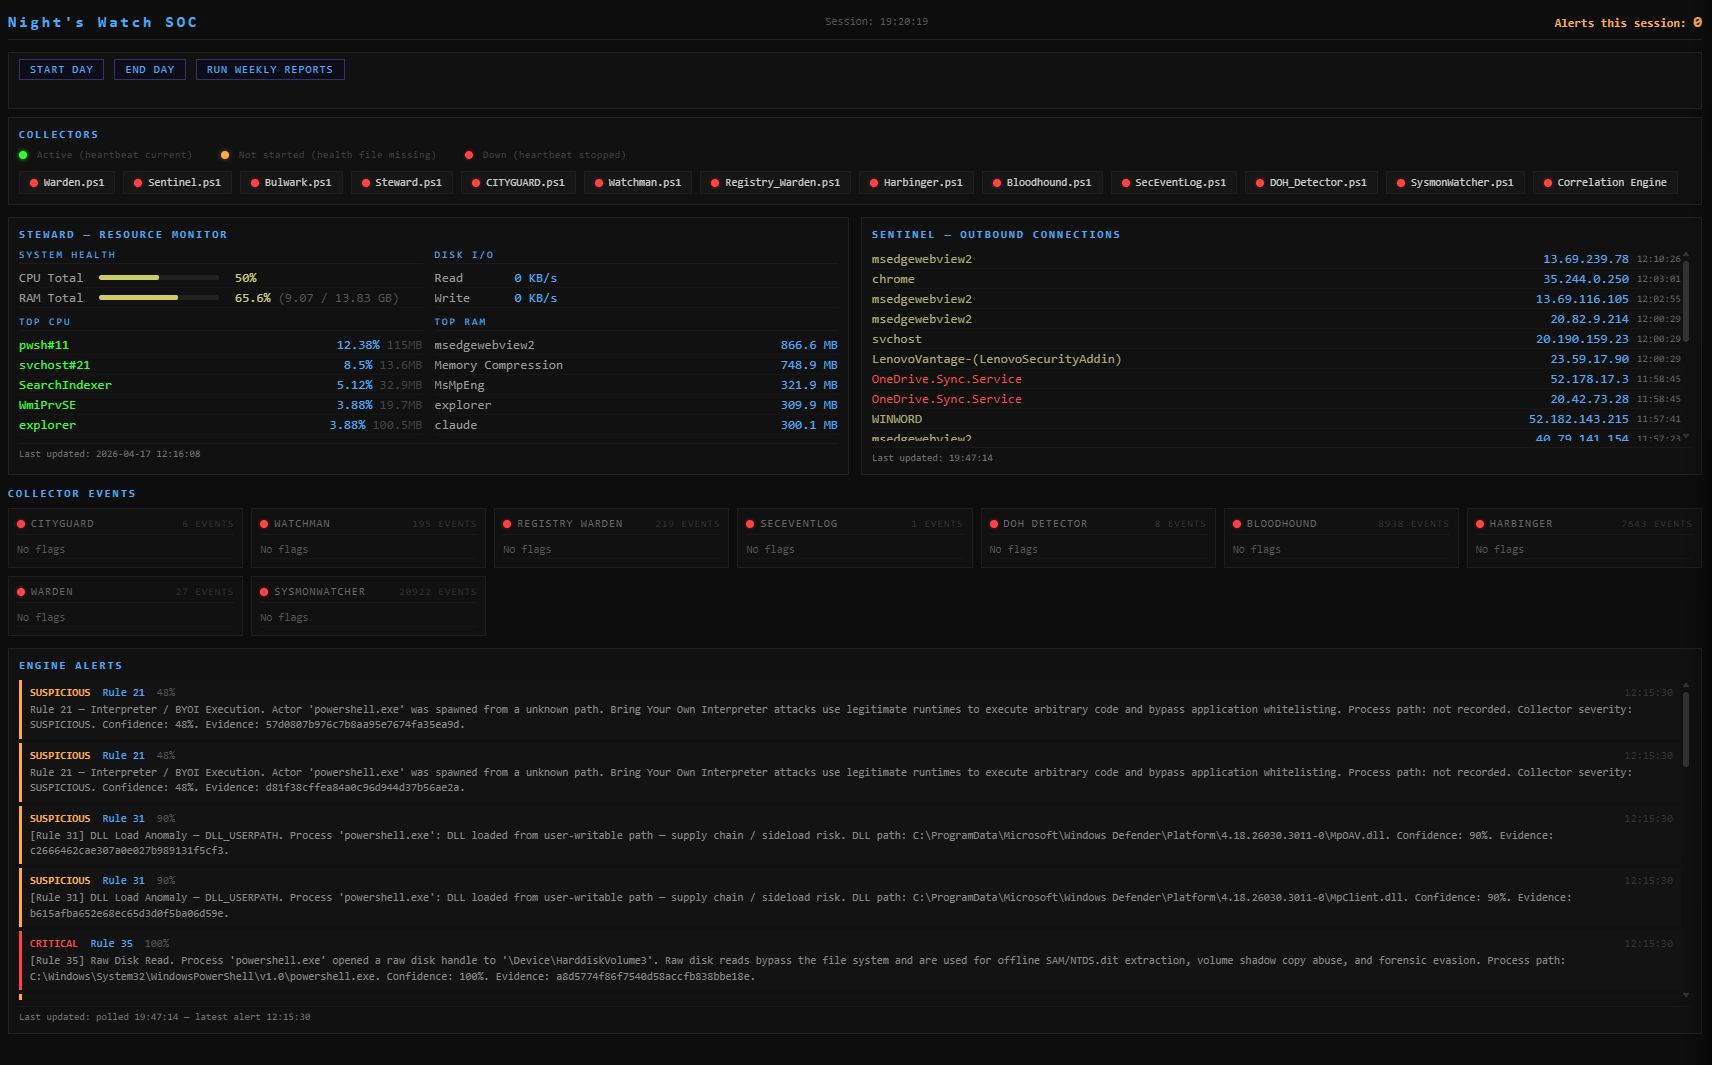 nate-ryan-7690/home_soc_suite
A personal Windows SOC suite built in PowerShell — monitors network connections, resource usage, scheduled tasks and power events with severity…
 jazbengu/threatdetect
Streamlit-based insider threat detection prototype using XGBoost and Isolation Forest to analyze employee activity data, generate risk summaries, and…
 adem-hosni/mappedimagesdetector
Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk
 siddharth2440/network-detection-engine
Lightweight network intrusion detection engine capturing live traffic with libpcap. Detects SYN/ICMP floods, port scans, and signature-based web…
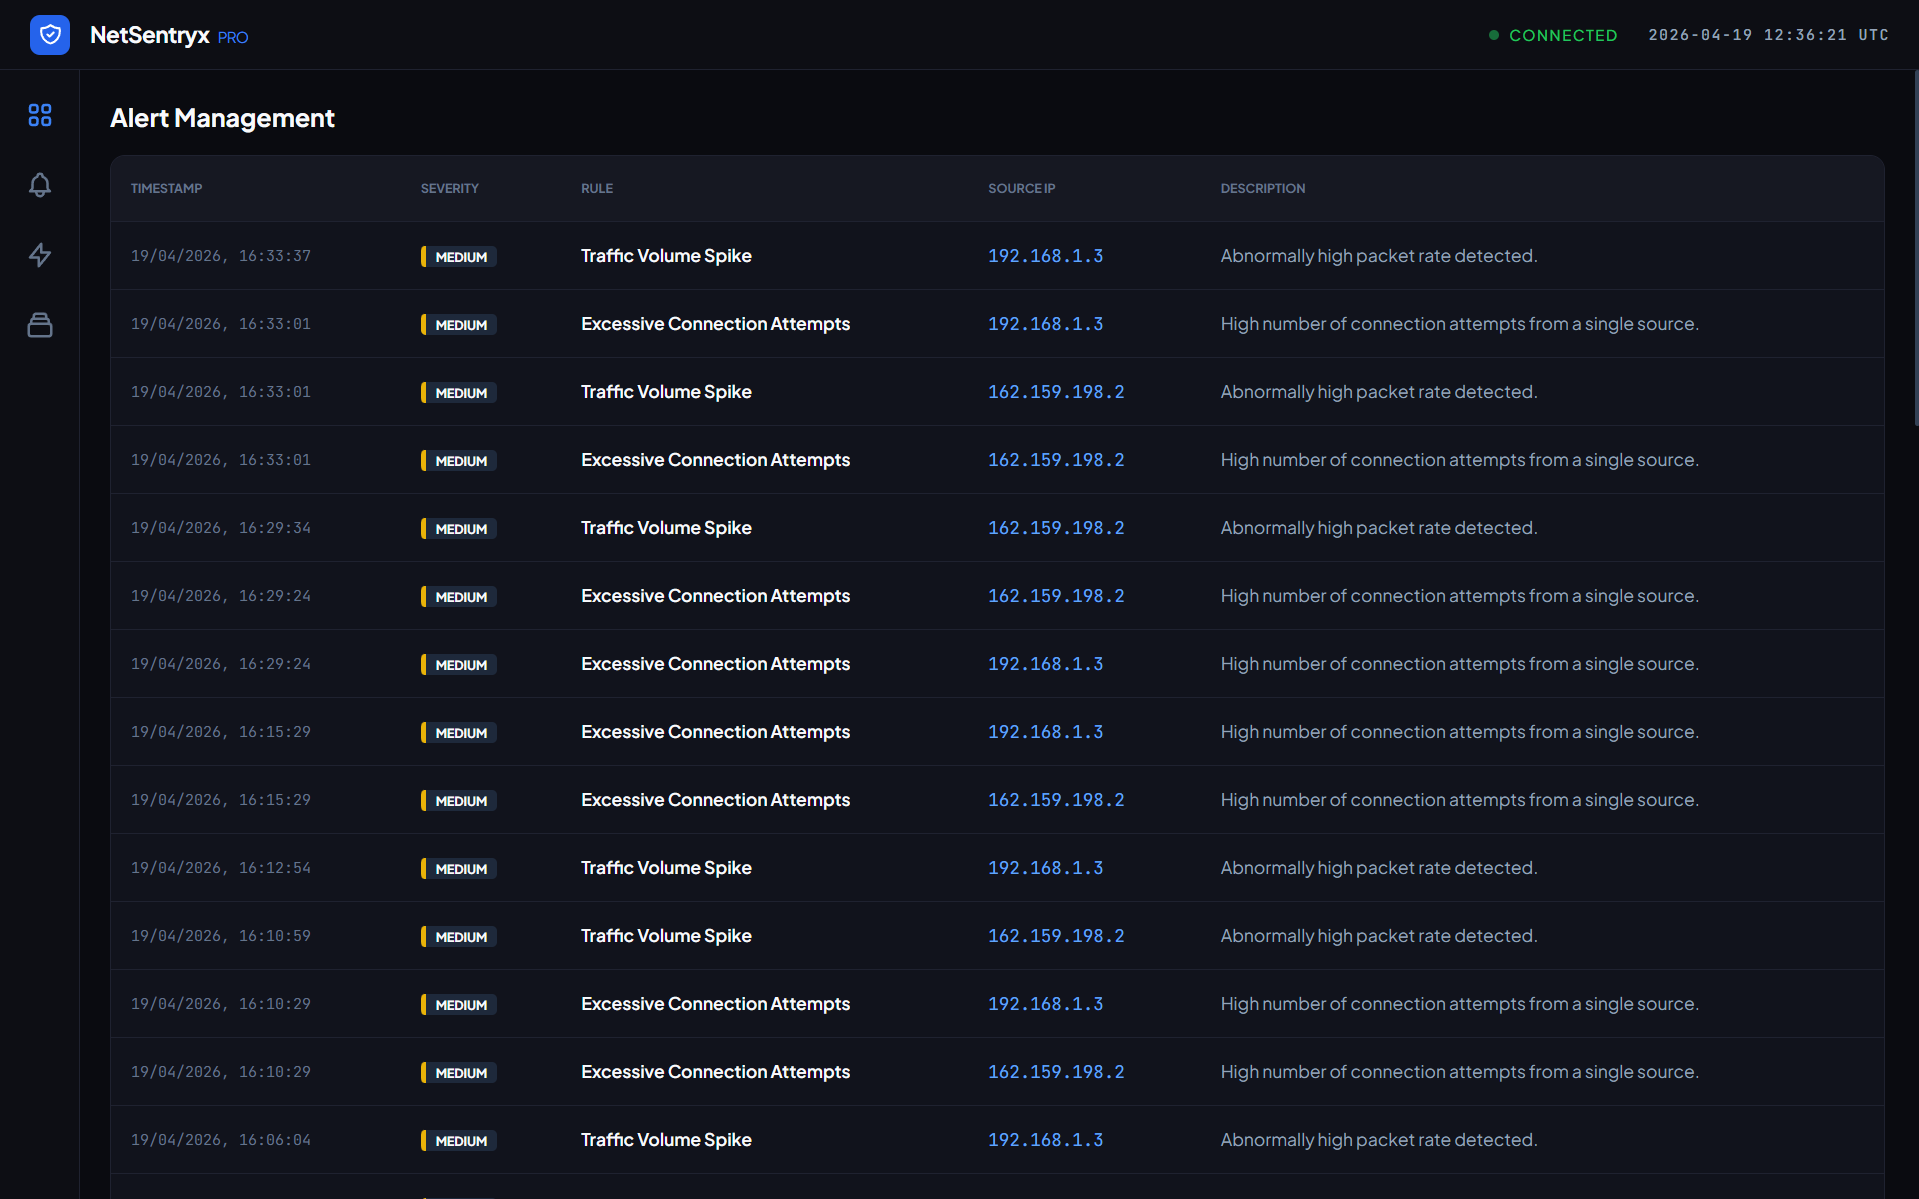 aman-sharma-dev/netsentryx
An event-driven network monitoring platform that performs live packet capture (Npcap), low-latency traffic analytics, and unsupervised threat…
 mlily2024/final-project-sql-injection-pipeline
Hybrid machine-learning pipelines for detecting SQL injection in web traffic, combining DistilBERT and BERT-GNN models with adversarial training and…
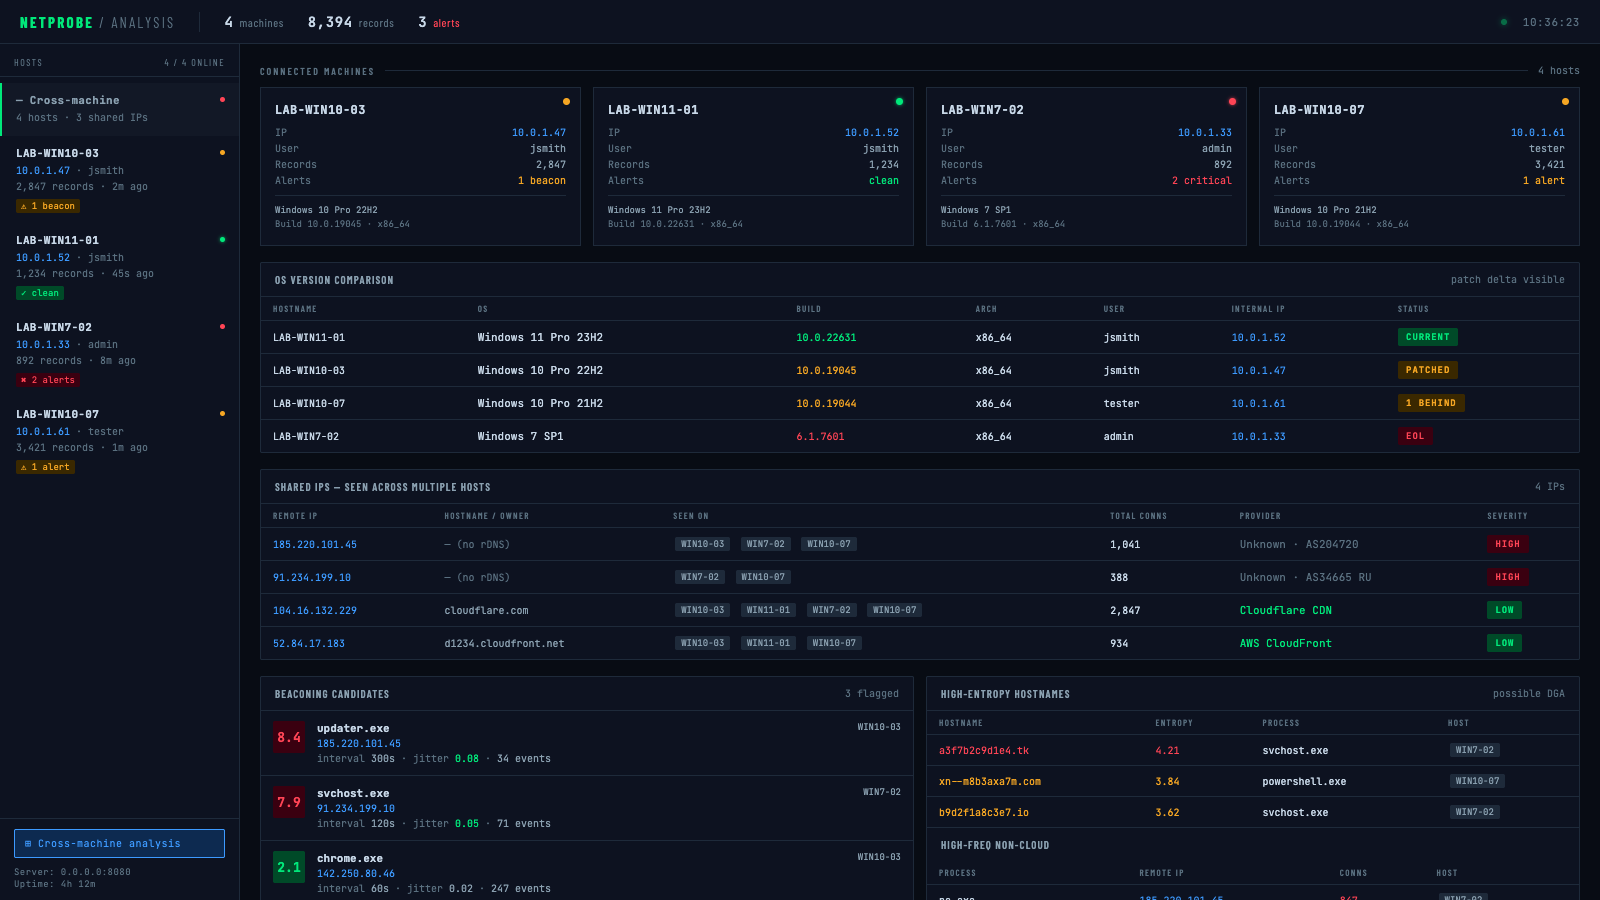 hackinglz/gibson
Network monitoring tool that maps process-to-network connections, identifies cloud providers, and detects beaconing activity
 mcastens/alycon-threat-landscape
Training-free anomaly detection framework using Shannon Entropy, Fisher Information, and Wasserstein Distance to map system states into geometrically…
 camp0/aiengine
AIEngine is a next generation interactive/programmable Python/Ruby/Java/Lua and Go NIDS (Network intrusion detection system).
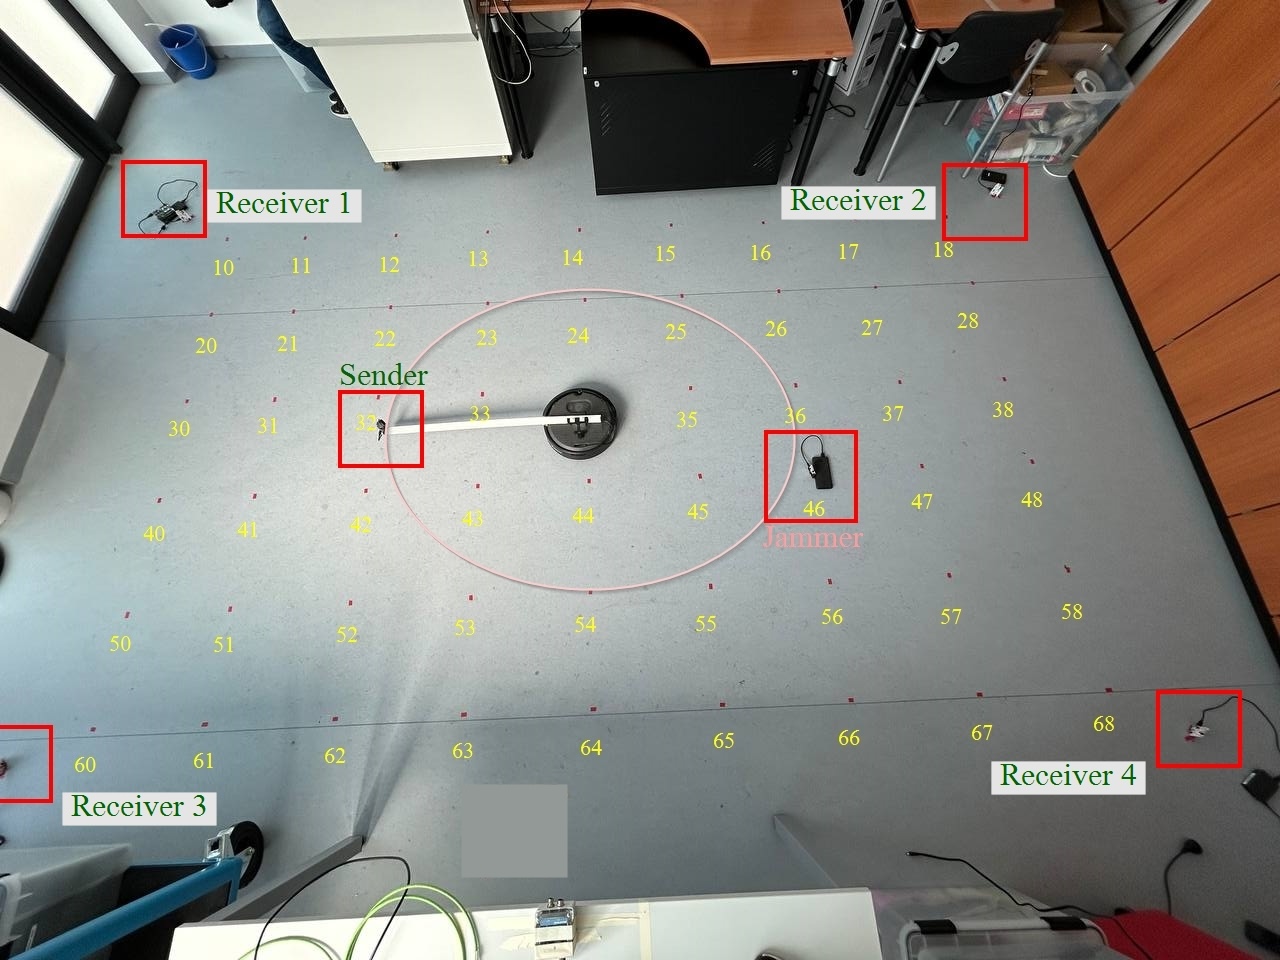 afbf4c8996f/jammer-loc
Implements machine and deep learning methods for indoor UWB jammer localization, including hyperparameter optimization, classification, and…