AI-driven-MITRE-Attack

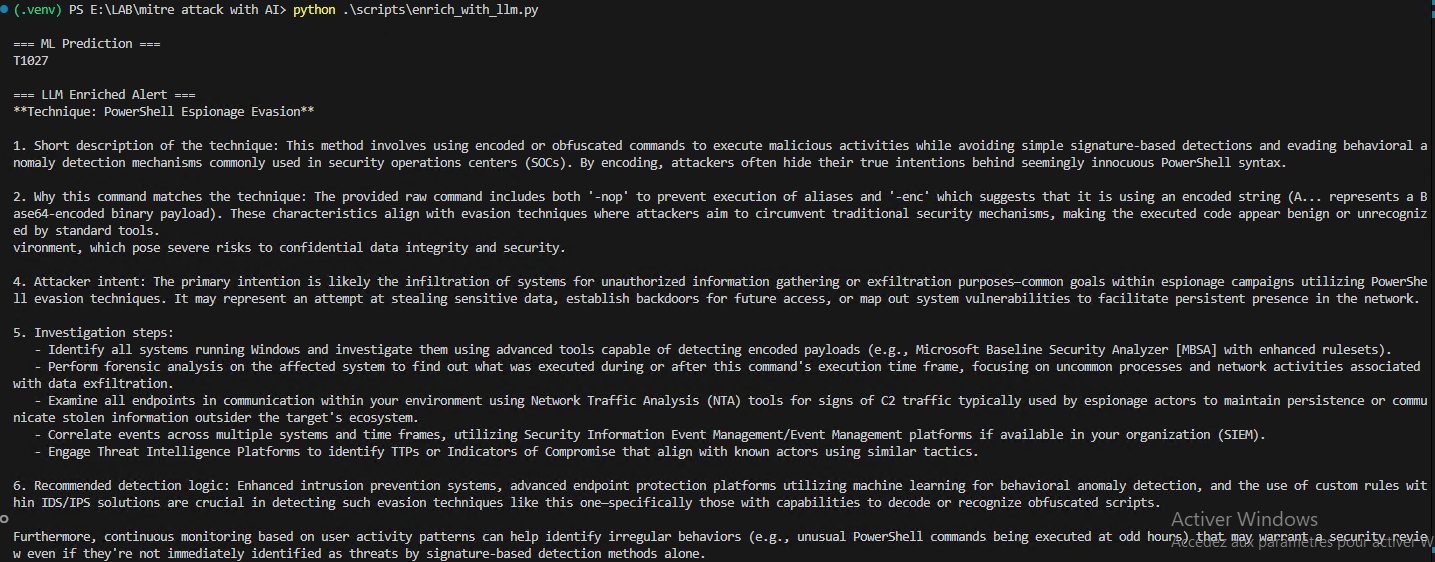
This repository demonstrates a machine learning pipeline for detecting MITRE ATT&CK techniques from logs and enriching the output using a local LLM.

This repository demonstrates a machine learning pipeline for detecting MITRE ATT&CK techniques from logs and enriching the output using a local LLM.

FLNET2023 is a dataset designed for intrusion detection in Federated Learning scenarios. It's built using the CORE emulator, simulating a realistic…

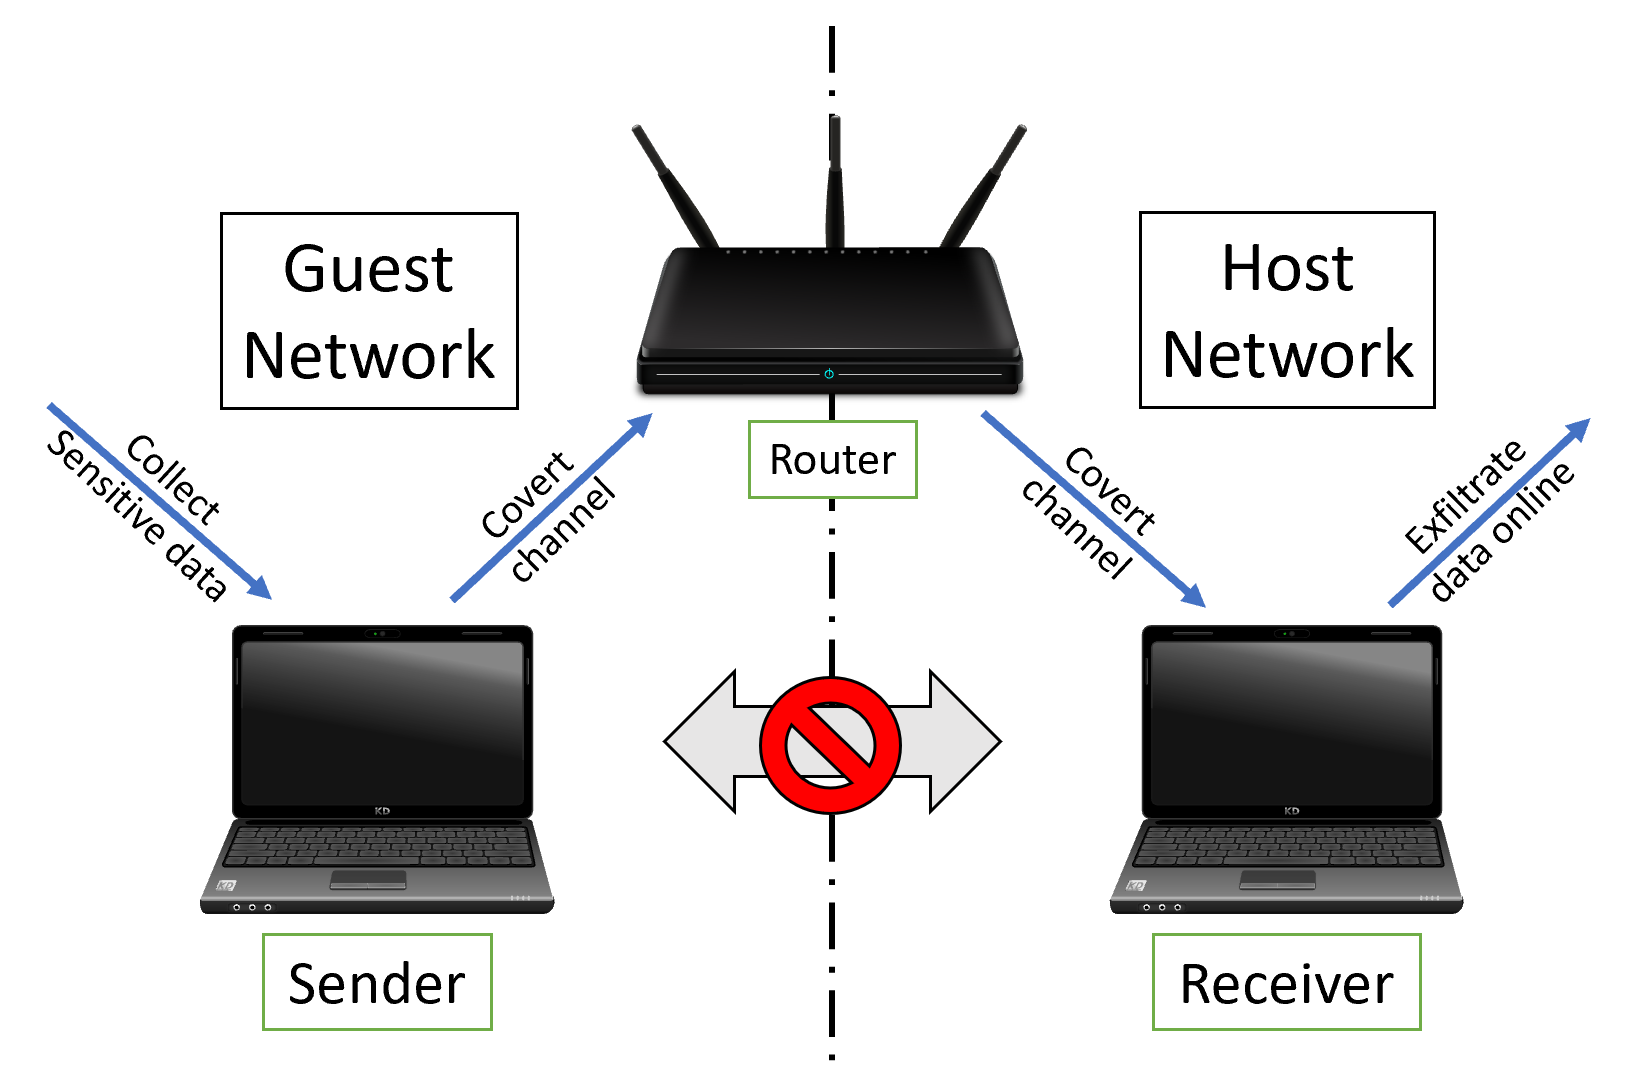
This repository includes the source code used in the "Characterization and Detection of Cross-Router Covert Channels" paper.

Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.

The StackRox Kubernetes Security Platform performs a risk analysis of the container environment, delivers visibility and runtime alerts, and provides…

Advanced Sysmon ATT&CK configuration focusing on Detecting the Most Techniques per Data source in MITRE ATT&CK, Provide Visibility into Forensic…

Ability to detect suspicious activity such as (WEP/WPA/WPS) attack by sniffing the air for wireless packets.

With Wireshark or TCPdump, you can determine whether there is harmful activity on your network traffic that you have recorded on the network you…

This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…

A canary designed to minimize the impact from certain Ransomware actors

3D multi-domain tactical intelligence map — live ships, flights, satellites, cables & space weather in the browser. Time scrubbing, scenario replay,…

The Console Monitor Driver is a KMDF kernel-mode filter driver that captures certain Fast I/O operations (input and output) that is sent to or from…

OSTE WLA automate the process of analyzing web server logs with the Python Web Log Analyzer.

A Zeek package for the passive detection of "Ripple20" vulnerabilities in the Treck TCP/IP stack.

Research related to the Power Tracks discovered in market microstructure.

The Whale Sentinel Services

Enrich the conn.log with EDR data

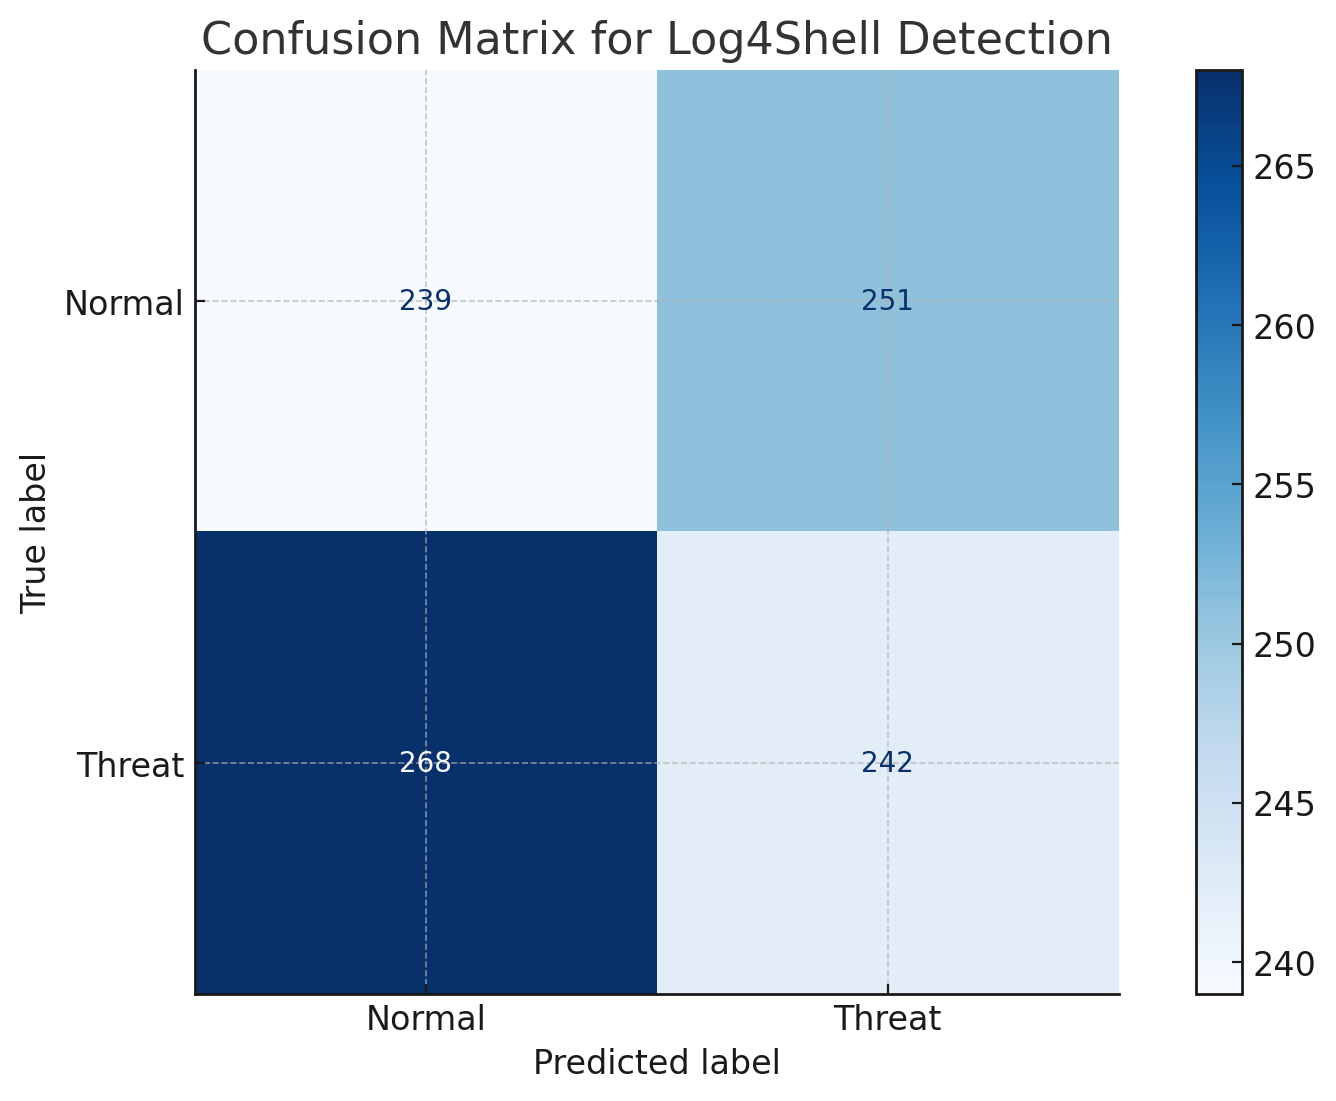
This repository provides an in-depth analysis of the Log4Shell vulnerability (CVE-2021-44228) and implements a machine learning-based approach to…