
reactor
 nccgroup/reactor
Runs custom filters on Elasticsearch and alerts on matches
anomaly-detectiondefensive-toolsincident-response+2
nccgroup/reactorRuns custom filters on Elasticsearch and alerts on matches
 trustedsec/artillery
Open-source blue team tool that protects Linux and Windows systems using multiple host and network defense and detection methods.
 silverfort-open-source/latma
Collects and analyzes AD and Azure AD authentication logs to detect lateral movement attacks using graph-based anomaly detection, visualizing…
 nccgroup/impossibletravelloganalysis
Basic log analysis tool to detect impossible travel via IP address geographic information
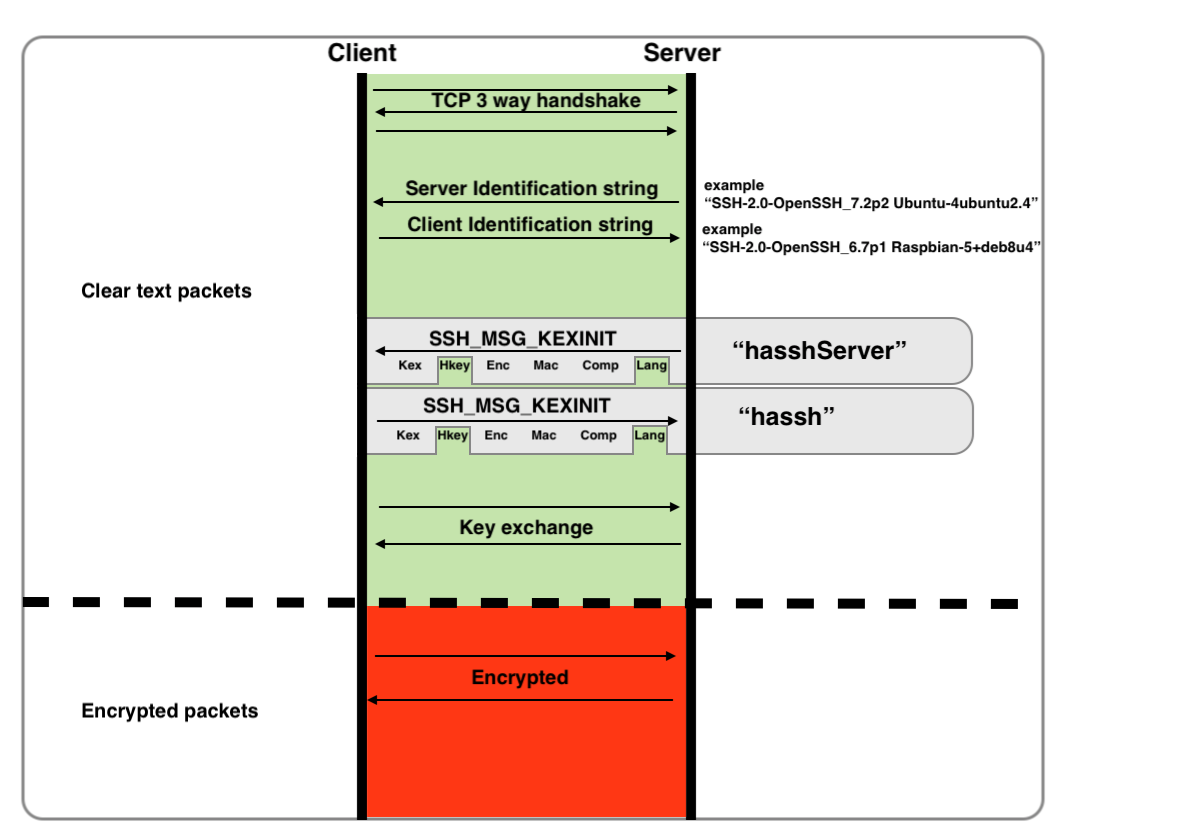 corelight/hassh
Fingerprint SSH clients and servers.