

dns_watchdog_windows2
 microlaser/dns_watchdog_windows2
PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…
anomaly-detectiondefensive-toolsdns-analysis+5
microlaser/dns_watchdog_windows2PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…
 cbuijs/sdproxy
DNS Proxy that is simple and fast with not so simple features. Focused on routed DNS forwarding, filtering and parental control.
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 corelight/zeek-spicy-ospf
A Zeek OSPF packet analyzer based on Spicy.
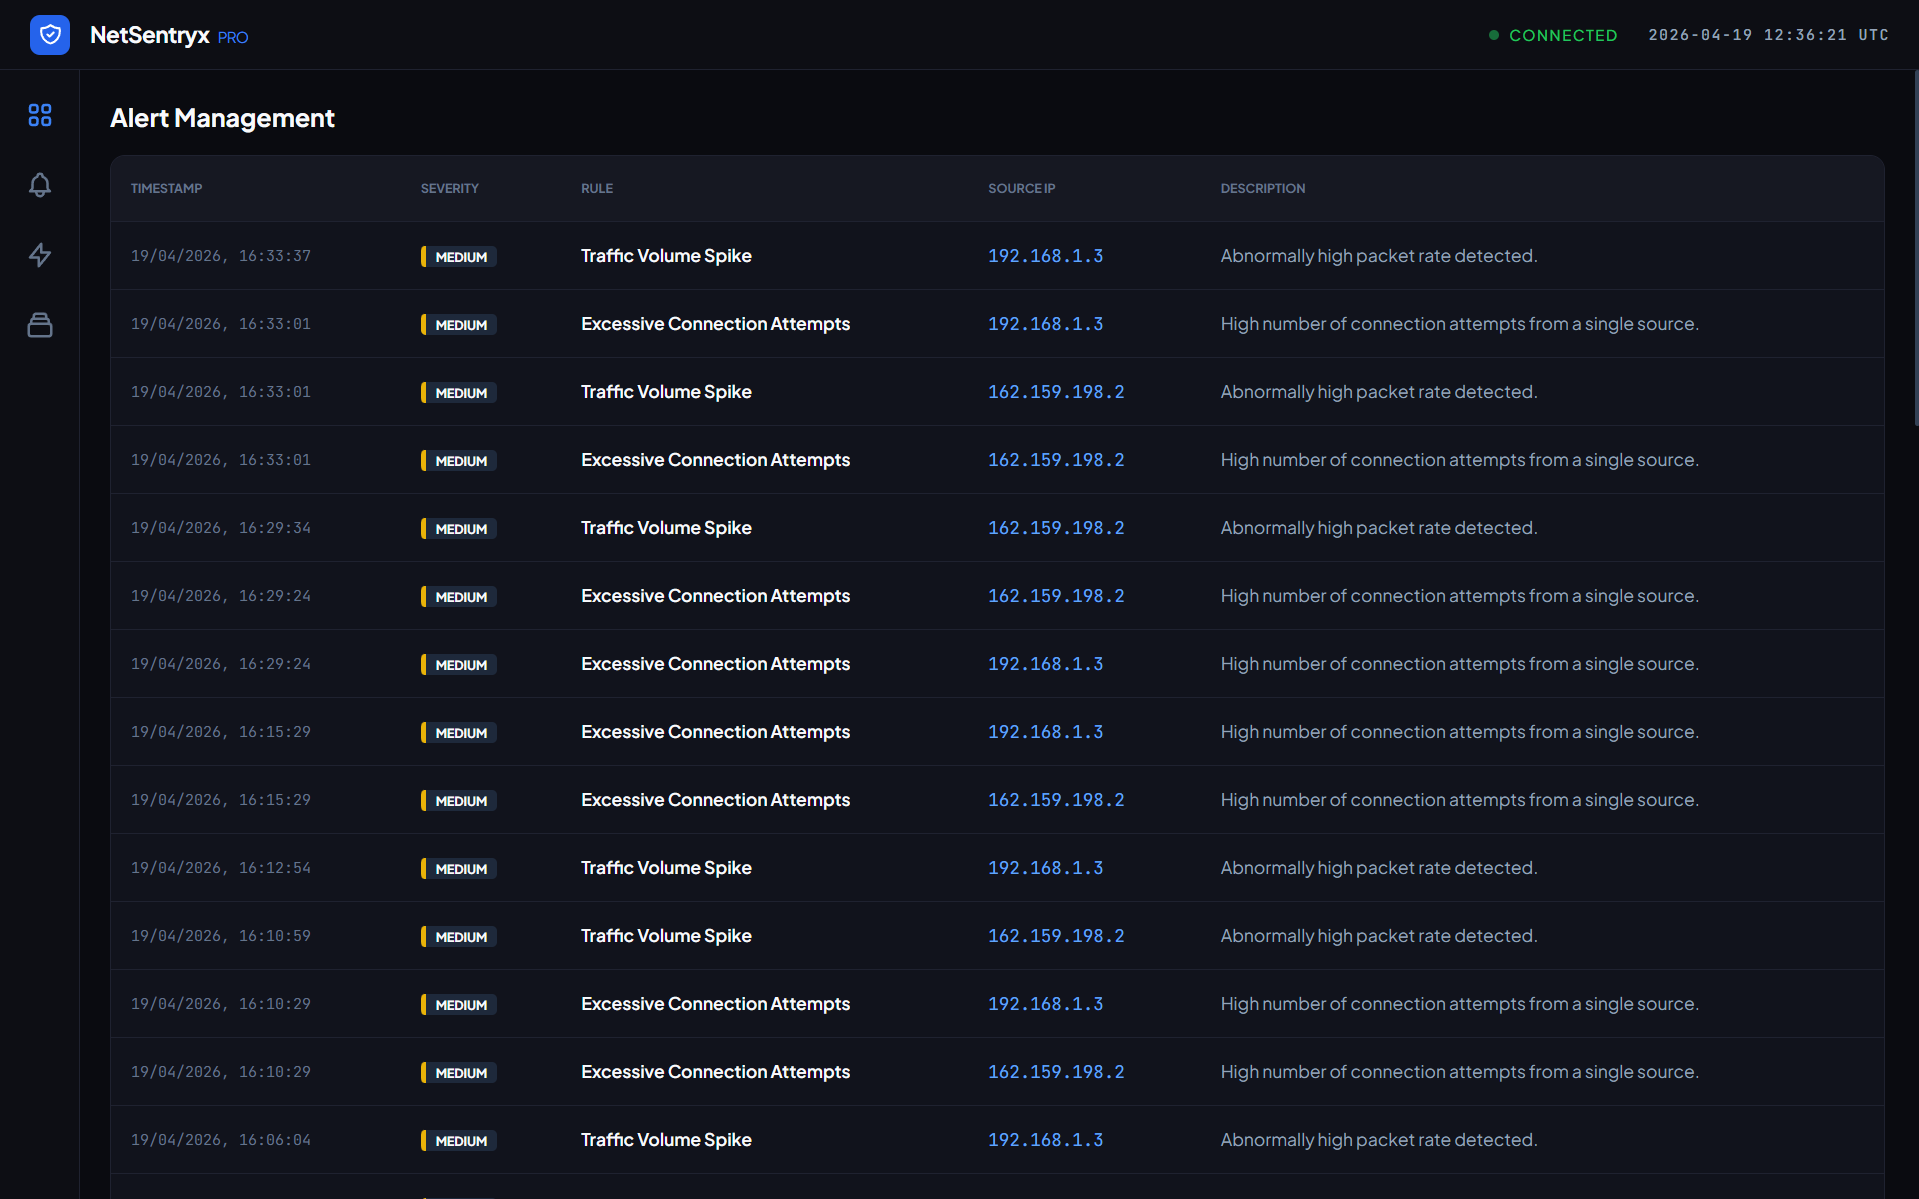 aman-sharma-dev/netsentryx
An event-driven network monitoring platform that performs live packet capture (Npcap), low-latency traffic analytics, and unsupervised threat…
 siddharth2440/network-detection-engine
Lightweight network intrusion detection engine capturing live traffic with libpcap. Detects SYN/ICMP floods, port scans, and signature-based web…
 cisco/joy
A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.
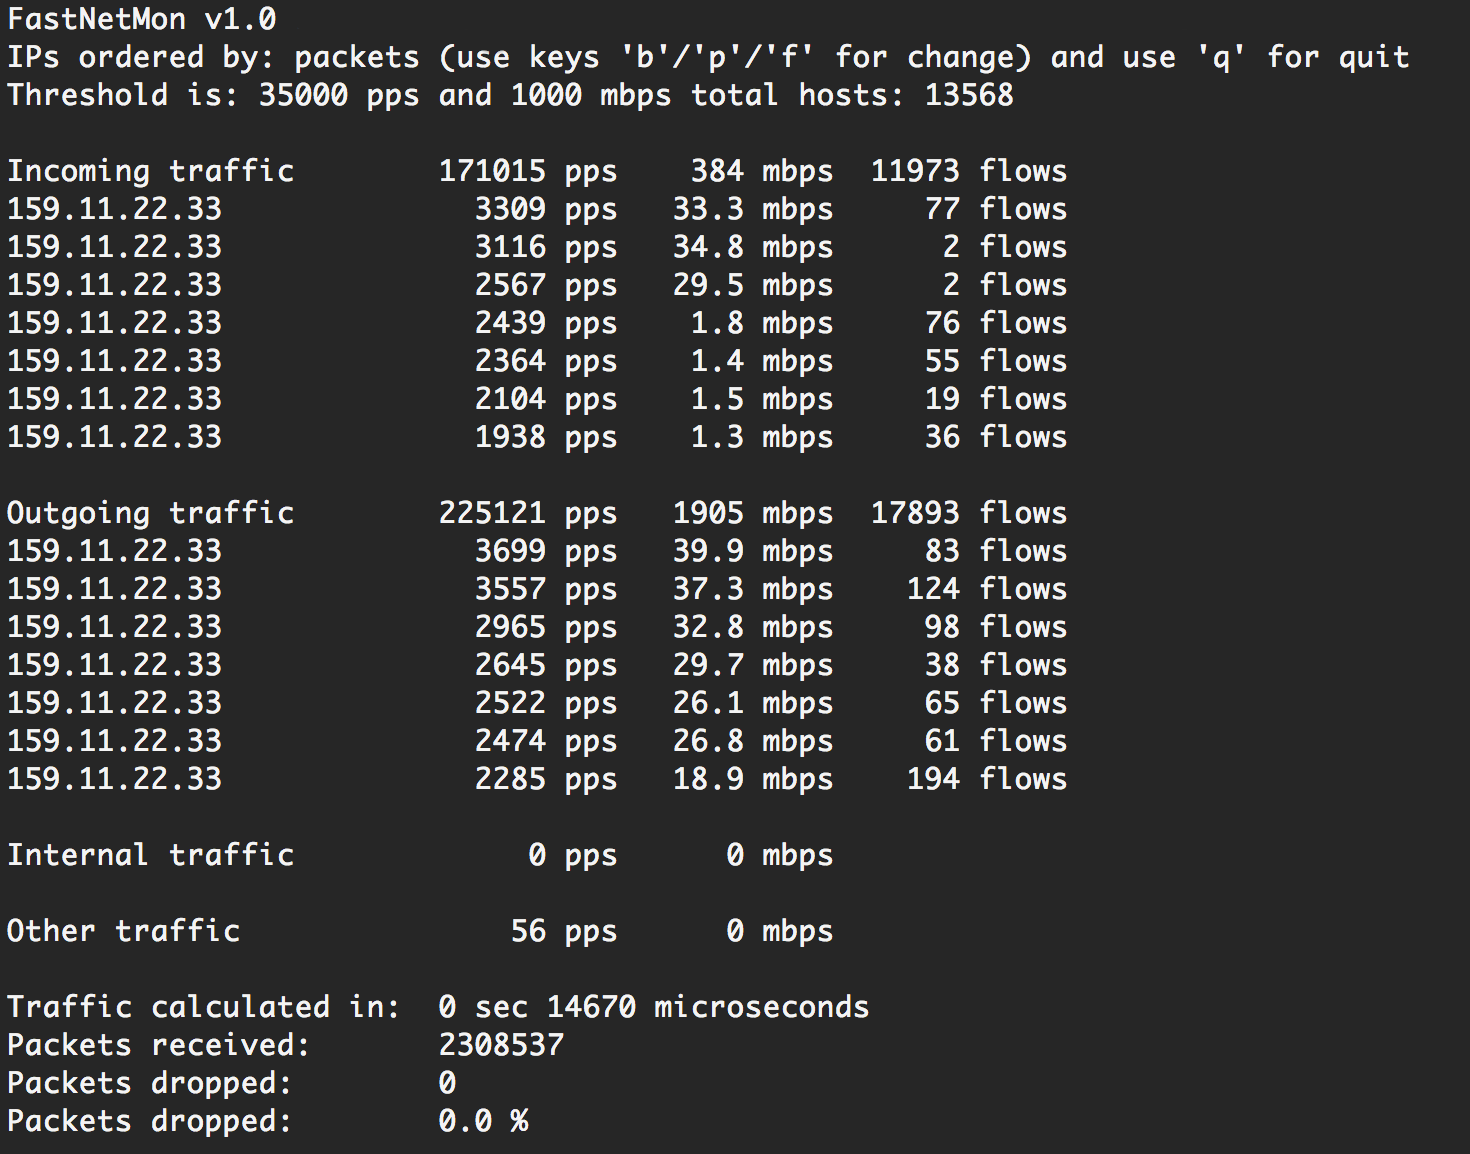 pavel-odintsov/fastnetmon
Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support
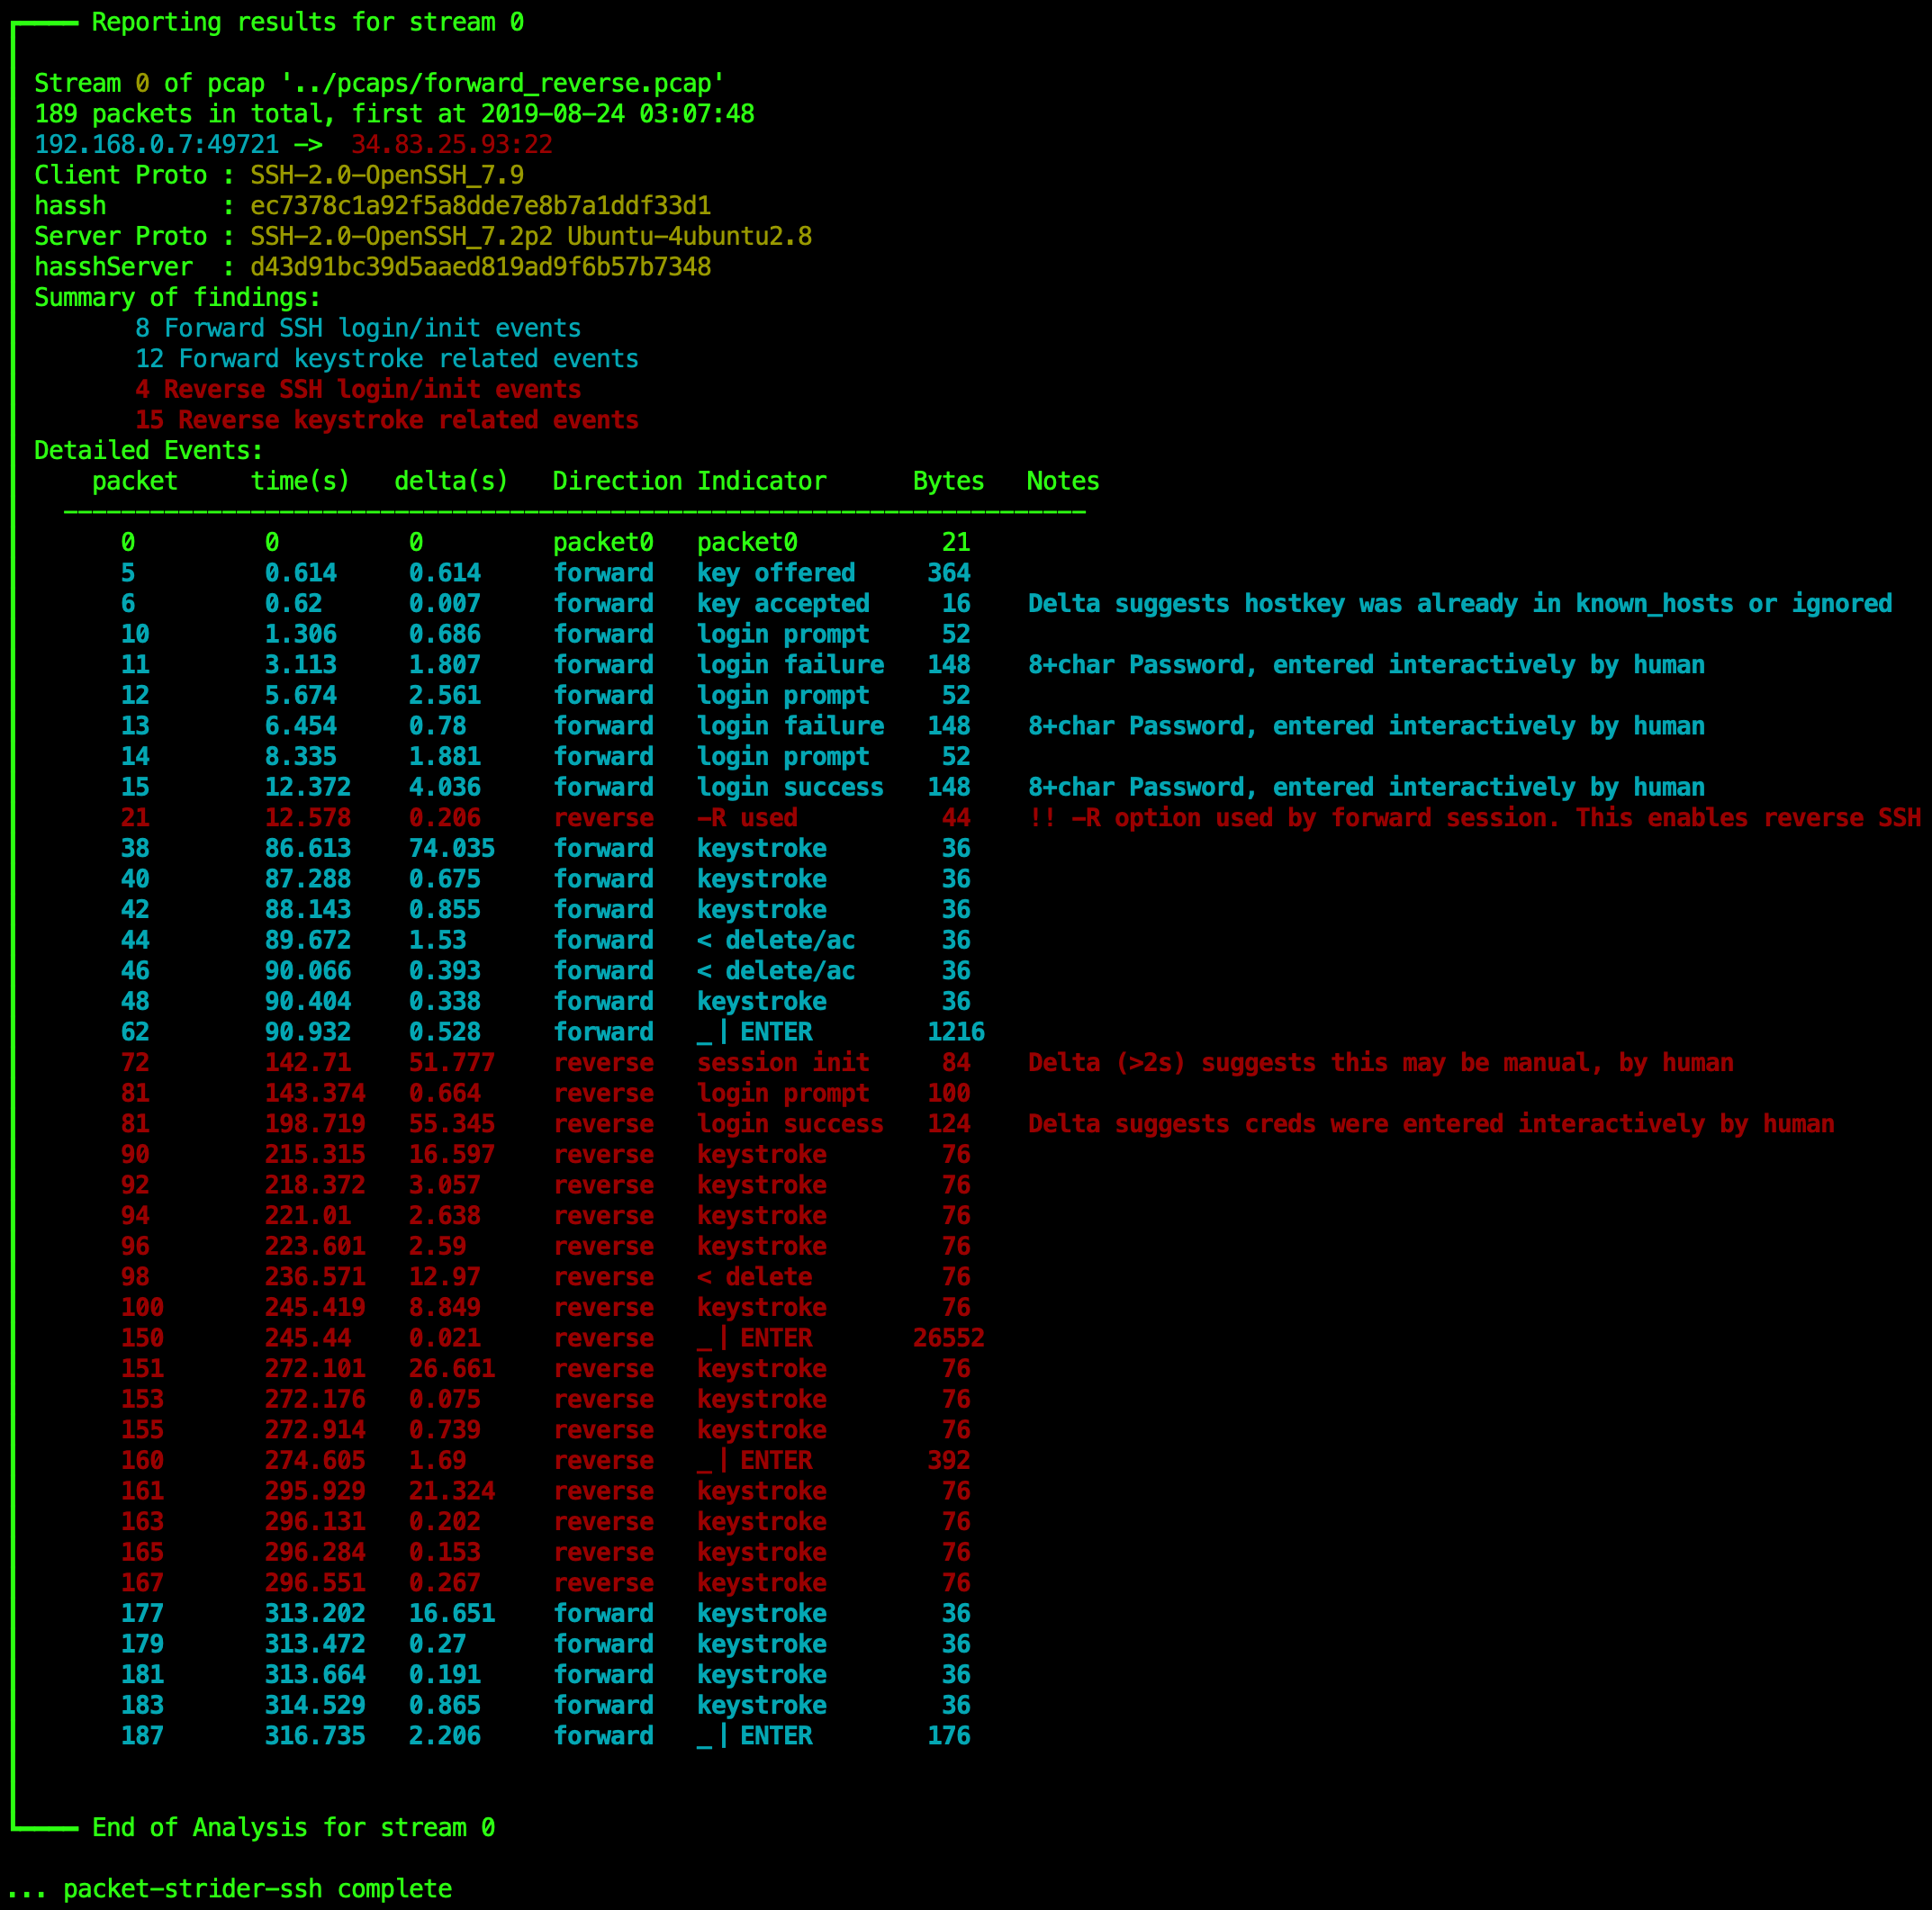 benjeems/packetstrider
A network packet forensics tool for SSH
 camp0/aiengine
Programmable packet inspection engine with NIDS, DNS classification, frequency analysis, and auto-regex generation. Supports Python/Ruby/Java/Lua…
 alperenugurlu/network_assessment
With Wireshark or TCPdump, you can determine whether there is harmful activity on your network traffic that you have recorded on the network you…