


 ion-storm/sysmon-config
Advanced Sysmon ATT&CK configuration focusing on Detecting the Most Techniques per Data source in MITRE ATT&CK, Provide Visibility into Forensic…
 nate-ryan-7690/home_soc_suite
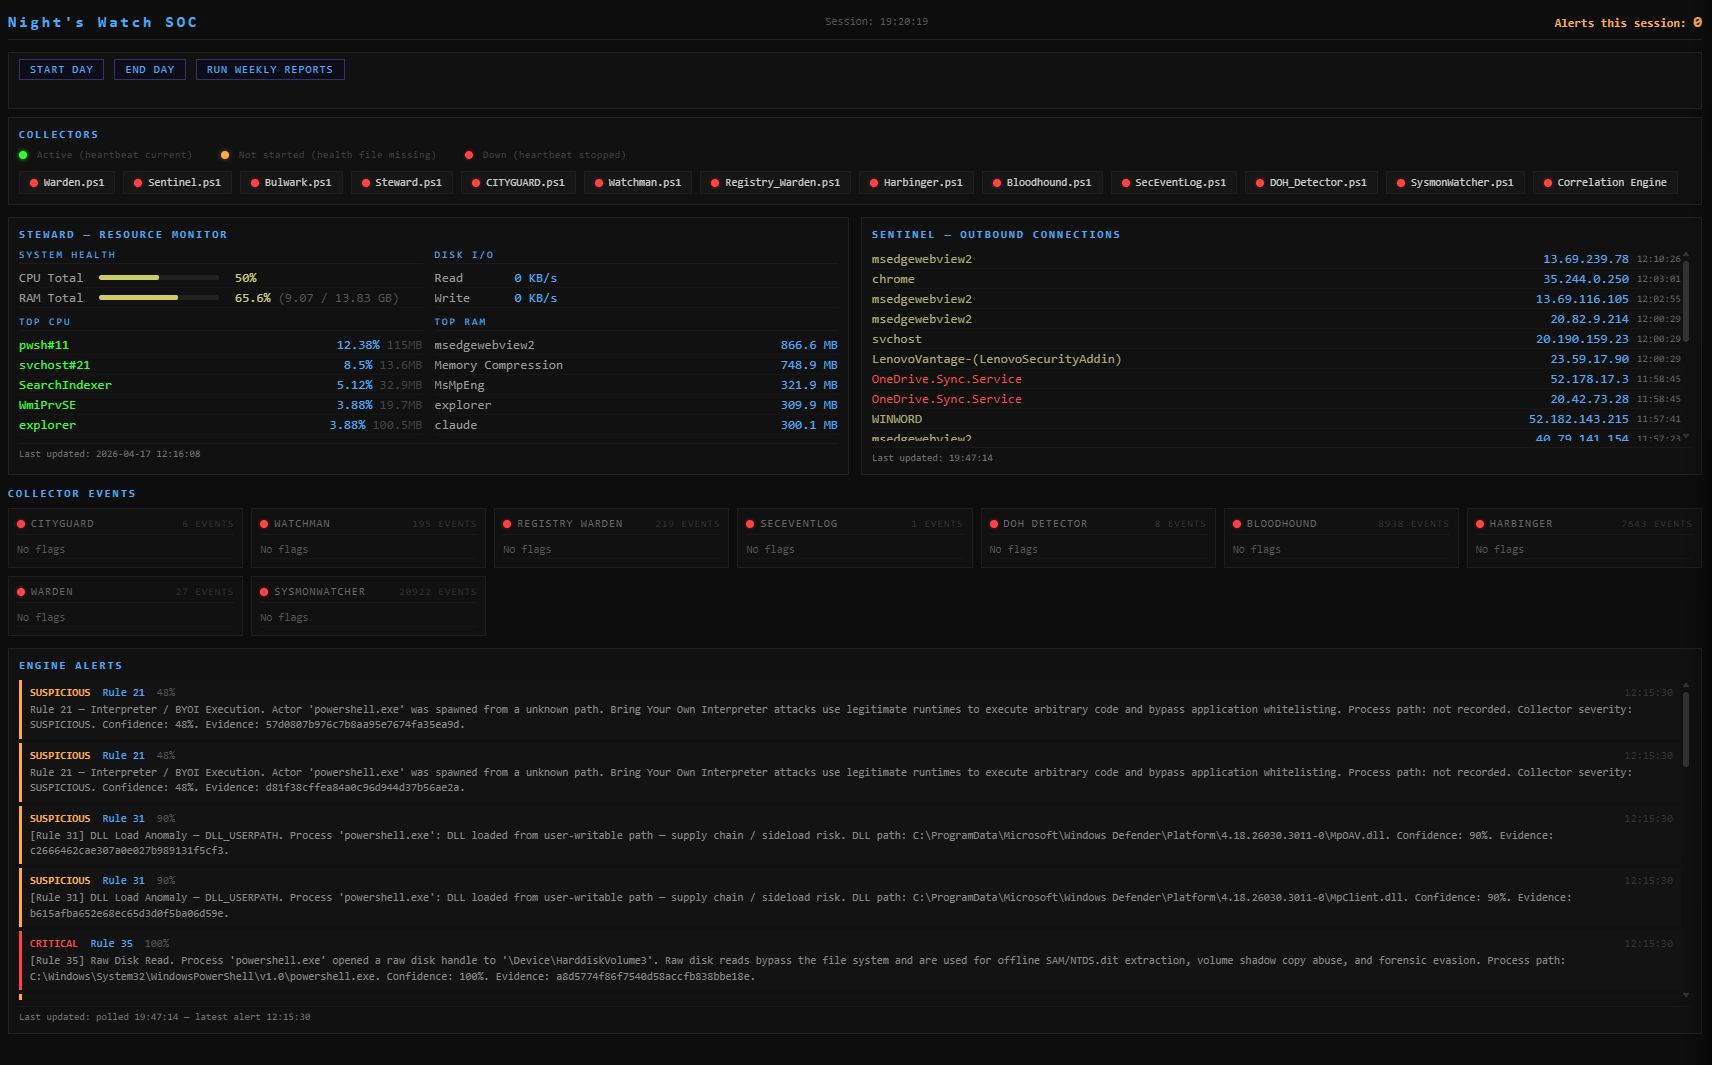
A personal Windows SOC suite built in PowerShell — monitors network connections, resource usage, scheduled tasks and power events with severity…
 theflink/hunt-weird-imageloads
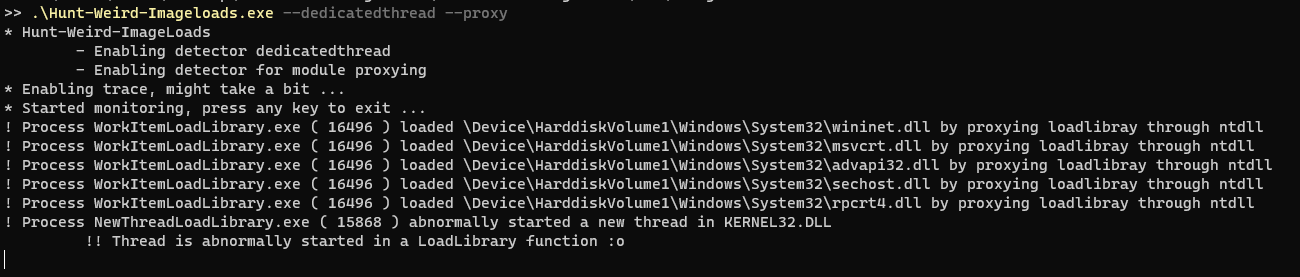
Small tool to play with IOCs caused by Imageload events
 asngs/agenttriage-open-source
Cross-agent tracing and security-diagnosis system for tool-using LLM agents: normalizes trace events, builds provenance graphs, extracts…