

rita
 activecm/rita
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
anomaly-detectioncommand-and-controldns-analysis+4
644
activecm/ritaReal Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
 travisbgreen/hunting-rules
Suricata rules for network anomaly detection
 cbuijs/sdproxy
DNS Proxy that is simple and fast with not so simple features. Focused on routed DNS forwarding, filtering and parental control.
 mahdi13830510/cve-2026-31431-mitigation-suite
Kernel-runtime defense framework for AF_ALG vulnerabilities, featuring eBPF socket tracing, Ansible hardening, and a crypto auditor for drift…
 corelight/zeek-asyncrat-detector
A Zeek based AsyncRAT malware detector.
 leitwacht/leitwacht
Leitwacht control plane — runtime security for GitLab Runner CI/CD: policy authoring, multi-tenancy, audit, GitLab integration
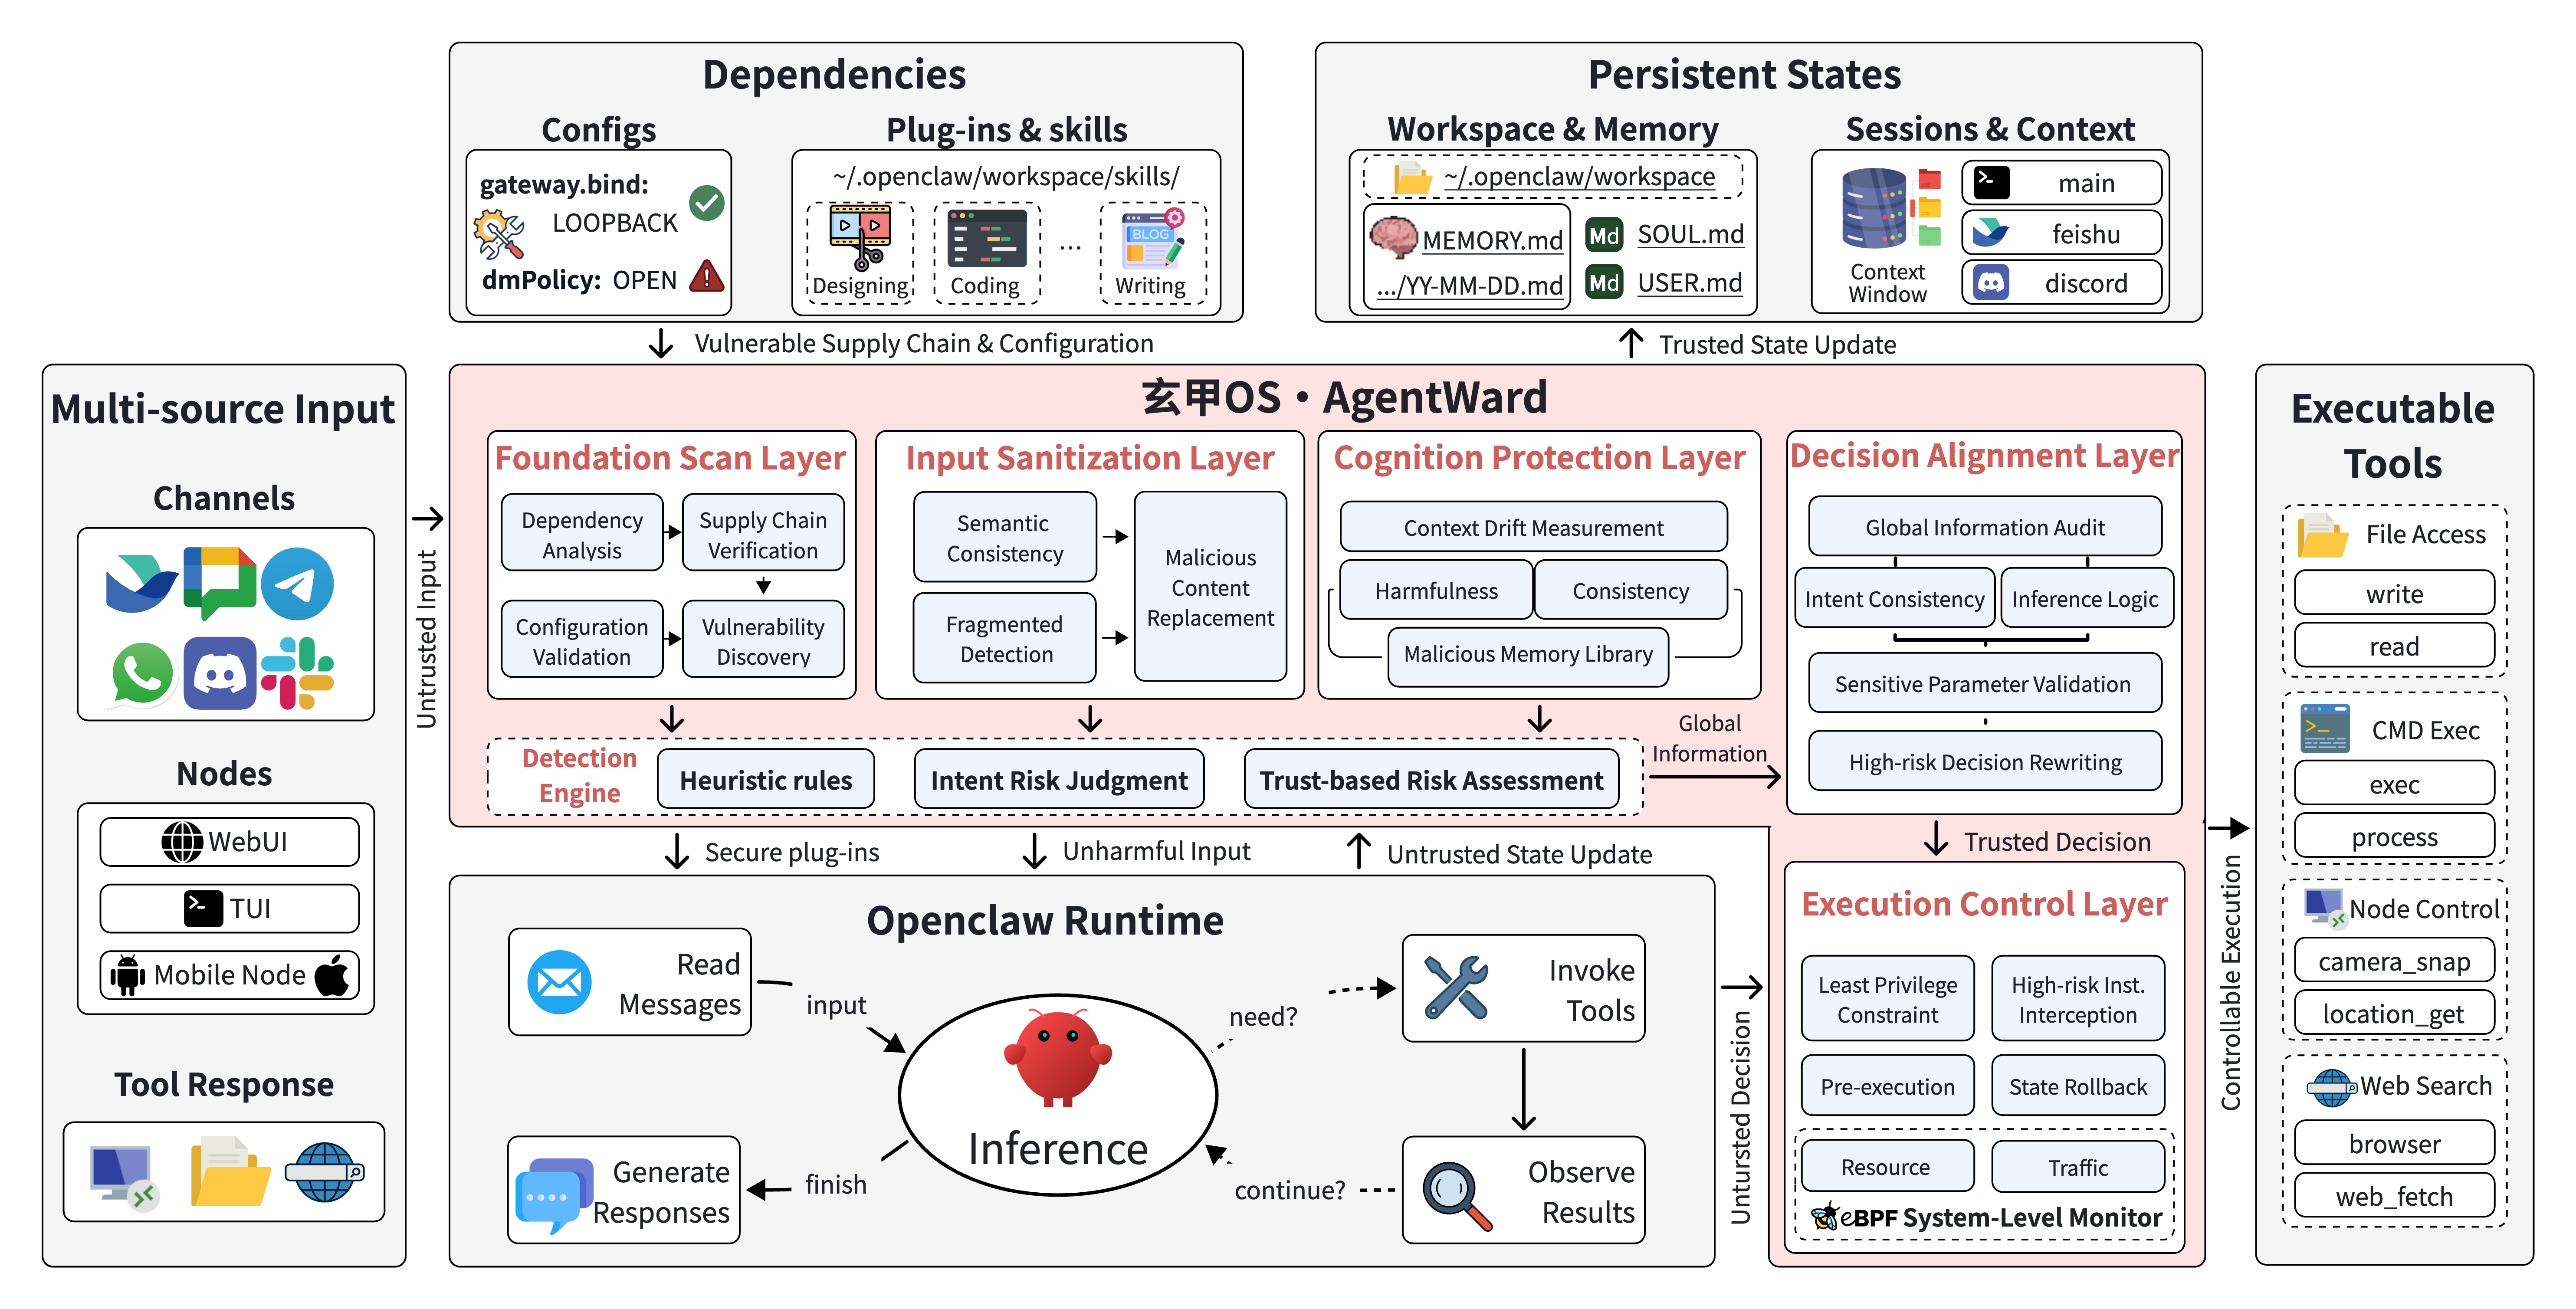 find-lab/agentward
Full-stack security OS for AI agents with five-layer defense-in-depth architecture covering foundation scan, input sanitization, cognition…
 dereeqw/berrysentinel
Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…
 baidu/openrasp
Runtime application self-protection engine that hooks into application servers to monitor and block malicious database queries, file operations, and…
 corelight/zeek-caldera-detector
A Zeek based Mitre Caldera detector.
 malwaremorghulis/sunburst
Detection for SUNBURST C2 Stage-1 using Shannon Entropy
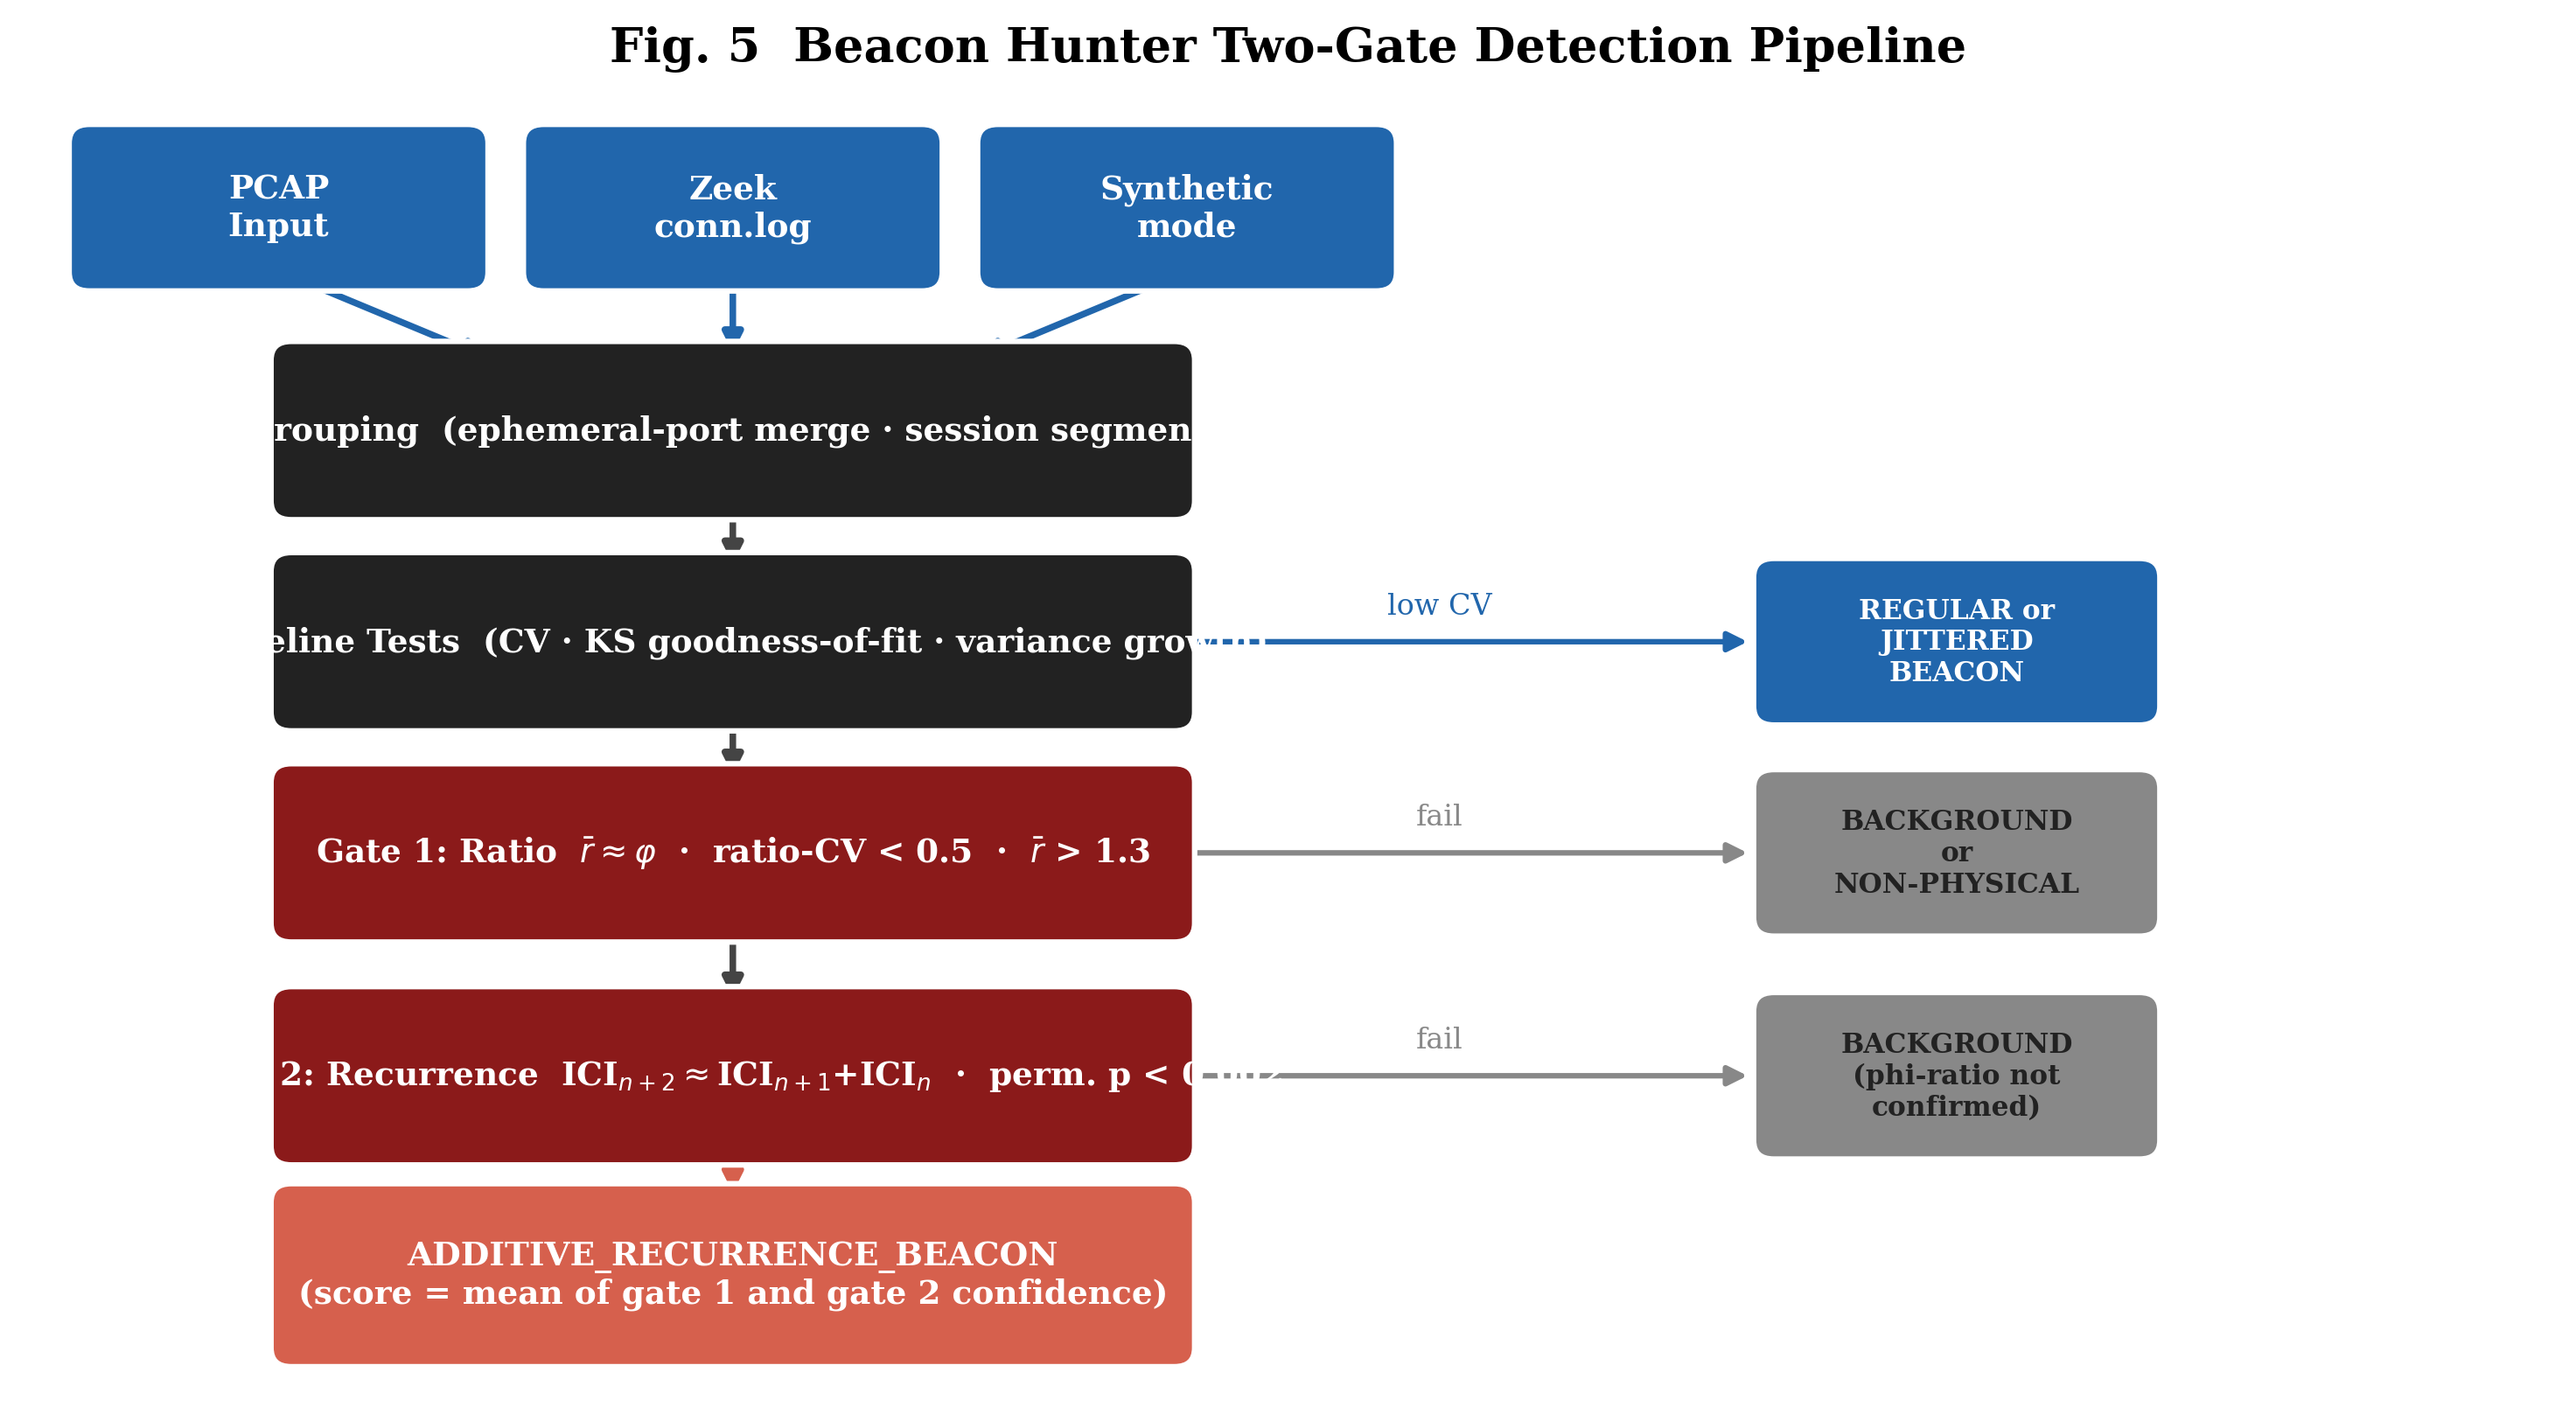 mrcord77/beacon-hunter
Detects phi-structured C2 beacons that evade RITA and standard regularity-based detectors
 corelight/zeek-quasarrat-detector
Zeek detector for QuasarRat