

Loki
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
anomaly-detectiondigital-forensicsdisk-forensics+11
3.8k
neo23x0/lokiIOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
 microlaser/dns_watchdog_windows2
PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…
 stumpy-dev/stumpy
Scalable Python library for time series analysis via matrix profiles, enabling motif discovery, anomaly detection, semantic segmentation, and…
 beenuar/aisoc
Self-hostable AI SOC that fuses security alerts, auto-triages via agentic AI, runs MITRE ATT&CK investigations, and logs every agent decision in a…
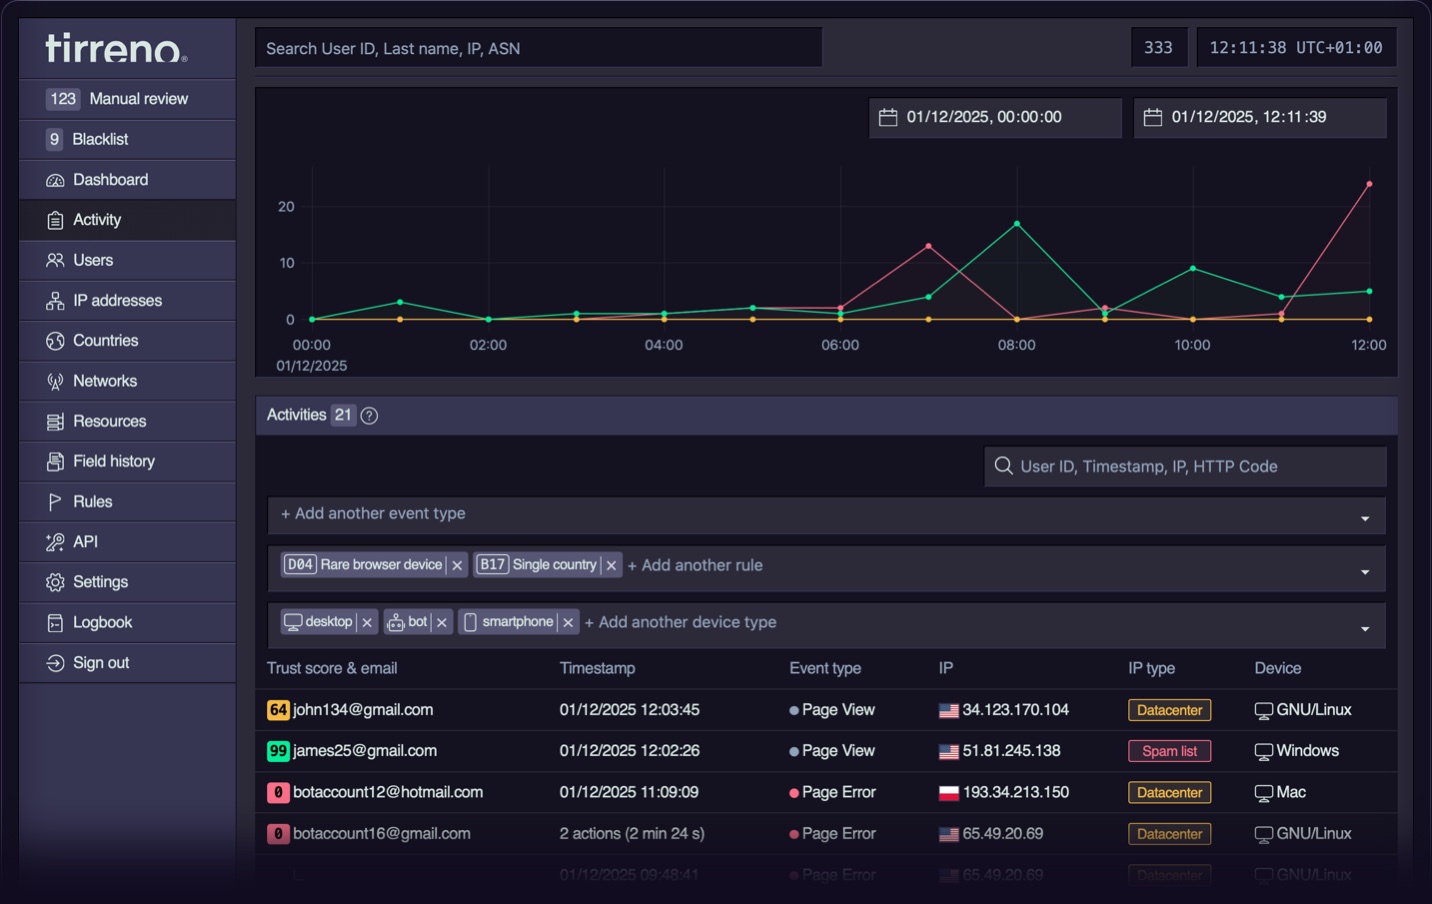 tirrenotechnologies/tirreno
Open-source security framework for real-time event tracking, threat detection, and risk scoring. Monitors user behavior, detects fraud, bot attacks,…
 owasp/intrusion-alert-educational-network-ids
Lightweight Python-based IDS that monitors network traffic in real-time using Scapy, detecting DoS/DDoS attacks via per-IP request rate analysis with…
 ang13t/dronextract
Digital forensics suite for DJI drones that parses telemetry files, extracts hidden data via steganography, visualizes flight paths, and detects…
 amavis/amavis
amavis is a high-performance email content filter framework written in Perl.
 safeagent-beihang/clawguard
Enterprise AI agent security toolkit providing pre-flight auditing, configuration hardening, runtime threat detection, and active defense against…
 vedantk6403/koobe-guard
Linux kernel module using Kprobes to detect and neutralize CVE-2024-1086 heap double-free exploits via temporal gap tracking and active register…
 aniketkarne/aco-prompt-shield
Stop prompt injection attacks before they reach your LLM — zero API costs, runs entirely locally, integrates in 2 minutes. Prompt injection is the…
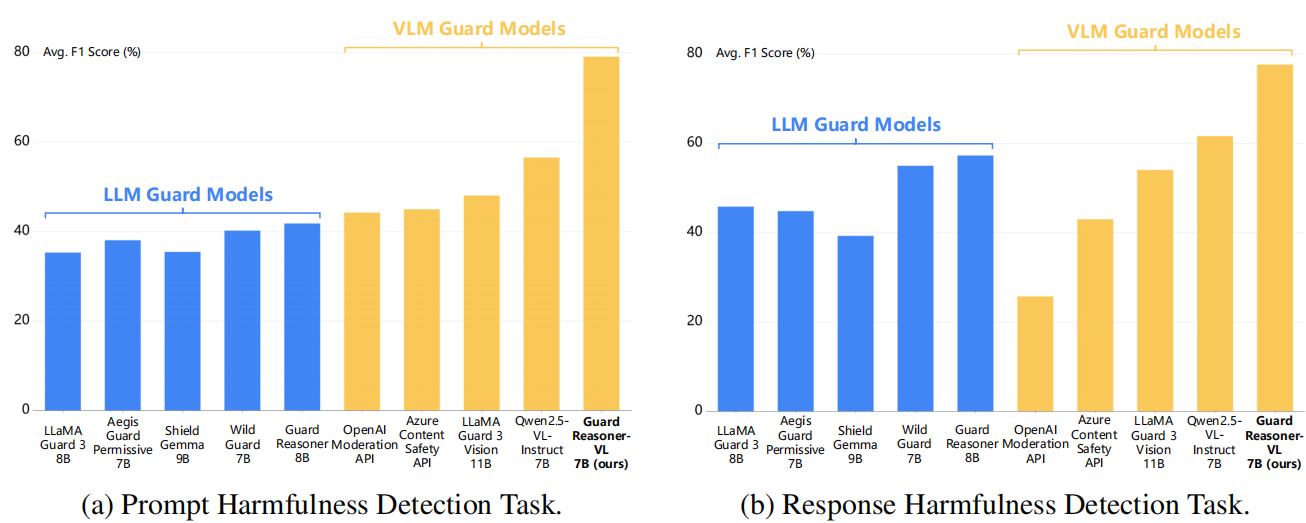 yueliu1999/guardreasoner-vl
[NeurIPS 2025] An official source code for paper "GuardReasoner-VL: Safeguarding VLMs via Reinforced Reasoning".
 corelight/petitpotam
Detects NTLM relay attacks via PetitPotam exploit using Zeek, distinguishing successful and unsuccessful attempts by analyzing DCERPC return codes.
 nccgroup/impossibletravelloganalysis
Basic log analysis tool to detect impossible travel via IP address geographic information
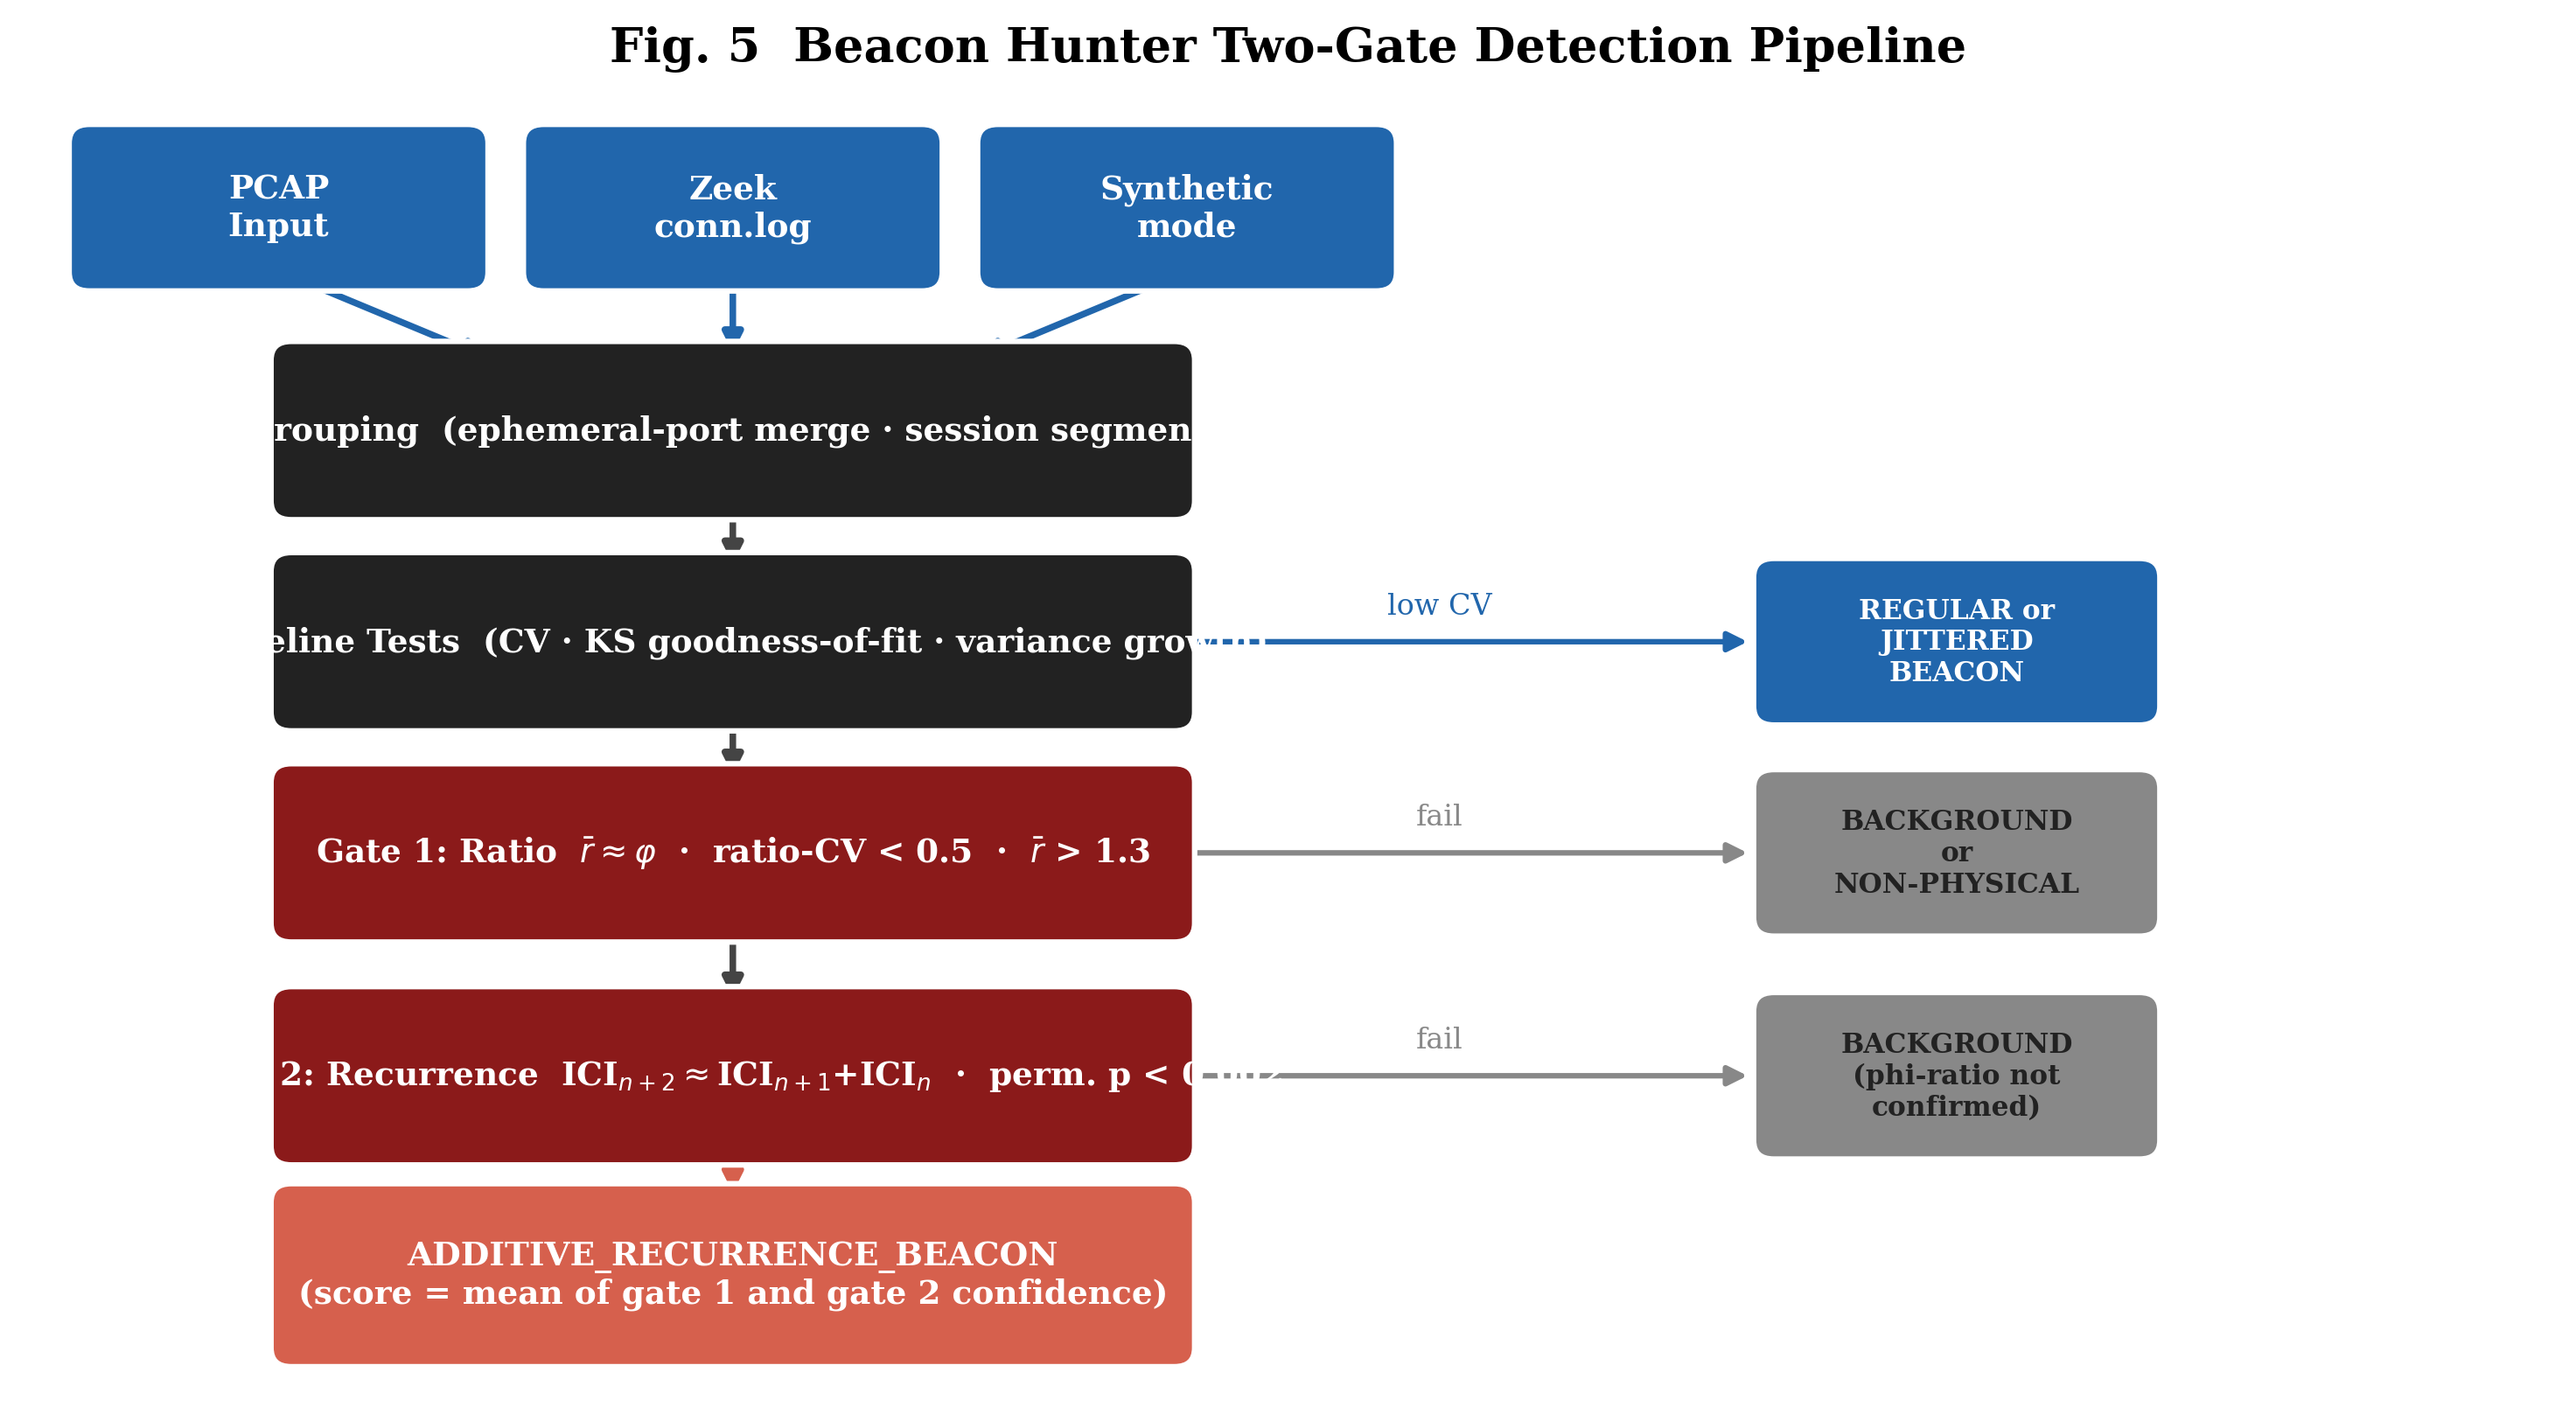 mrcord77/beacon-hunter
Detects phi-structured C2 beacons that evade RITA and standard regularity-based detectors
 jepsen-io/duckdb
Jepsen-based transactional correctness testing framework for DuckDB, detecting isolation anomalies like G2-item and SSI violations via randomized…
 ztsprofessionalaiid7-alt/prompt-injection-firewall
Two-layer LLM firewall that blocks prompt-injection inputs via regex rules plus a Gemini classifier, and catches secret or system-prompt leaks in bot…