

joy
 cisco/joy
A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.
anomaly-detectiondigital-forensicsdns-analysis+7
1.4k6 years ago
cisco/joyA package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.
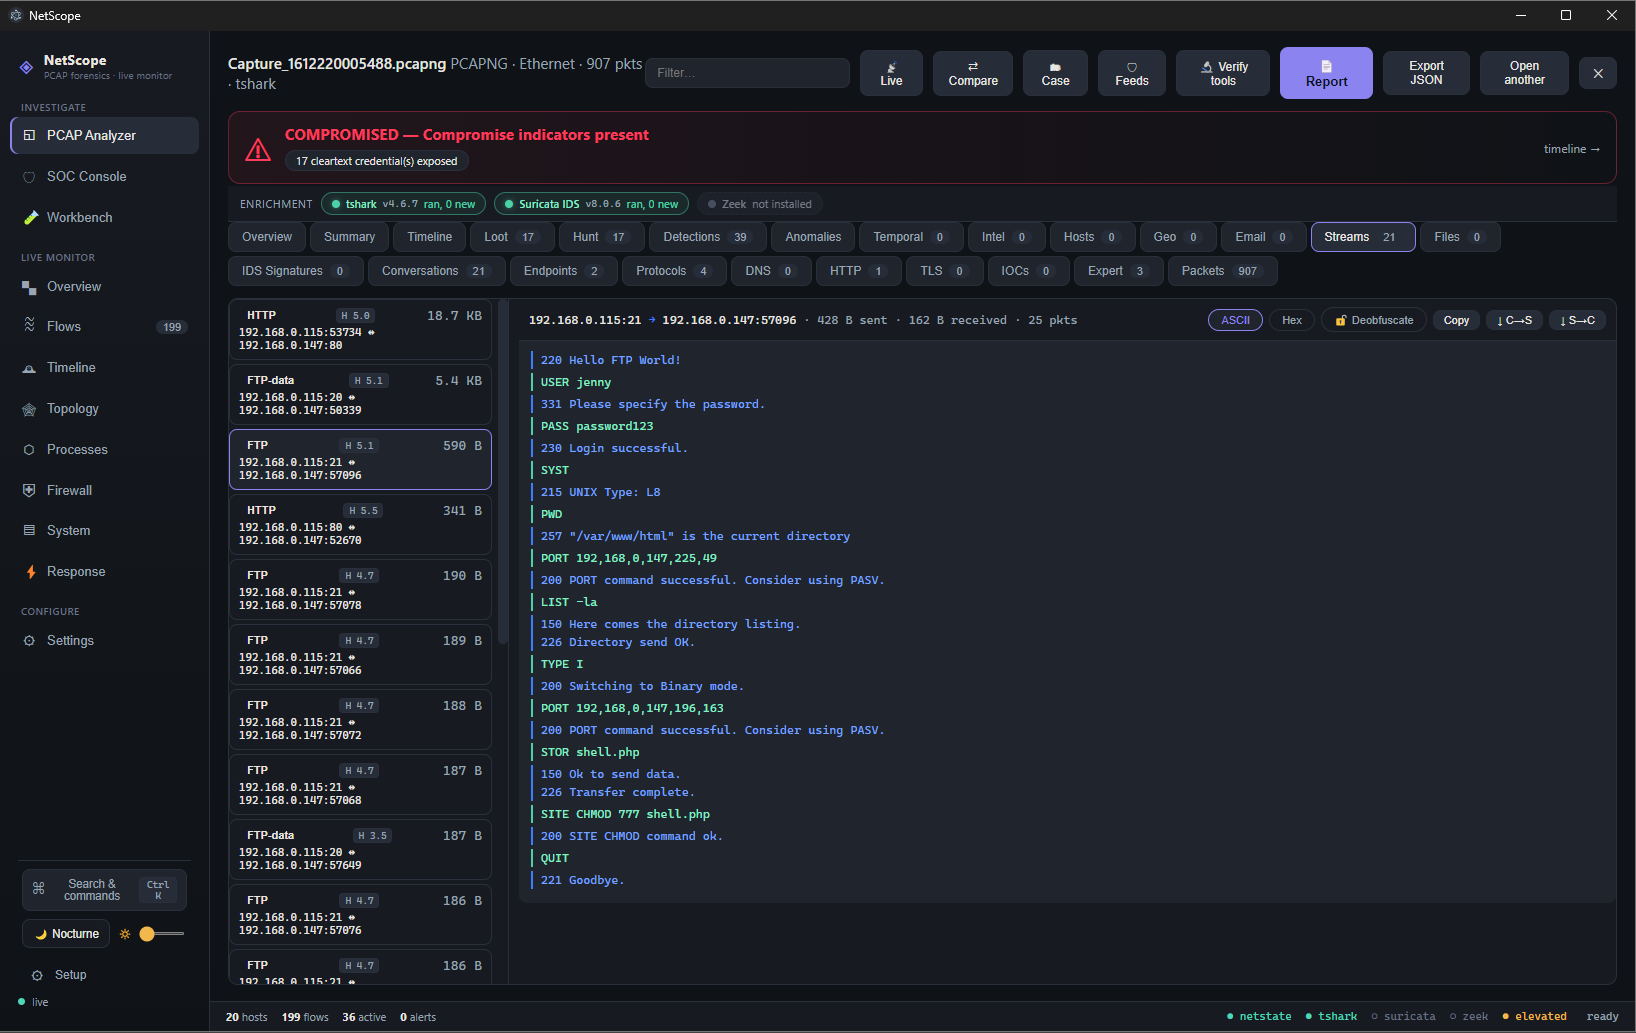 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 puniaze/portdog
Network anomaly detector that monitors raw packets to identify port scanning activity in real time, with flexible sniffing duration controls and live…
 visma-prodsec/columbo
ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…
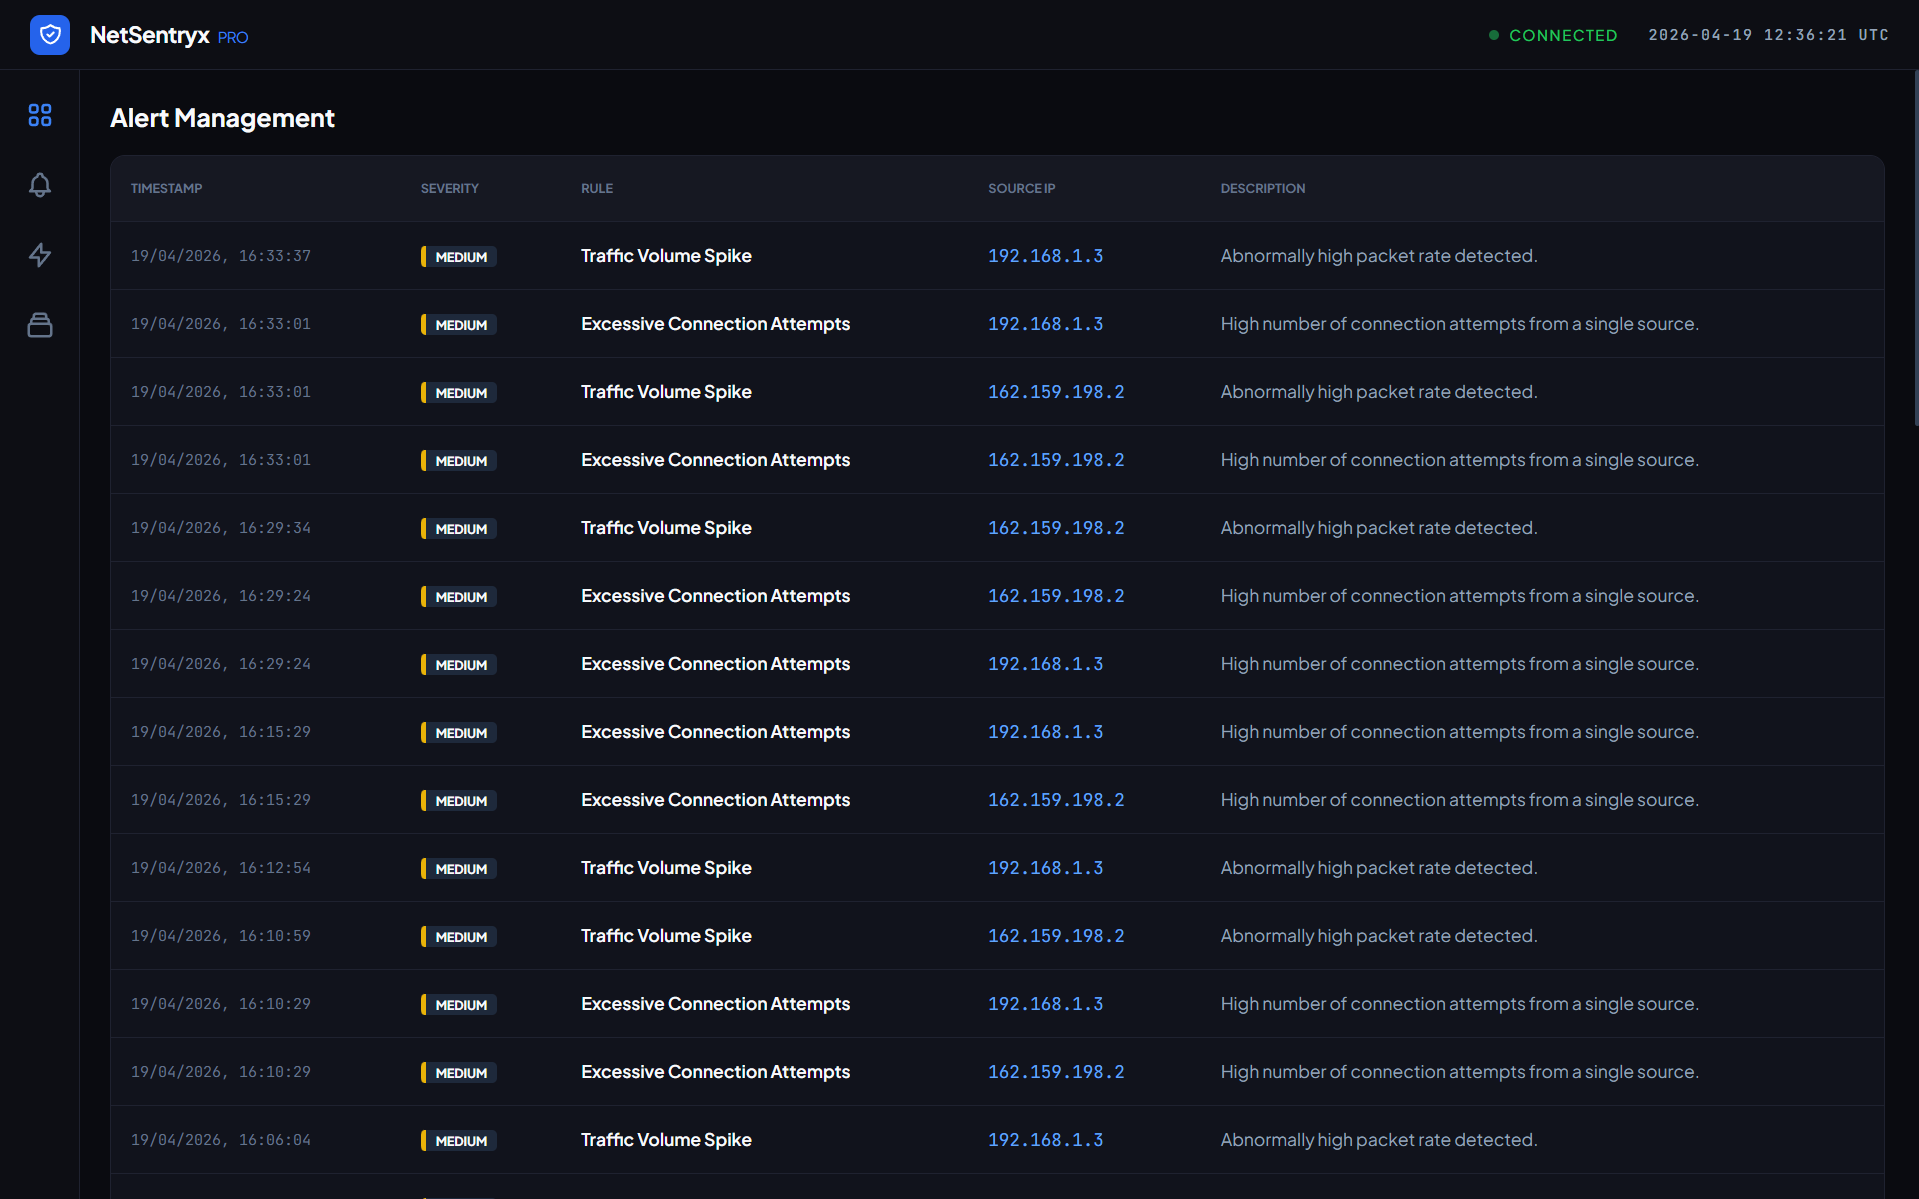 aman-sharma-dev/netsentryx
An event-driven network monitoring platform that performs live packet capture (Npcap), low-latency traffic analytics, and unsupervised threat…
 siddharth2440/network-detection-engine
Lightweight network intrusion detection engine capturing live traffic with libpcap. Detects SYN/ICMP floods, port scans, and signature-based web…
 jamalrfordii-arch/vanguard-map
3D multi-domain tactical intelligence map — live ships, flights, satellites, cables & space weather in the browser. Time scrubbing, scenario replay,…
 1-bit-wonder/kestrel
Single-host runtime-security dashboard on eBPF — Go agent + SvelteKit. Live process tree, network map, and rule-based alerts for plain Linux hosts.