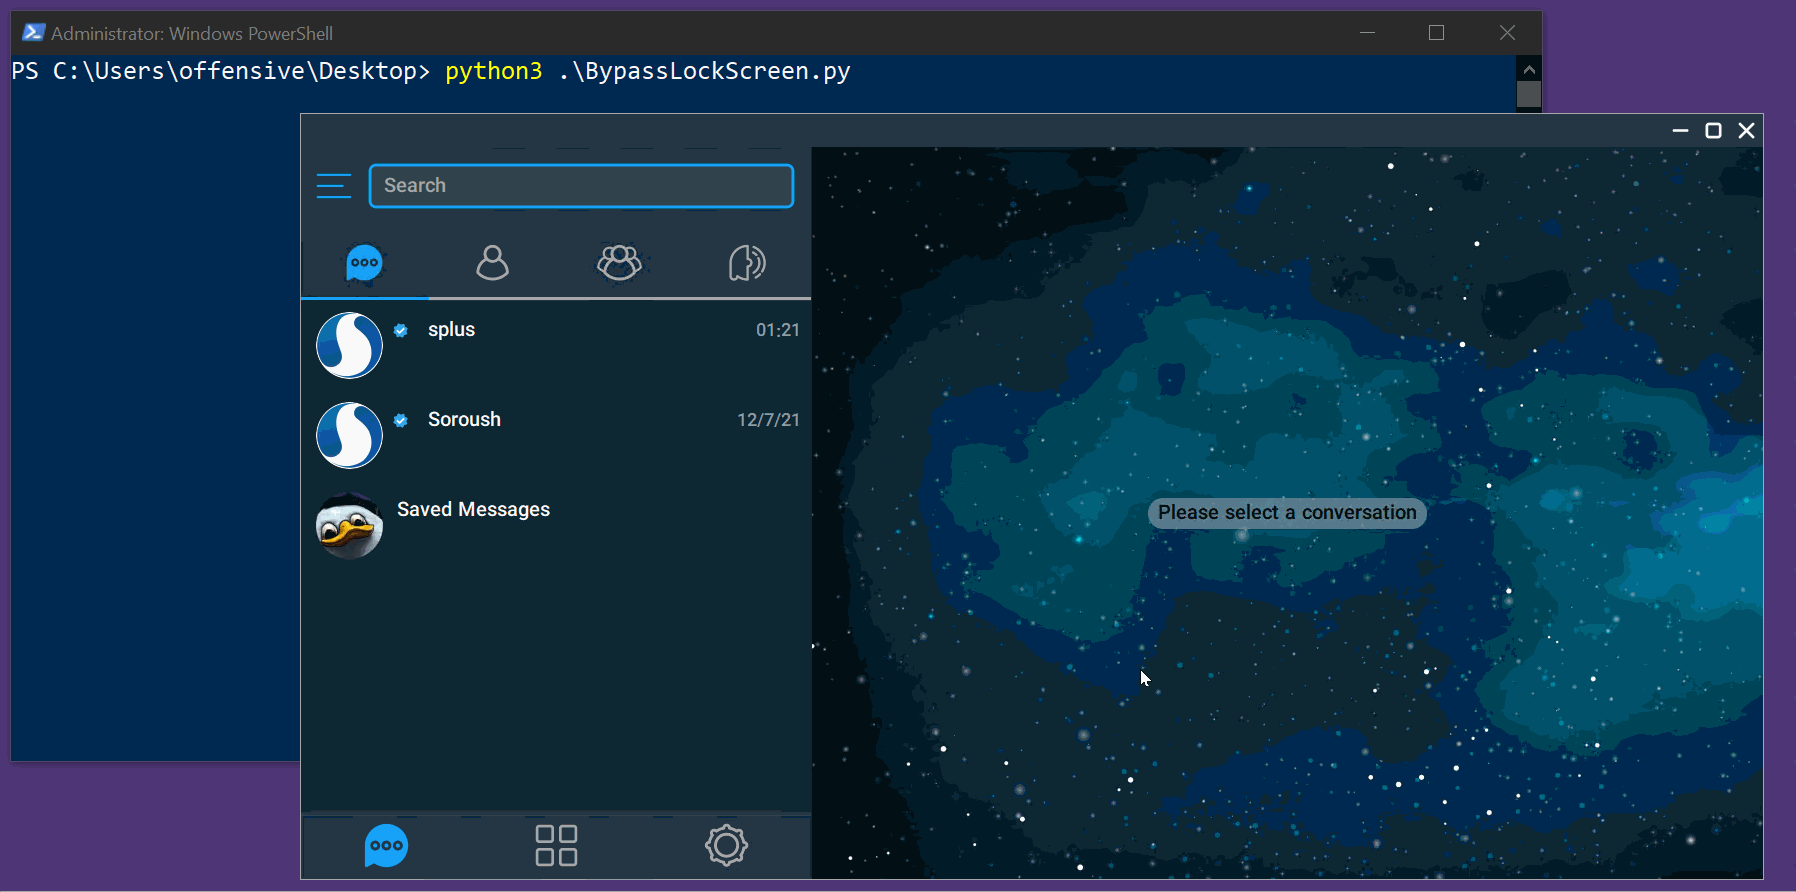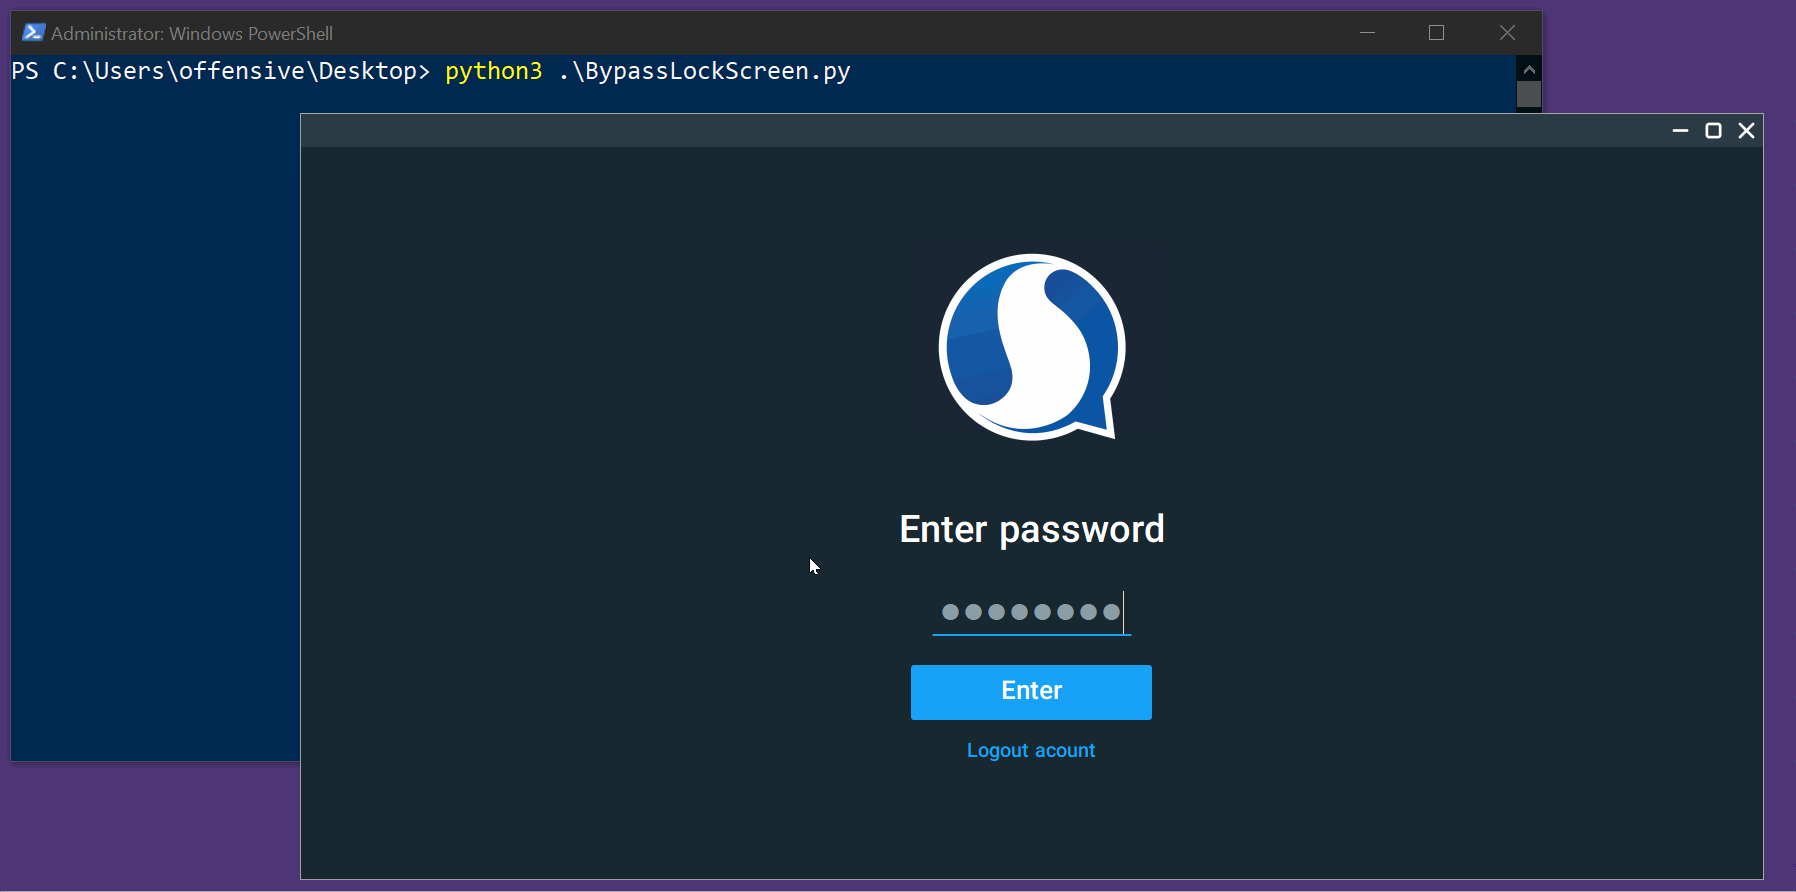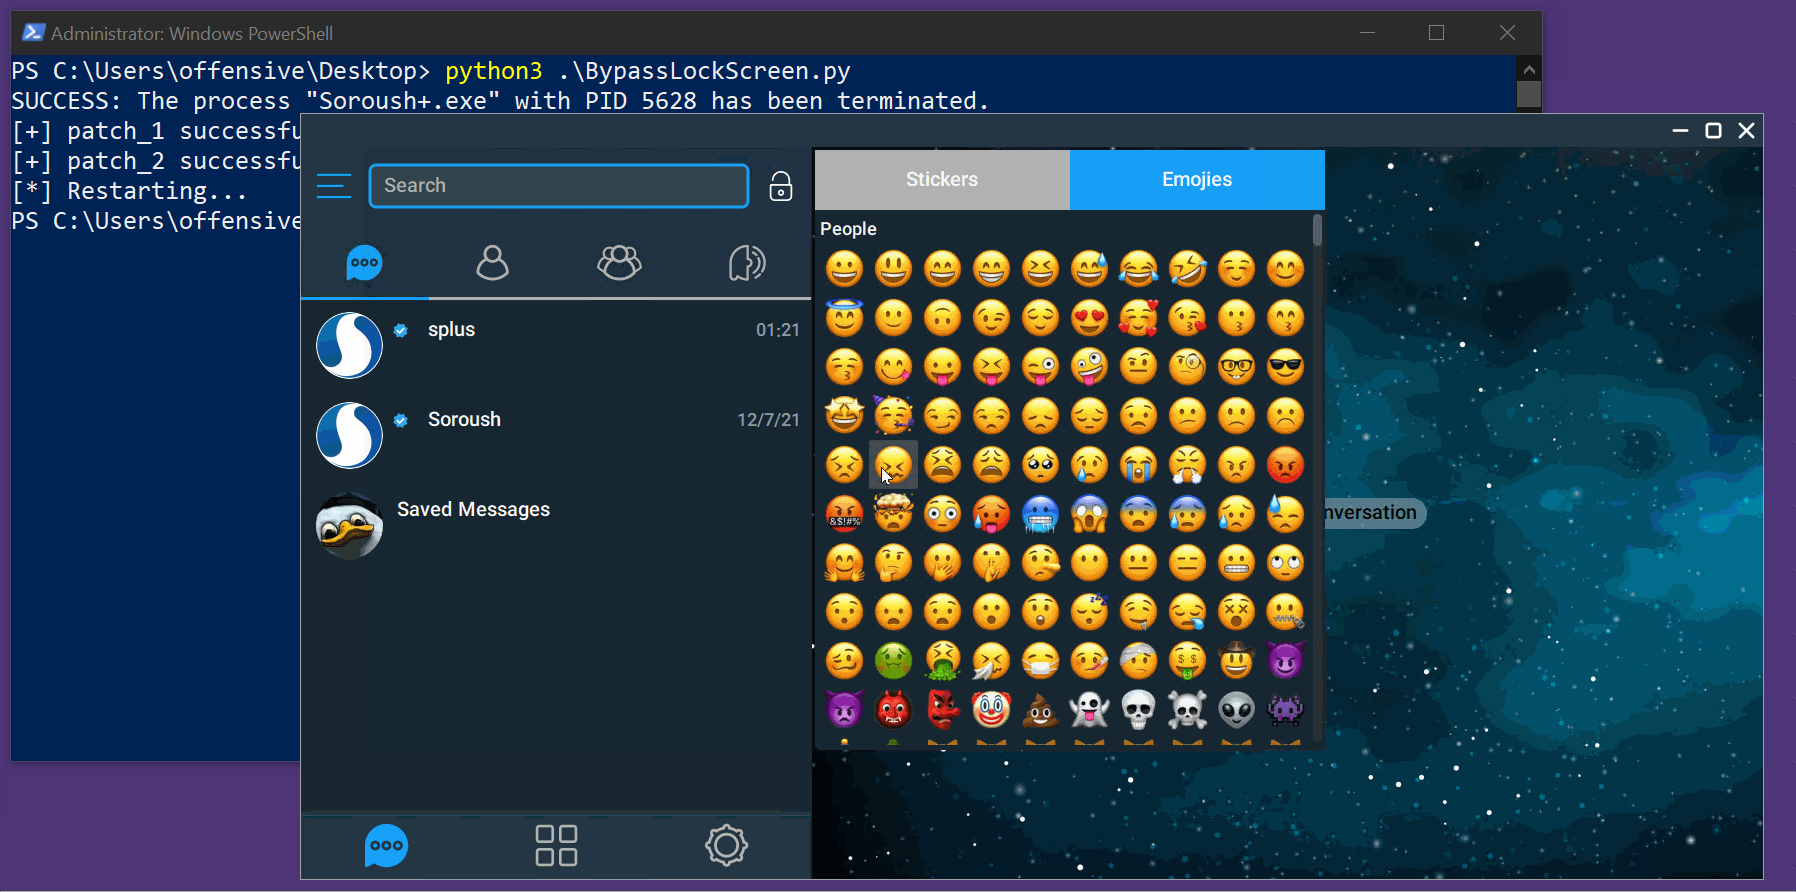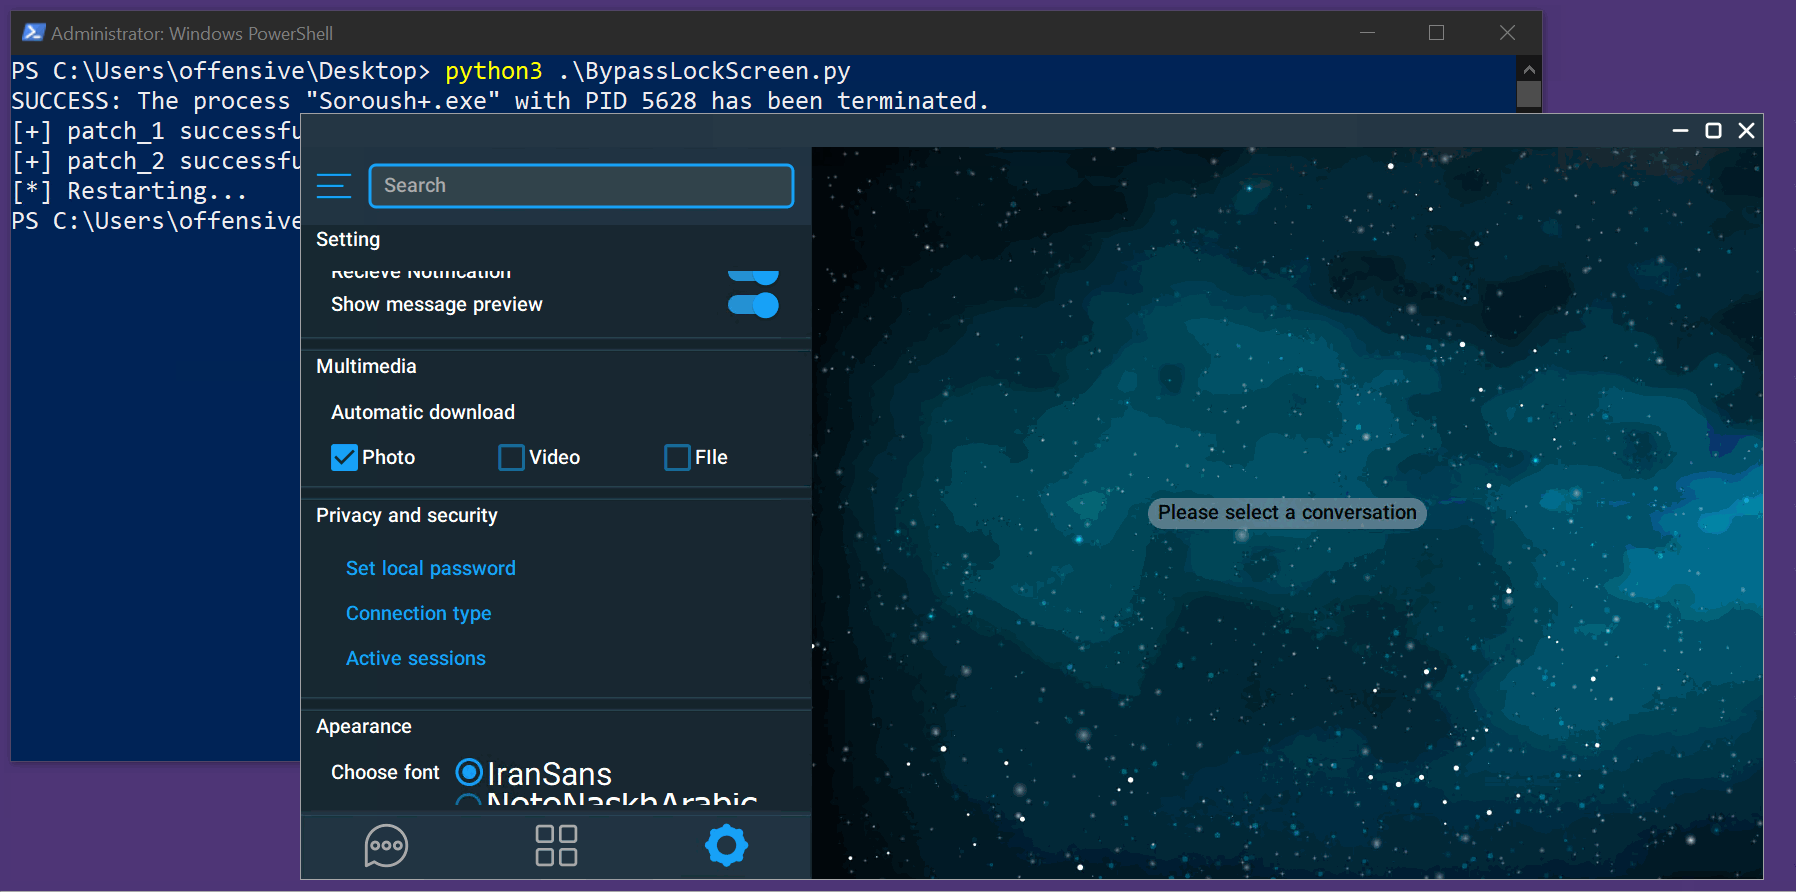
CVE-2022-26629
 scopion/cve-2022-26629
PoC exploit for CVE-2022-26629: bypasses the lock screen on SoroushPlus+ Messenger 1.0.30 via improper access control. Includes an auto-exploit…
android-securityexploitationmobile-security+2
scopion/cve-2022-26629PoC exploit for CVE-2022-26629: bypasses the lock screen on SoroushPlus+ Messenger 1.0.30 via improper access control. Includes an auto-exploit…
 gmh5225/androiddrivesignity
AndroidDriveSignity is a Python utility designed to bypass driver signature verification in Android kernel(ARMv8.3), facilitating the loading of…
 idanshechter/cve-2017-13208-scanner
Python script using r2pipe to detect CVE-2017-13208 in Android libnetutils.so by checking for missing dhcp_size validation via static binary analysis.
 jduck/cve-2015-1538-1
Python exploit for CVE-2015-1538-1 targeting Stagefright's 'stsc' MP4 atom integer overflow to achieve remote code execution and a reverse shell on…
 renjithsasidharan/cve-2015-1538-1
An exploit for CVE-2015-1538-1 - Google Stagefright ‘stsc’ MP4 Atom Integer Overflow Remote Code Execution