Mobile-Security-Framework-MobSF

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

The Leading Security Assessment Framework for Android.

Android framework base exploit for CVE-2023-20943, enabling privilege escalation testing on vulnerable Android devices.

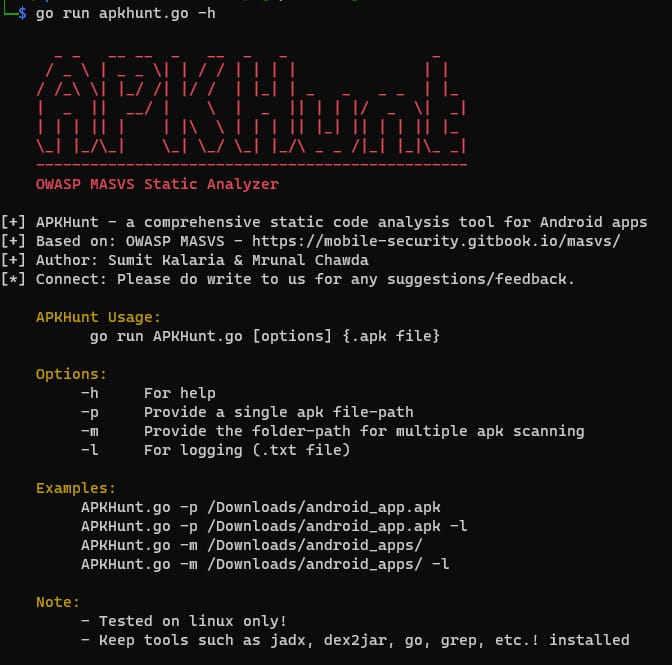
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…

Repository for the Smartphone Pentest Framework (SPF)

Android framework vulnerability analysis and exploitation tool targeting CVE-2021-0315 for security testing and research.

Install and run Metasploit Framework 6 on Android via Termux with automated setup, payload generation (msfvenom), and full msfconsole access for…

Framework to create, generate, and embed APK payloads for Android penetration testing, leveraging Metasploit for exploitation and Apktool for…

MARA is a Mobile Application Reverse engineering and Analysis Framework. It is a toolkit that puts together commonly used mobile application reverse…

Modular Android APK security analysis framework integrating static, dynamic, and reverse engineering tools for comprehensive vulnerability assessment…

Android framework base repository modified to address CVE-2022-20004, providing a patched version for security analysis and testing.

Android framework base repository modified to address CVE-2021-0705, providing a patched or vulnerable version for security research and exploitation…

Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…

Ghidra is a software reverse engineering (SRE) framework

UNIX-like reverse engineering framework and command-line toolset

Ghost Framework is an Android post-exploitation framework that exploits the Android Debug Bridge to remotely access an Android device.

An easy-to-learn/use static analysis framework for Java and Android

DECAF (short for Dynamic Executable Code Analysis Framework) is a binary analysis platform based on QEMU. This is also the home of the DroidScope…