

jadx
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
android-securitybinary-analysisdebuggers+5
skylot/jadxCommand-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 anonymous941/zygote-injection-toolkit
A command-line utility to exploit Android Zygote injection (CVE-2024-31317)
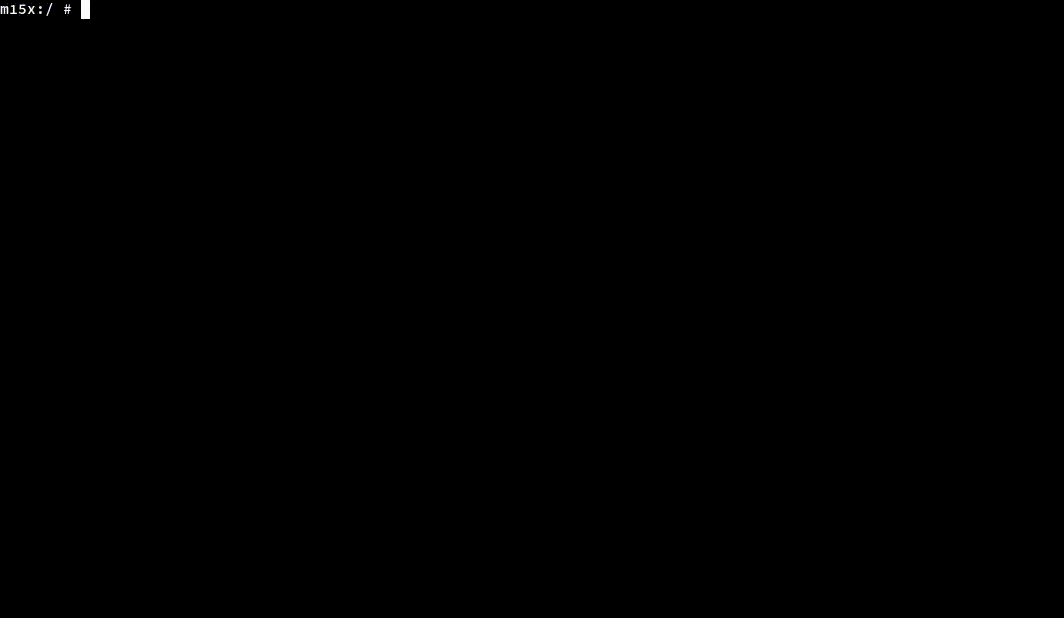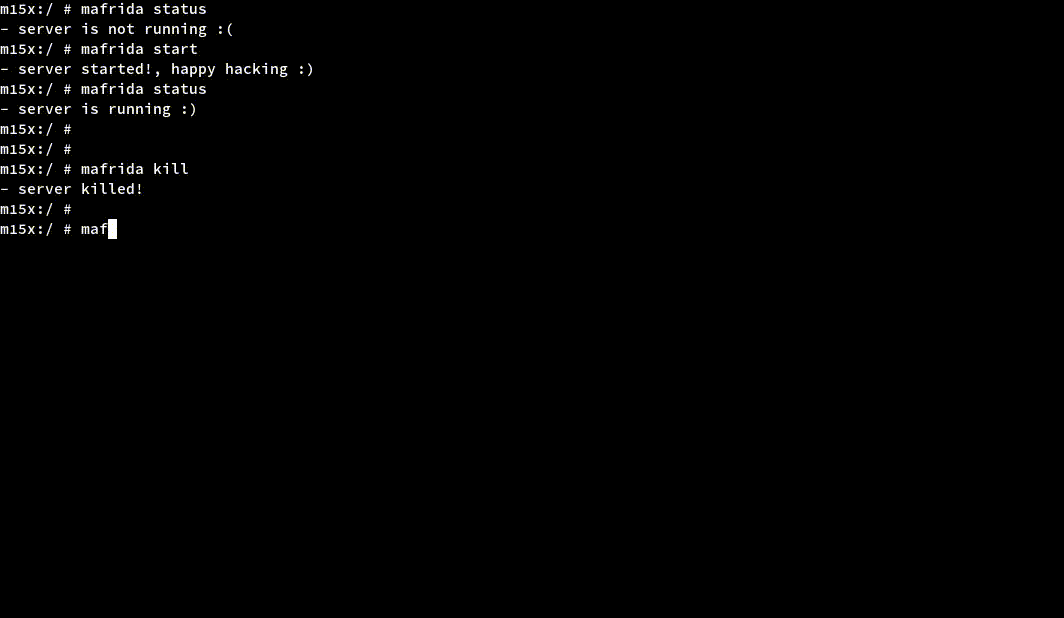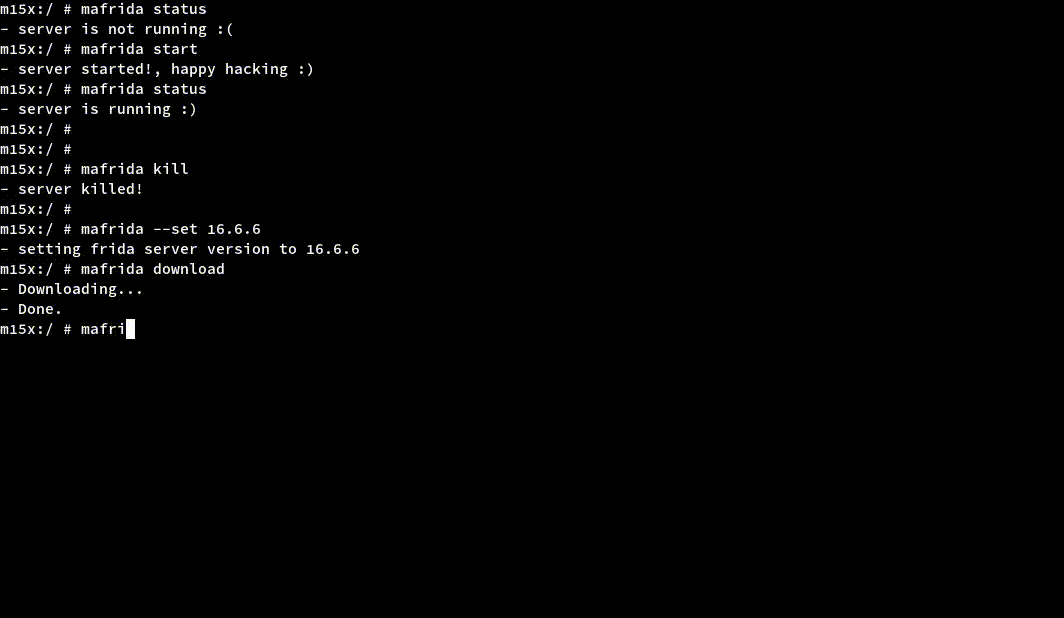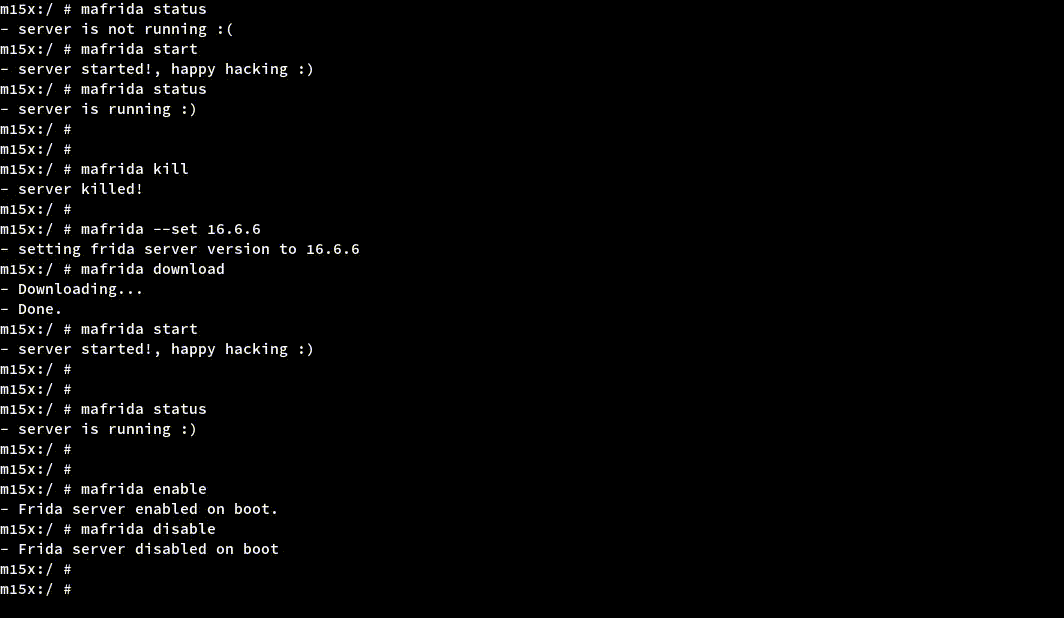 theshinigami/mafrida
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
 piotr-kniaz/eslockdecryptor
Utility for recovering ES File Explorer encrypted files (.eslock)
 superandroidanalyzer/super
Secure, Unified, Powerful and Extensible Rust Android Analyzer
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework