
Magisk
 topjohnwu/magisk
Android customization suite providing root access (MagiskSU), systemless module installation, boot image unpacking/repacking, and Zygisk runtime code…
android-securitymobile-securityprivilege-escalation
topjohnwu/magiskAndroid customization suite providing root access (MagiskSU), systemless module installation, boot image unpacking/repacking, and Zygisk runtime code…
 vino-theva/cve-2019-6447
This paper is about manual exploitation of android open port vulnerability found in ES file manager. This open TCP 59777 port allows the attacker to…
 idanr1986/cuckoo-droid
CuckooDroid - Automated Android Malware Analysis with Cuckoo Sandbox.
 theandersmadsen/humane-aipin-ghostlock
Guarded, source-only Humane AI Pin root PoC for CVE-2026-43499
 vaibhavpandeyvpz/apkstudio
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…
 donctl/sandy
Release of the sandy framework.
 irsl/cve-2022-3168-adb-unexpected-reverse-forwards
Proof of concept code to exploit flaw in adb that allowed opening network connections on the host to arbitrary destinations
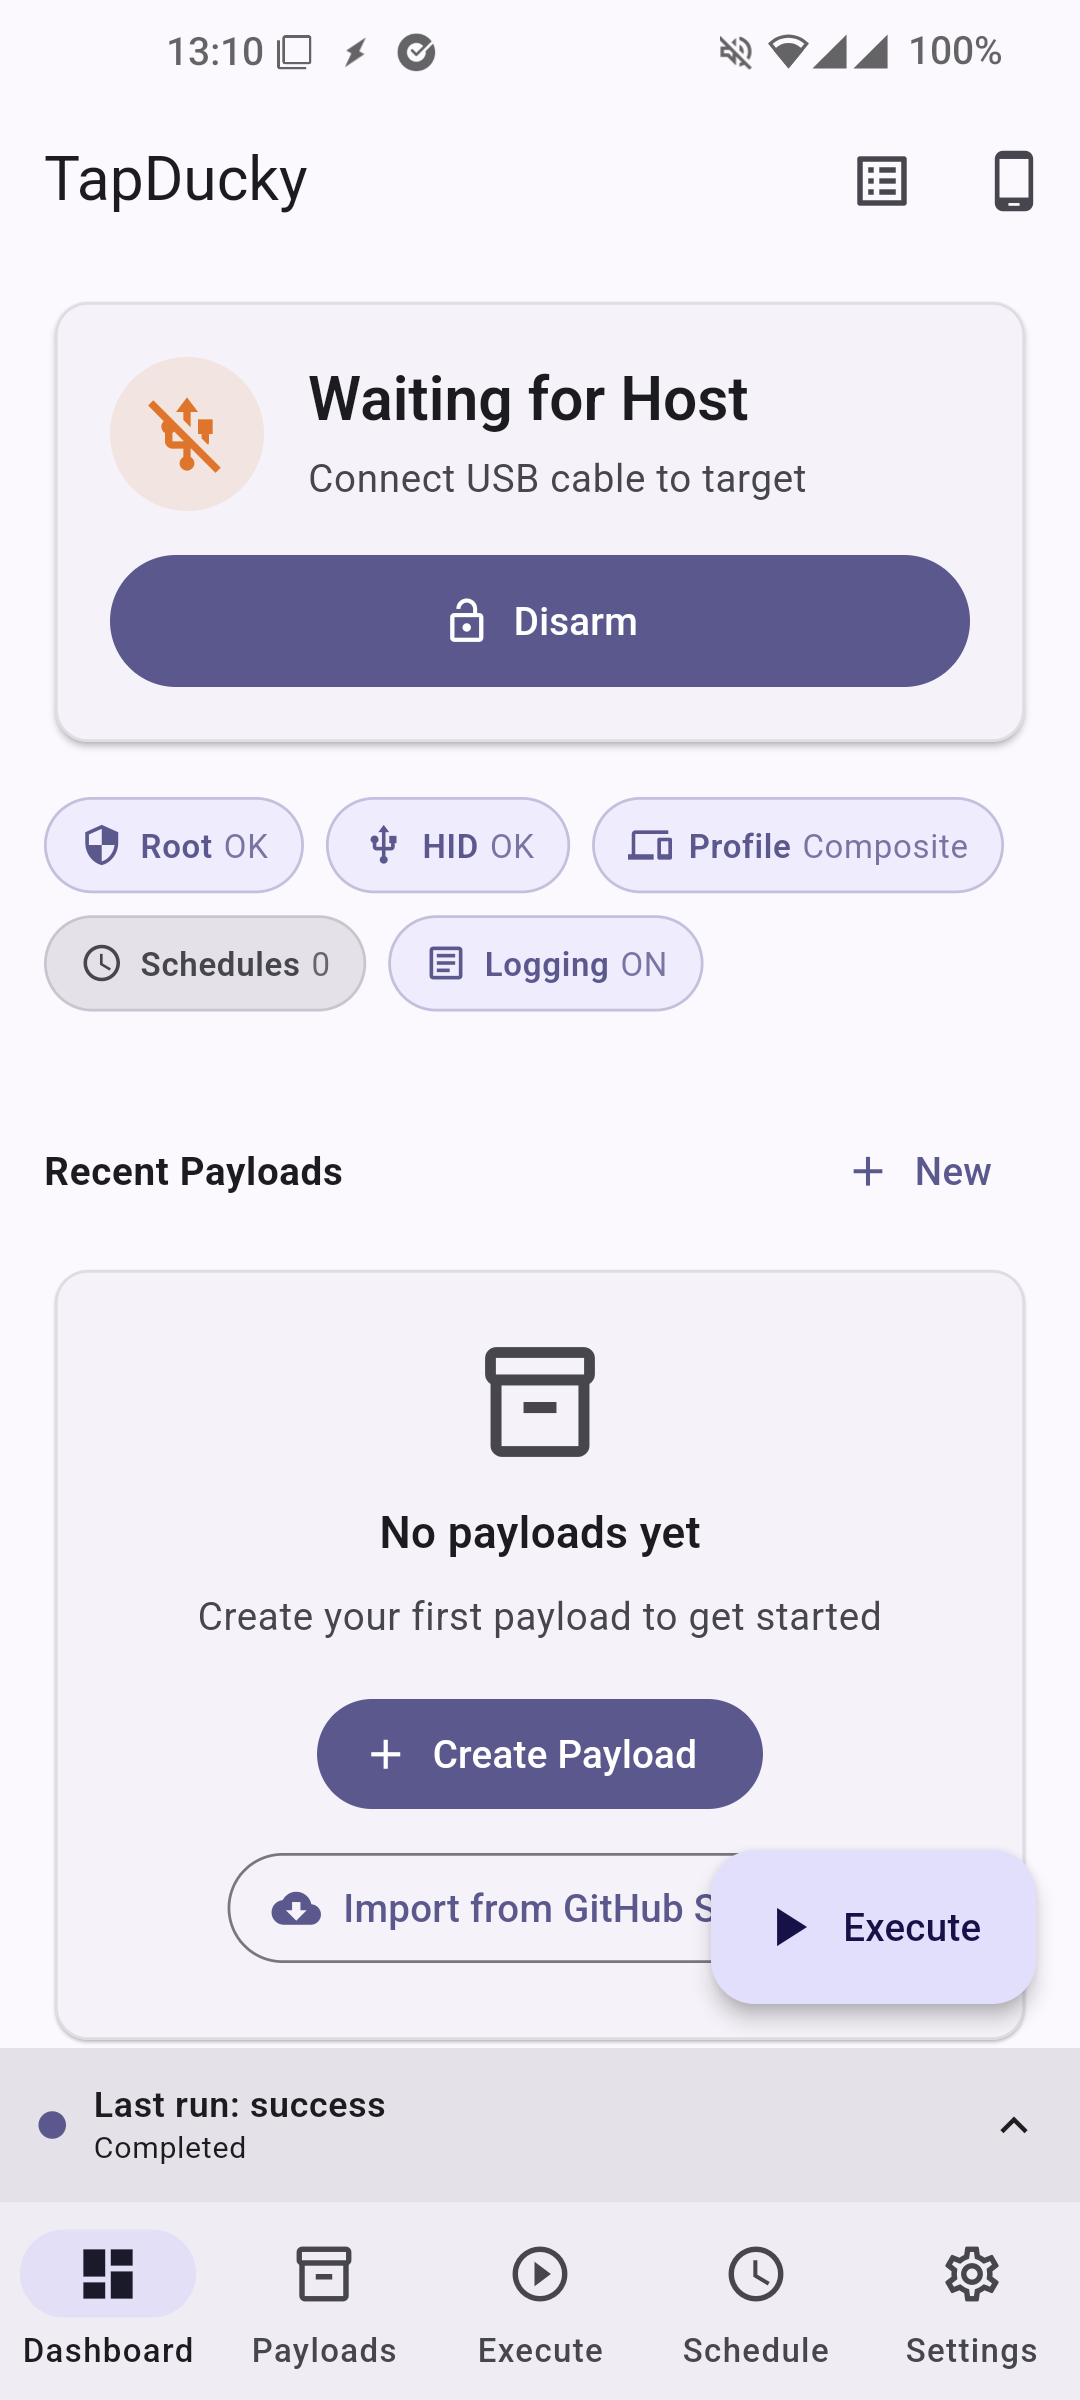 iodn/tap-ducky
Turns any rooted phone into the legendary USB Rubber Ducky. Android USB HID Keystroke Injector
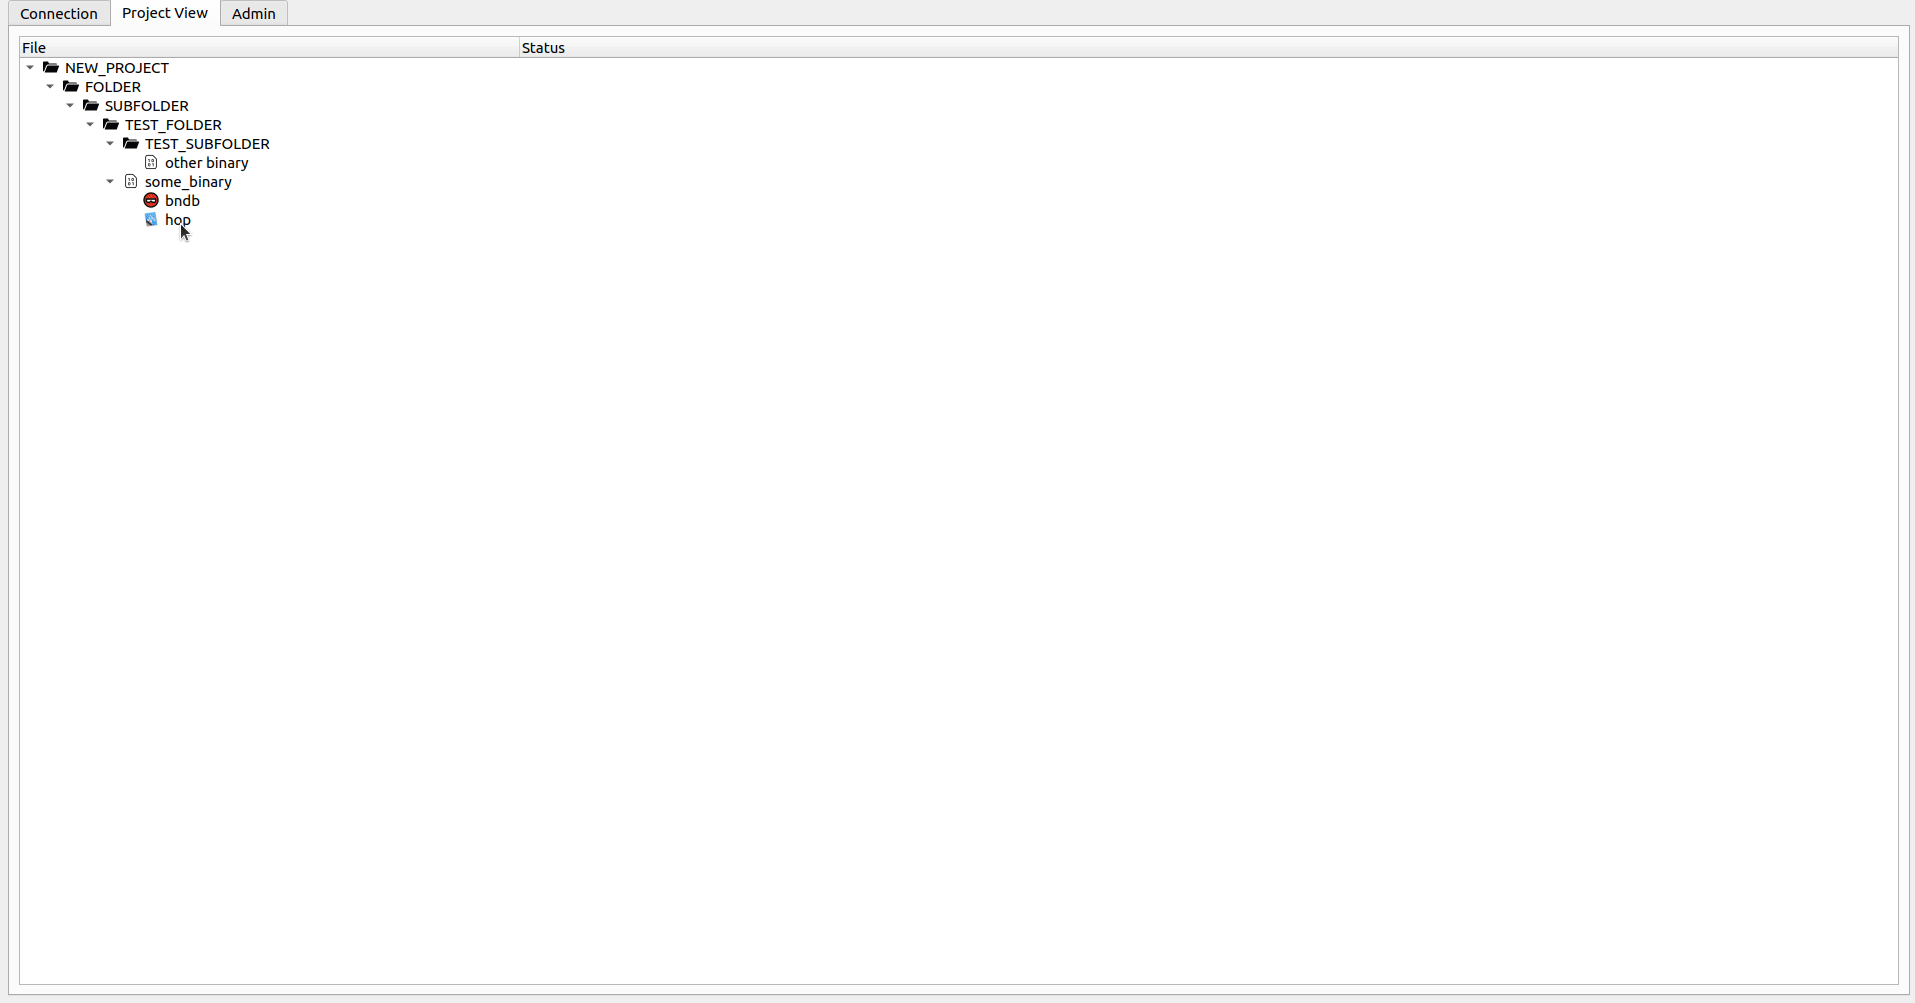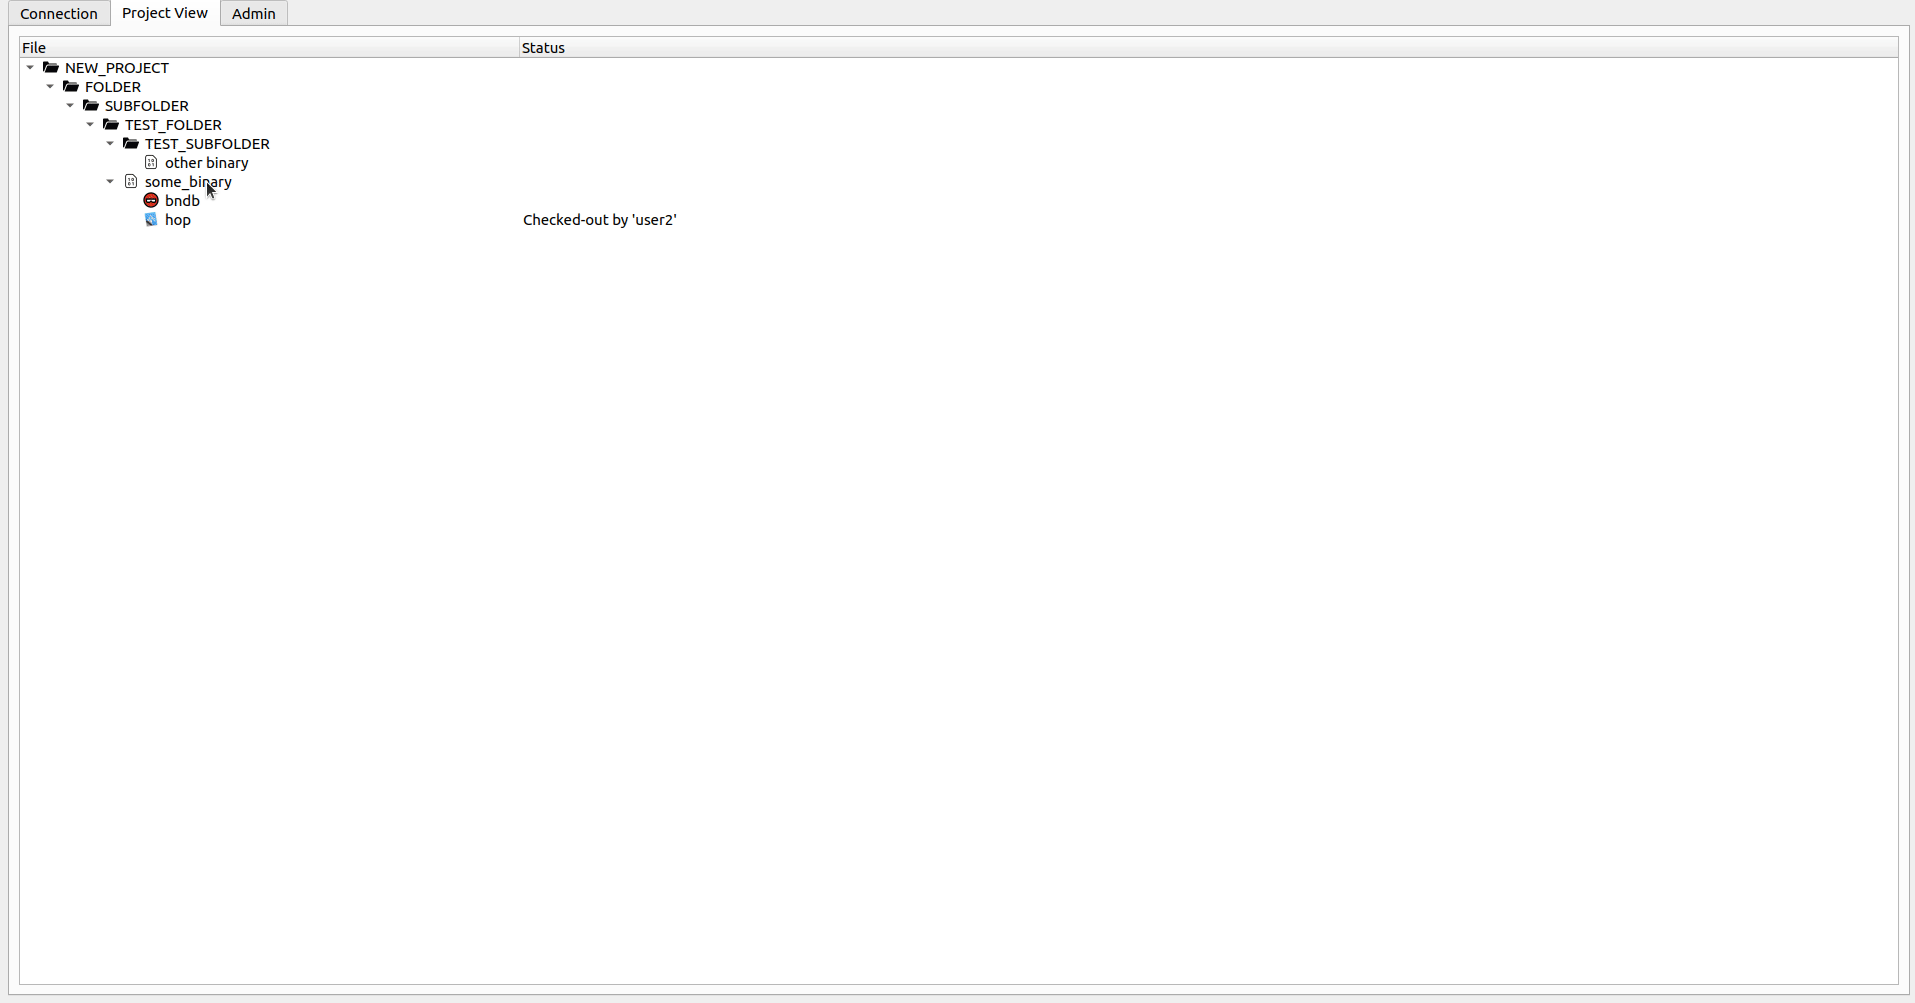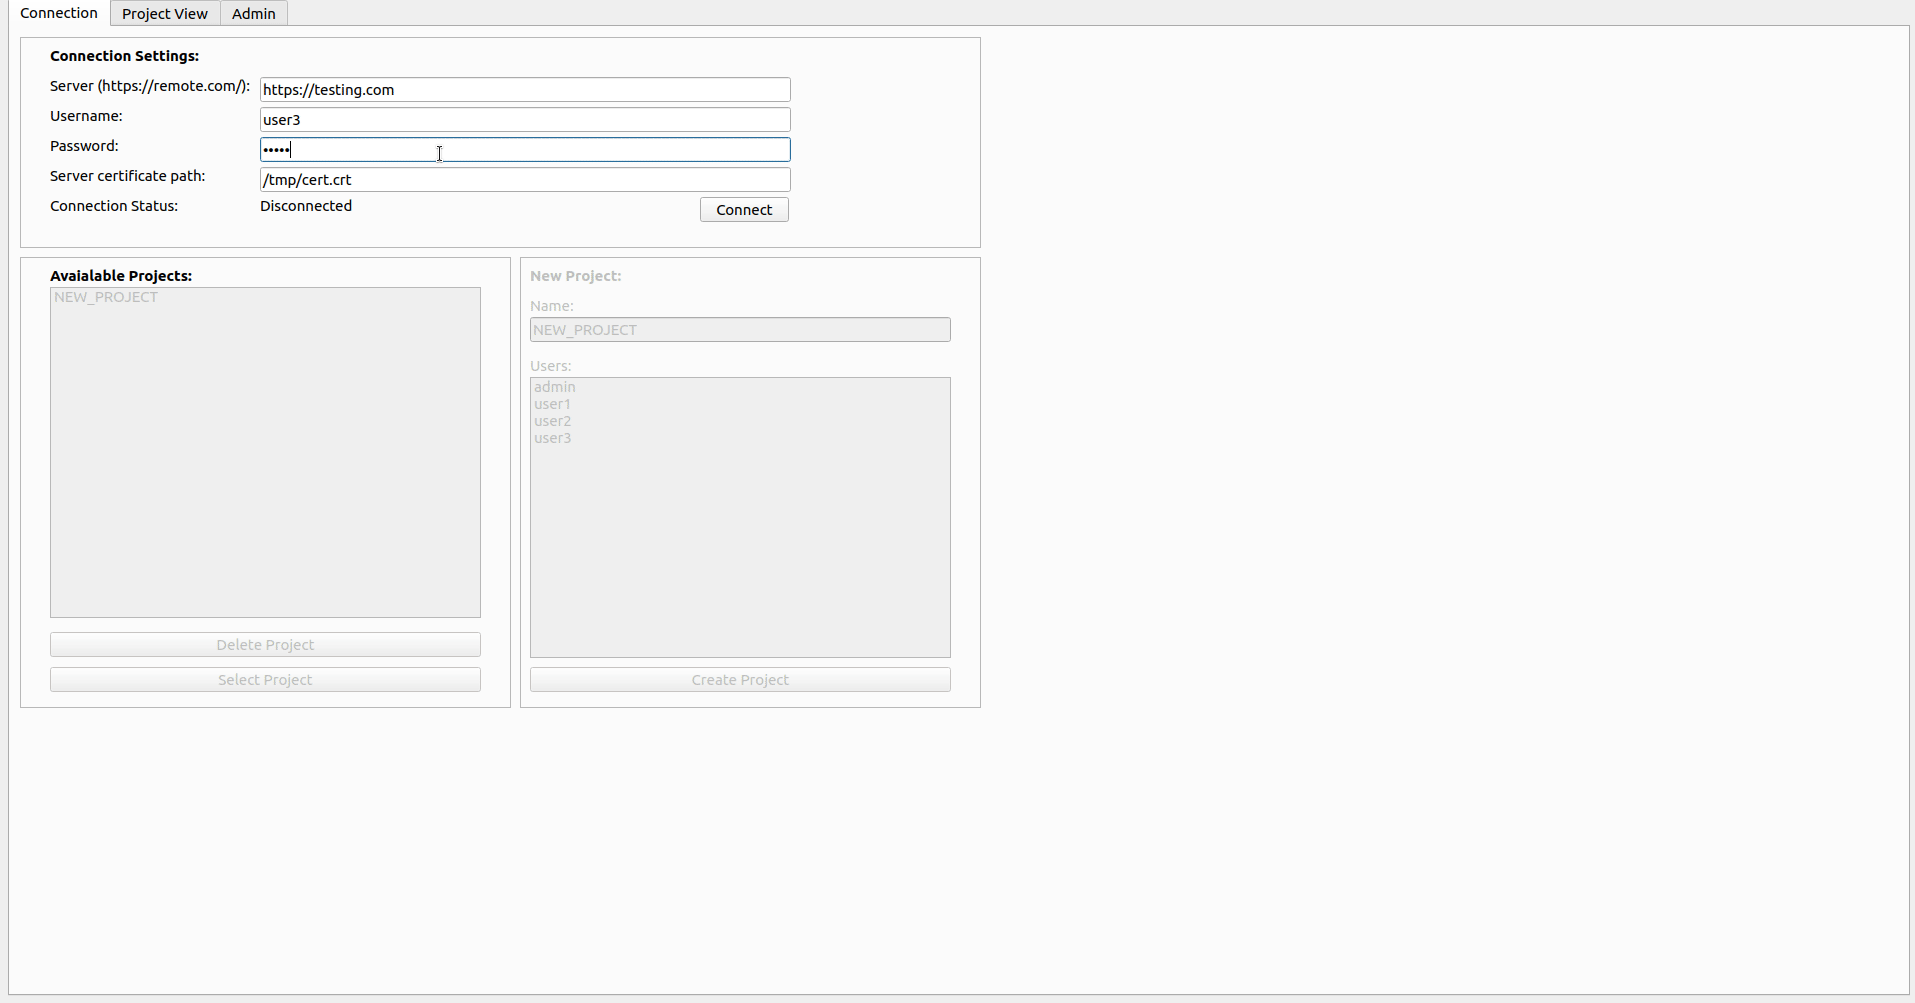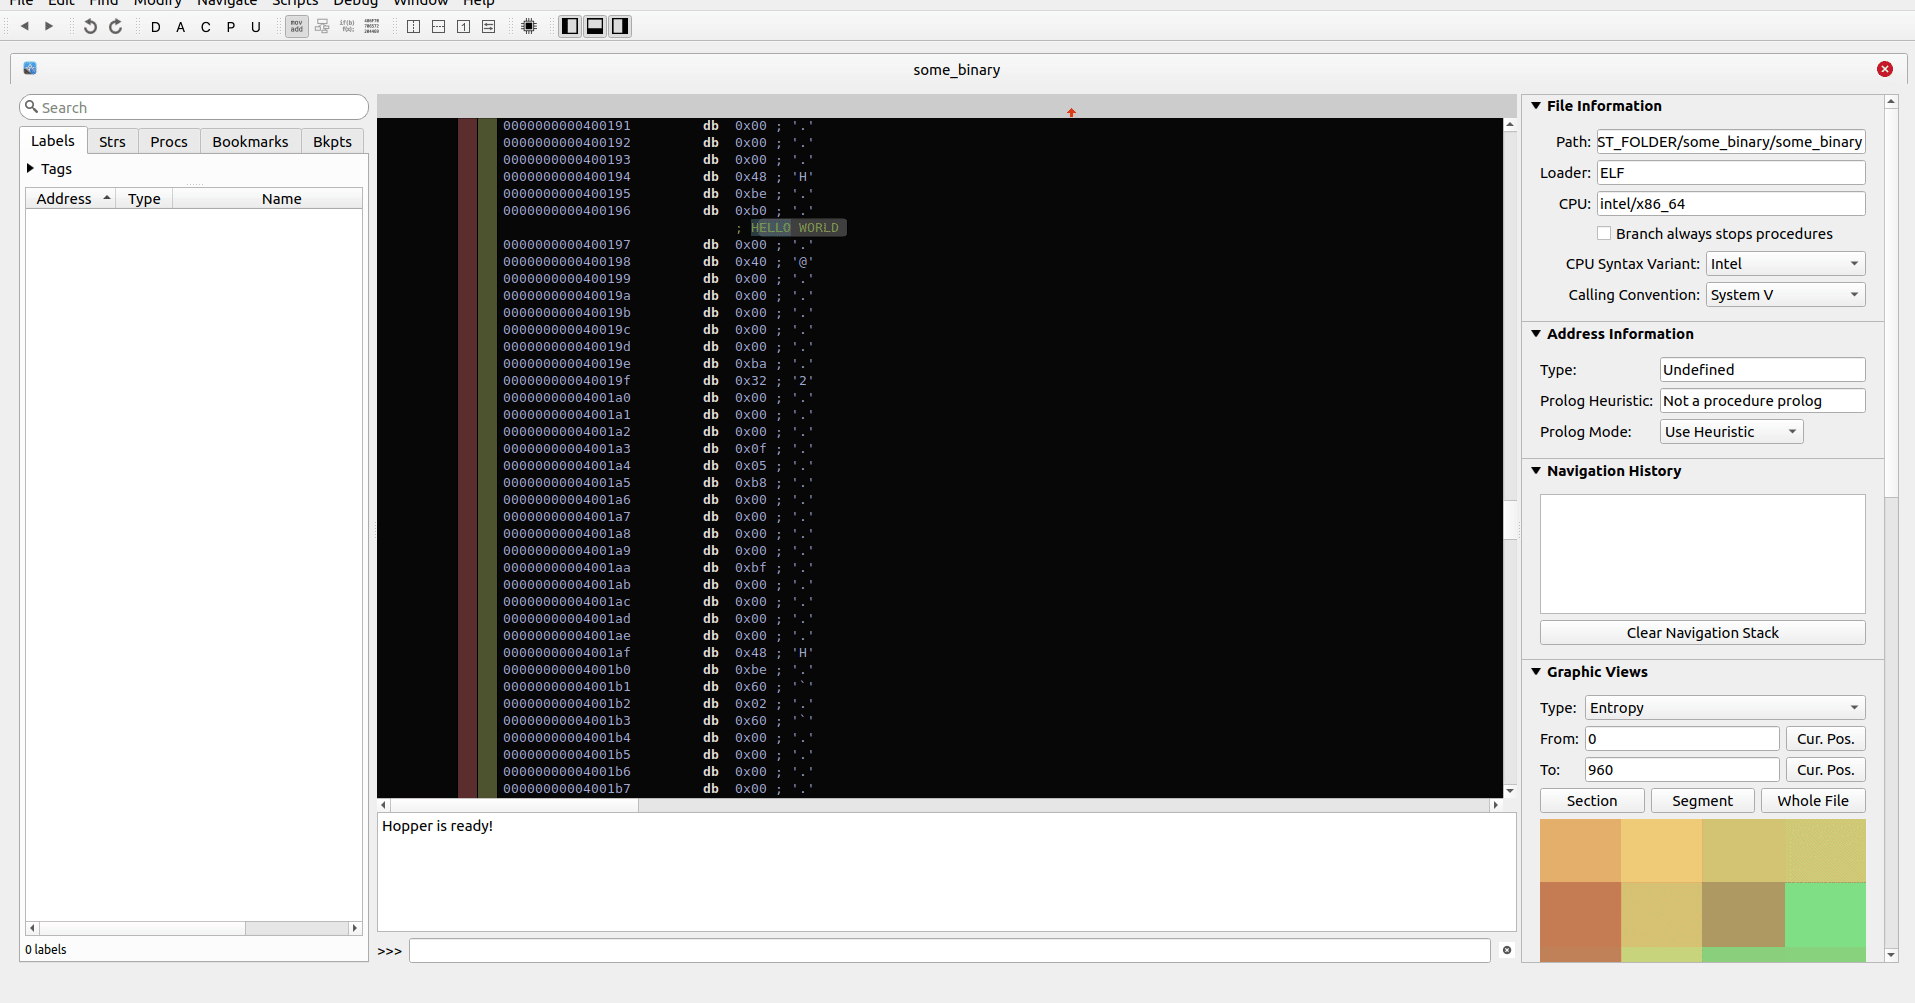 martyx00/collare
Multi-tool reverse engineering collaboration solution.
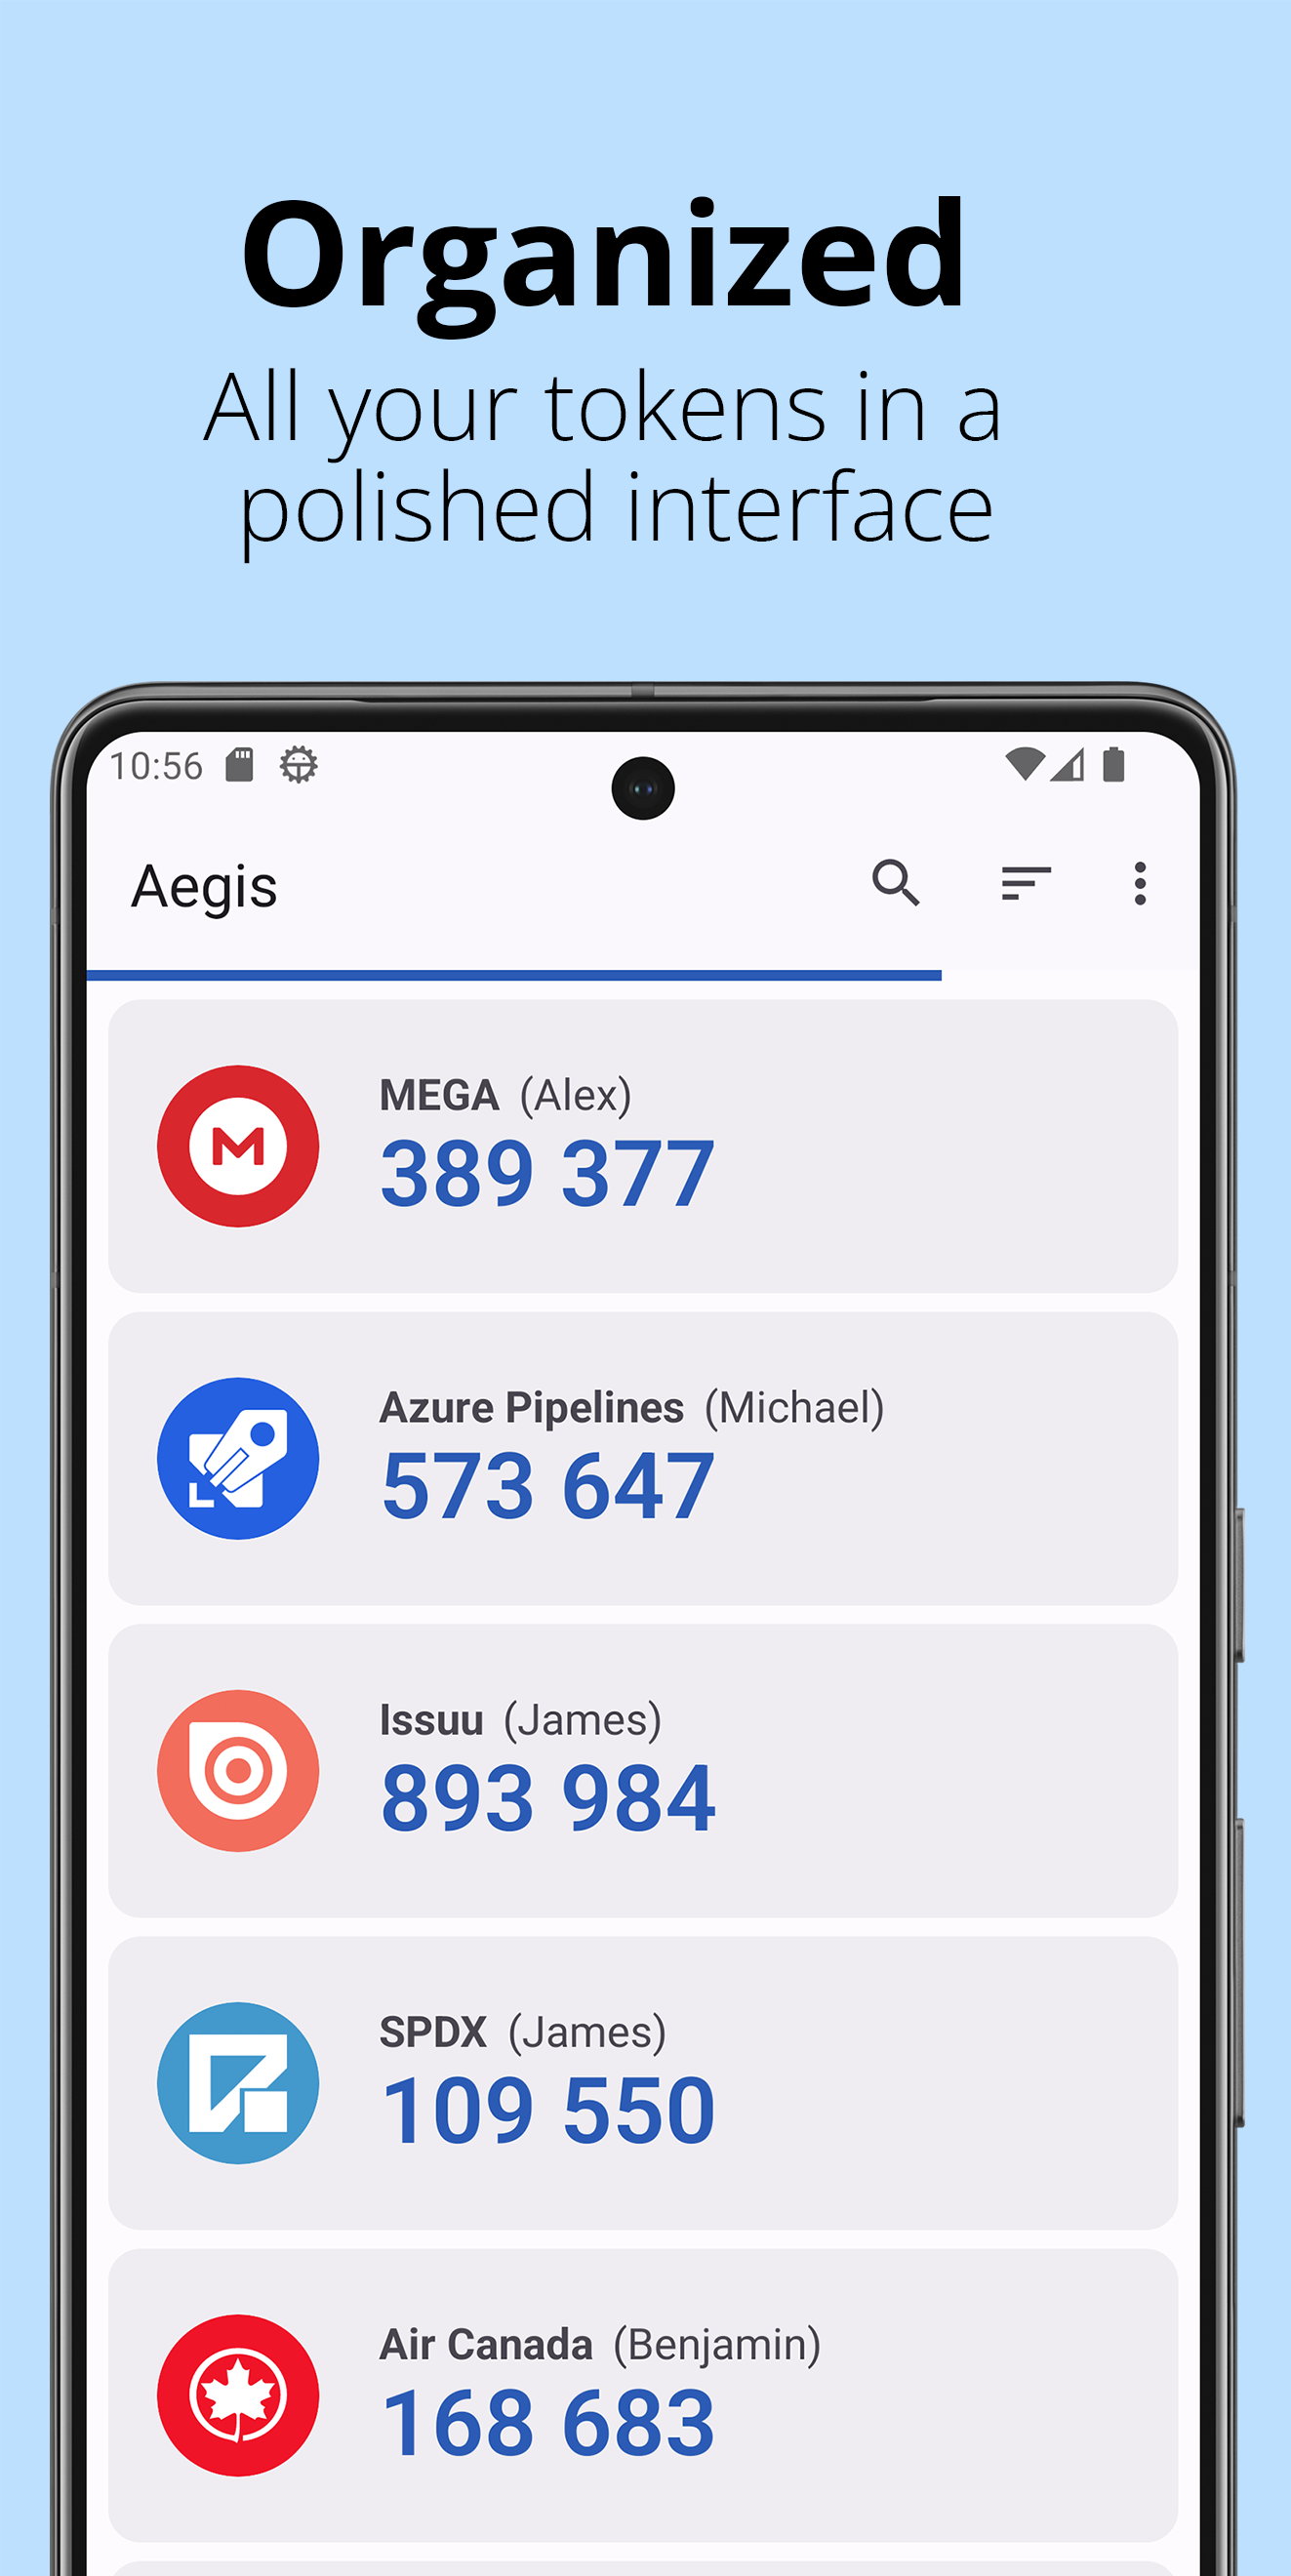 beemdevelopment/aegis
A free, secure and open source app for Android to manage your 2-step verification tokens.
 fs0c131y/esfileexploreropenportvuln
ES File Explorer Open Port Vulnerability - CVE-2019-6447
 fmd-foss/fmd-android
Find your device and control it remotely. Works over SMS, instant messengers, or FMD Server's web interface. A secure open source alternative to…
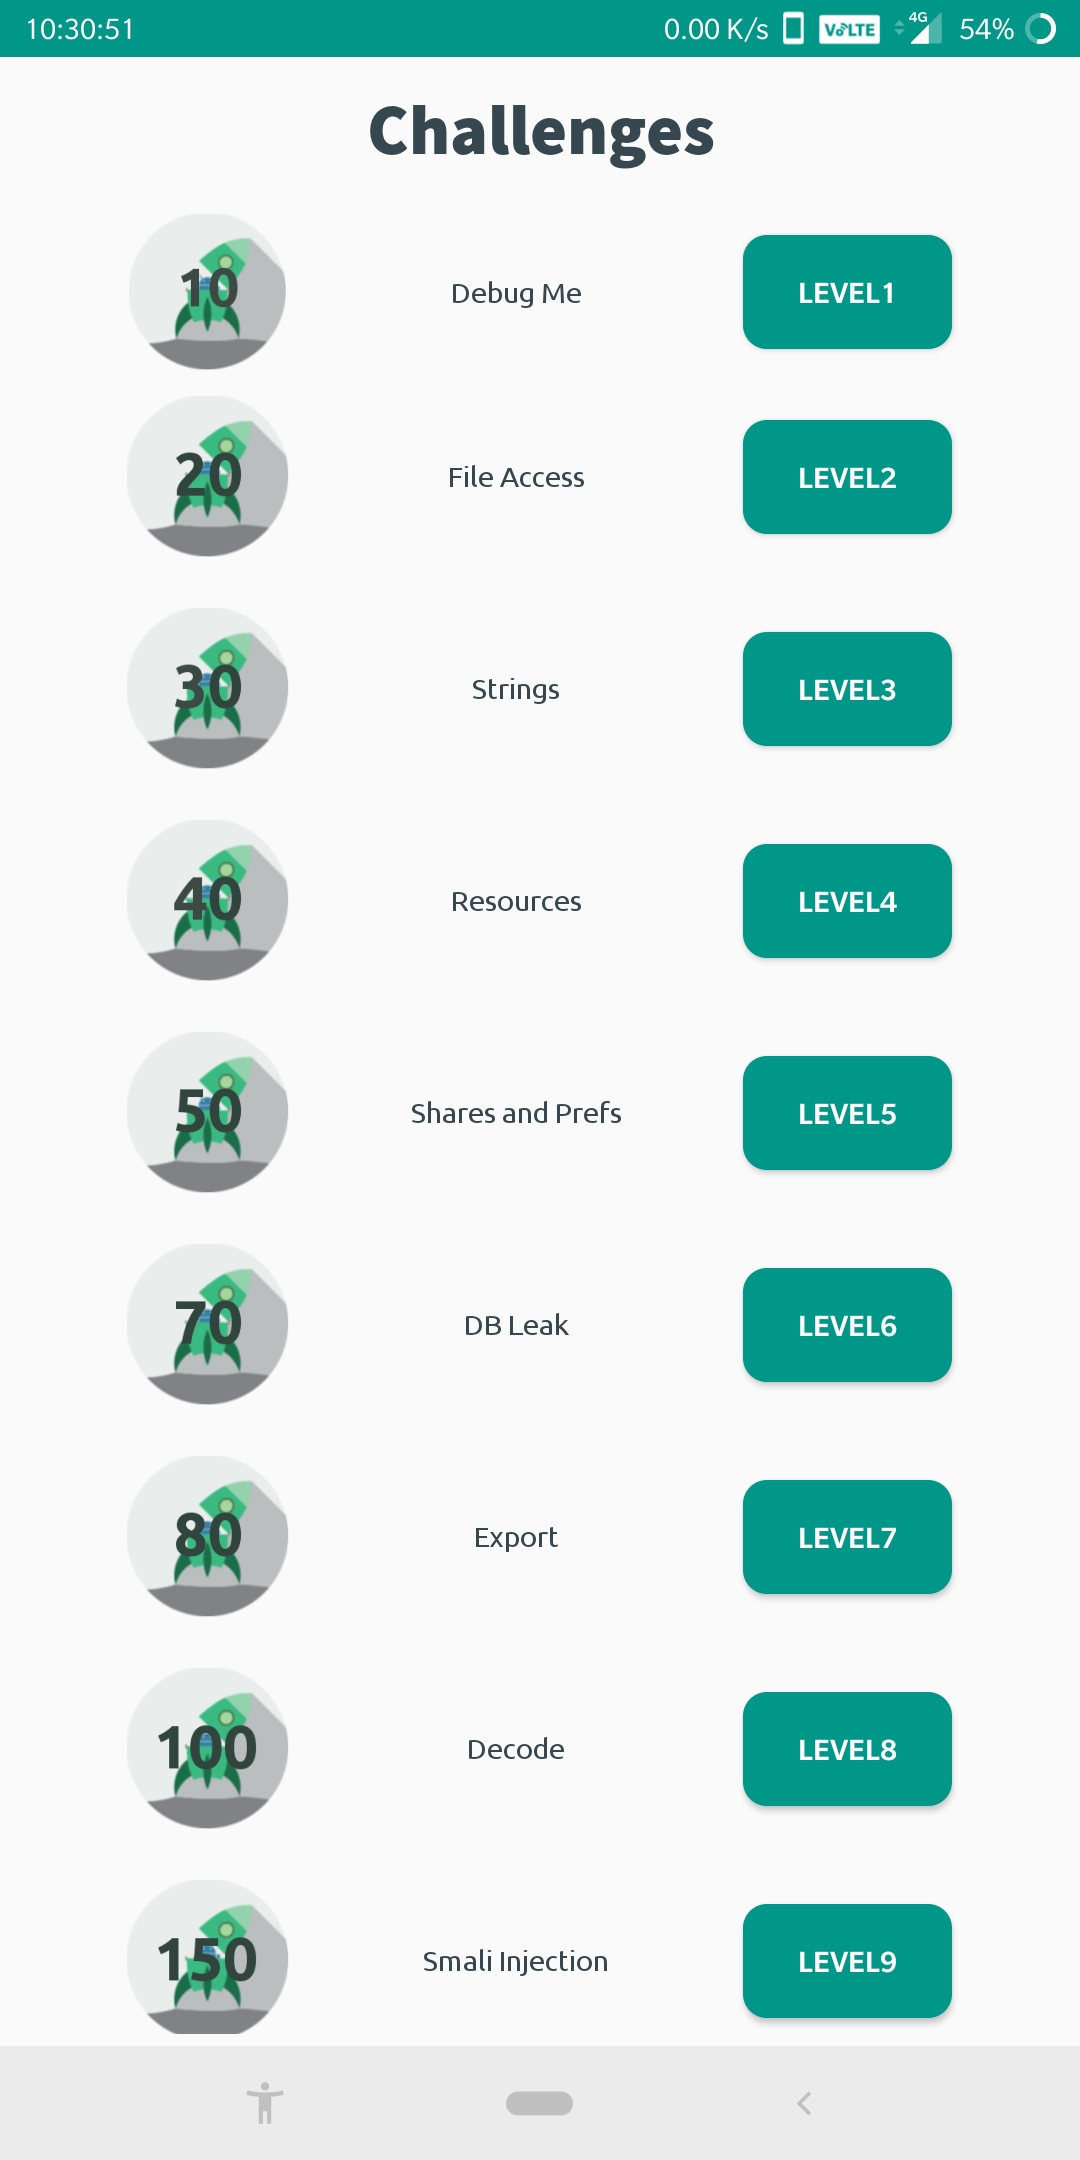 abhi-r3v0/evabs
An open source Android application that is intentionally vulnerable so as to act as a learning platform for Android application security beginners.
 febinrev/cve-2019-6447-esfile-explorer-exploit
ES File Explorer v4.1.9.7.4 Open port vulnerability exploit. CVE-2019-6447
 sandarufdo/es-file-explorer-open-port-vulnerability---cve-2019-6447
ES File Explorer Open Port Vulnerability - CVE-2019-6447
 nowsecure/android-forensics
Open source Android Forensics app and framework
 androguard/androguard
Reverse engineering and pentesting for Android applications
 protonvpn/android-app
Open-source Android VPN client that encrypts traffic via OpenVPN and IKEv2, ensuring privacy and secure access on untrusted networks.