CVE-2022-3168-adb-unexpected-reverse-forwards

Proof of concept code to exploit flaw in adb that allowed opening network connections on the host to arbitrary destinations

Proof of concept code to exploit flaw in adb that allowed opening network connections on the host to arbitrary destinations

True P2P Email on top of Yggdrasil Network for Android

Low Interaction Mobile Honeypot

A PoC tool for the CVE-2026-0073 on android 11+ devices which allows instant zero click RCE on any unpatched device with adb over tcp enabled

Pixnapping Attack: Compromising private keys and seed phrases through vulnerability CVE-2025-48561 represents a new critical threat to the Bitcoin…

No-root network monitor, firewall and PCAP dumper for Android

Dynamic analysis sandbox for Android apps that monitors network traffic, file operations, cryptographic API usage, permission circumvention, and…

Know what changed inside your Electron release: diff two builds for IPC, preload, windows, fuses and hosts, with file:line. CLI, CI gate, MCP server.

CVE-2025-48593

The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…

⚡️An awesome list of the best Termux hacking tools

A curated list of awesome Android Reverse Engineering training, resources, and tools.

Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…

Android complete exploit chain that enables privilege escalation from a local untrusted app to root/kernel, combination of CVE-2026-49881 and…

A tool to automate the boring process of APK recon

Significant security enchancements of recent major Android versions.

Grammar-guided evolutionary fuzzer for dynamic analysis of AT command interfaces on Android smartphones via Bluetooth and USB, uncovering DoS,…

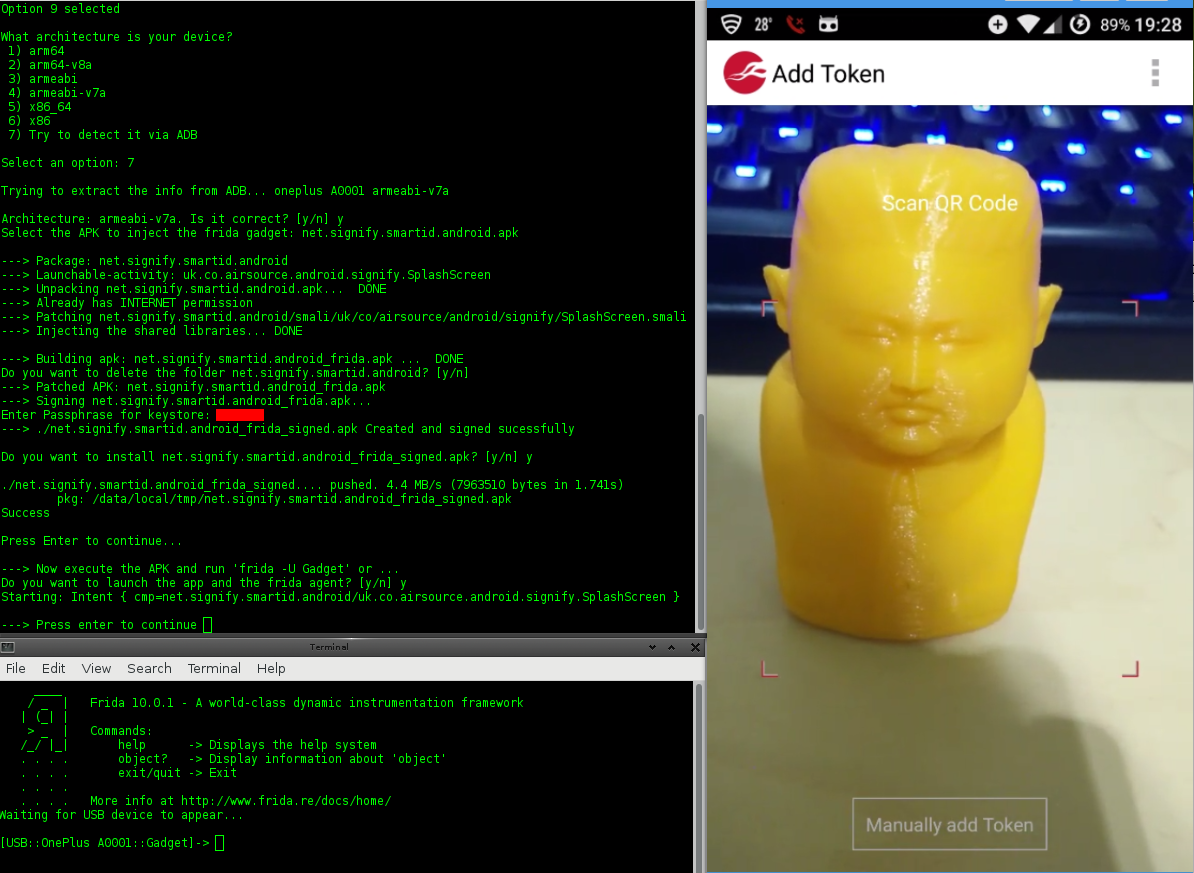
bash script to facilitate some aspects of an Android application assessment