
Archived
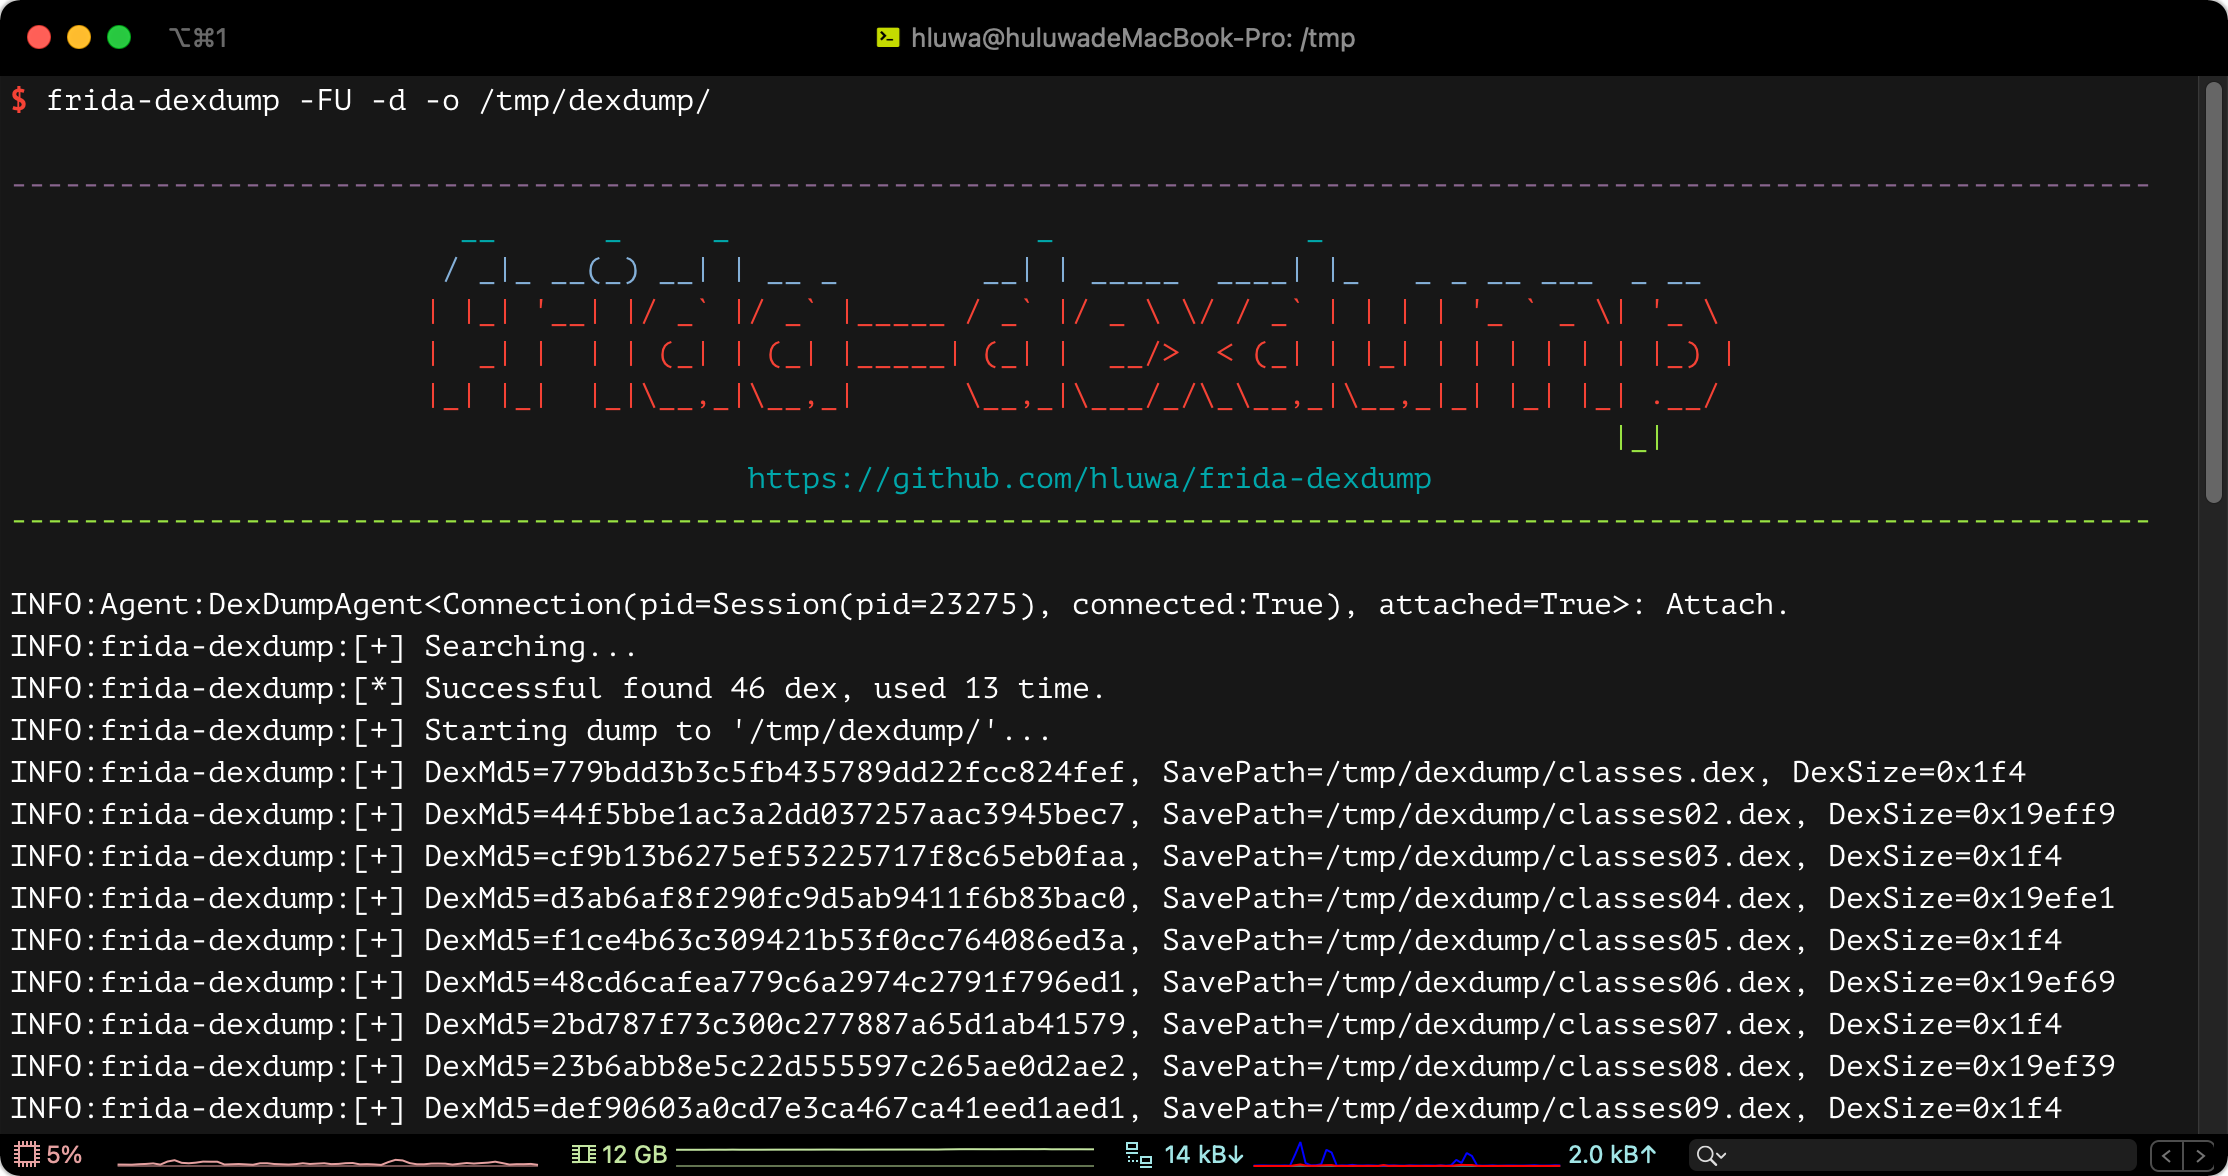
frida-dexdump
 hluwa/frida-dexdump
A frida tool to dump dex in memory to support security engineers analyzing malware.
android-securitybinary-analysisdynamic-analysis-sandboxing+5
hluwa/frida-dexdumpA frida tool to dump dex in memory to support security engineers analyzing malware.
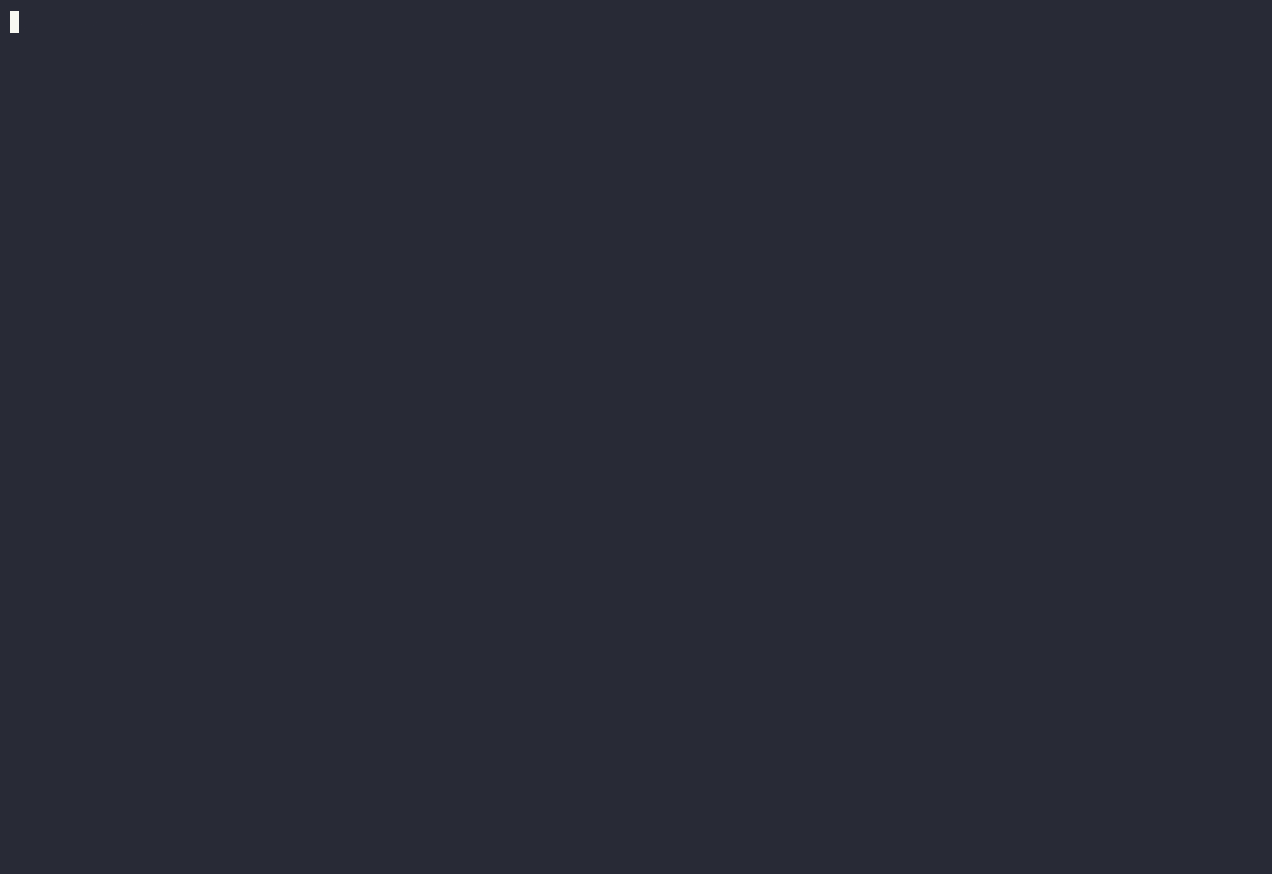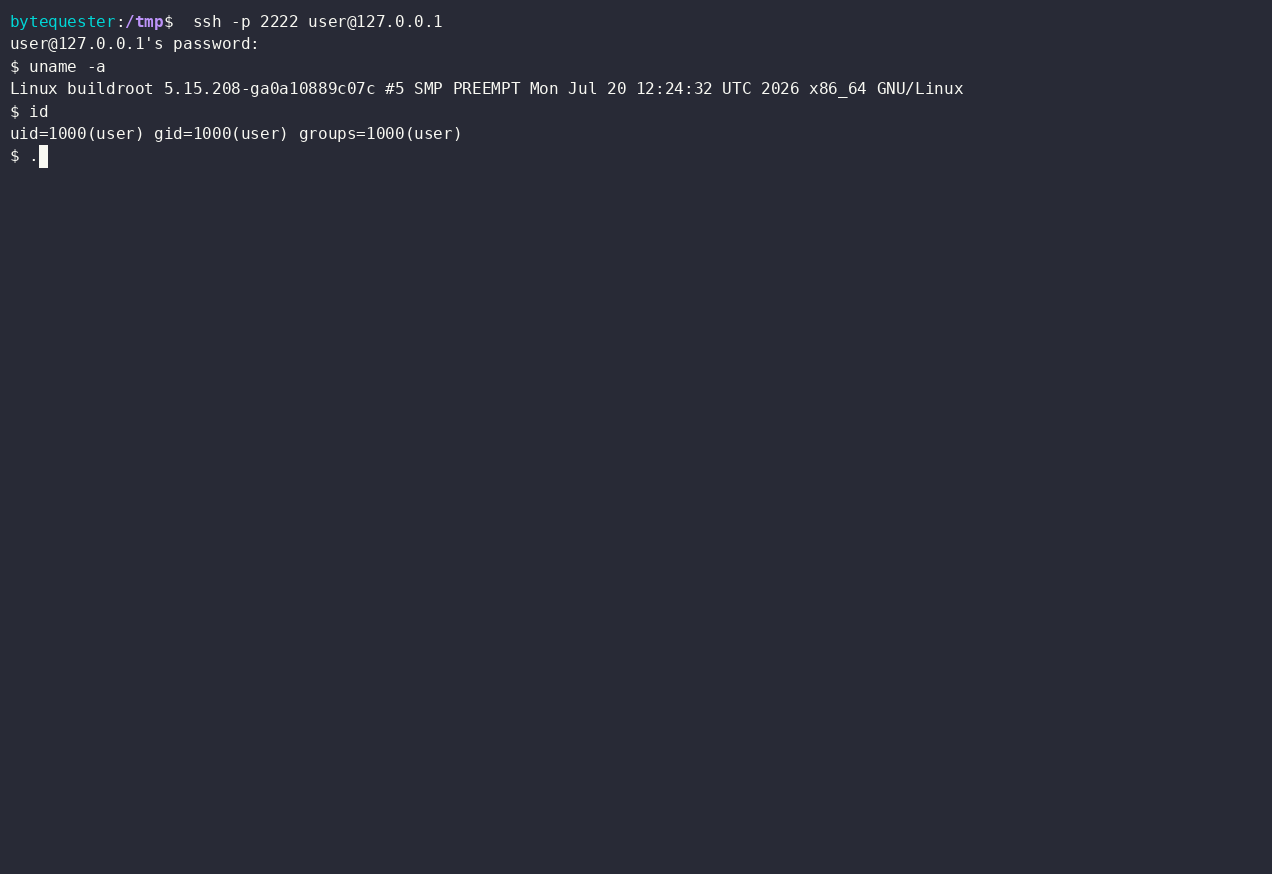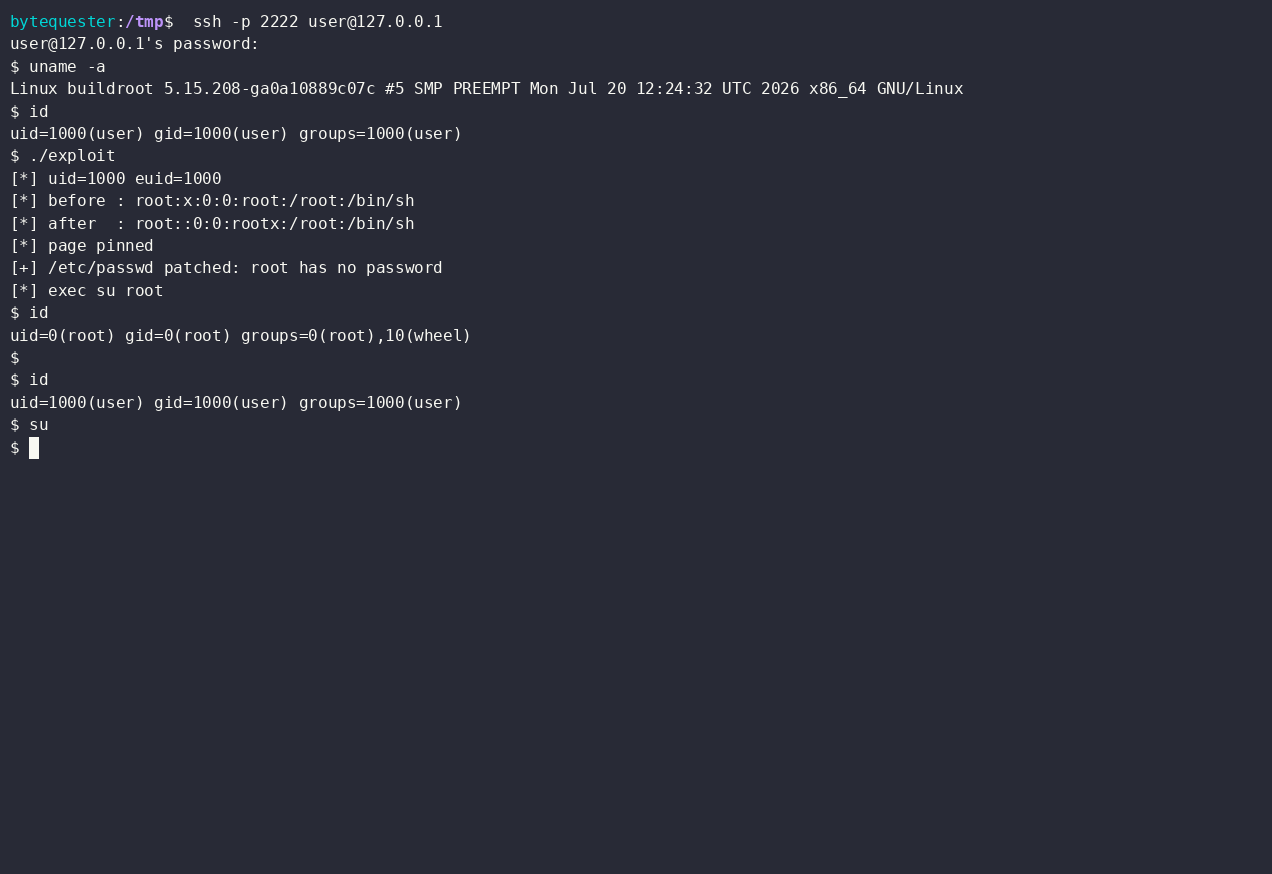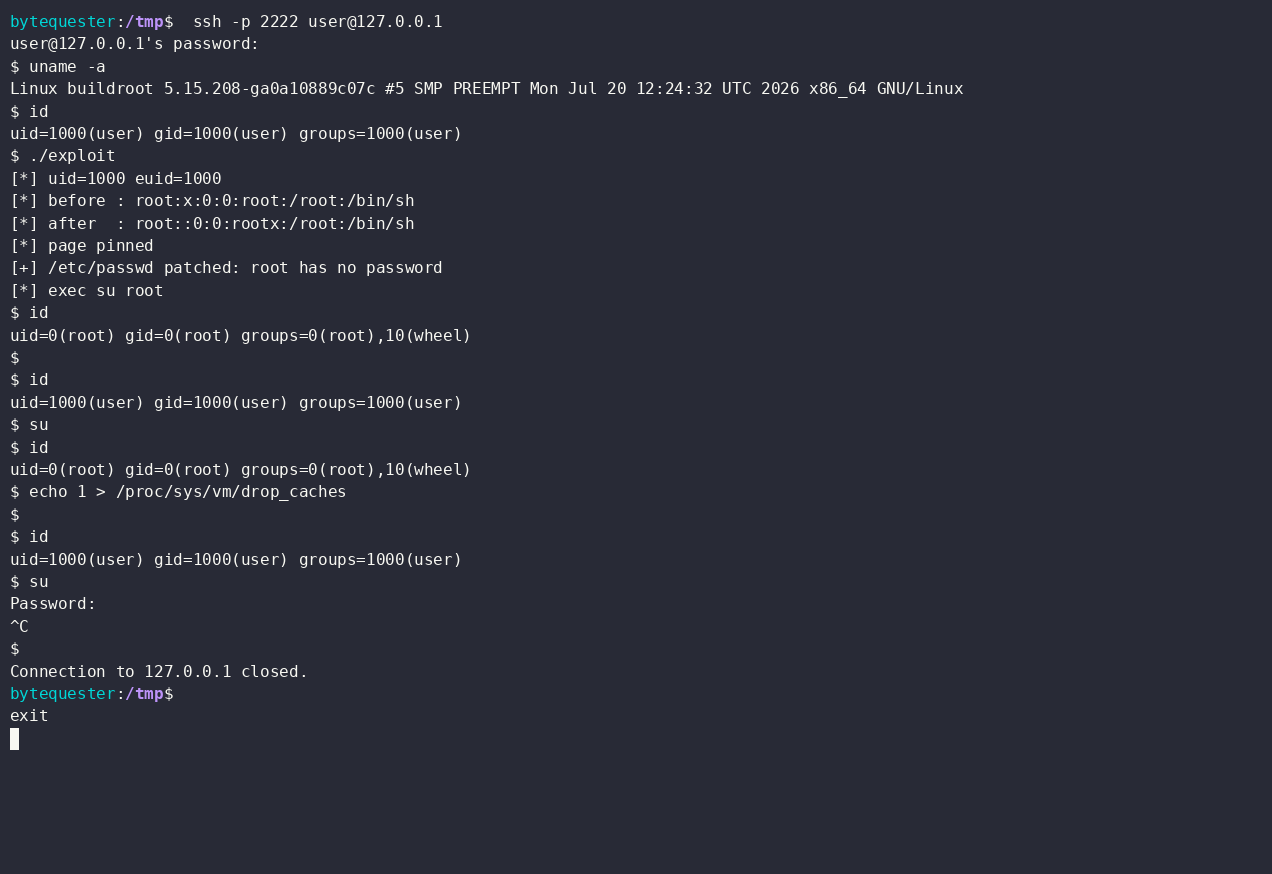 byt3quester/cve-2022-22706-poc
Proof-of-concept exploit for CVE-2022-22706: exploits a Mali GPU kernel driver page-cache write flaw to modify /etc/passwd in memory and obtain a…
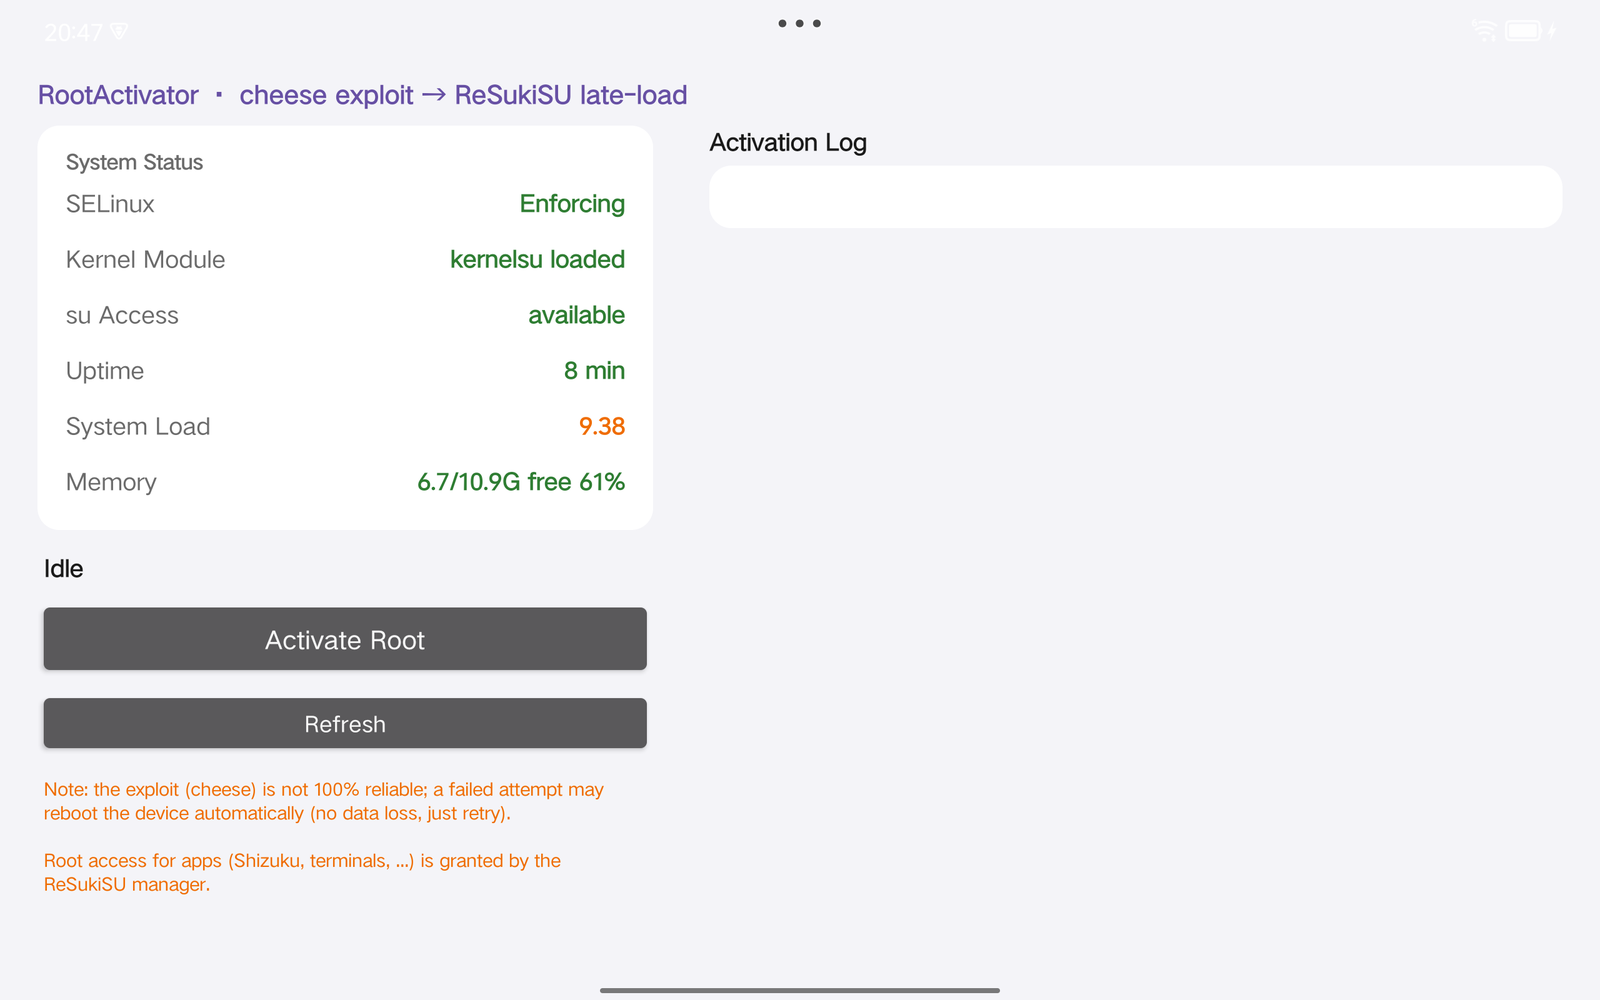 xjoker/lenovo_y700_tb320fc_on_cve-2025-21479
In-memory kernel privilege escalation for Lenovo Legion Y700 2023 (TB320FC) exploiting CVE-2025-21479, a Qualcomm Adreno GPU SMMU flaw, with ReSukiSU…
 fi01/libmsm_cameraconfig_exploit
C exploit for CVE-2013-2595 targeting a kernel memory corruption in Qualcomm MSM camera driver on Android devices, enabling local privilege…
 satirush/cve-2025-14174-poc
Proof-of-Concept exploit for CVE-2025-14174 (EUVD-2025-203113) - Memory corruption in ANGLE allowing out-of-bounds access and RCE in web browsers.…
 hasan-khalil/cve-2020-6514
Exploit for CVE-2020-6514 targeting WebRTC SCTP memory corruption in Android applications. Uses Frida to hook native functions and alter SCTP packets…
 satheesh575555/external_aac_aosp10_r33_cve-2022-20130
Android AAC codec vulnerability analysis and patch for CVE-2022-20130, focusing on memory corruption in external AAC library.
 lsw29475/cve-2020-0022
Exploit for CVE-2020-0022, an Android Bluetooth RCE vulnerability. Provides proof-of-concept code for testing and understanding the memory corruption…
 satheesh575555/libhwbinder_aosp10_r33_cve-2020-0136
Exploit for CVE-2020-0136, a use-after-free vulnerability in Android's libhwbinder, demonstrating memory corruption and potential privilege…
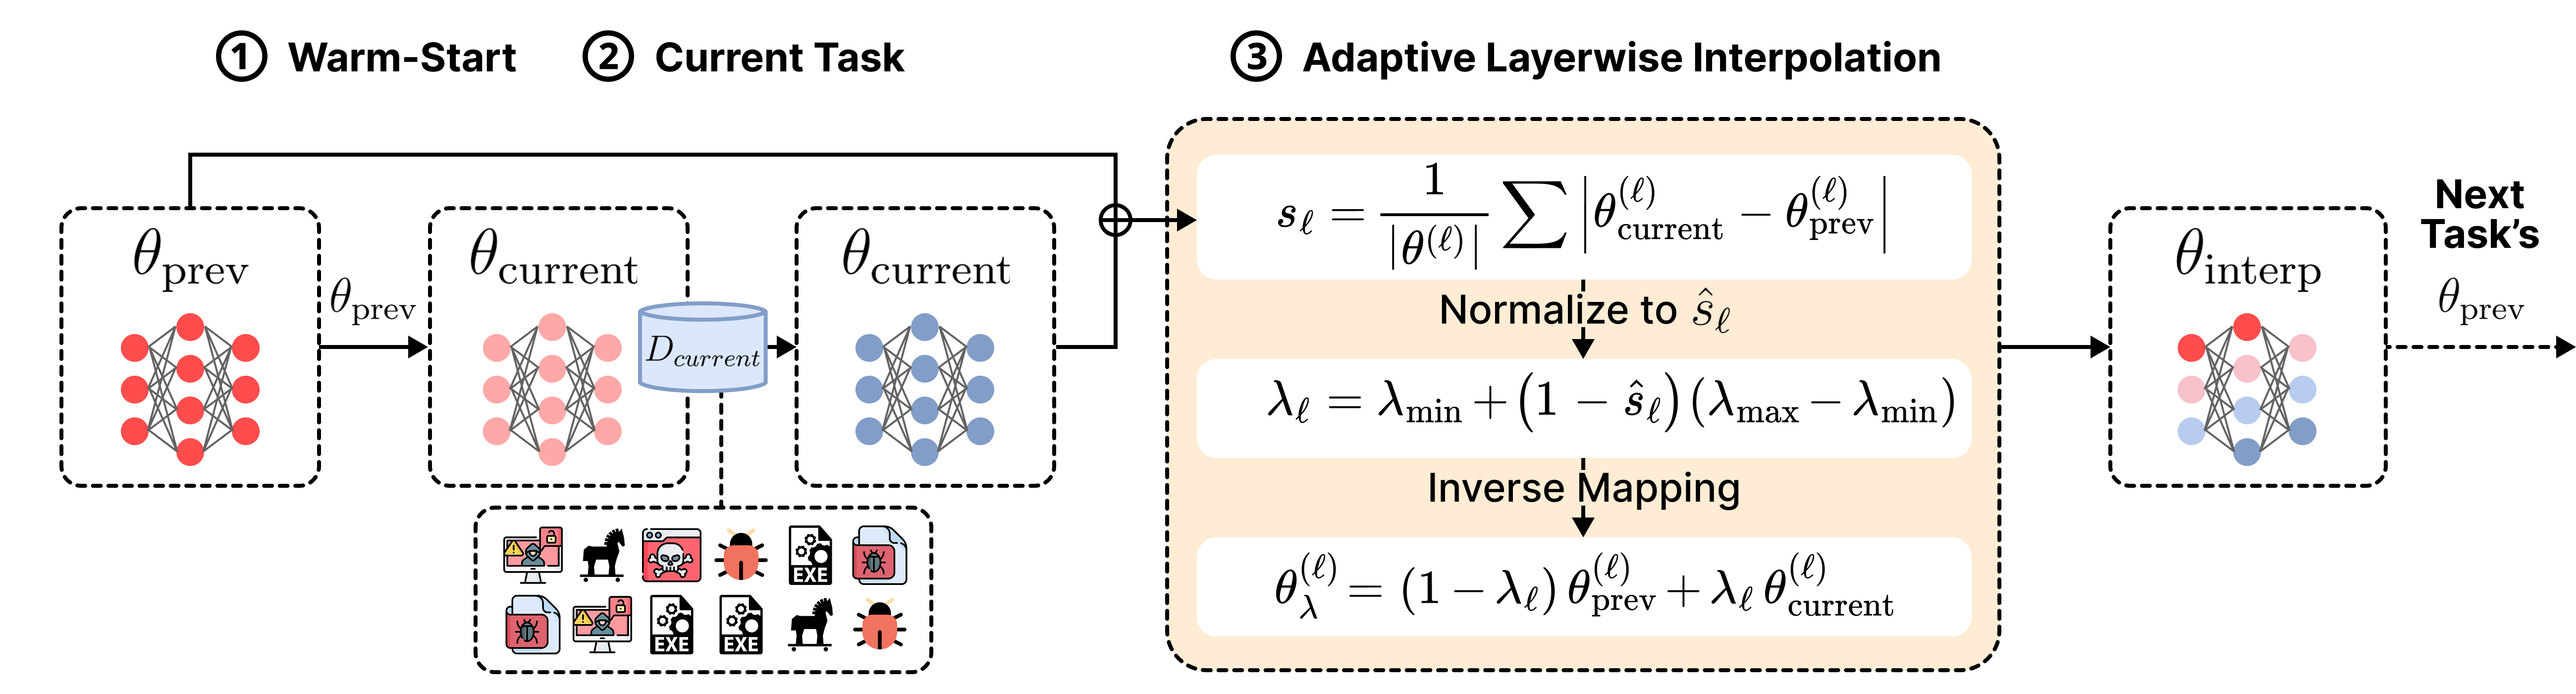 iqsec-lab/freemoca
Memory-free continual learning framework for malware classification using mode connectivity-based interpolation. Supports class-incremental and…
 kangtastic/cve-2019-2215
Temproot for Pixel 2 and Pixel 2 XL via CVE-2019-2215
 nestle19/cve-2019-2215
Android kernel exploit for CVE-2019-2215, a use-after-free in the Binder driver, enabling privilege escalation to root via memory corruption and cred…
 lntrx/cve-2021-28663
Proof-of-concept exploit for CVE-2021-28663, a design flaw in the Mali GPU Android kernel driver enabling arbitrary read via memory alias and…
 thomasking2014/slides
Curated collection of security conference slide decks covering Android rooting, kernel exploitation, browser memory corruption, JIT mitigations, and…
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 sterrasec/apk-medit
memory search and patch tool on debuggable apk without root & ndk
 quarkslab/cve-2020-0069_poc
Proof-of-concept exploit for CVE-2020-0069 on Mediatek Android devices, enabling kernel memory read/write and syscall hooking for privilege…
 vichhka-git/renef-skills
Agent Skill for operating renef.io — Android ARM64 dynamic instrumentation: hook native/Java, patch memory, trace syscalls, bypass SSL pinning/root…