
LSPromise
 lsposed/lspromise
Android complete exploit chain that enables privilege escalation from a local untrusted app to root/kernel, combination of CVE-2026-49881 and…
android-securityexploitationexploit-frameworks+4
432
lsposed/lspromiseAndroid complete exploit chain that enables privilege escalation from a local untrusted app to root/kernel, combination of CVE-2026-49881 and…
 retme7/cve-2014-7911_poc
Local root exploit for Nexus5 Android 4.4.4(KTU84P)
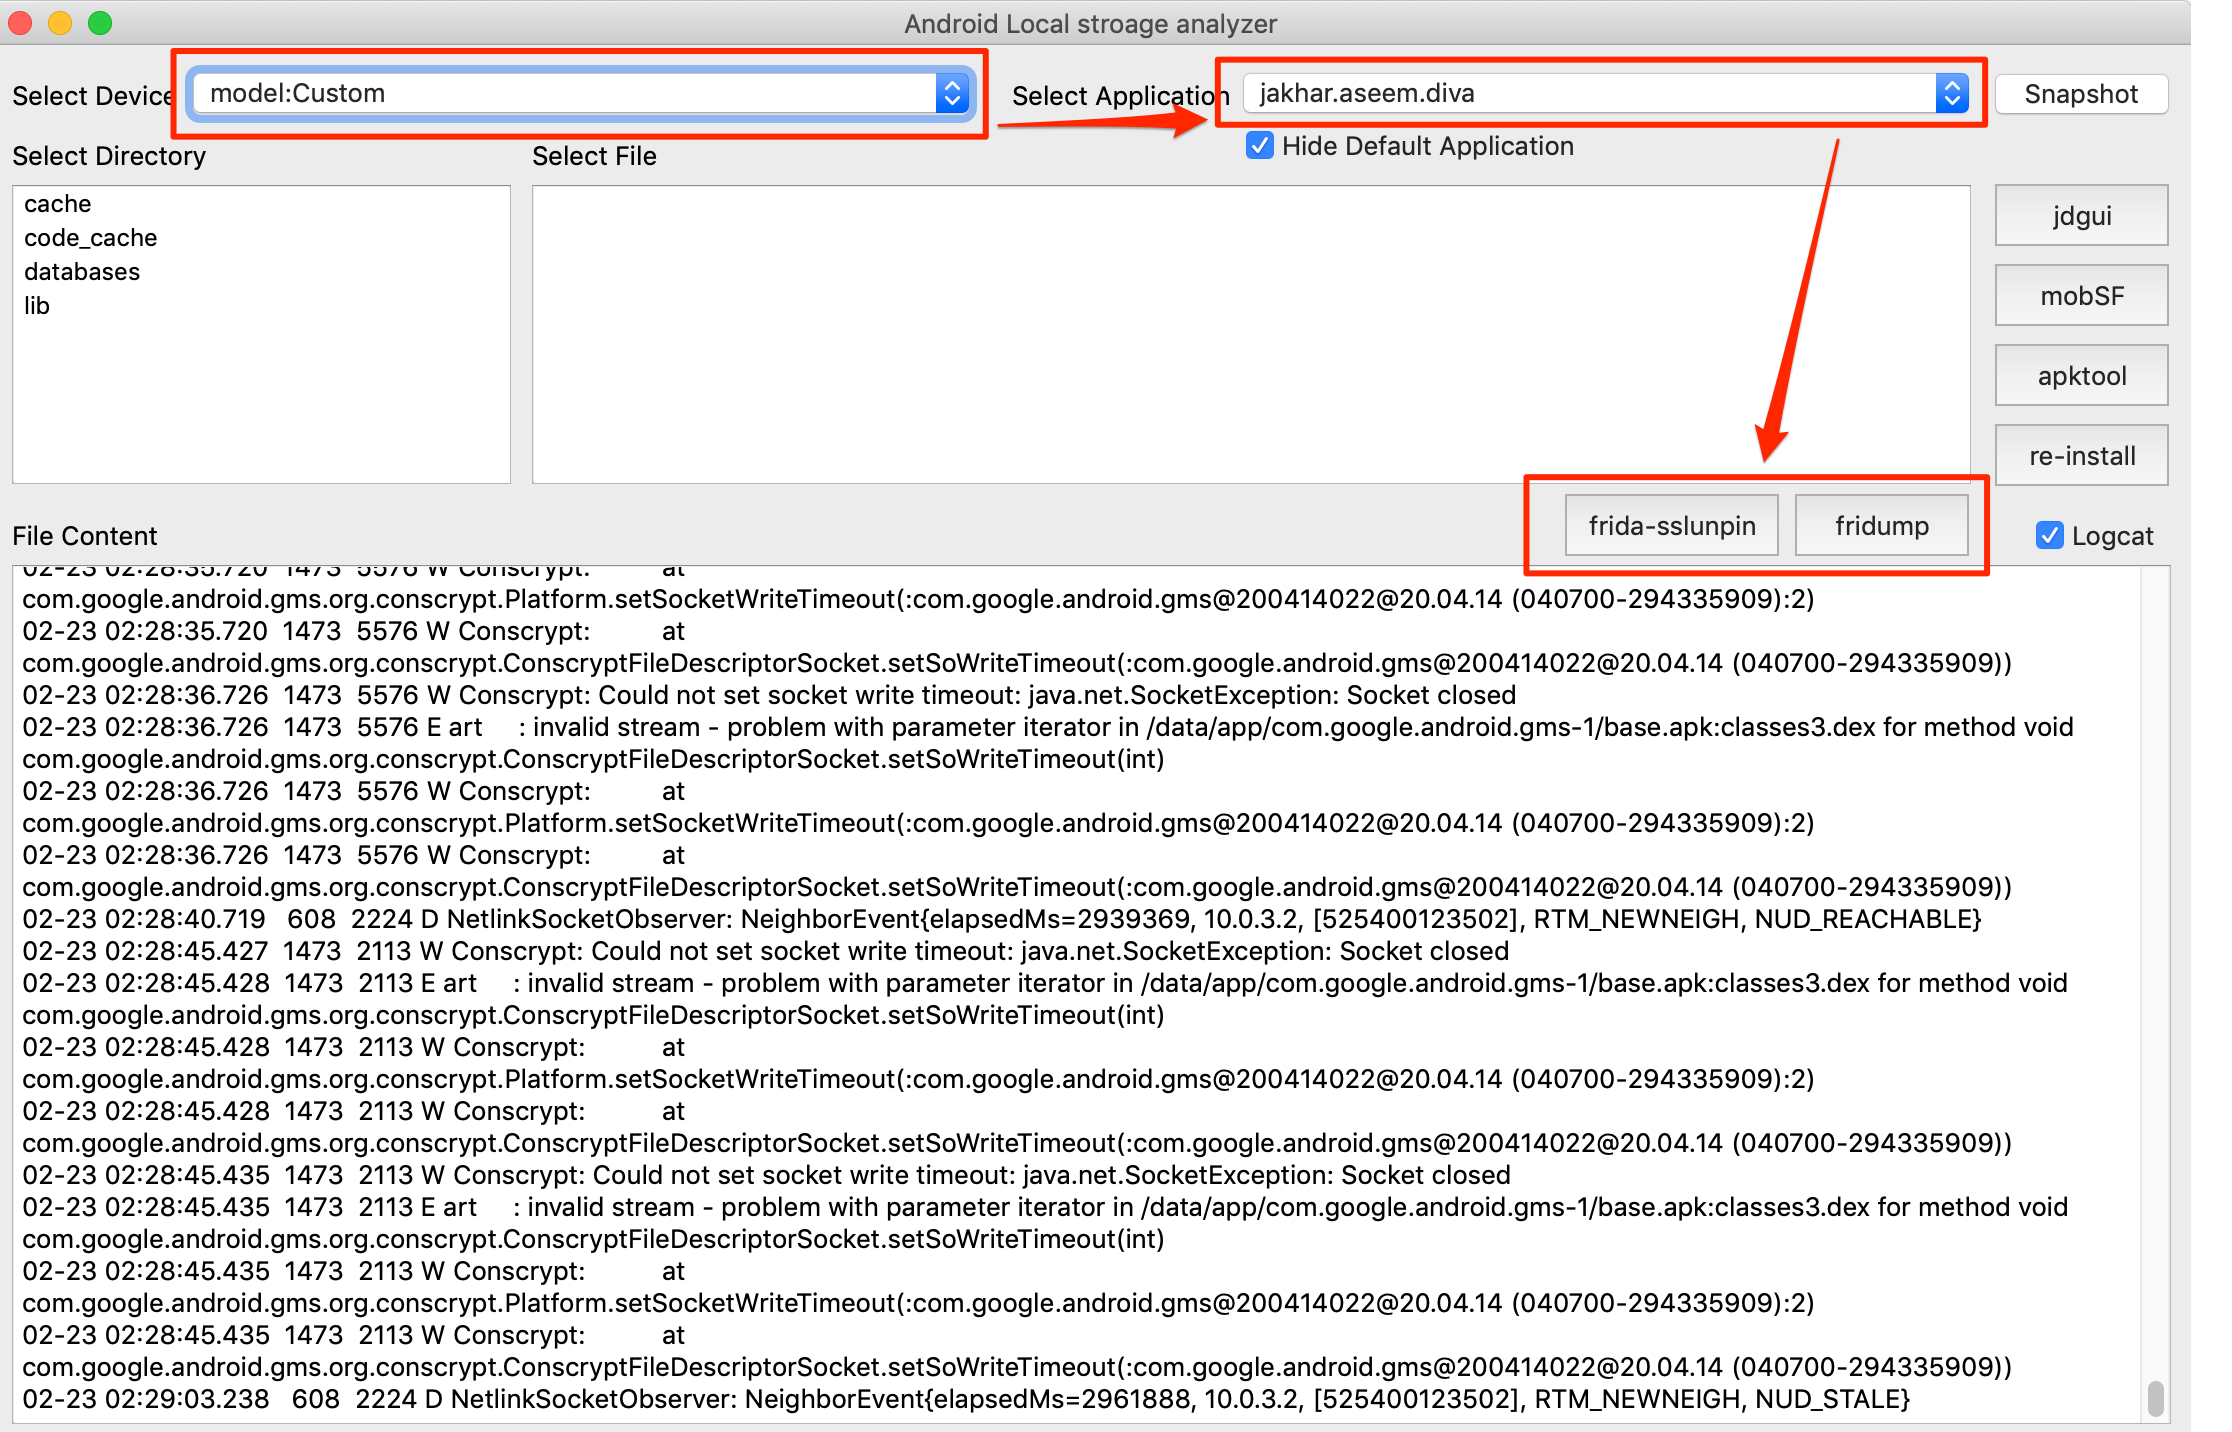 notsosecure/android_application_analyzer
The tool is used to analyze the content of the android application in local storage.
 j4nn/cve-2020-0041
Local privilege escalation exploit for Android kernel vulnerability CVE-2020-0041, with portability across devices and kernel versions.
 0x742/cve-2020-0082-externalvibration
This repo contains a proof-of-concept for 📱🚀👑⚡, a deserialization vuln for local escalation of privilege to system_server in Android 10. This…
 jaf0rk/cve-2023-20938
Technical analysis and proof-of-concept exploit for CVE-2023-20938, a use-after-free vulnerability in the Android kernel's Binder driver, enabling…
 jcalabres/root-exploit-pixel3
Local privilege escalation exploit for Pixel 3 (CVE-2020-0041) that disables SELinux and spawns a root shell via kernel memory corruption and offset…
 sorrow404null/cve-2026-43499-rmx5200
Android 16 local privilege escalation exploit for realme RMX5200 using LD_PRELOAD-based preload.so chain to achieve temporary root access via…
 bartixxx32/cve-2026-43499-oneplus15
Educational proof-of-concept for Android 16 local privilege escalation on OnePlus 15, featuring kernel offset detection, target generation, and…
 oopnv70-lab/ghostlock-aak-apk
GhostLock AAK Launcher - CVE-2026-43499 Linux kernel rtmutex stack UAF local privilege escalation trigger (GPLv3)
 ele7enxxh/cve-2014-7911
Proof-of-concept exploit for Android local privilege escalation (CVE-2014-7911) targeting Nexus5 with ROP chain and heap spraying to gain system uid.
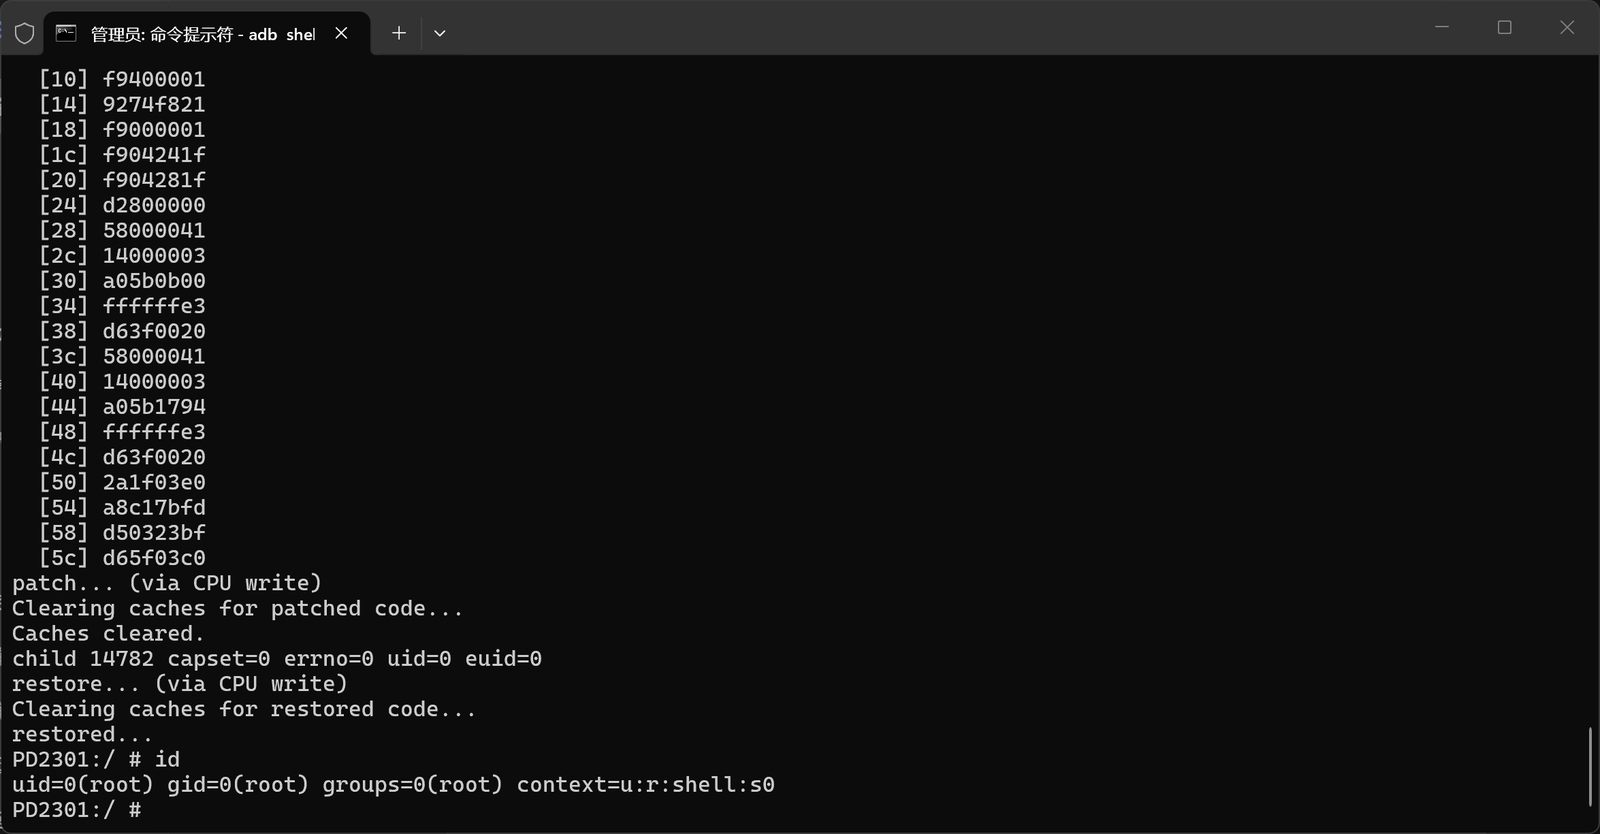 qingizi7/cve-2025-21479_iqooneo8
Local root exploit for CVE-2025-21479 (Adreno KGSL) on iQOO Neo8 (SM8475) - physical memory r/w, disables SELinux, spawns root shell
 fi01/libmsm_cameraconfig_exploit
C exploit for CVE-2013-2595 targeting a kernel memory corruption in Qualcomm MSM camera driver on Android devices, enabling local privilege…
 soralis0912/cve-2026-43499-aristotle
Local privilege escalation exploit for Xiaomi XIG04 (Android 12) via CVE-2026-43499 kernel use-after-free. Data-only direct-root technique with MTE…
 vaginessa/cve-2020-0041-pixel-3a
Local privilege escalation exploit for Android Binder bug CVE-2020-0041 (Pixel 3a)
 dingo97/cve-2026-20516
Write-up and ADB proof of concept for CVE-2026-20516, a confused deputy flaw in MediaTek Android TV MiracastService allowing local Wi-Fi Direct state…
 soralis0912/cve-2026-43499-warhol-root
Local privilege escalation exploit targeting CVE-2026-43499 for the Xiaomi 17T Pro (warhol) on Android 16 with MediaTek MT6993 SoC.
 aemmitt-ns/pacpoc
A local PoC exploit for CVE-2019-2205