

apkvuln
 josue87/apkvuln
Static analysis of APKs with regular expressions
android-securitymobile-app-pentestingstatic-analysis+1
josue87/apkvulnStatic analysis of APKs with regular expressions
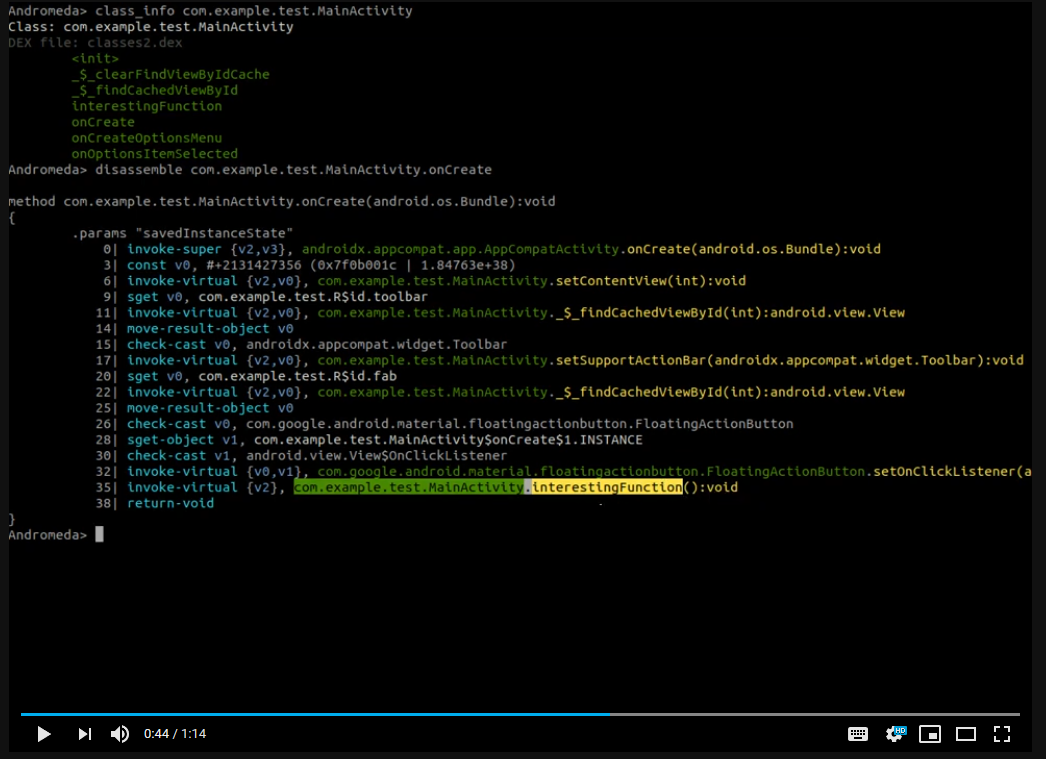 secrary/andromeda
C/C++ interactive reverse engineering tool for Android applications, enabling fast static analysis and binary inspection of APK files.
 idanr1986/cuckoo-droid
CuckooDroid - Automated Android Malware Analysis with Cuckoo Sandbox.
 seqred-s-a/cve-2019-14220
Arbitrary file read in BlueStacks
 pealeap/cve-2026-21045_and_cve-2026-21048
Generates crafted TIFF/DNG files to trigger out-of-bounds writes in Samsung's libimagecodec.quram.so, including binary analysis and reproduction…
 ejfkdev/ddc
DEX → Java decompiler in Rust — fast, progressive analysis, bilingual CLI
 0xdsm/apepe
Extracts app settings, permissions, deeplinks, and SSL pinning bypass suggestions from Android APK files via static analysis of AndroidManifest.xml,…
 gmh5225/androiddrivesignity
AndroidDriveSignity is a Python utility designed to bypass driver signature verification in Android kernel(ARMv8.3), facilitating the loading of…
 bend0us/dexloader
A demo Android project showcasing dynamic DEX loading using DexClassLoader, PathClassLoader, and in-memory execution. For educational purposes only.
 jakev/pyxamstore
Python utility for parsing Xamarin AssemblyStore blob files
 skorpion96/cve-2026-40000
A poc for a vulnerability in ZTE File Manager (zte.com.cn.filer) which allows to read arbitrary files from other apps as the privileges of this file…
 haxatron/cve-2022-0219
Proof-of-concept exploit for CVE-2022-0219, an XXE vulnerability in Jadx that allows local file disclosure when exporting malicious APK files via the…
 idanshechter/cve-2017-13208-scanner
Python script using r2pipe to detect CVE-2017-13208 in Android libnetutils.so by checking for missing dhcp_size validation via static binary analysis.
 niklashigi/apk-mitm
🤖 A CLI application that automatically prepares Android APK files for HTTPS inspection
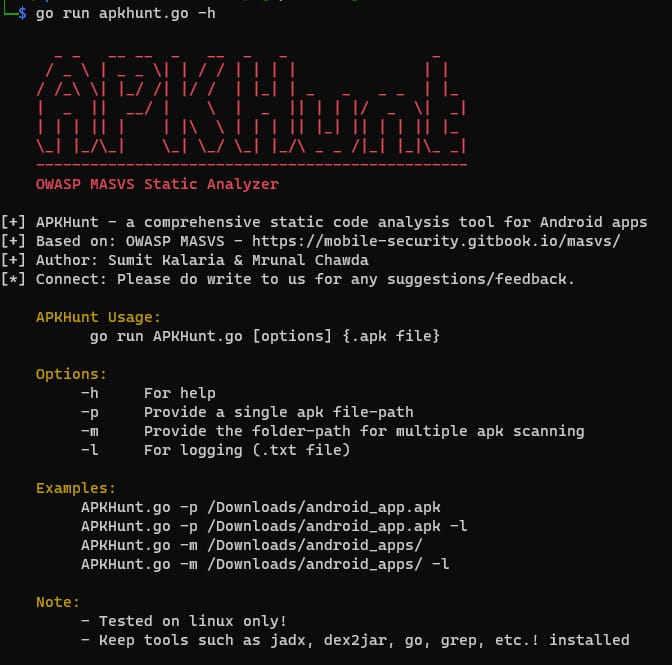 cyber-buddy/apkhunt
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…
 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
 0x742/noia
Web-based tool for browsing mobile application sandboxes, previewing SQLite databases and binary files, and downloading app data via Frida…
 julio-cfa/poc-es-file-explorer-cve-2019-6447
Bash PoC script exploiting CVE-2019-6447 in ES File Explorer to list files, photos, videos, apps, and download files from vulnerable Android devices.