

androidqf
 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
android-securitydata-recoverydigital-forensics+4
321
mvt-project/androidqfandroidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
 aancw/sslpindetect
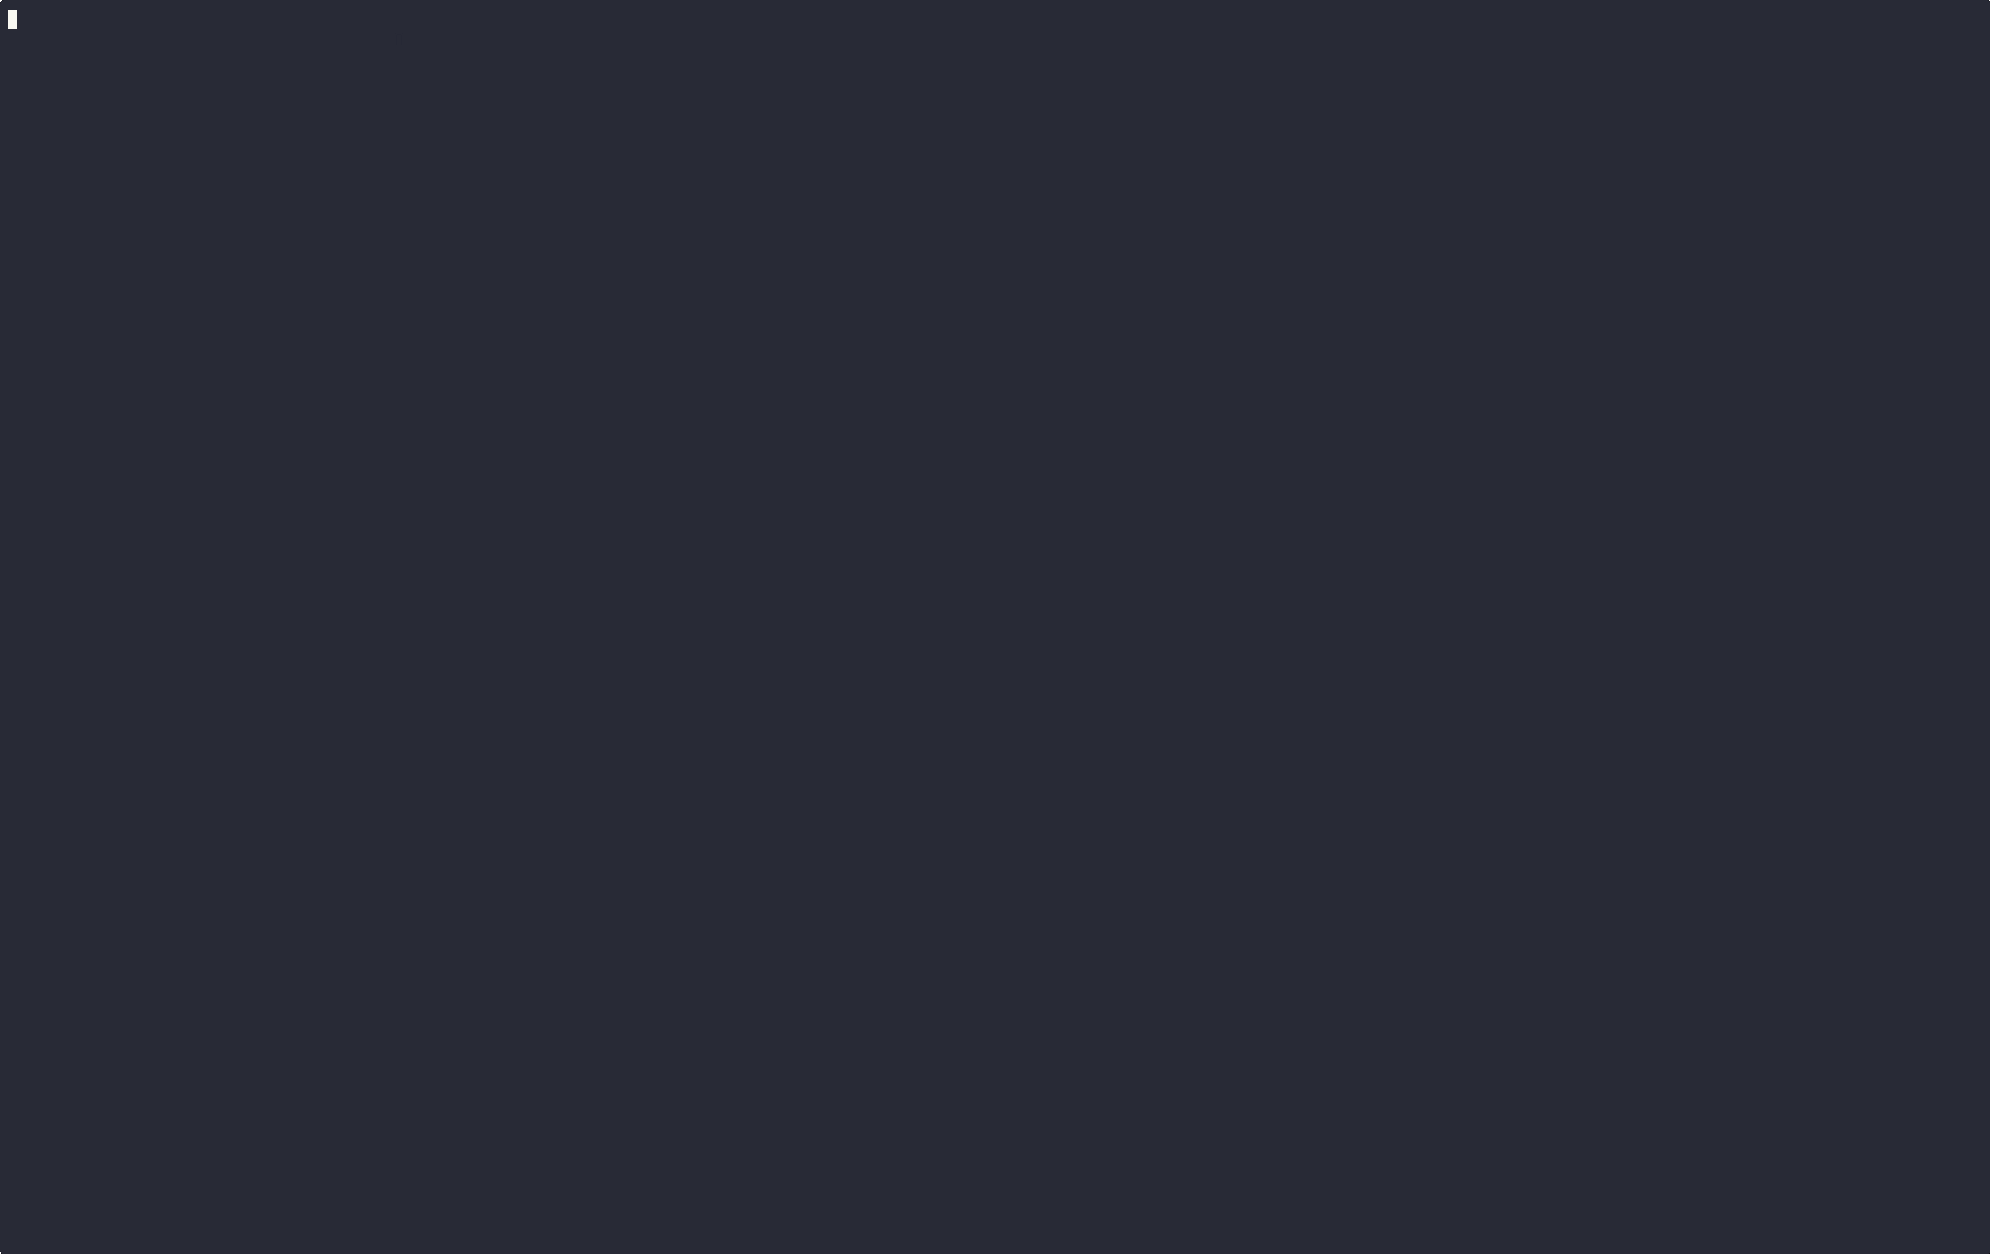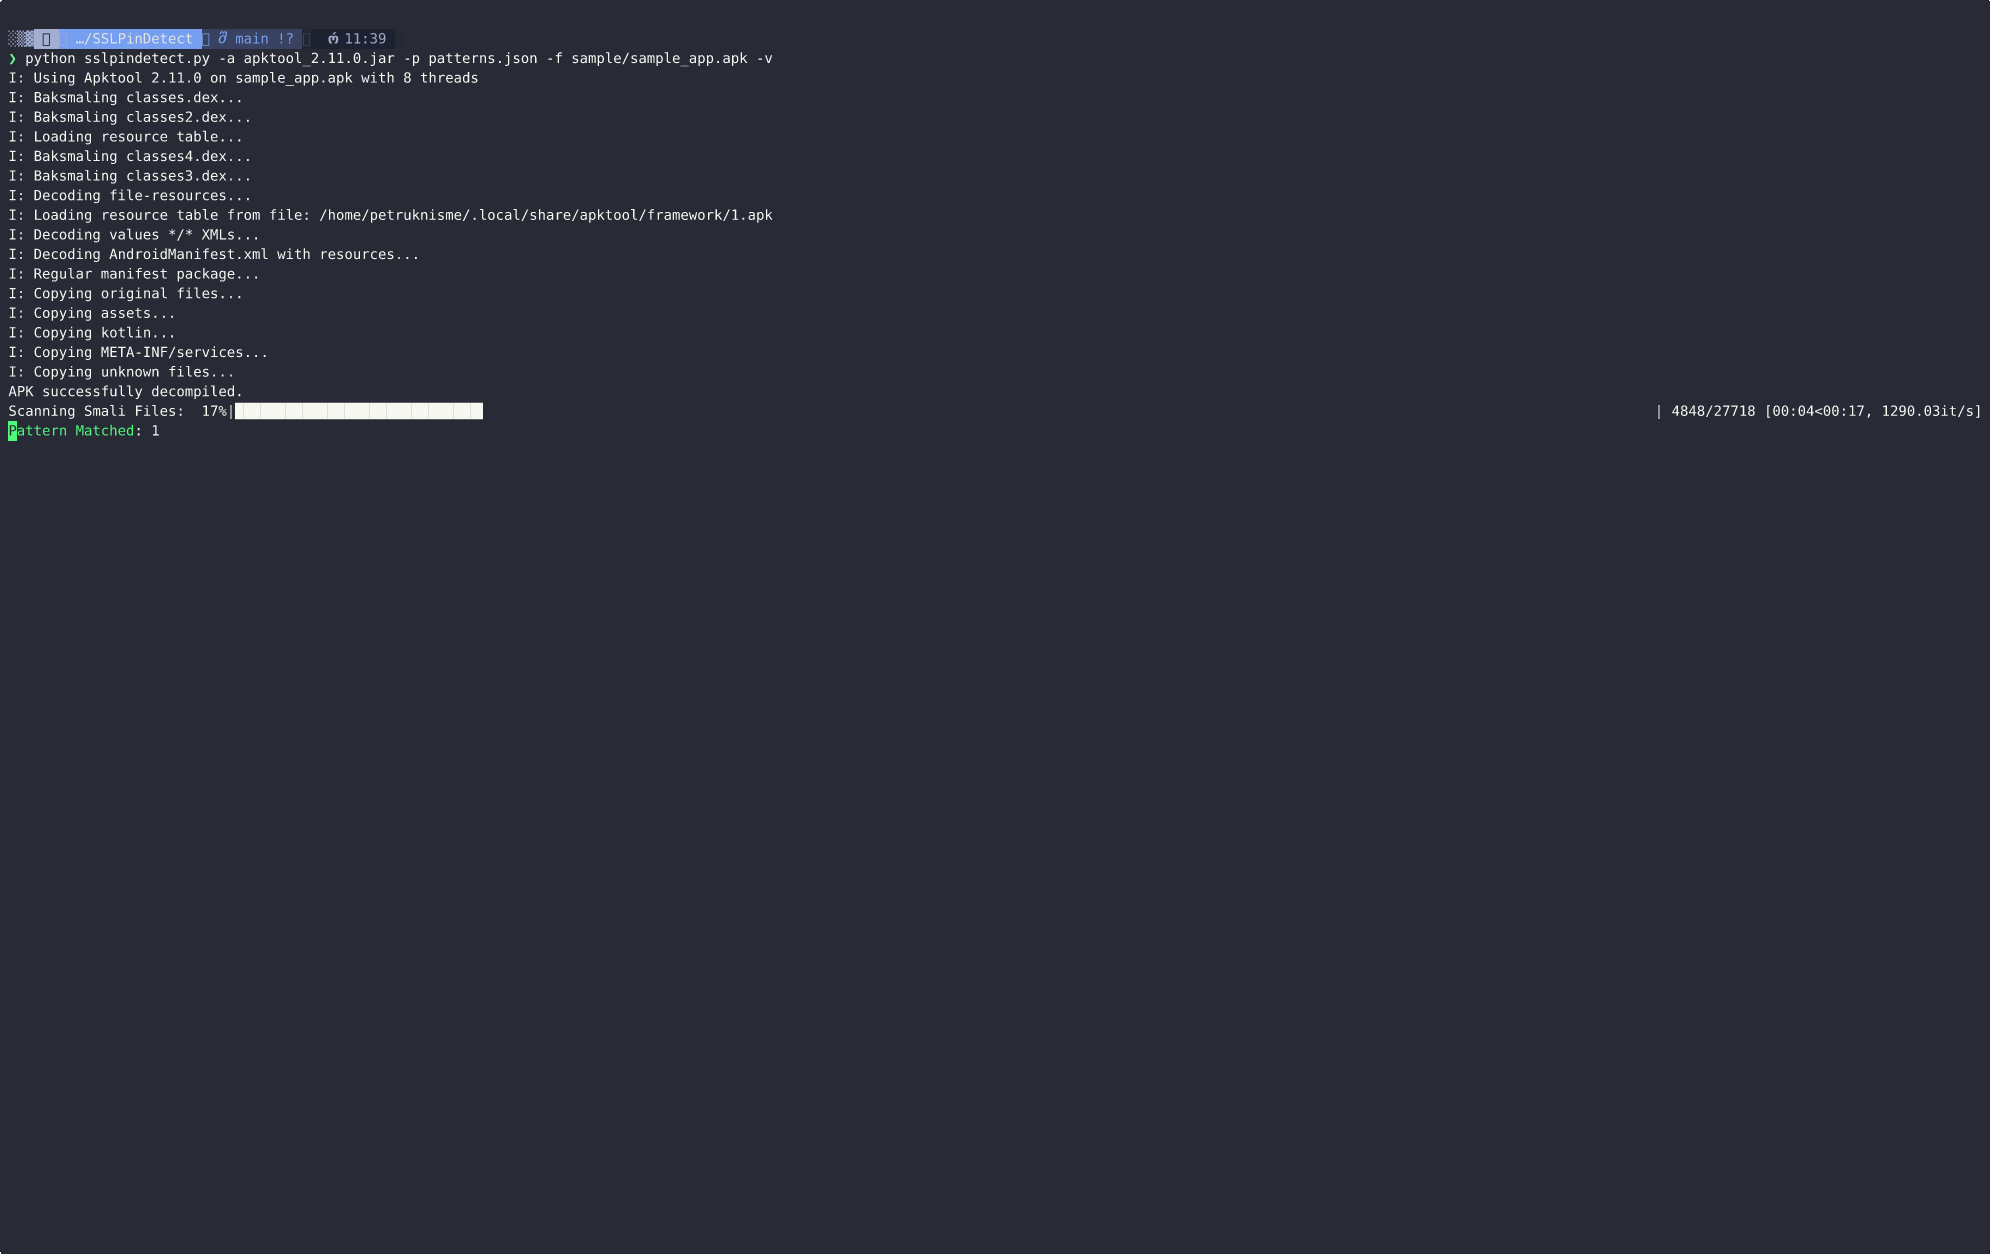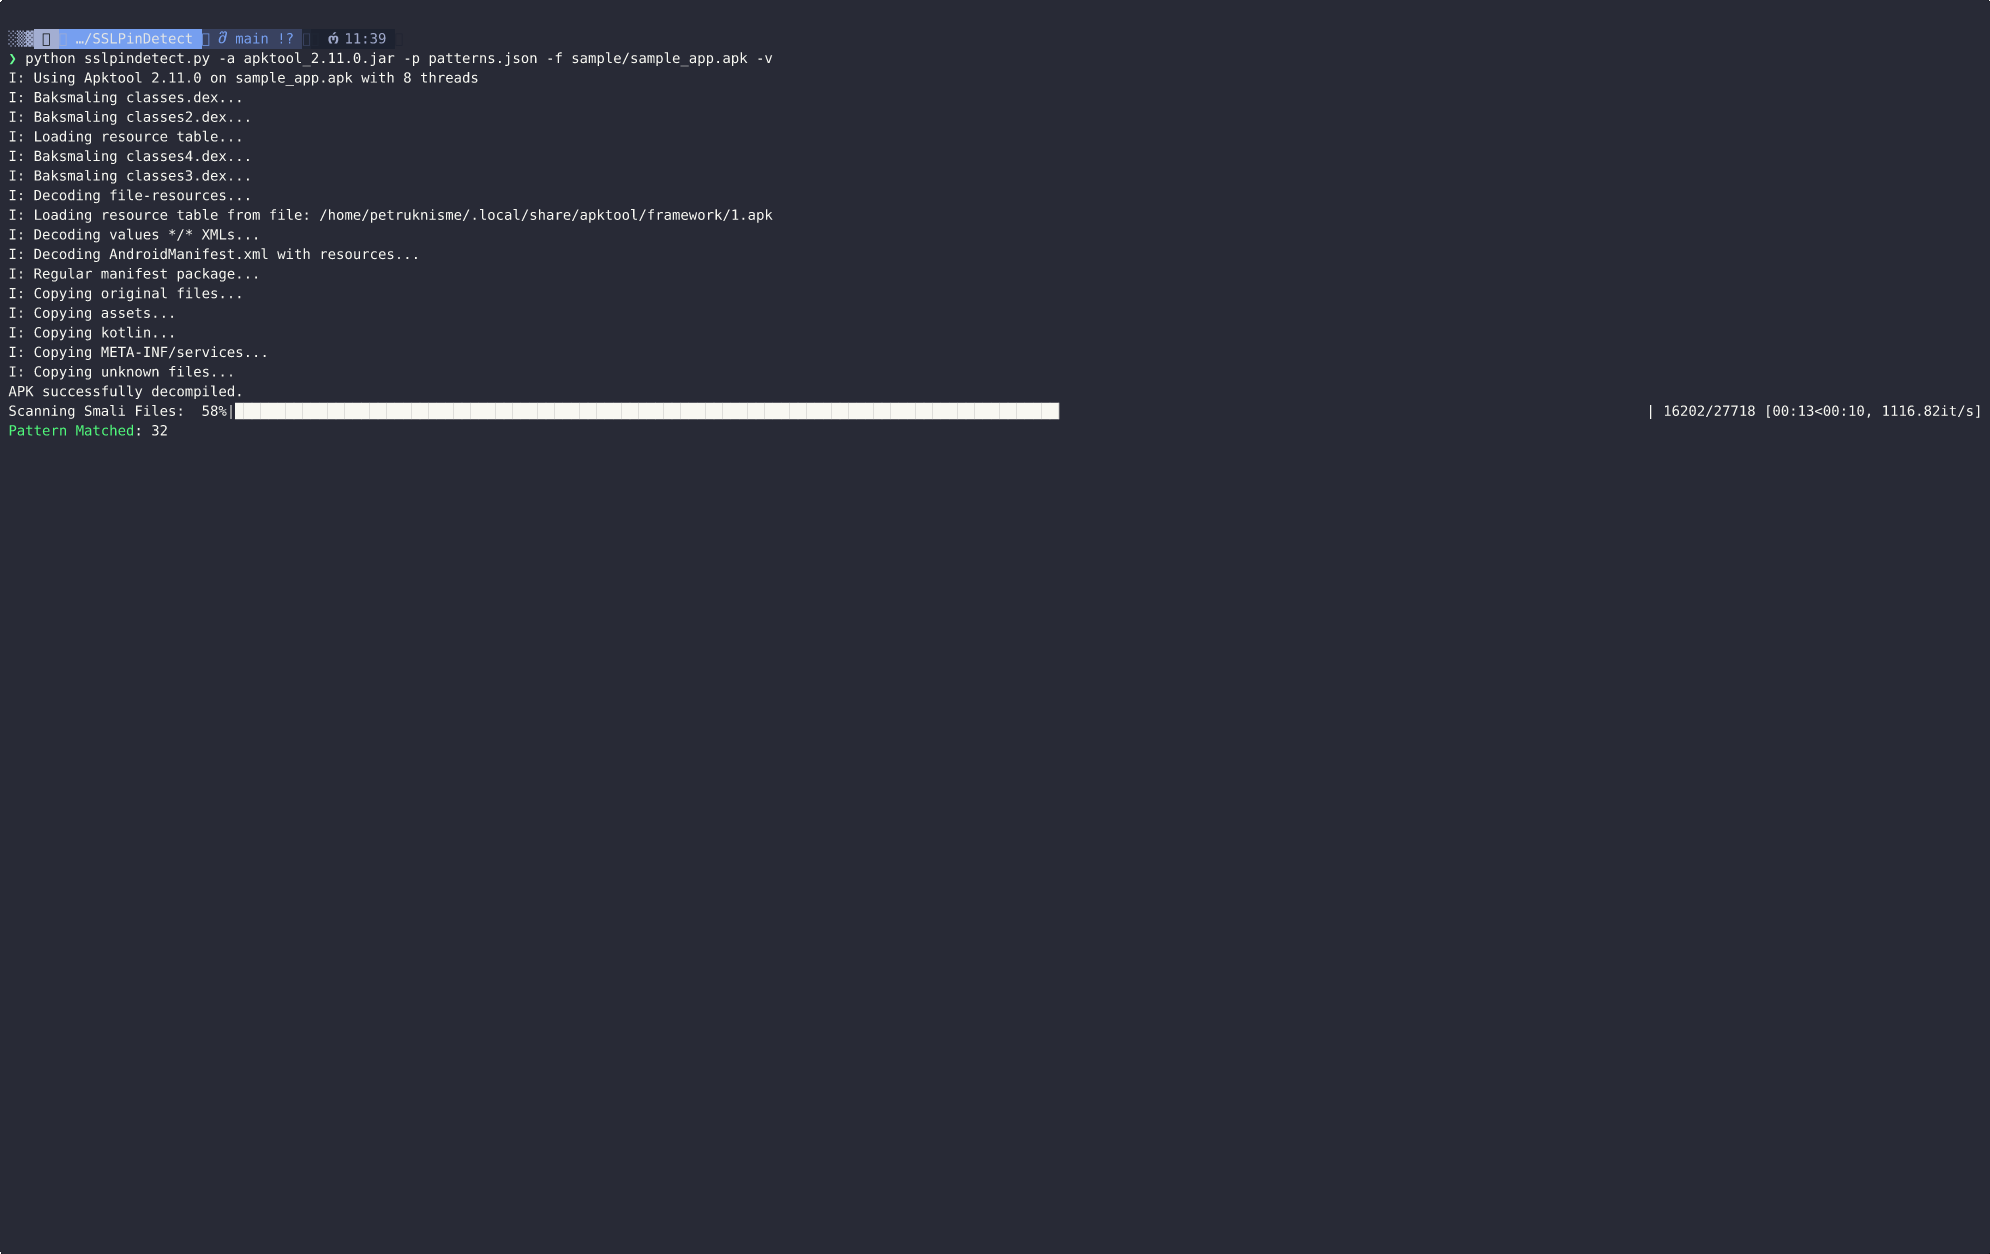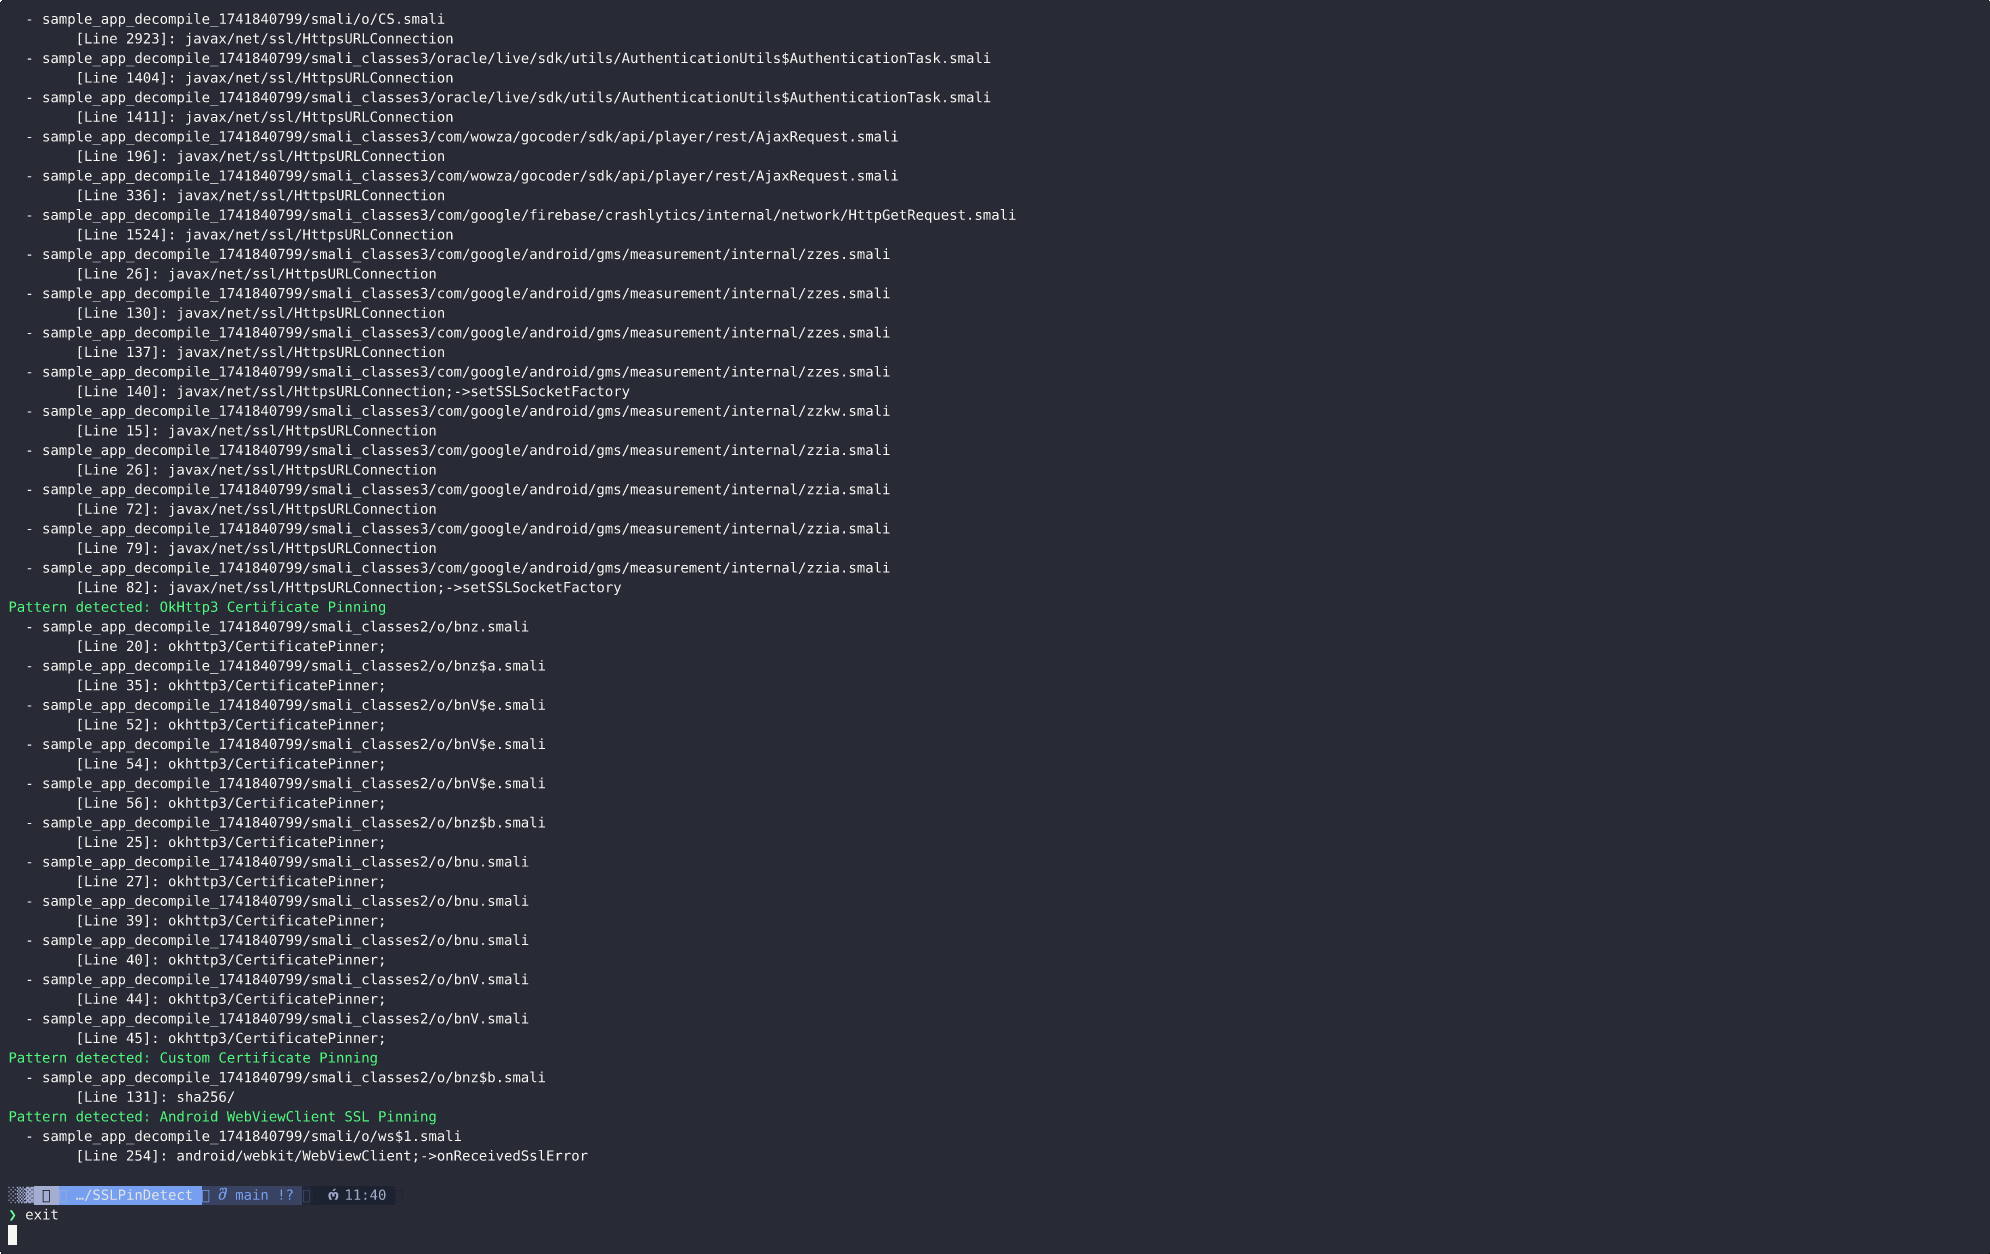
SSLPinDetect is a tool for analyzing Android APKs to detect SSL pinning implementations by scanning for known patterns in decompiled code. It helps…
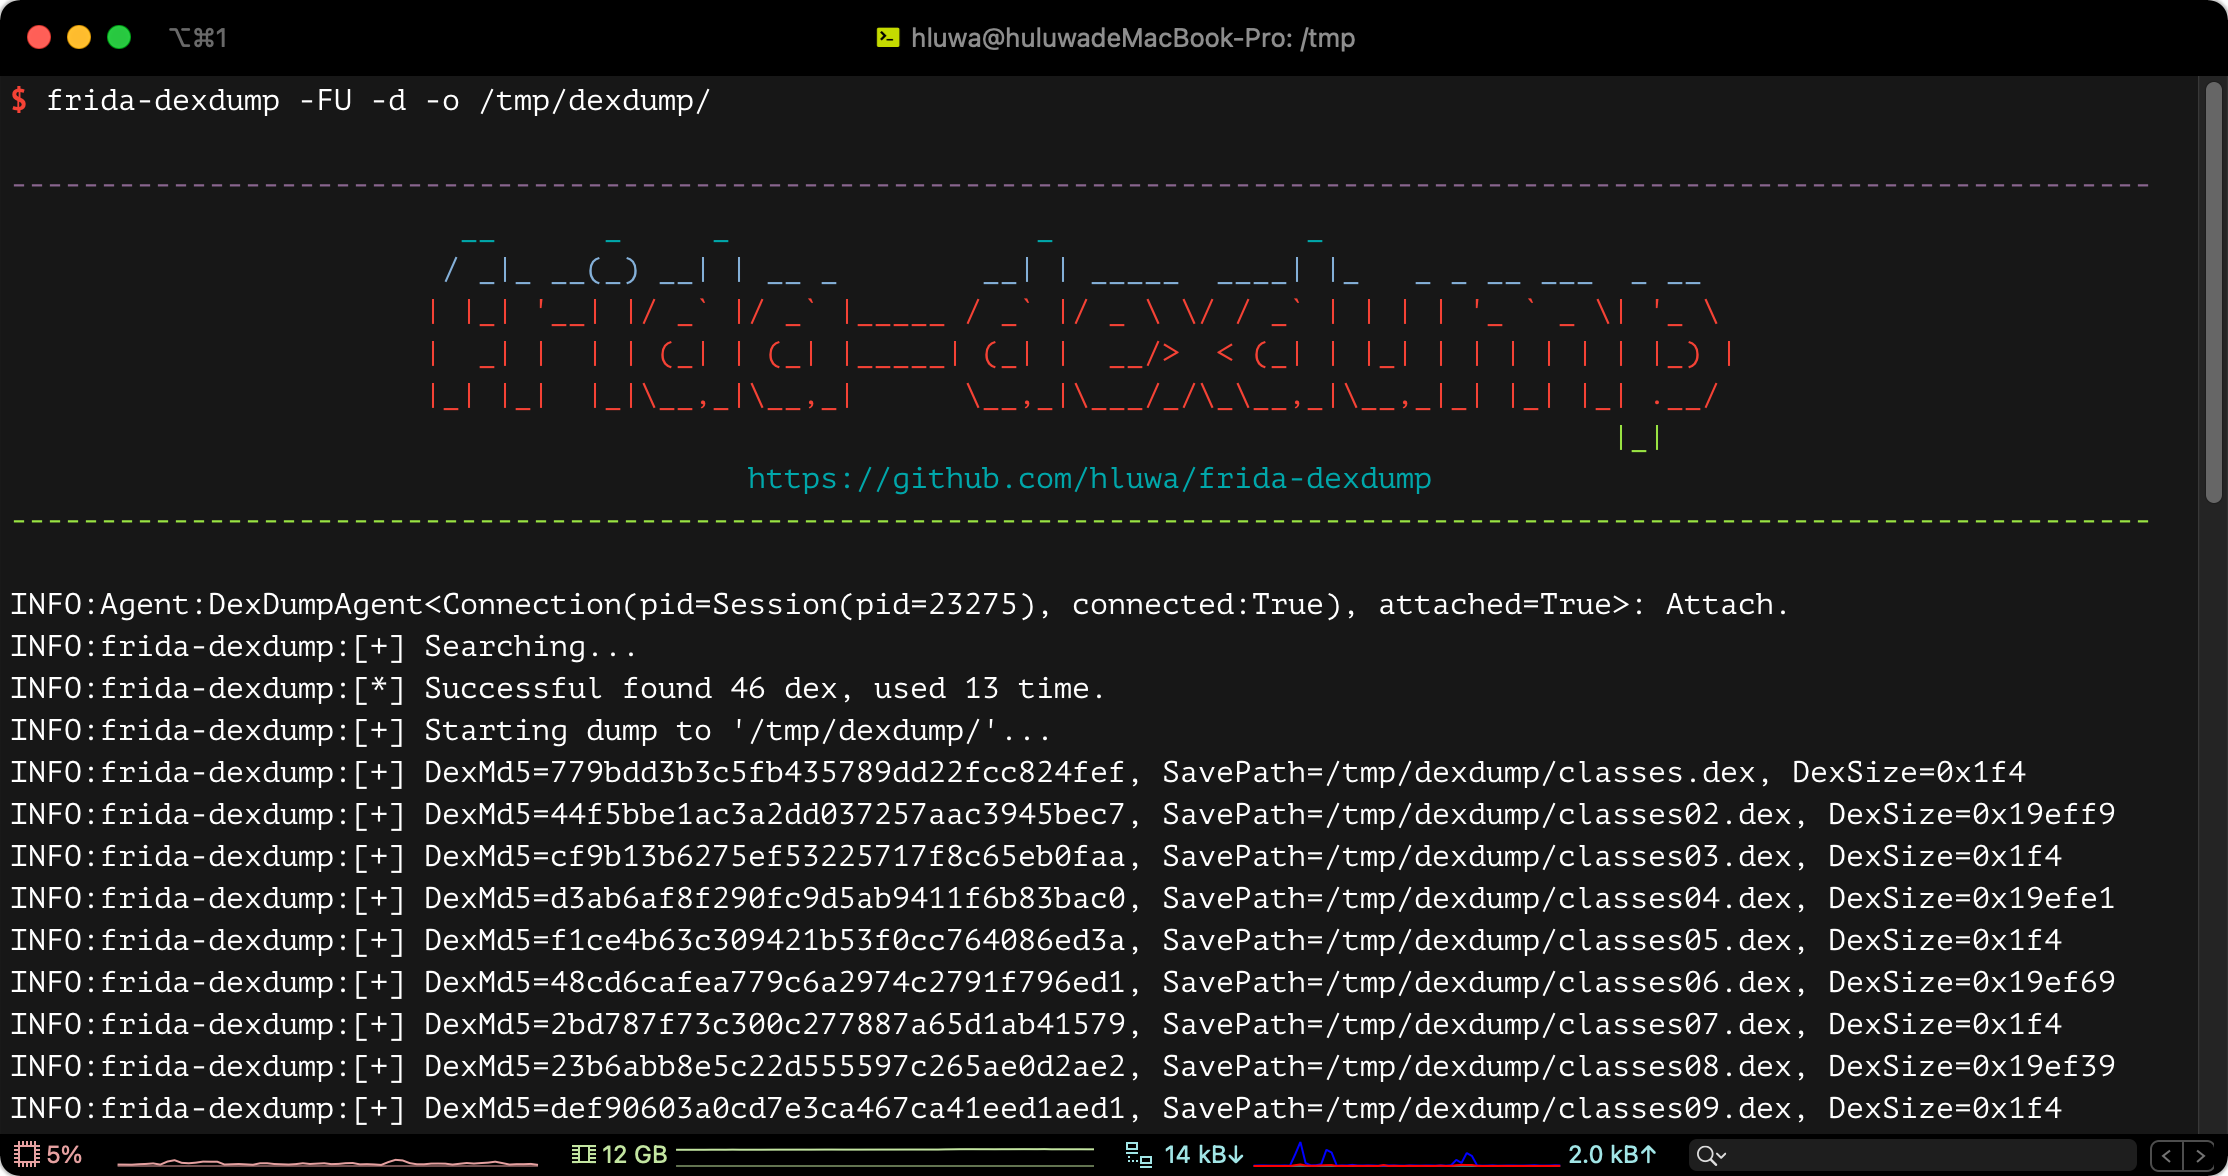 hluwa/frida-dexdump
A frida tool to dump dex in memory to support security engineers analyzing malware.
 rscloura/doldrums
A Flutter/Dart reverse engineering tool
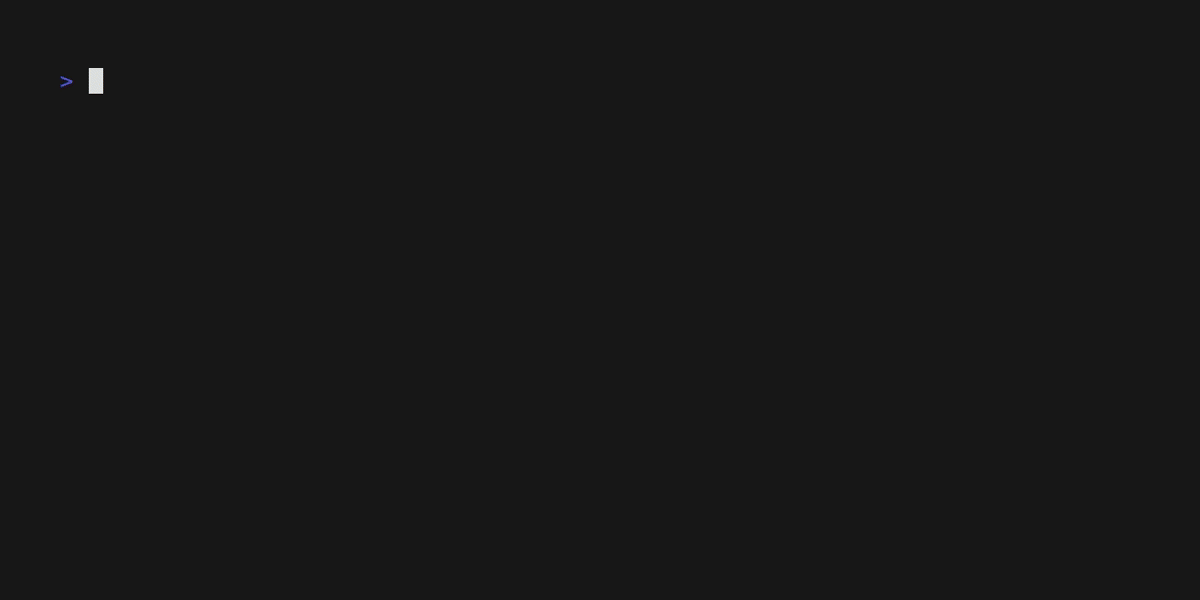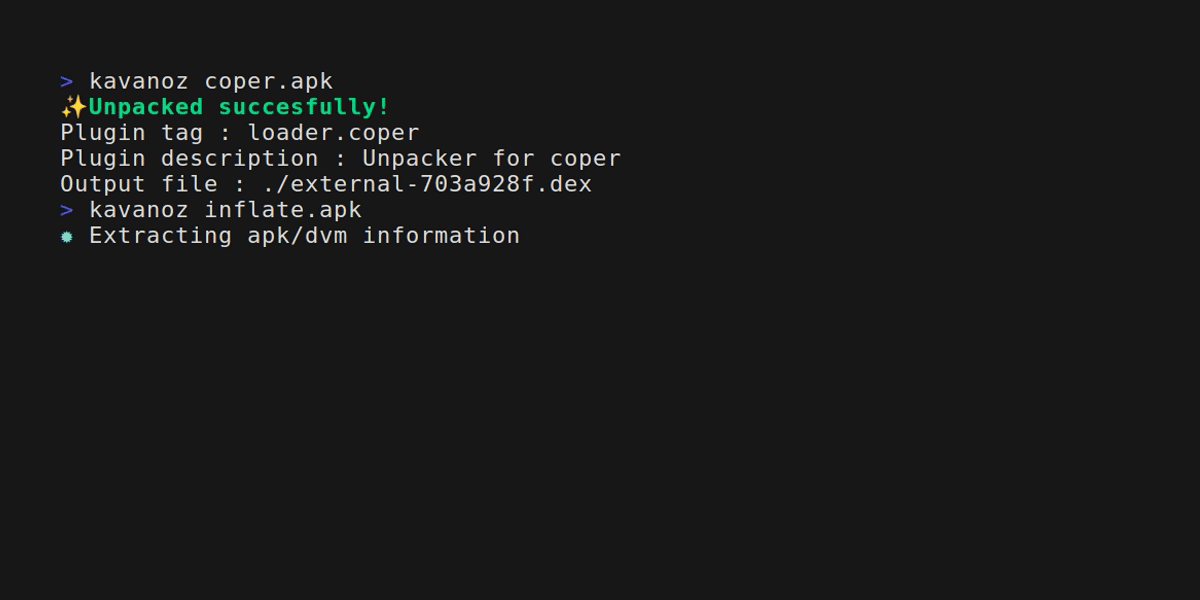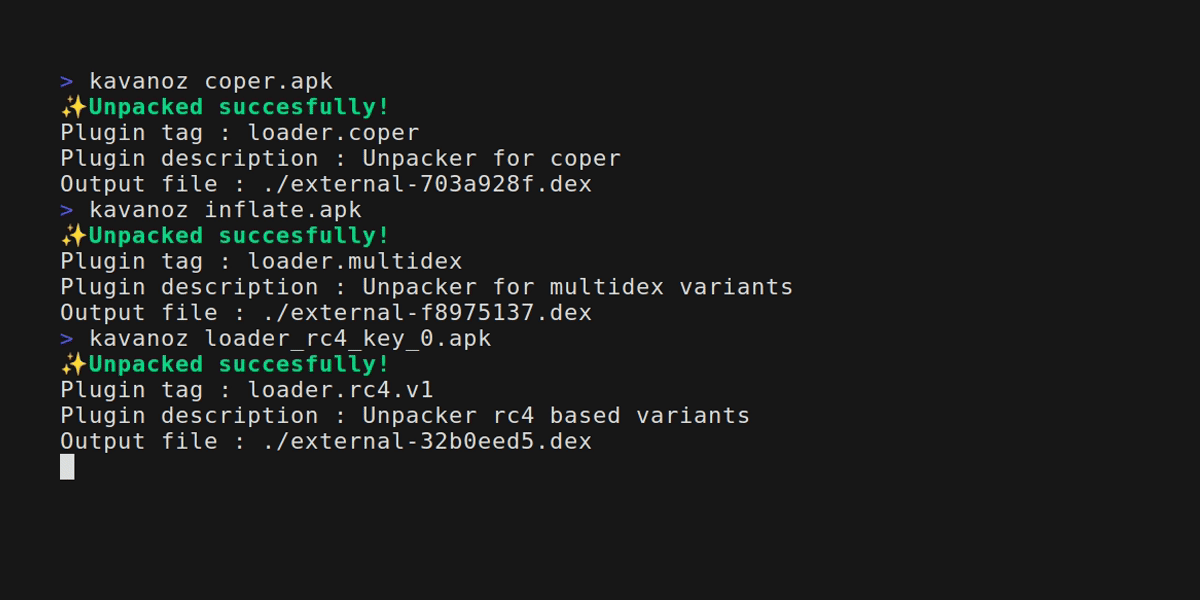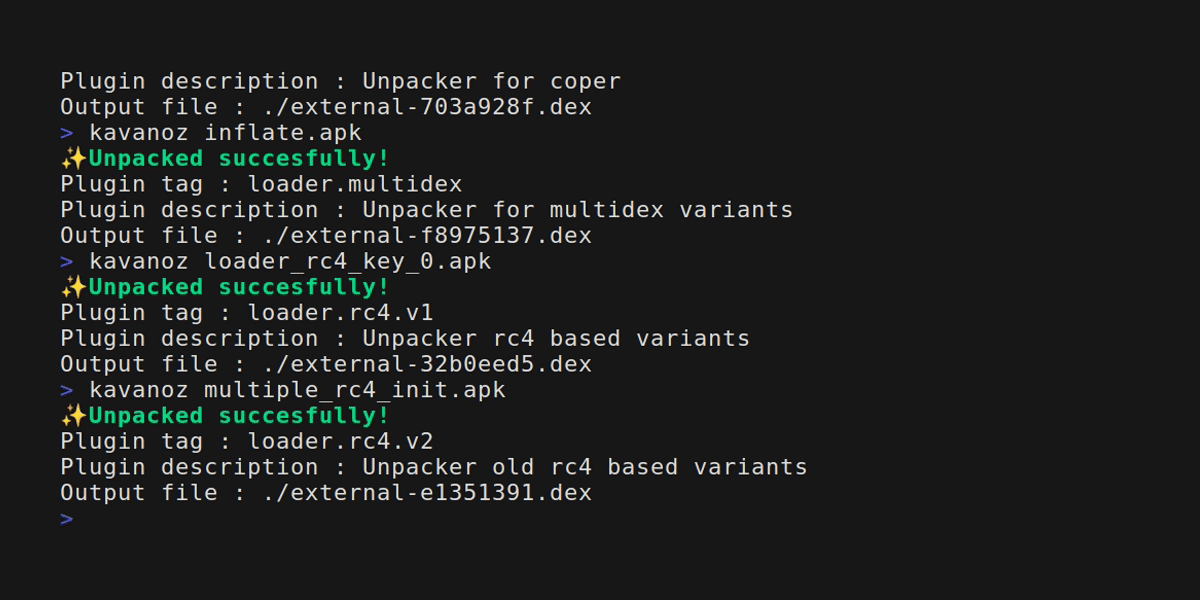 eybisi/kavanoz
Statically unpacking common android banker malware.
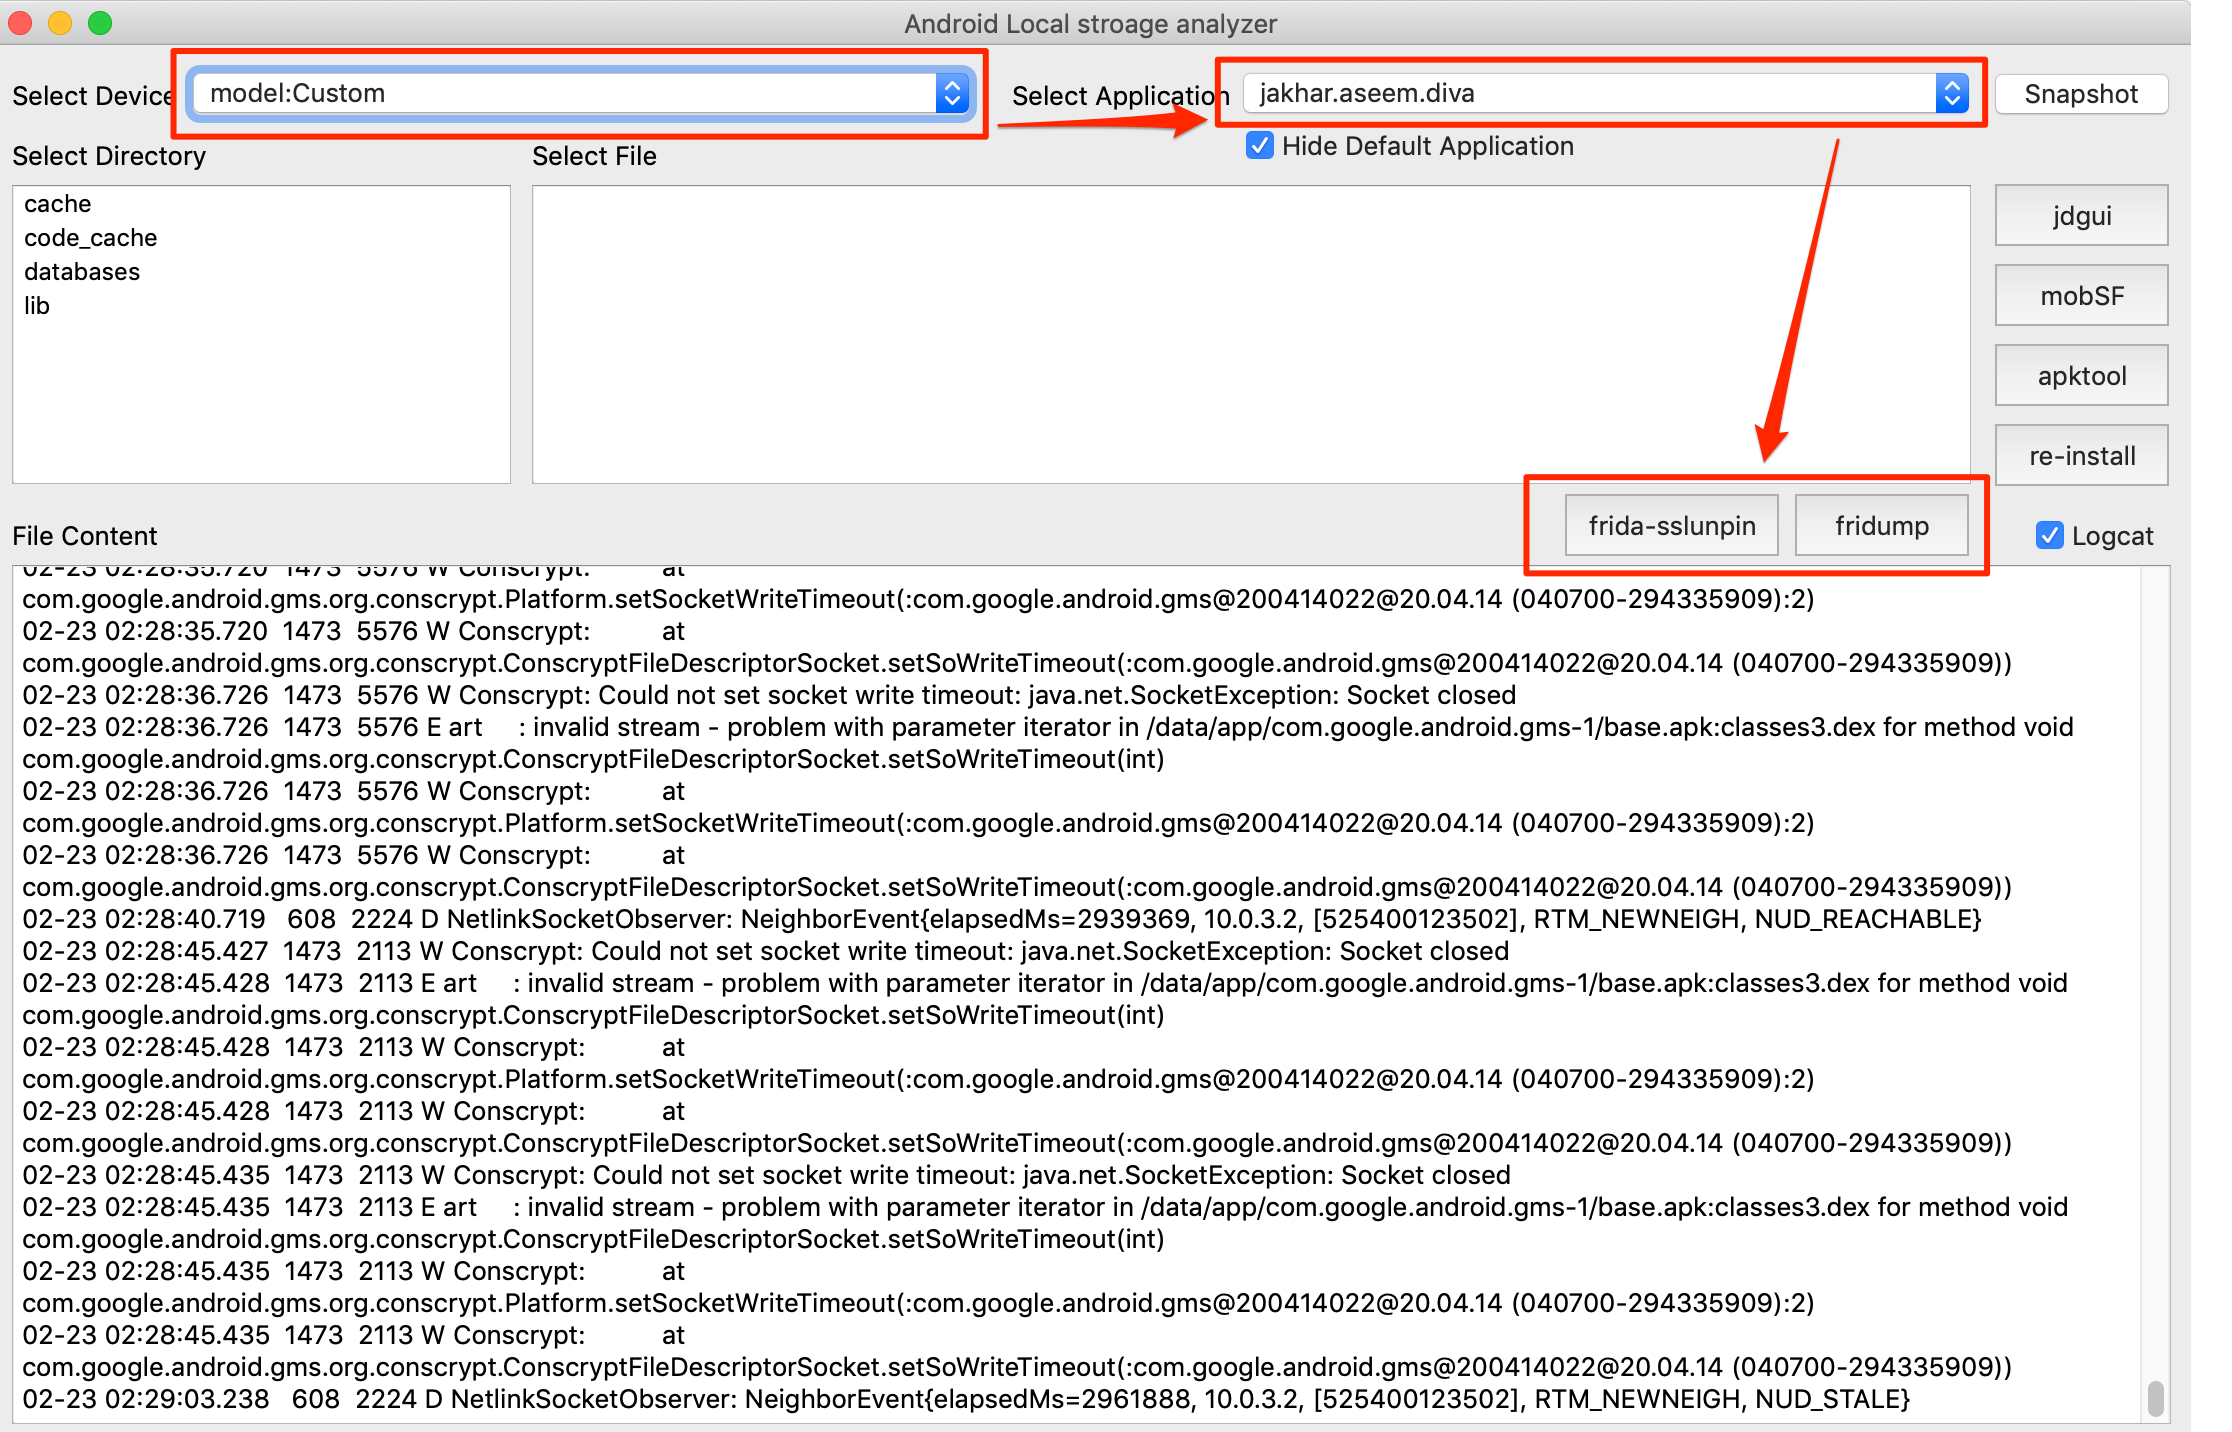 notsosecure/android_application_analyzer
The tool is used to analyze the content of the android application in local storage.
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 linkedin/qark
Tool to look for several security related Android application vulnerabilities
 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
 cybersecsi/robodroid
Manage Android machines with pre-defined behaviors for Cyber Range environments.
 xtiankisutsa/twiga
A tool that enumerates Android devices for information useful in understanding its internals and for exploit development. It supports android 4.2 to…
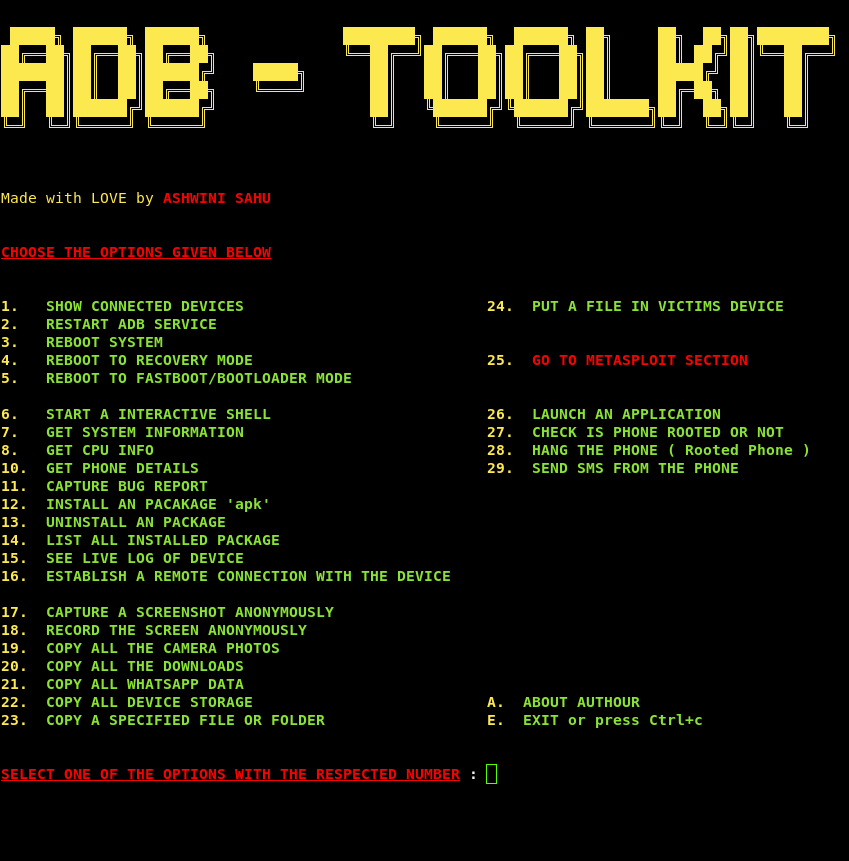 ashwin990/adb-toolkit
ADB-Toolkit V2 for easy ADB tricks with many perks in all one. ENJOY!
 stuxctf/mhf
Mobile Helper Framework (mhf) is a tool that automates the process of identifying the framework/technology used to create a mobile application.…
 alw1ez/arkhota
Arkhota, a web brute forcer for Android.
 xtiankisutsa/mara_framework
MARA is a Mobile Application Reverse engineering and Analysis Framework. It is a toolkit that puts together commonly used mobile application reverse…
 0x742/cve-2020-0082-externalvibration
This repo contains a proof-of-concept for 📱🚀👑⚡, a deserialization vuln for local escalation of privilege to system_server in Android 10. This…
 abrarkhan/g3_frameworks_av_cve-2024-0023
Proof-of-concept exploit for CVE-2024-0023 in Android's frameworks/av, implemented in C++ to demonstrate the media framework vulnerability.
 michalbednarski/leakvalue
Exploit for CVE-2022-20452, privilege escalation on Android from installed app to system app (or another app) via LazyValue using Parcel after…