
CVE-2020-6514
Exploit for CVE-2020-6514 targeting WebRTC SCTP memory corruption in Android applications. Uses Frida to hook native functions and alter SCTP packets…

Exploit for CVE-2020-6514 targeting WebRTC SCTP memory corruption in Android applications. Uses Frida to hook native functions and alter SCTP packets…

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…

Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…

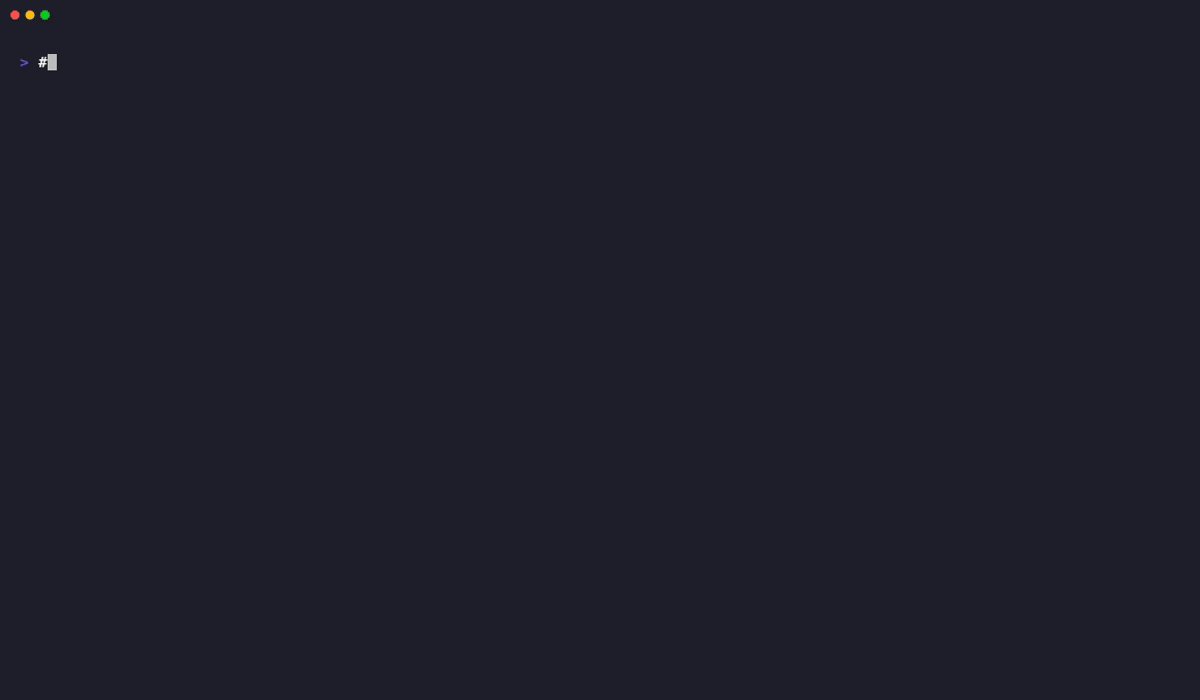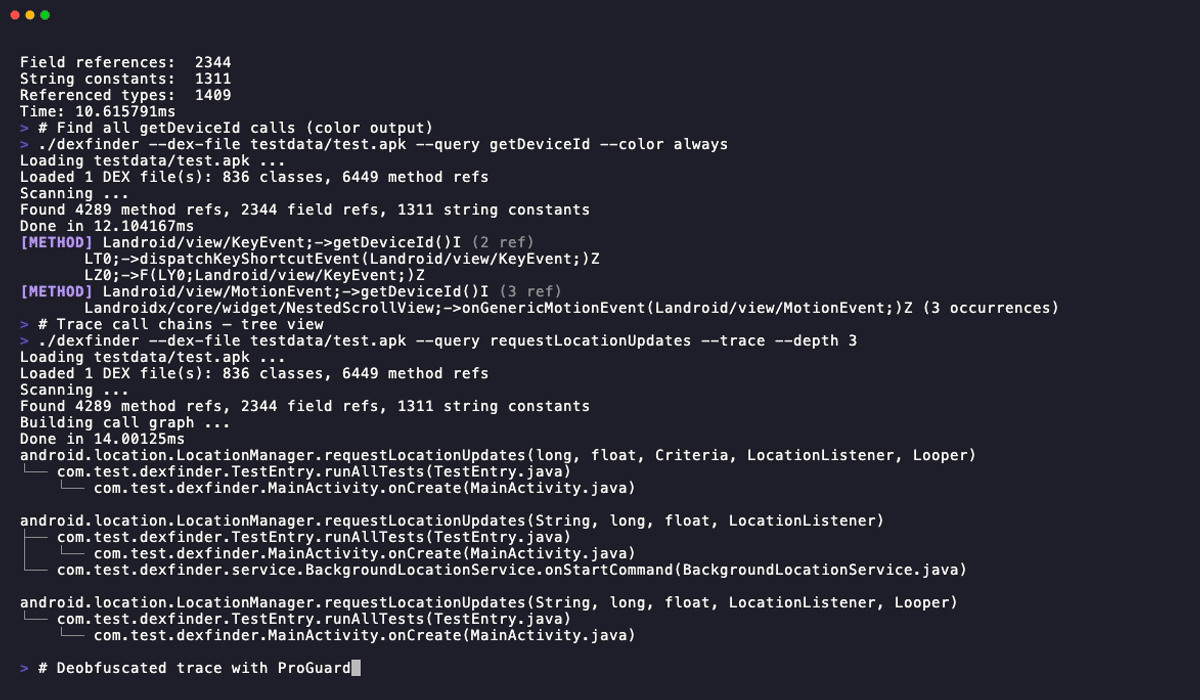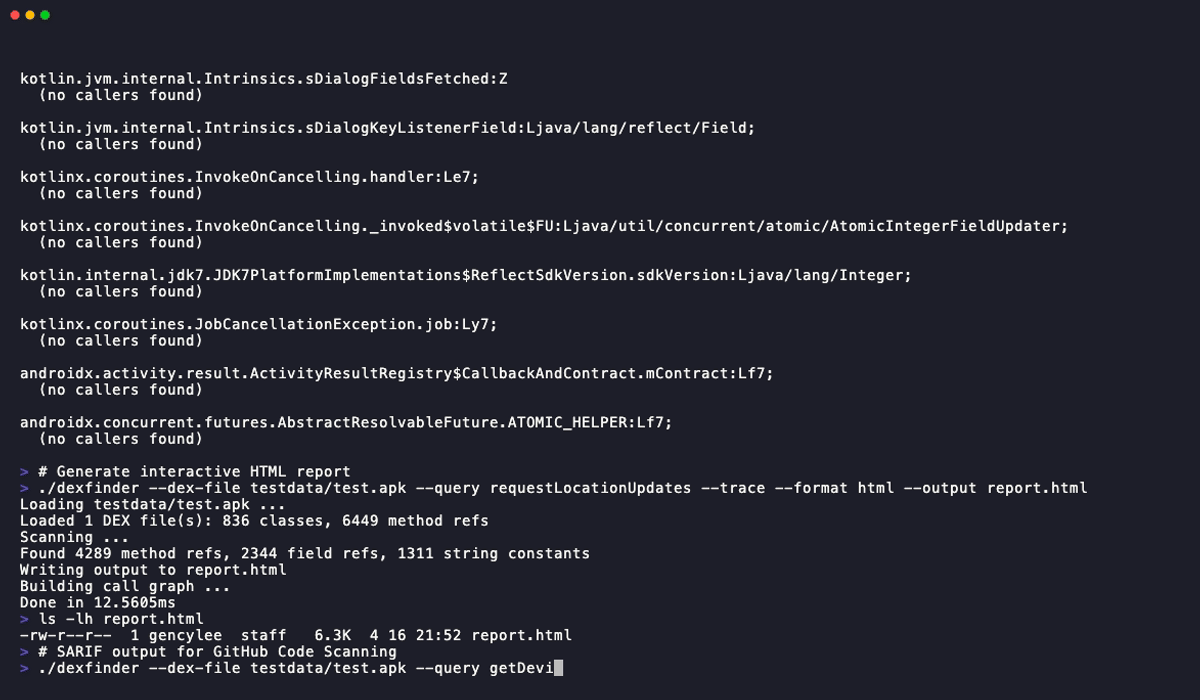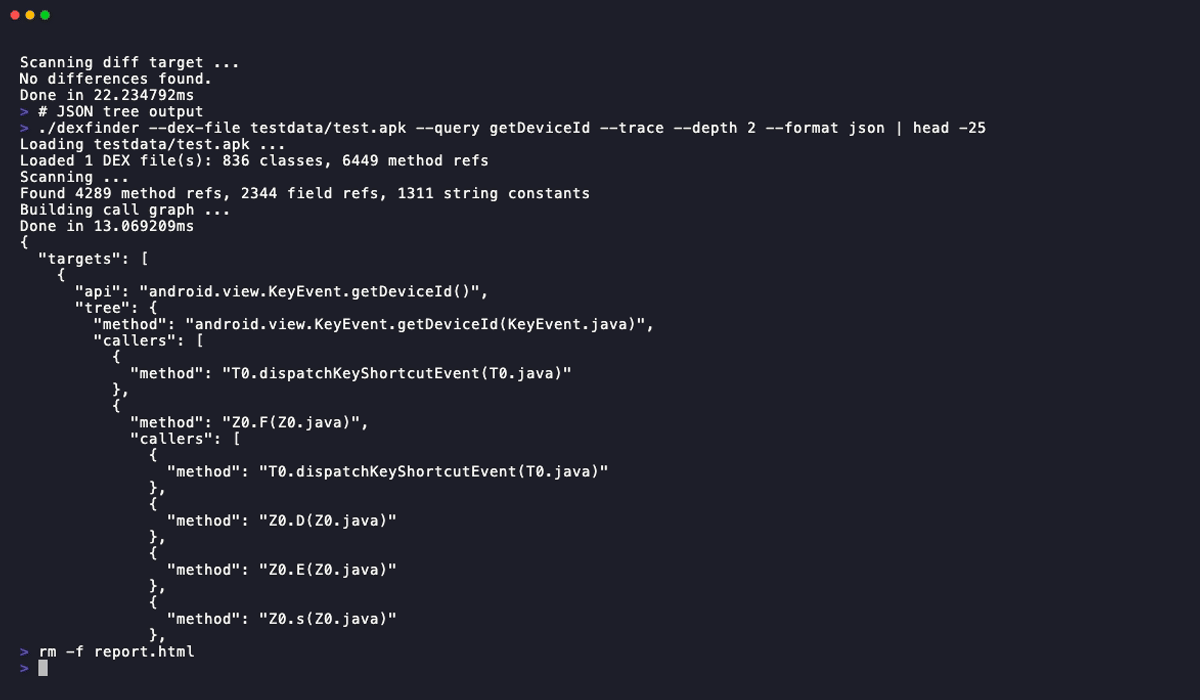
Cross-platform APK/DEX method finder with call chain tracing, ProGuard deobfuscation, and hidden API detection

A Remote Administration Tool for Android devices

Hooker is an opensource project for dynamic analyses of Android applications. This project provides various tools and applications that can be use to…

Dynamic analysis sandbox for Android apps that monitors network traffic, file operations, cryptographic API usage, permission circumvention, and…

Rust-based Tor library for Android and iOS, providing a standard API to integrate the Arti Tor runtime into mobile apps for private,…

Android Package Inspector - dynamic analysis with api hooks, start unexported activities and more. (Xposed Module)

In-depth analysis and proof-of-concept for CVE-2026-27280, an out-of-bounds write in Adobe DNG SDK's dng_render_task::ProcessArea, reachable via…

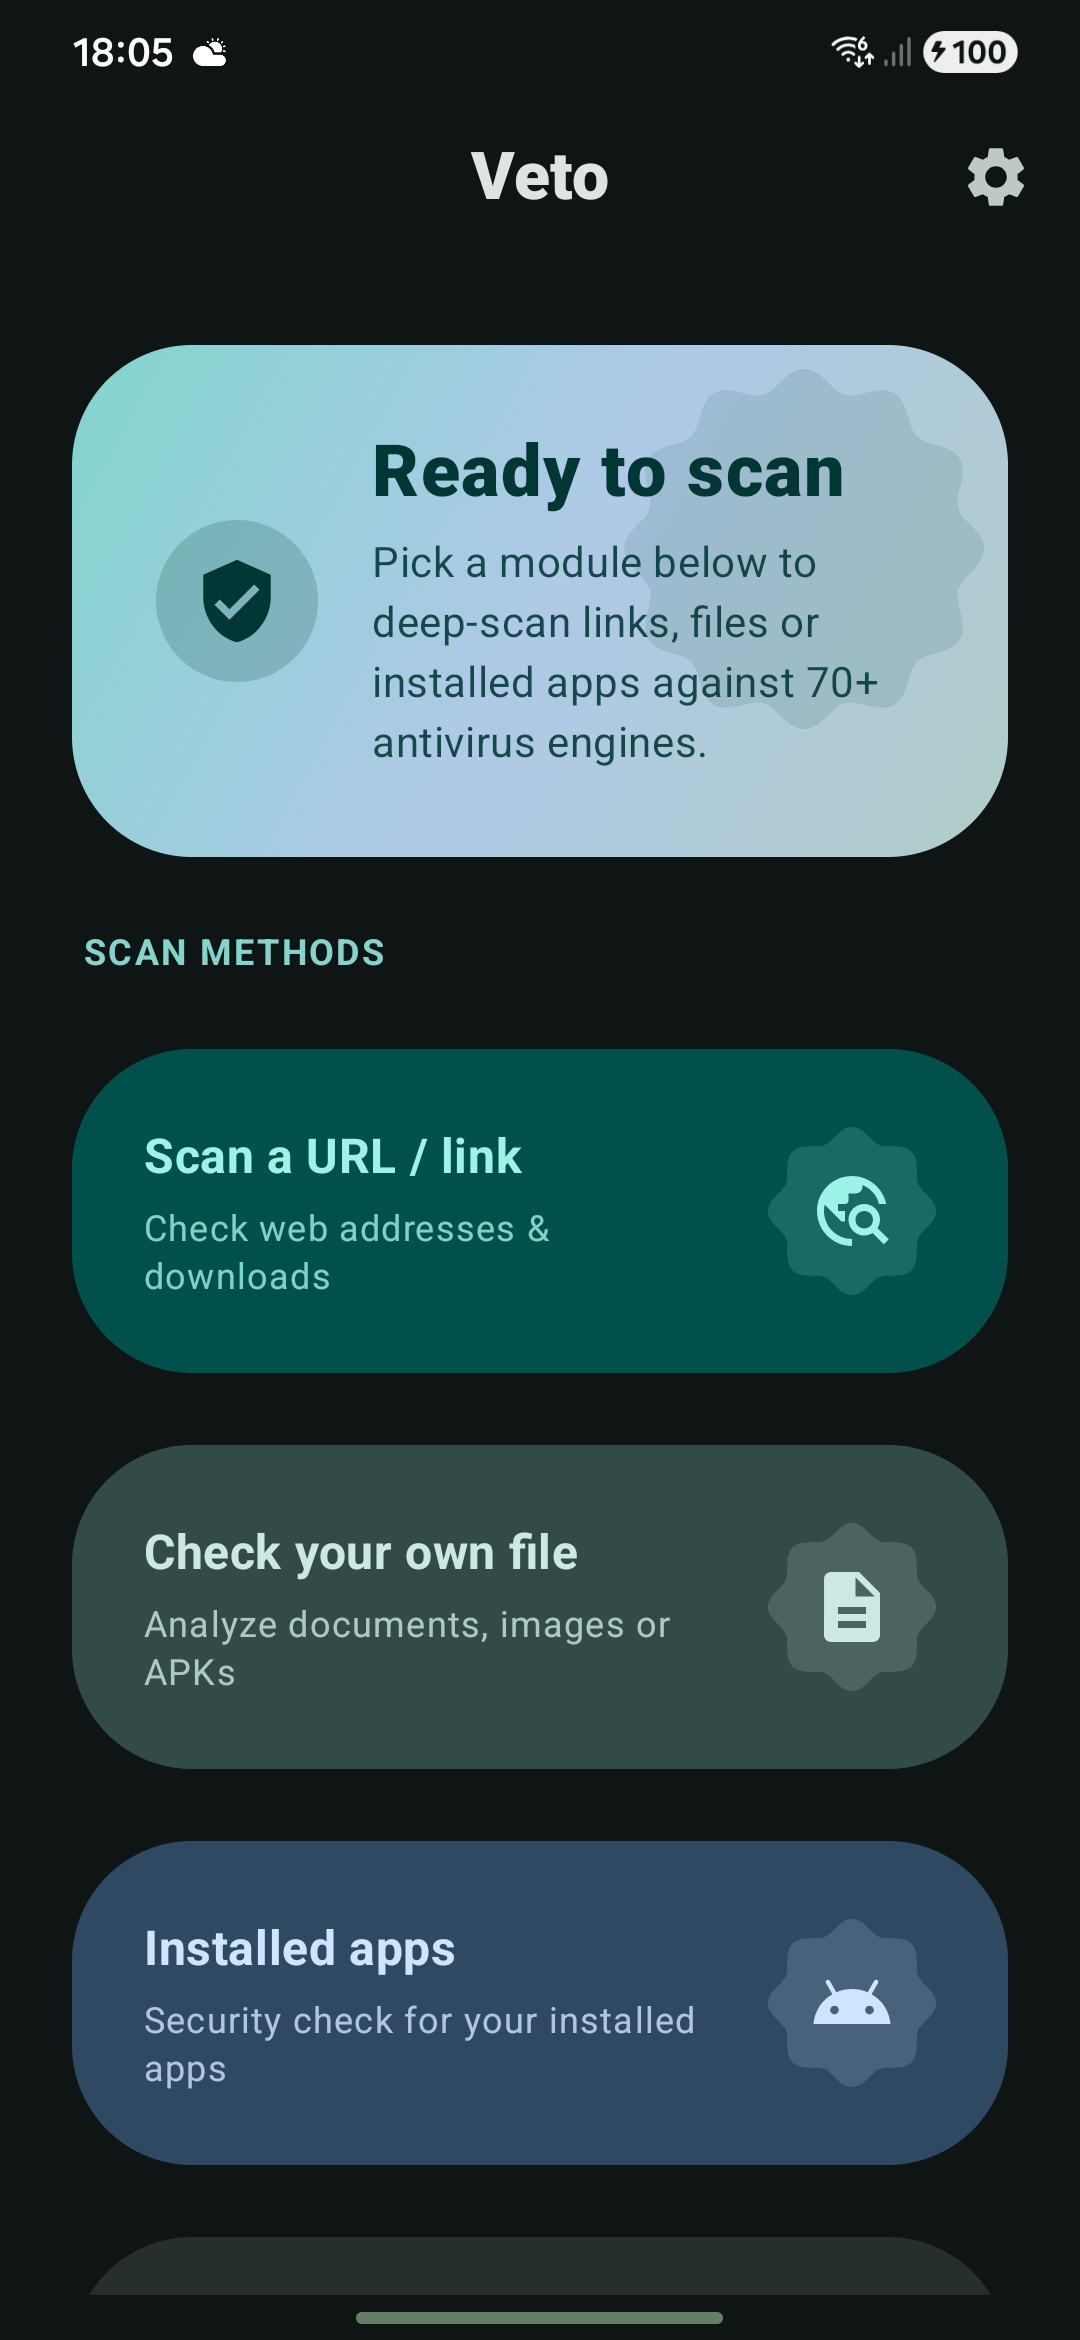
Open-source Android client for VirusTotal. Scan files, URLs, and installed apps against 70+ antivirus engines. View detailed reports with hashes,…

Frida-based runtime API monitor for Android apps that logs invoked APIs, parameters, return values, and call origins across predefined or custom…

APK decompiler & secrets scanner for Android security research! Extract leaked API keys, hardcoded credentials, endpoints from APK files. apk2url,…

Display and control your Android device

An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.

Natural-language Android automation agent that drives real devices via ADB, captures Logcat and screenshots, and exposes an MCP server for AI IDEs…