android-backup-extractor

Extract and repack Android ADB backups (ICS+). Supports encrypted archives, tar conversion, and standard I/O for forensic analysis or data recovery.

Extract and repack Android ADB backups (ICS+). Supports encrypted archives, tar conversion, and standard I/O for forensic analysis or data recovery.

Bash script to build your own system.prop

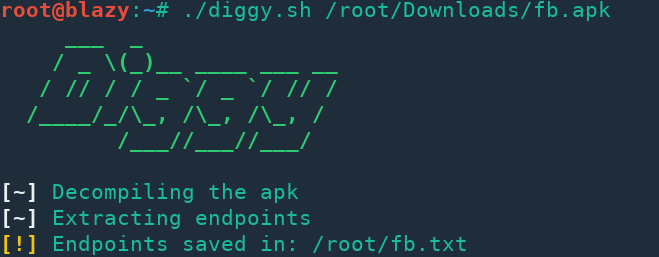
APK decompiler & secrets scanner for Android security research! Extract leaked API keys, hardcoded credentials, endpoints from APK files. apk2url,…

Extract WhatsApp private key from any non-rooted Android device (Android 7+ supported)

Simple framework to extract "actionable" data from Android malware (C&Cs, phone numbers etc.)

This is a toolkit that uses CVE-2024-31317 to extract private app data via ADB or spawn a shell with an app's UID.

Extract the managed (.NET) assemblies out of a MAUI Android assembly store.

Extract a concerning amount of user information from Unisoc ZTE devices using CVE-2022-38694.