
cromite
 uazo/cromite
Hardened Chromium/Bromite fork for Android, Windows and Linux with built-in ad blocking, anti-fingerprinting mitigations and privacy-focused patches.
android-securityanti-botfingerprint-spoofing+4
8.5k
uazo/cromiteHardened Chromium/Bromite fork for Android, Windows and Linux with built-in ad blocking, anti-fingerprinting mitigations and privacy-focused patches.
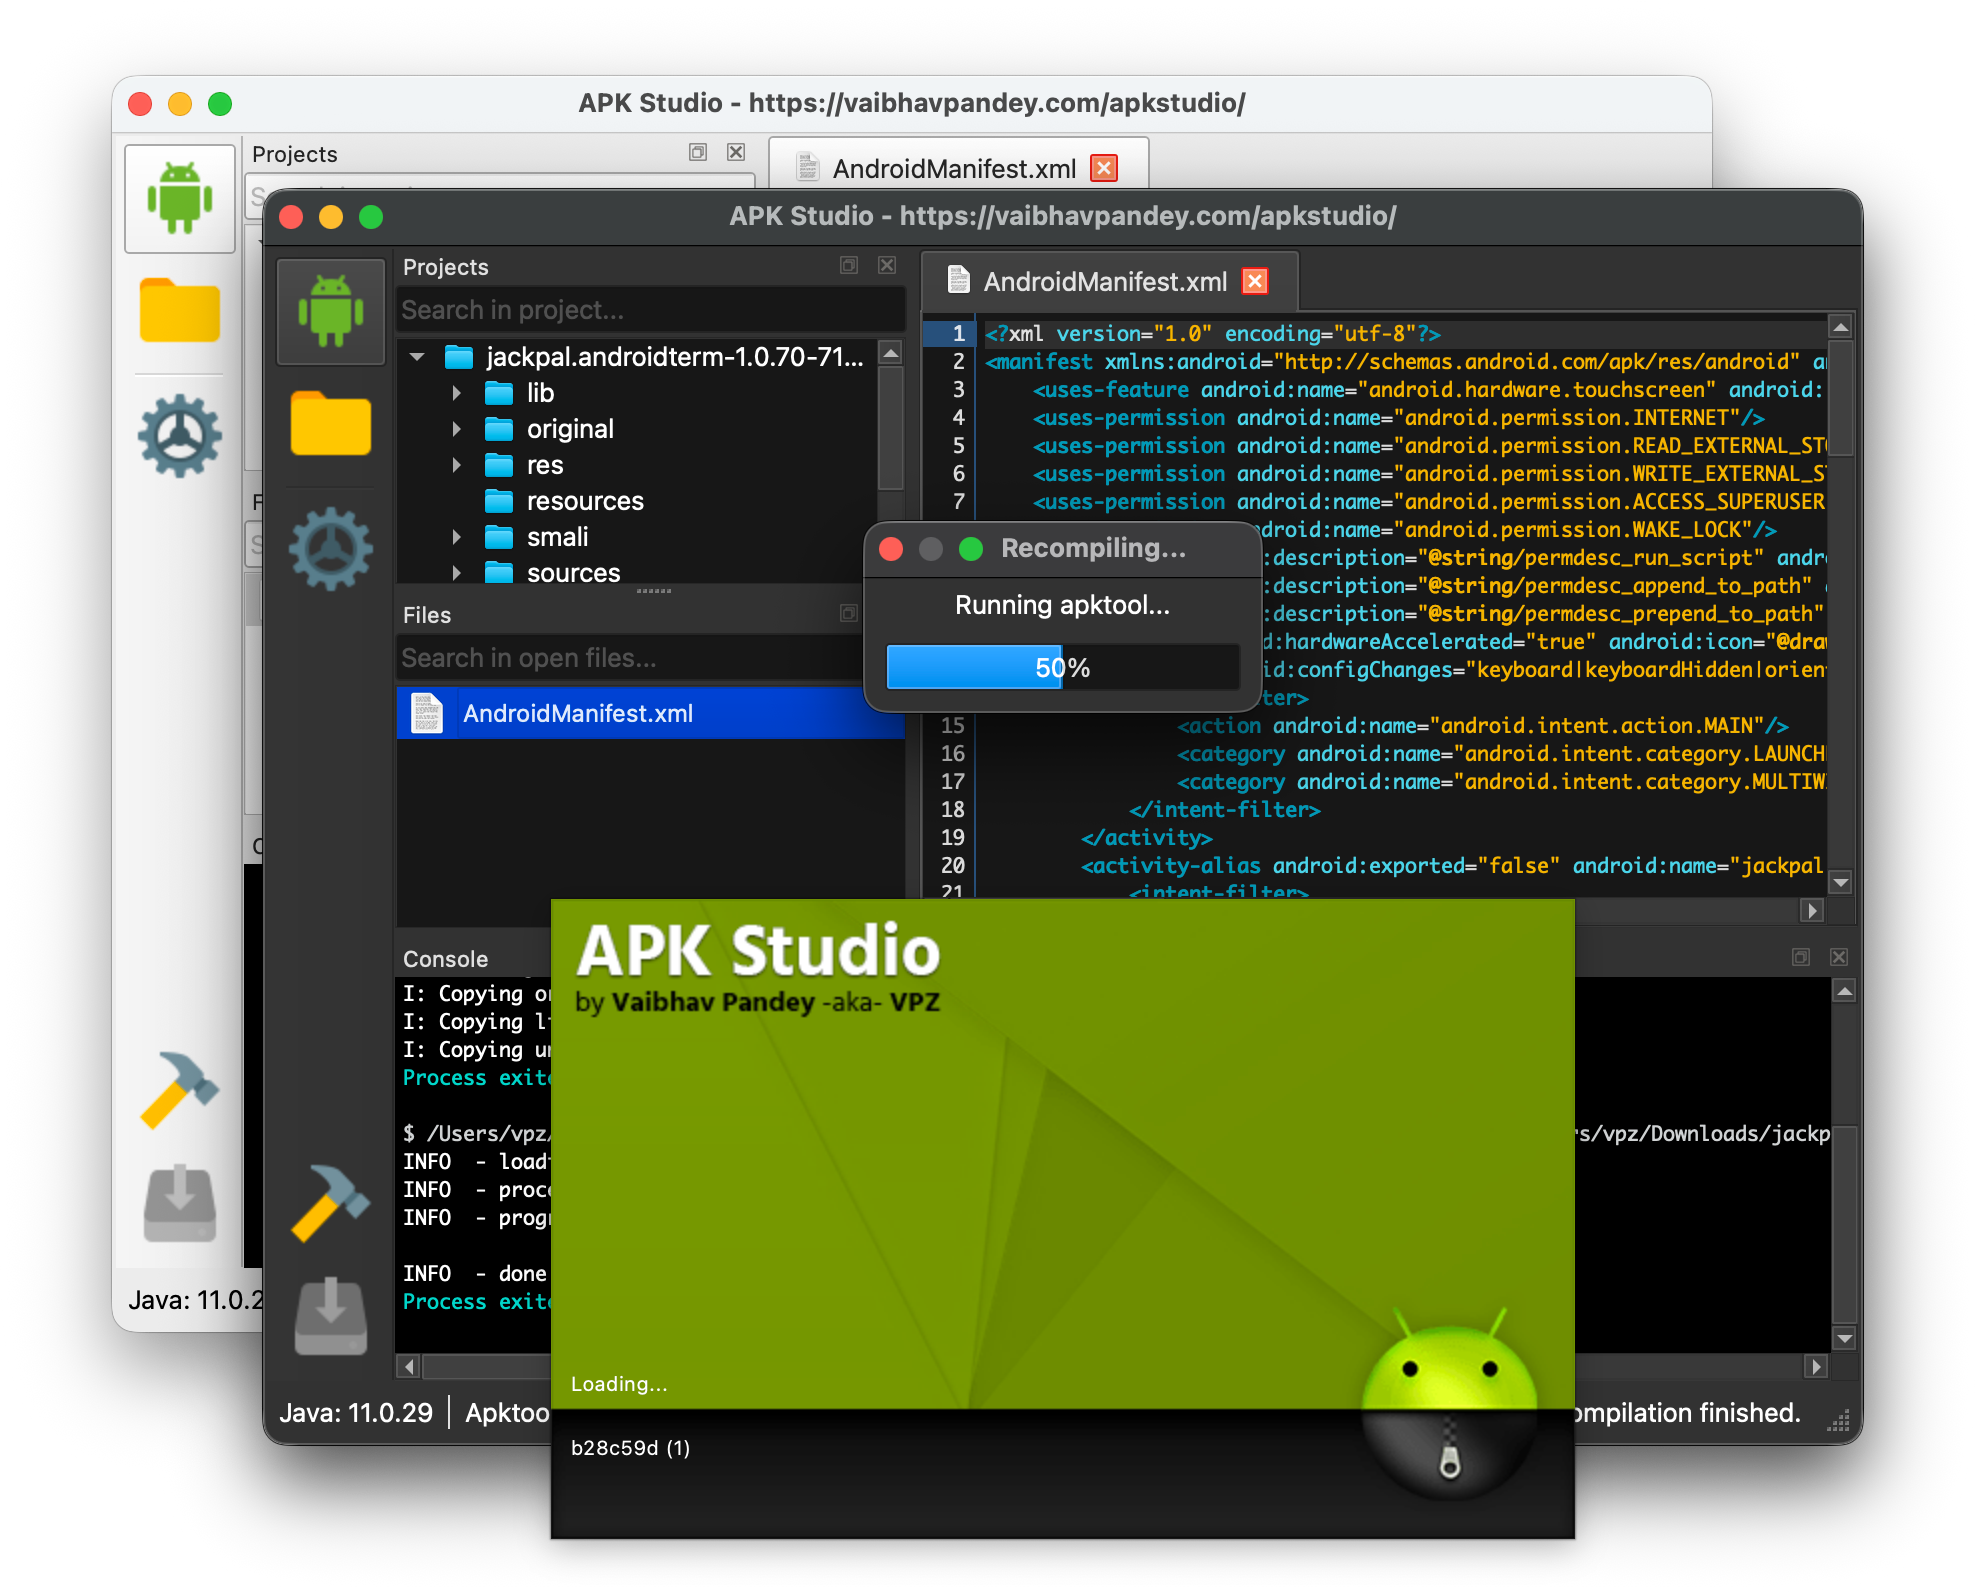 vaibhavpandeyvpz/apkstudio
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…
 mesquidar/adbsploit
A python based tool for exploiting and managing Android devices via ADB
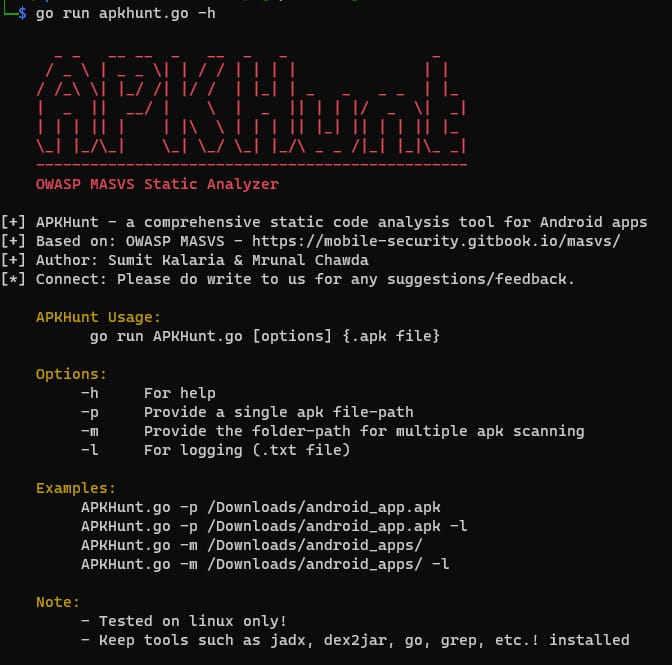 cyber-buddy/apkhunt
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…
 xiaohj233/ghostlock-x200-root
GhostLock-X200 v1.0 - temporary root toolchain for vivo X200 (PD2415 / b57 kernel) based on CVE-2026-43499. For authorized security research only.
 0xdsm/apepe
Extracts app settings, permissions, deeplinks, and SSL pinning bypass suggestions from Android APK files via static analysis of AndroidManifest.xml,…
 0xdad0/papimonitor
Frida-based runtime API monitor for Android apps that logs invoked APIs, parameters, return values, and call origins across predefined or custom…
 enceka/cve-2019-2215-3.18
for kernel 3.18.x
 slapah/ghostlock-h8q
GhostLock CVE-2026-43499 port for Galaxy Z Fold 8 (h8q)

 c3r34lk1ll3r/cve-2019-2215
PoC for old Binder vulnerability (based on P0 exploit)
 davidbuchanan314/nxloader
My first Android app: Launch Fusée Gelée payloads from stock Android (CVE-2018-6242)
 zhuowei/blueshrimp
Proof-of-concept for CVE-2025-48593
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
 nccgroup/assethook
LD_PRELOAD magic for Android's AssetManager
 ele7enxxh/cve-2014-7911
Proof-of-concept exploit for Android local privilege escalation (CVE-2014-7911) targeting Nexus5 with ROP chain and heap spraying to gain system uid.
 heeeeen/cve-2014-7911poc
Proof-of-concept exploit for CVE-2014-7911 targeting Android 4.4.4 on Nexus5, using a custom ROP chain to escalate privileges and write files as the…
 danielebert/cve-2016-5195
DirtyCOW Exploit for Android