
Olyx
 shacode/olyx
🔗 Lightweight security orchestrator mobile application for URI vetting, providing a unified, multi-engine interface to aggregate and validate link…
android-securityapi-securitydns-analysis+7
shacode/olyx🔗 Lightweight security orchestrator mobile application for URI vetting, providing a unified, multi-engine interface to aggregate and validate link…
 ustayready/mavd
Mobile Application Vulnerability Detection
 bkojusner/cve-2021-25461
Proof of concept for CVE-2021-25461, a vulnerability in Android Unix domain sockets, demonstrating exploitation techniques and providing analysis for…
 bariskizilkaya/cve-2022-20186_ctxz
Exploit for CVE-2022-20186 in Arm Mali kernel driver, achieving arbitrary kernel code execution from untrusted app domain to disable SELinux and gain…
 fusiondrive/cve-2026-43499-s24u
CVE-2026-43499 research port for Galaxy S24 Ultra SM-S928U1 DZF2 (COMPLETED)
 irsl/cve-2022-3168-adb-unexpected-reverse-forwards
Proof of concept code to exploit flaw in adb that allowed opening network connections on the host to arbitrary destinations
 newazbenalam/root-my-galaxy-payloads
Device-specific CVE-2026-43499 root payloads and KernelSU artifacts for Samsung Galaxy models, with firmware profiles, exploit source, and a support…
 camsshaft/ionstack-s22-cve-2026-43499
Android kernel exploit for Samsung Galaxy S22 that gains kernel-domain root via CVE-2026-43499, with SELinux permissive, device-specific kallsyms,…
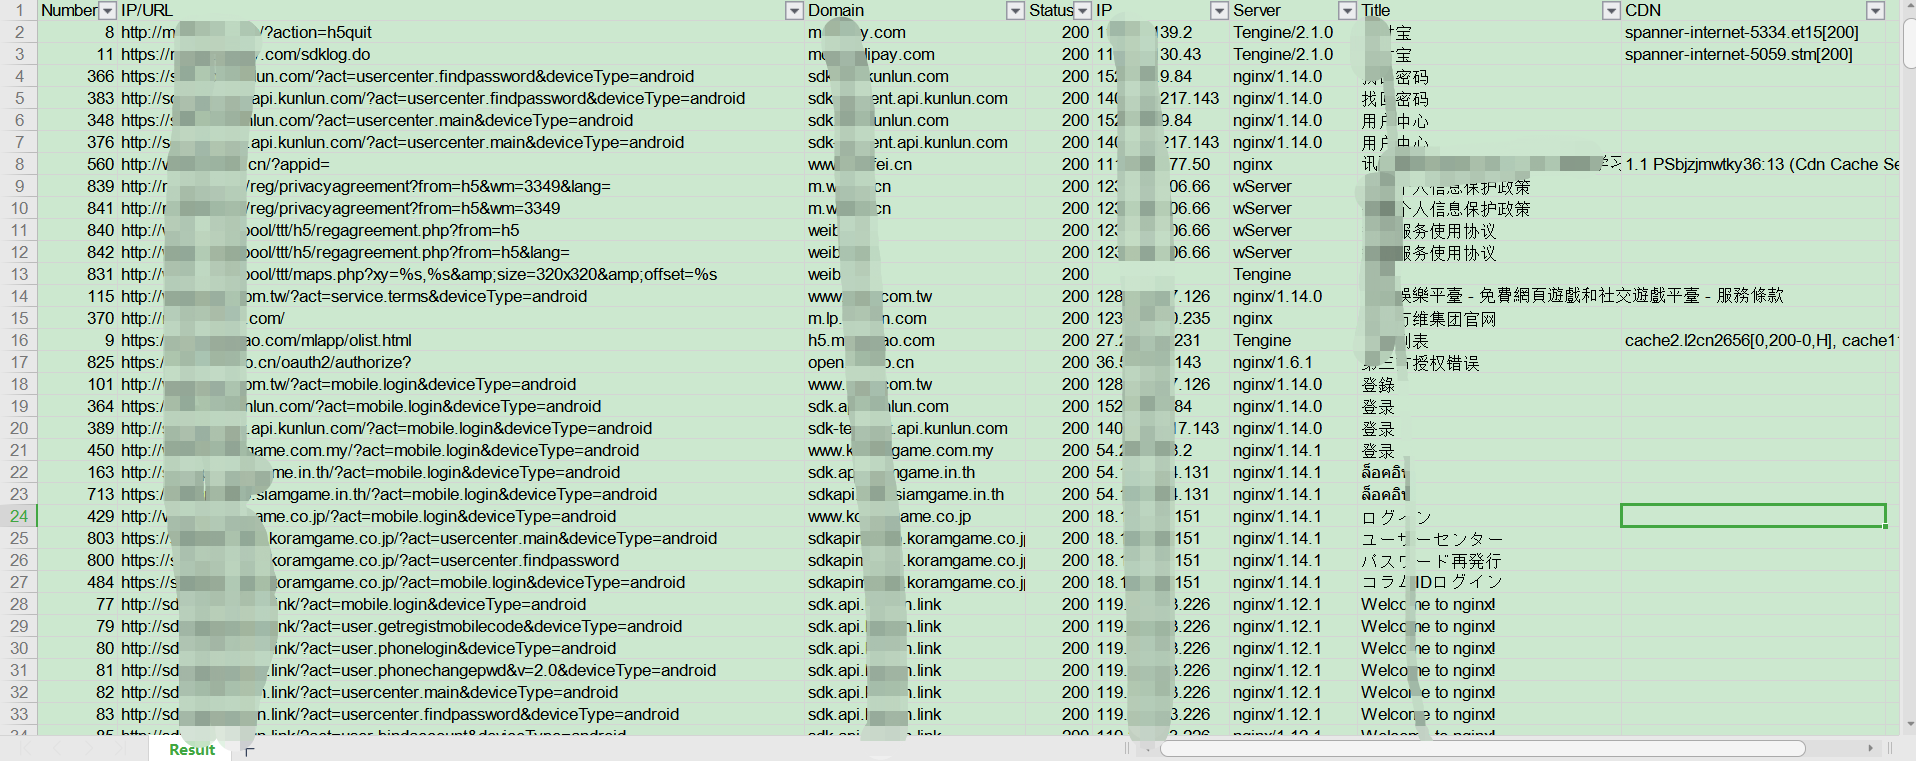 kelvinben/appinfoscanner
一款适用于以HW行动/红队/渗透测试团队为场景的移动端(Android、iOS、WEB、H5、静态网站)信息收集扫描工具,可以帮助渗透测试工程师、攻击队成员、红队成员快速收集到移动端或者静态WEB站点中关键的资产信息并提供基本的信息输出,如:Title、Domain、CDN、指纹信息、状态信息等。
 hadesscs/artemis
Extracts and investigates infrastructure (IPs, domains) from APK files, with manifest parsing and WHOIS lookup for mobile application reconnaissance.
 hydradragonantivirus/hydradragonav-mobile
Android Antivirus which doesn't require root, adb, ca install and cloud with many features and ways to detect more zero-day malware
 xingchenrs/cybermeowfians
The next stage of CyberMeowfil (CVE-2026-43499 and 43074),Possibly biased toward vivo devices?
 2932796375github/cve-2026-43499_oppo-mt6835
Proof-of-concept exploit chain for CVE-2026-43499 targeting OPPO MT6835 Android devices, with preload payload, build system, and analysis notes for…
 hunt-benito/the-callback-that-outlived-the-page-cve-2026-78997-uc-browser-android-universal-xss
PoC for CVE-2026-78997, a Universal XSS in UC Browser for Android. Includes a crafted URL builder, a callback-dispatch oracle, and Frida hooks to…
 fusiondrive/cve-2026-43499-a36
Standalone CVE-2026-43499 port for Galaxy A36 5G SM-A366W A366WVLS3AYG1 with KernelSU late-load
 dorlow/hazel-cve-2026-43499
Firmware-specific temporary root exploit for Toshiba/Amazon Fire TV (hazel) using CVE-2026-43499. Implements ARM32 futex-PI UAF, kernel address leak,…
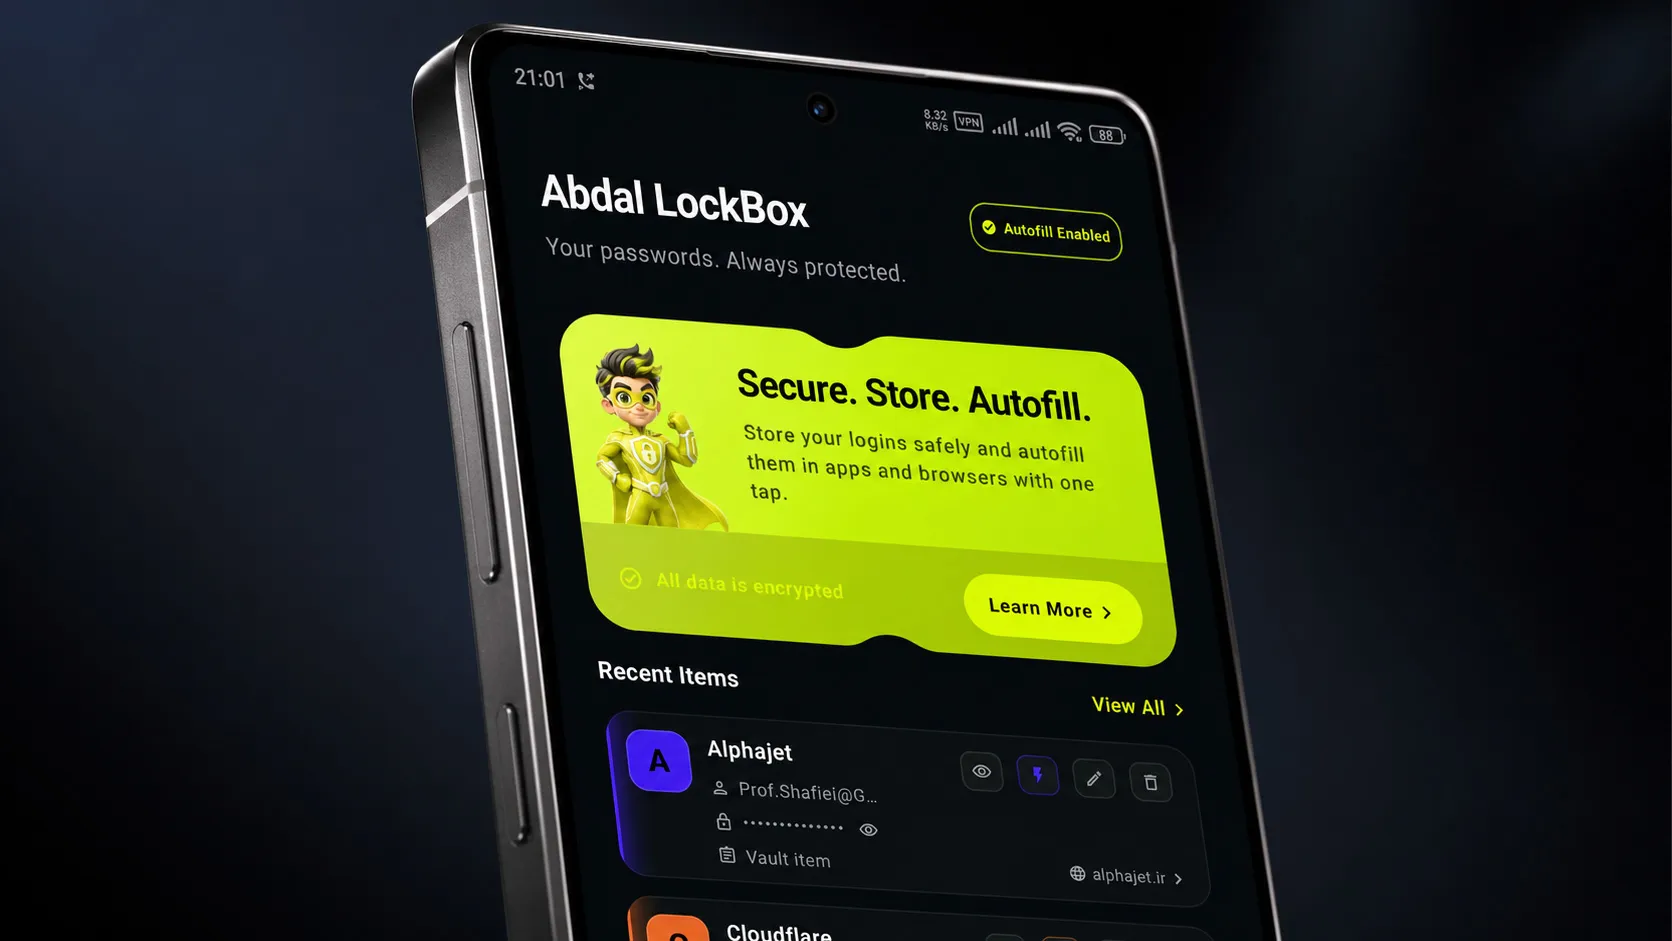 prof.shafiei/abdal-lockbox
Local-first encrypted password vault for Android with Master Password access, Recovery Key support, Autofill integration, and portable encrypted…
 smiletablabo/cve-2022-46395
Exploit for CVE-2022-46395, an Arm Mali kernel driver vulnerability, achieving arbitrary kernel code execution to disable SELinux and gain root on…