GDA-android-reversing-Tool

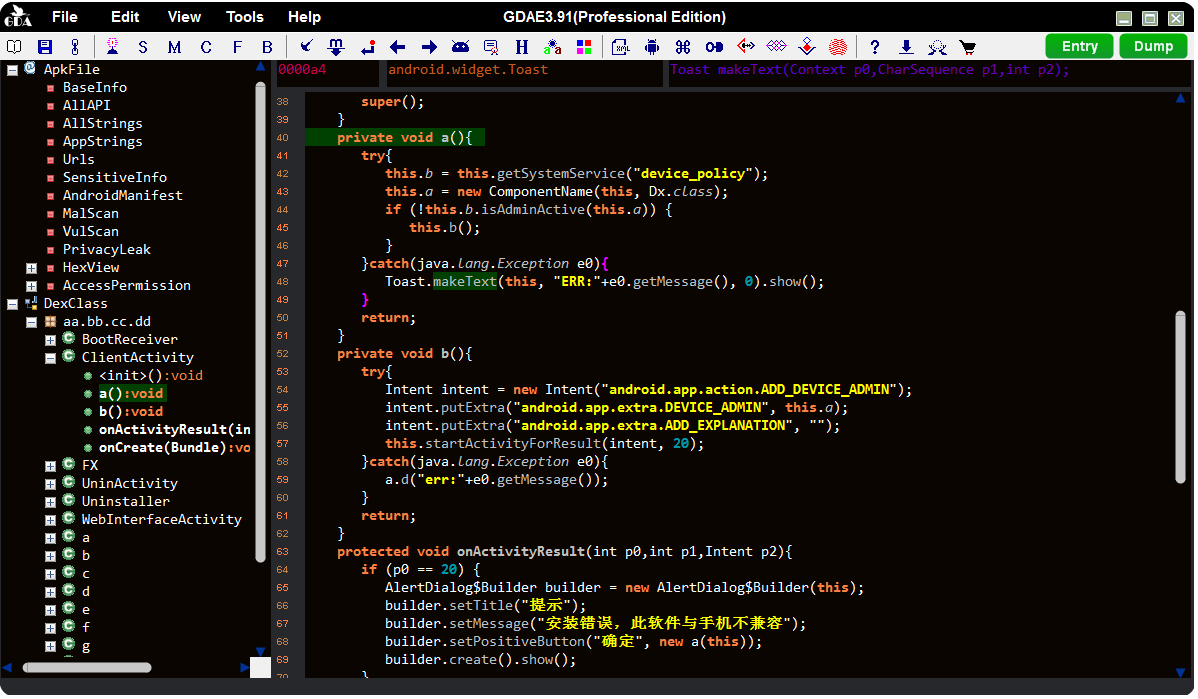
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…

the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…

Scanning APK file for URIs, endpoints & secrets.

backdoor-apk is a shell script that simplifies the process of adding a backdoor to any Android APK file. Users of this shell script should have…

Cloud-based Android monitoring tool with GPS tracking, microphone recording, SMS/call logging, live notification capture, file explorer, and built-in…

ES File Explorer Open Port Vulnerability - CVE-2019-6447

Dynamic analysis sandbox for Android apps that monitors network traffic, file operations, cryptographic API usage, permission circumvention, and…

Writeup and exploit for CVE-2024-34740, integer overflow in Android's BinaryXmlSerializer to system_server file write and then to system_server code…

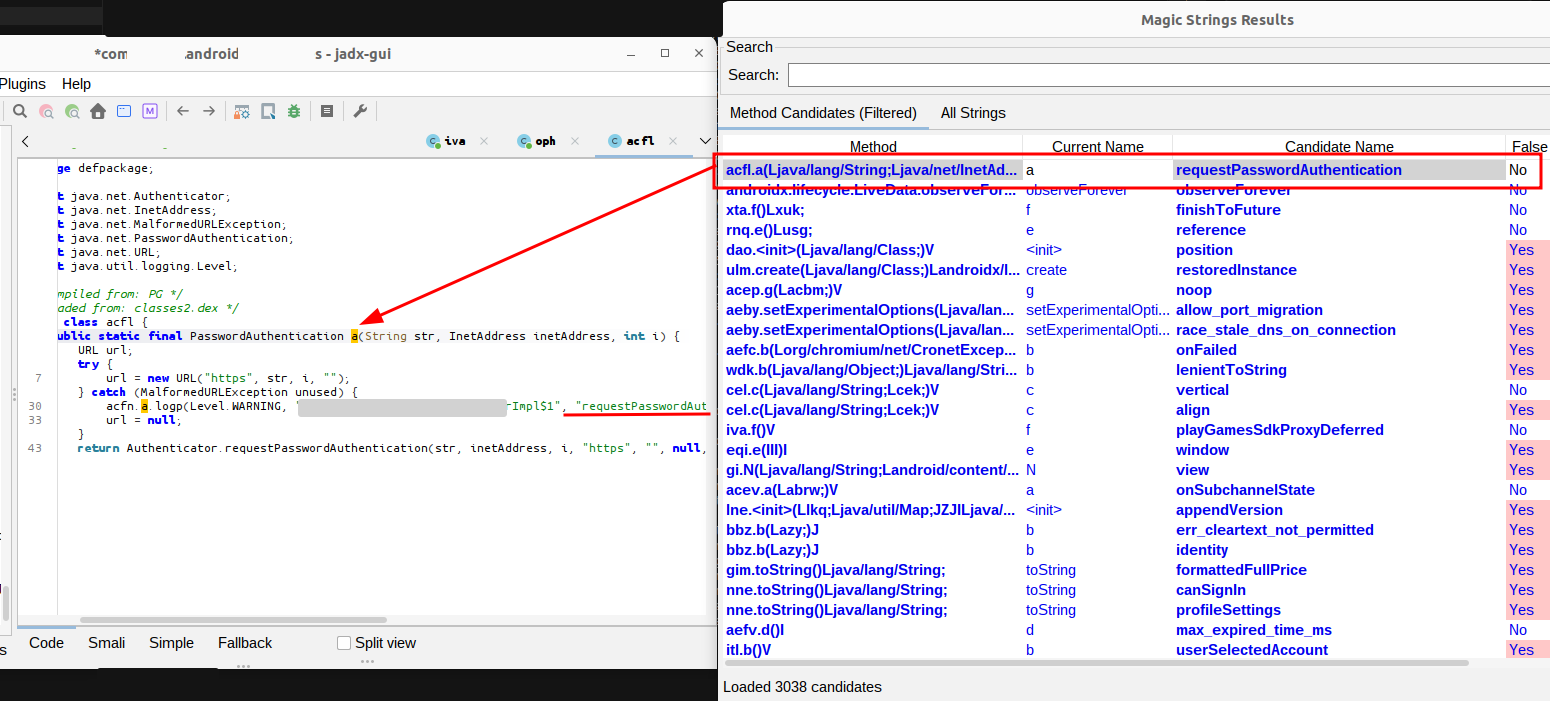
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.

Exploit for CVE-2016-2434, a buffer overflow in Android mediaserver enabling arbitrary code execution via crafted media file.

Writeup and exploit for CVE-2024-49746: Android's Parcel::continueWrite closing File Descriptors that are later used

This native code file aims to be complementary to the published Whatsapp GIF RCE exploit by Awakened , by calculating the system() function address…

Python script to generate a malicious MP4 file and start a CherryPy web server hosting a simple HTML page with the embedded file. Exploits another…

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

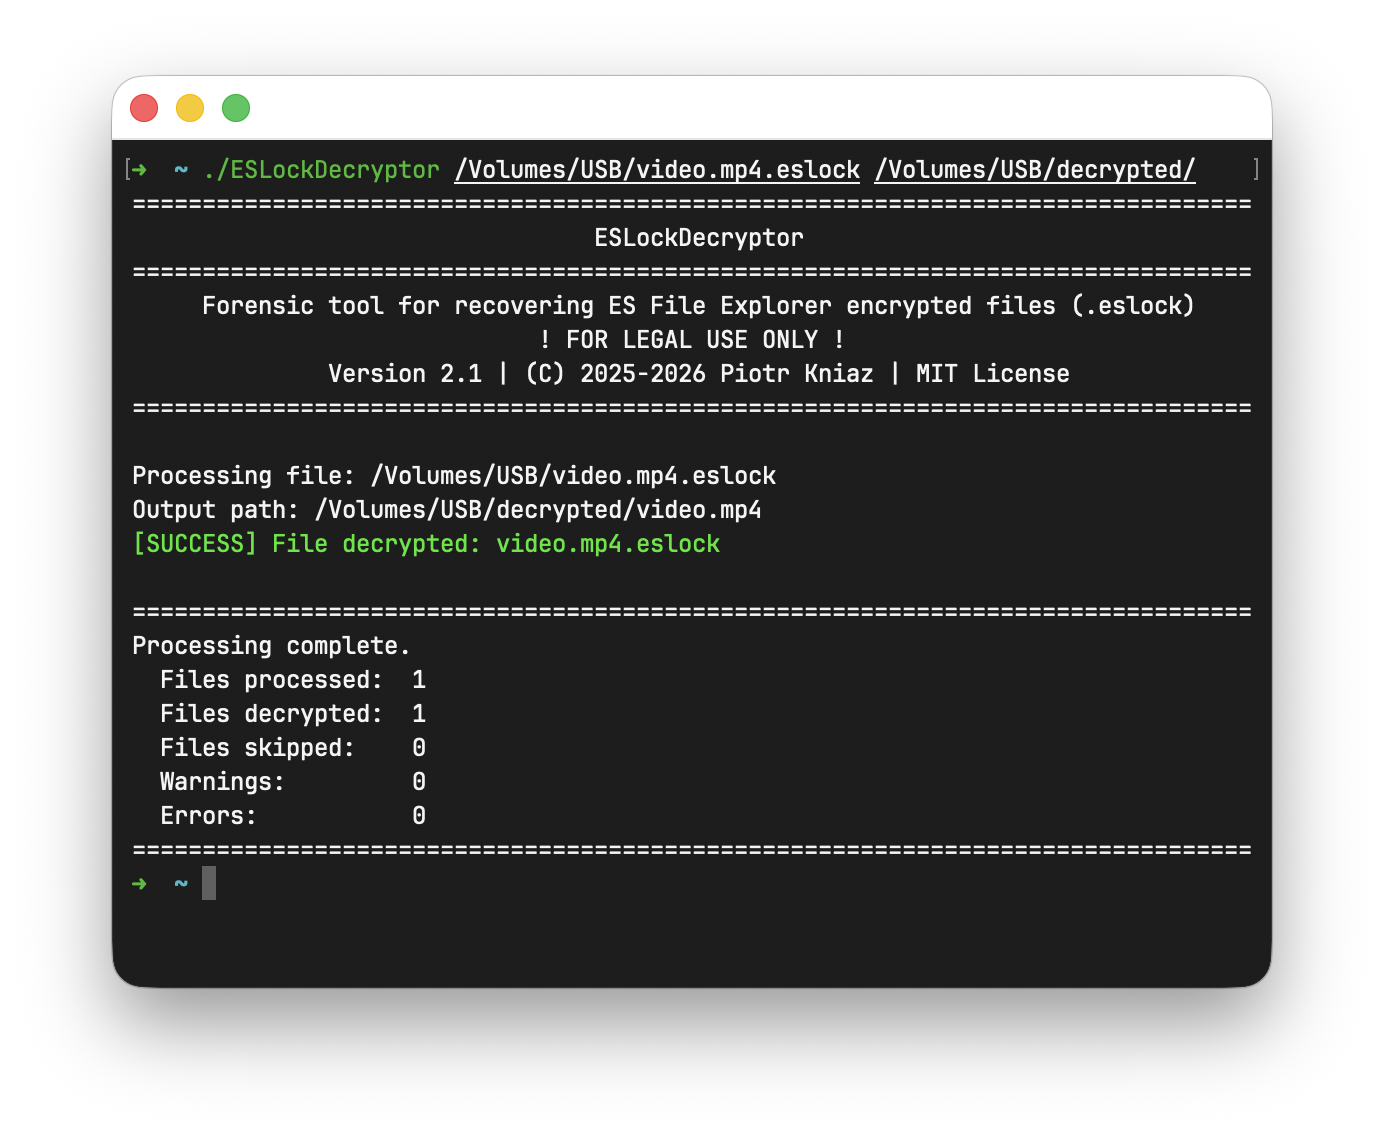
Utility for recovering ES File Explorer encrypted files (.eslock)

Proof-of-concept and instrumented reproduction harness for CVE-2026-28609, an out-of-bounds write in Android's MatroskaExtractor reachable via a…

Java-based exploit tool for CVE-2017-13156 that bypasses Android APK signature verification by appending a DEX file to an existing APK, enabling code…

CVE-2016-5195 dirtycow by timwr automated multi file patch tool

Technical write-up and exploit code for CVE-2019-11932, a double-free vulnerability in WhatsApp for Android that leads to remote code execution via a…