
MaFrida
 theshinigami/mafrida
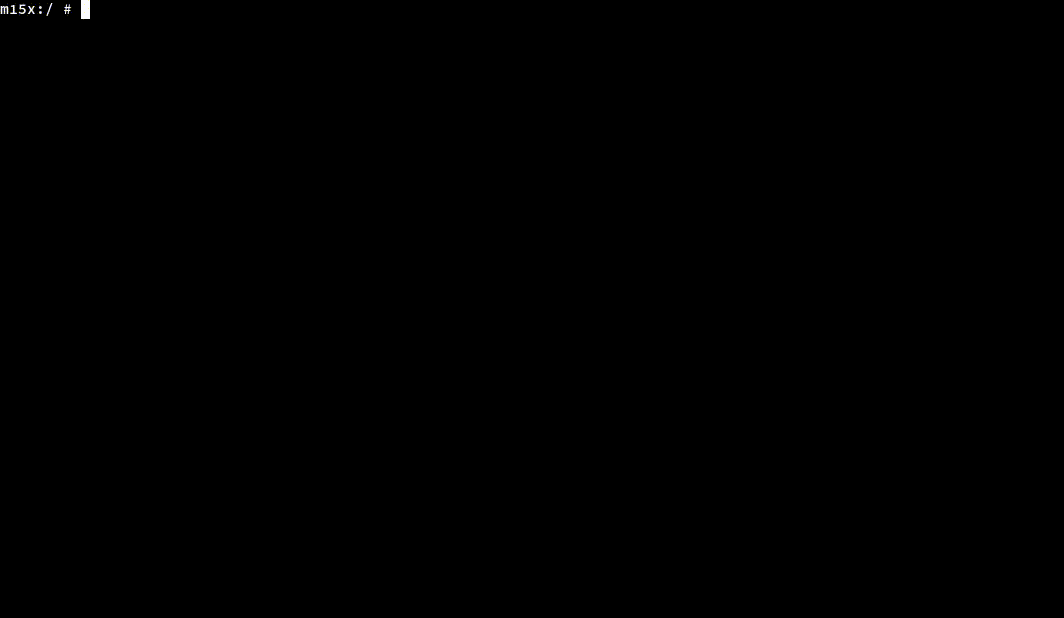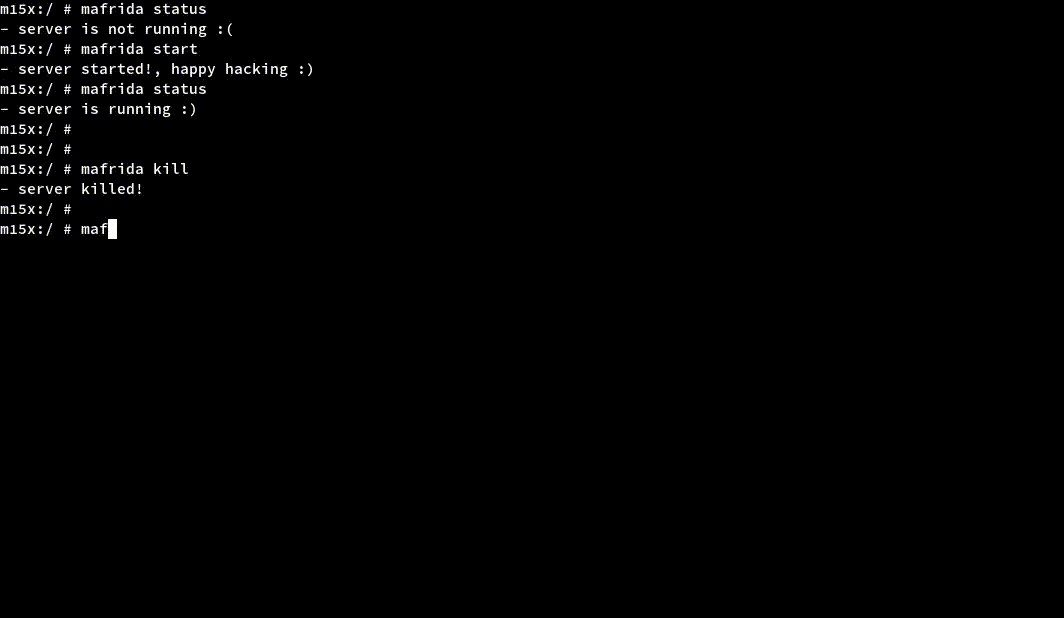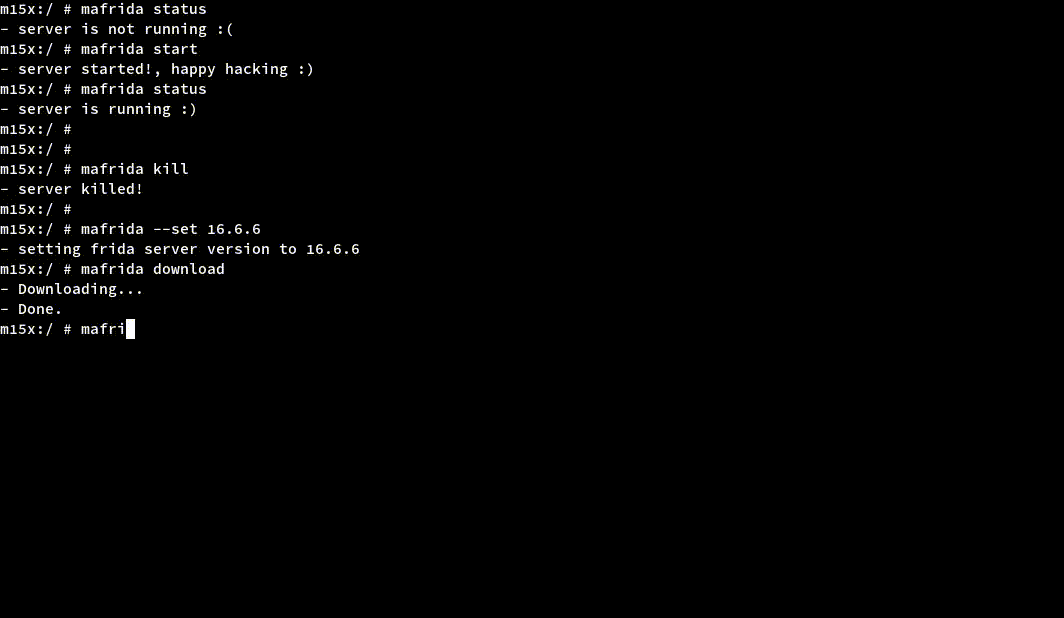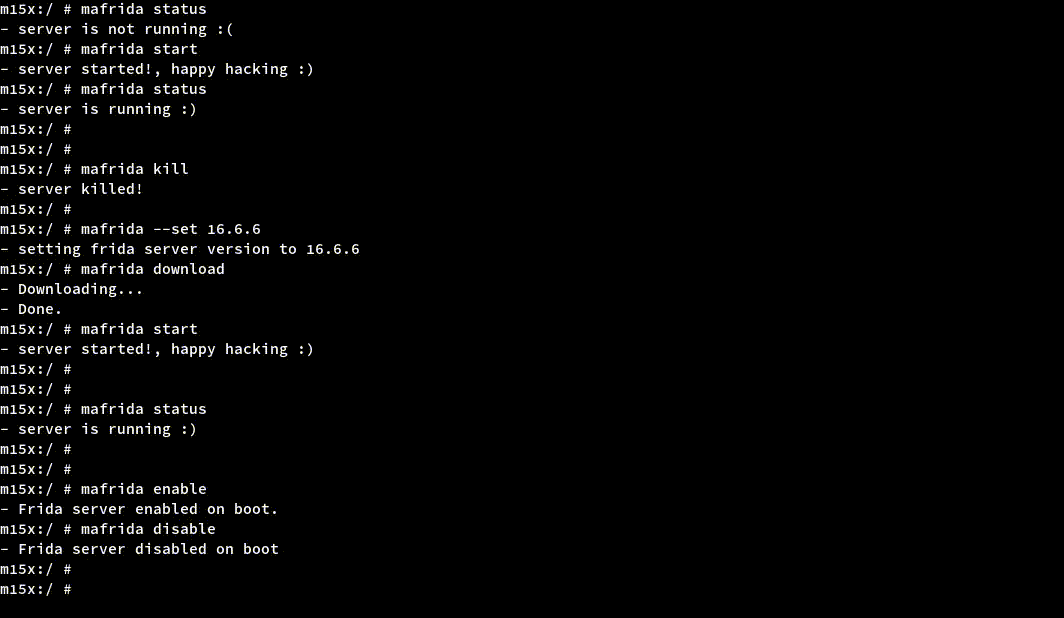
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
android-securitydynamic-analysis-sandboxingdynamic-code-analysis+5
40
theshinigami/mafridaA Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
 topjohnwu/magisk
Android customization suite providing root access (MagiskSU), systemless module installation, boot image unpacking/repacking, and Zygisk runtime code…
 ac-pm/inspeckage
Android Package Inspector - dynamic analysis with api hooks, start unexported activities and more. (Xposed Module)
 alirezaparsi/copg
Advanced per-app device / CPU / GPU spoofer for rooted Android — device profiles, per-app CPU models, prop & Android-ID spoofing, all driven by a…
 android1500/androidfaker
Android Faker a Simple Xposed Module Which Spoof Your Device IDs Values. Supporting Android 8.1+
 nccgroup/conscrypttrustusercerts
Magisk module for Android 14 that adds user-installed CA certificates to the system's Conscrypt trust store, enabling HTTPS interception with proxy…
 yakidango-official/ghostlock-h80gt
Honor 80 GT privilege escalation PoC: GhostLock (CVE-2026-43499) + custom KernelSU module loading
 vichhka-git/magisk-renef
Magisk module that auto-packages renef_server (dynamic instrumentation for Android)
 jeboo/bypasslkm
Using CVE-2013-6282 to bypass Samsung kernel module authentication
 jacobsoo/malconfig
This is part of a module for the framework that i'm constantly developing. Currently only information of the C2 are disclosed here.
 ravss/bluetooth-crash-cve-2017-0785
Exploit script for CVE-2017-0785 that crashes the Bluetooth module on Android 4.0+ devices by sending crafted SDP search requests, causing…
 satheesh575555/frameworks_av_aosp10_r33_cve-2020-0245
Android frameworks_av module with modifications addressing CVE-2020-0245, a vulnerability in media framework. Provides patched source code for AOSP…
 labcif/fama
Forensic Analysis for Mobile Apps (FAMA) -- module for the Autopsy Forensic Browser
 yukonga/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
 jacobsoo/amtracker
Android Malware Tracker
 e-r-butch/f9360-cve43499
SM-F9360 (Galaxy Z Fold4, q4q) locked-bootloader KernelSU root — CVE-2026-43499 temp root → LD_PRELOAD DEFEX bypass → no-LTO clang-12 kernelsu.ko.…
 crackercat/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 nicchongwb/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration