
mas-website
 owasp/mas-website
The OWASP Mobile Application Security Project website is the central hub for industry-leading standards, guides, and resources—helping developers and…
android-securitycurated-resourceseducation+4
12
owasp/mas-websiteThe OWASP Mobile Application Security Project website is the central hub for industry-leading standards, guides, and resources—helping developers and…
 isec-tugraz/file-notification-attacks
Research artifacts for file-notification side-channel attacks on Linux, Windows, and macOS, demonstrating inotify/FSEvents leakage, keystroke timing,…
 librepods-org/librepods
AirPods liberated from Apple's ecosystem.
 retme7/cve-2014-7911_poc
Local root exploit for Nexus5 Android 4.4.4(KTU84P)
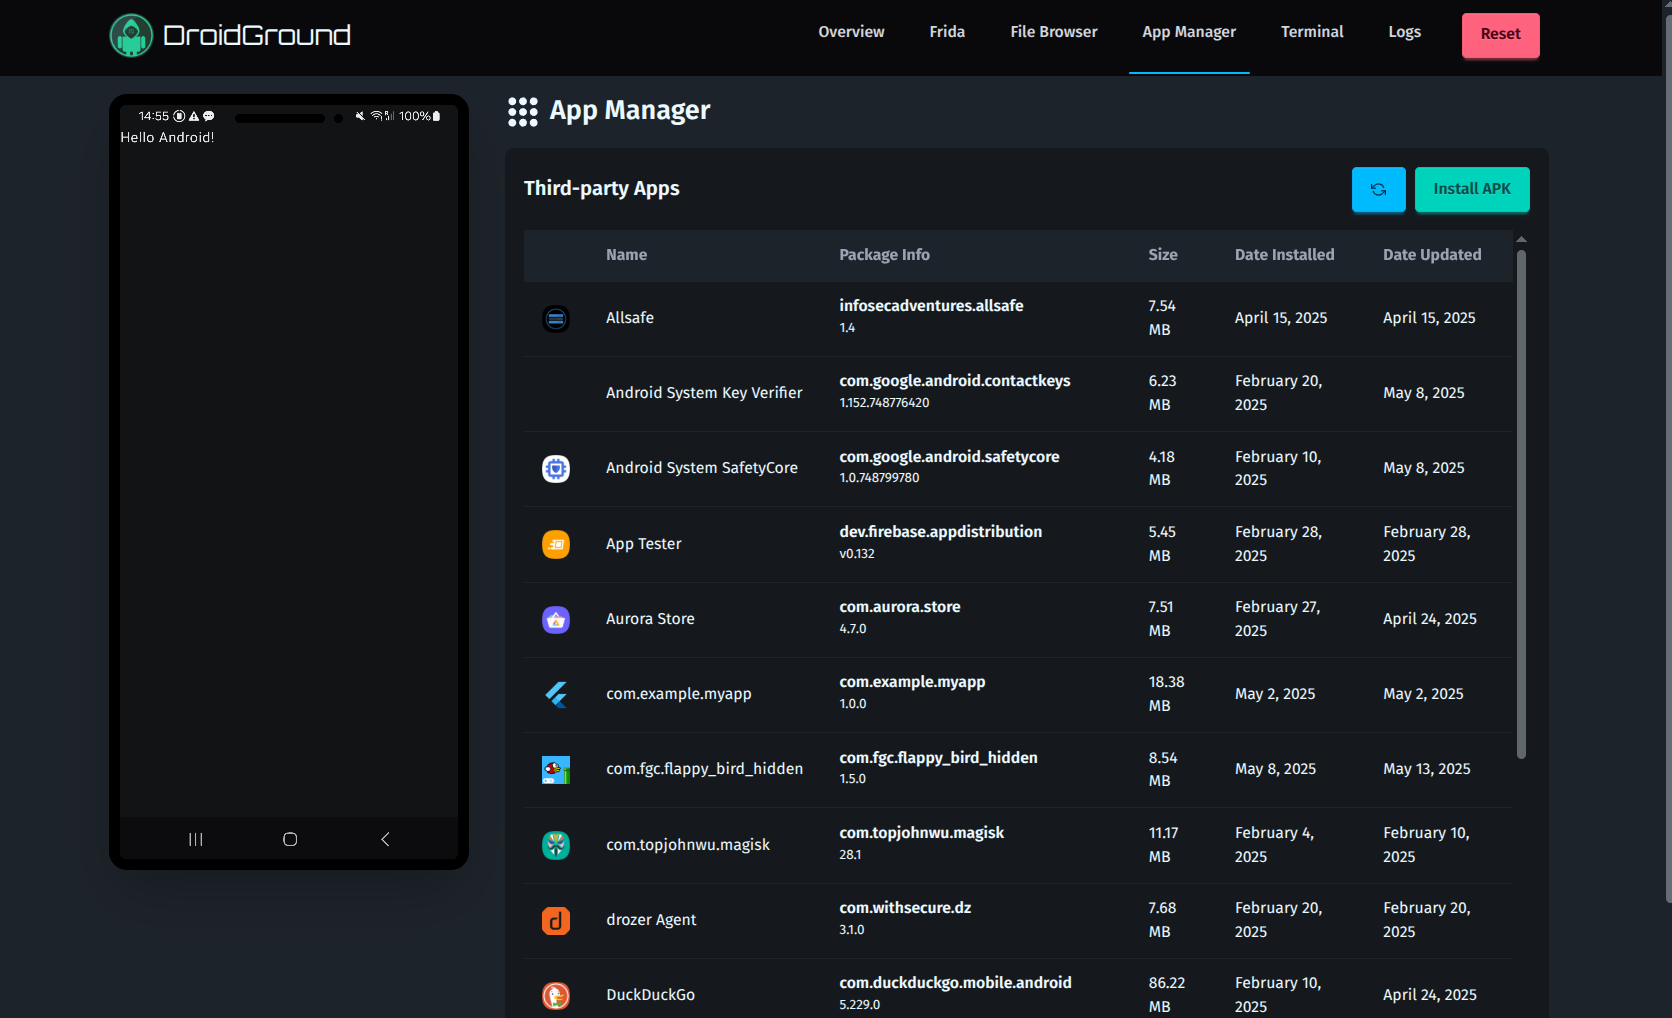 secforce/droidground
A flexible playground for Android CTF challenges.
 retme7/cve-2014-4322_poc
Gain privileges:system -> root,as a part of https://github.com/retme7/CVE-2014-7911_poc
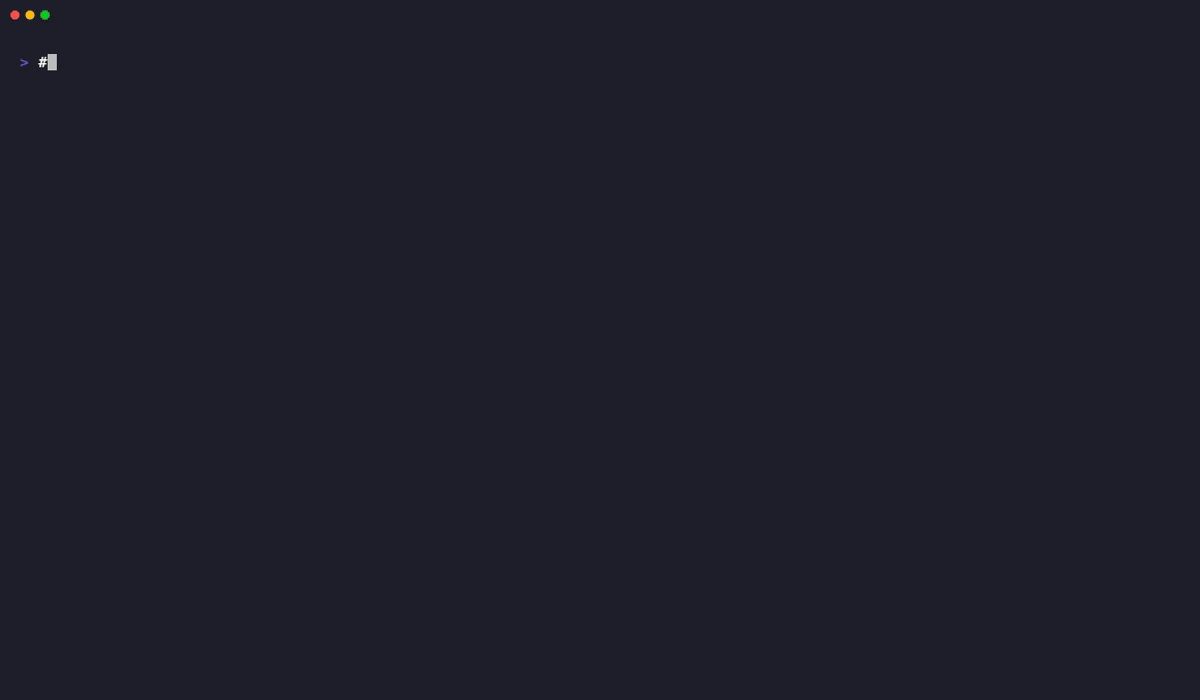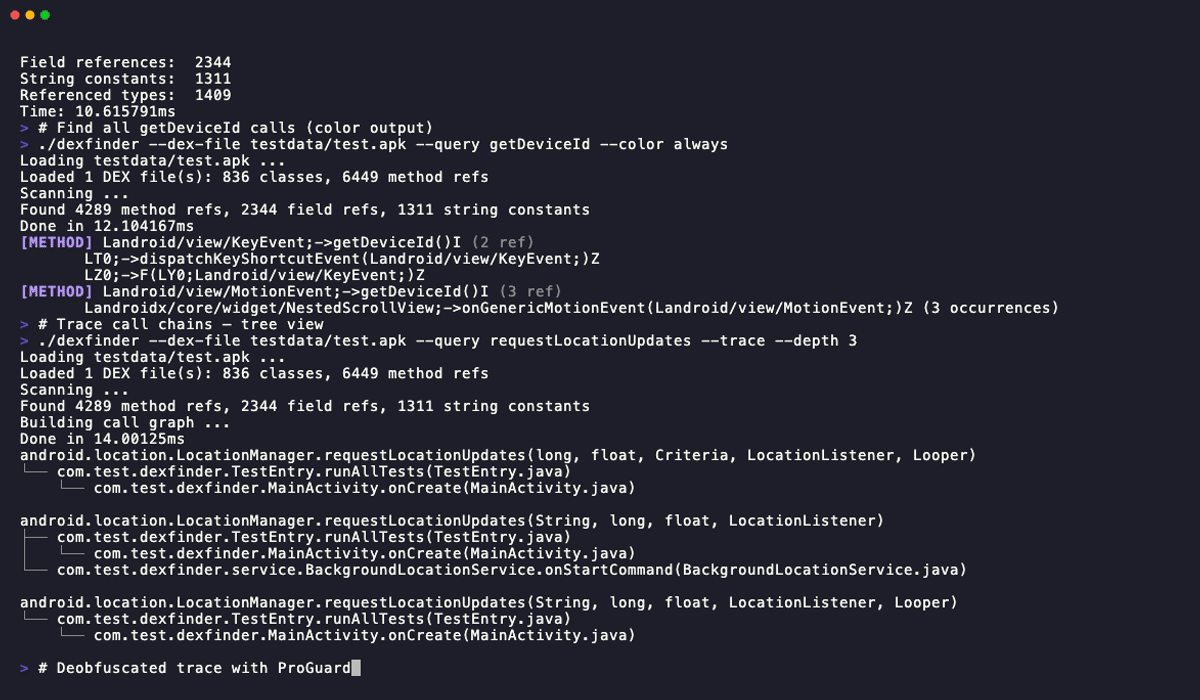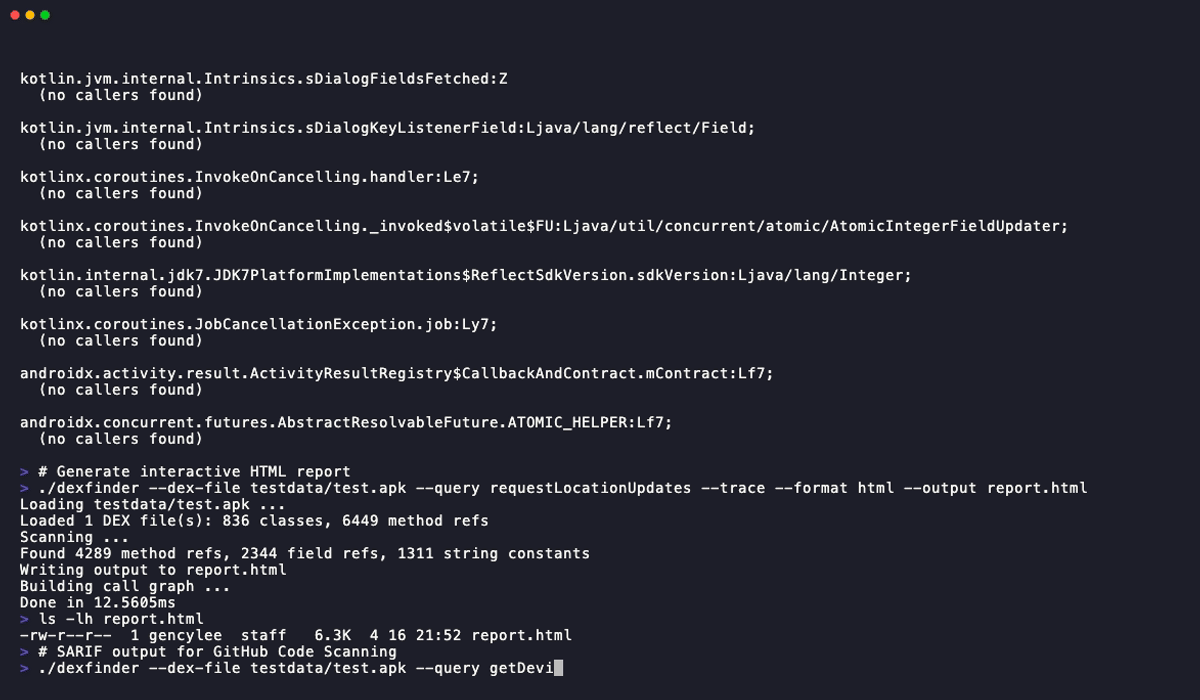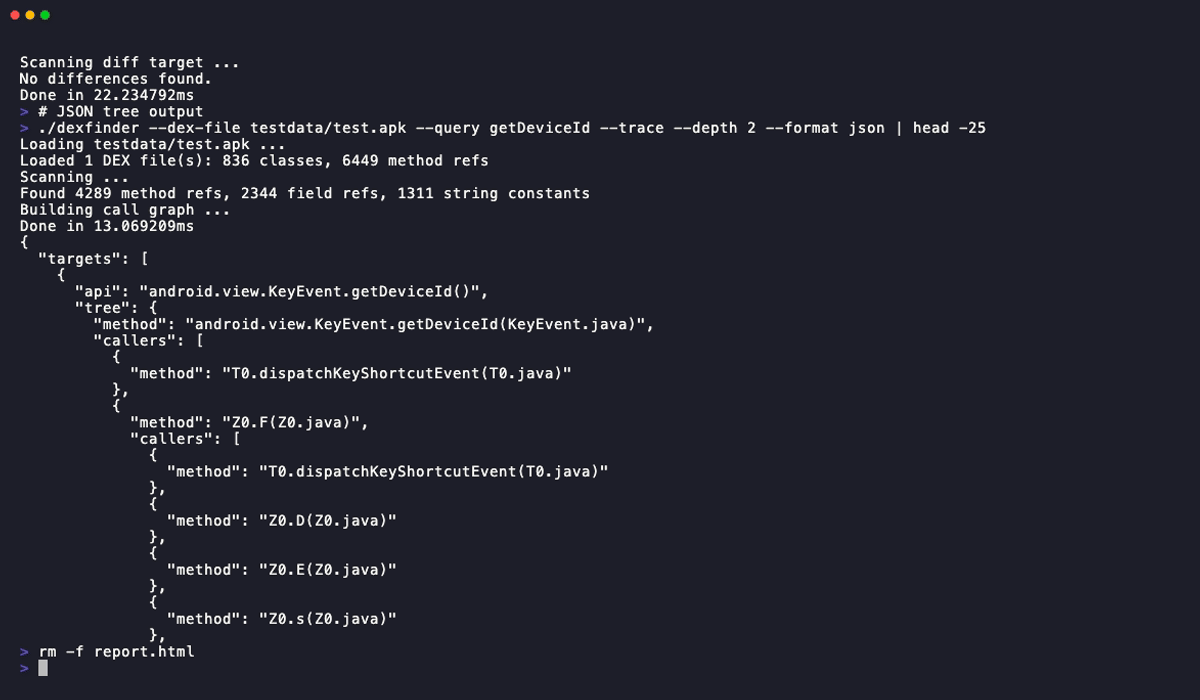 junelegency/dexfinder
Cross-platform APK/DEX method finder with call chain tracing, ProGuard deobfuscation, and hidden API detection
 koozxcv/cve-2014-7911-cve-2014-4322_get_root_privilege
CVE-2014-7911 vulnerability and CVE-2014-4322 vulnerability to get root privilege!
 justsoman/cybermeowfia-ace3
CVE-2026-43499 exploit with OnePlus Ace3 support