
DroidSniper
 k3ystr0k3r/droidsniper
DroidSniper - Misconfigured Android Debug Bridge Scanner
android-securitymisconfigurationpenetration-testing+2
17
k3ystr0k3r/droidsniperDroidSniper - Misconfigured Android Debug Bridge Scanner
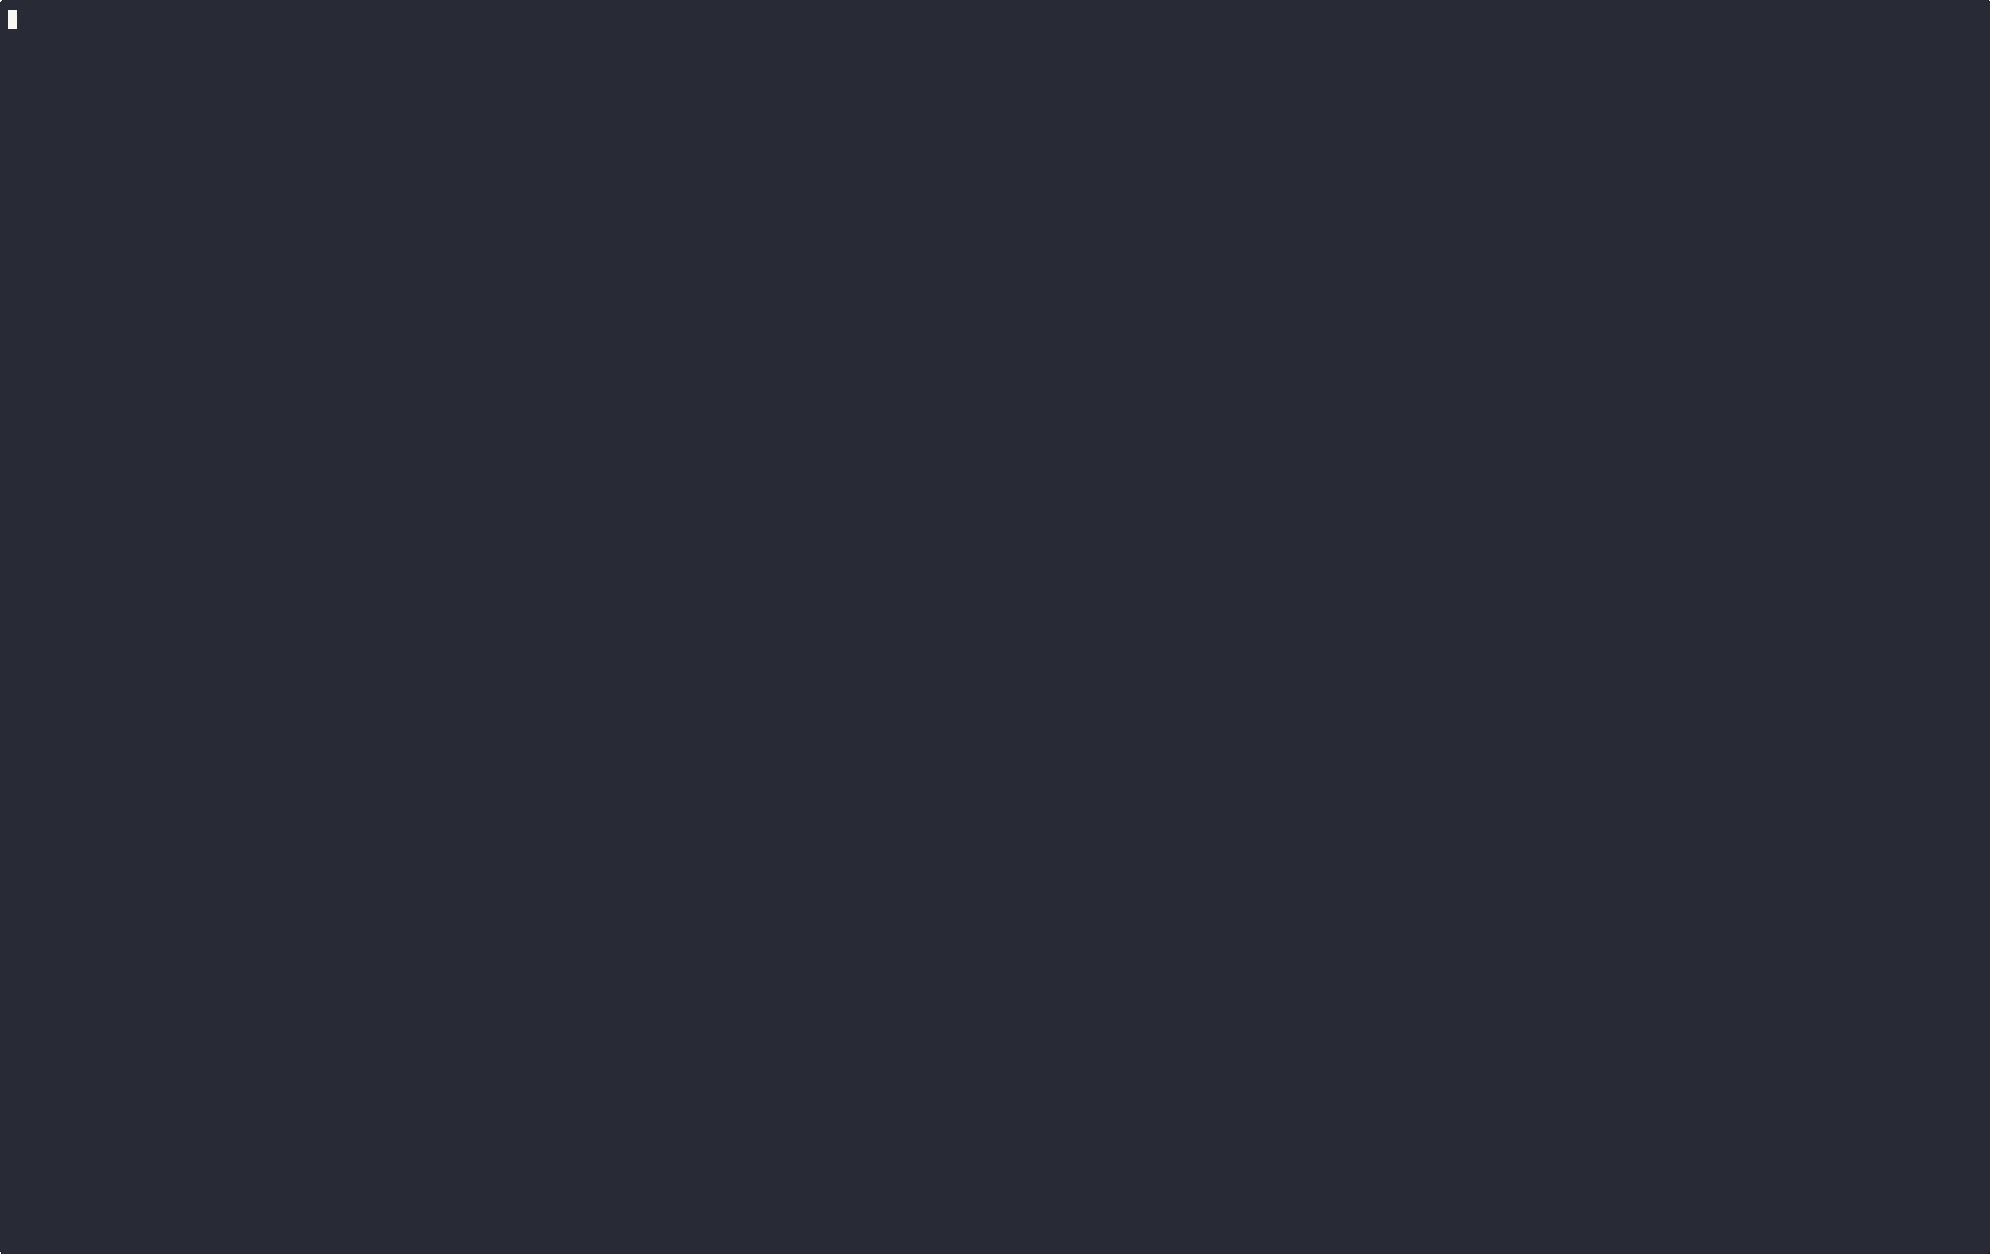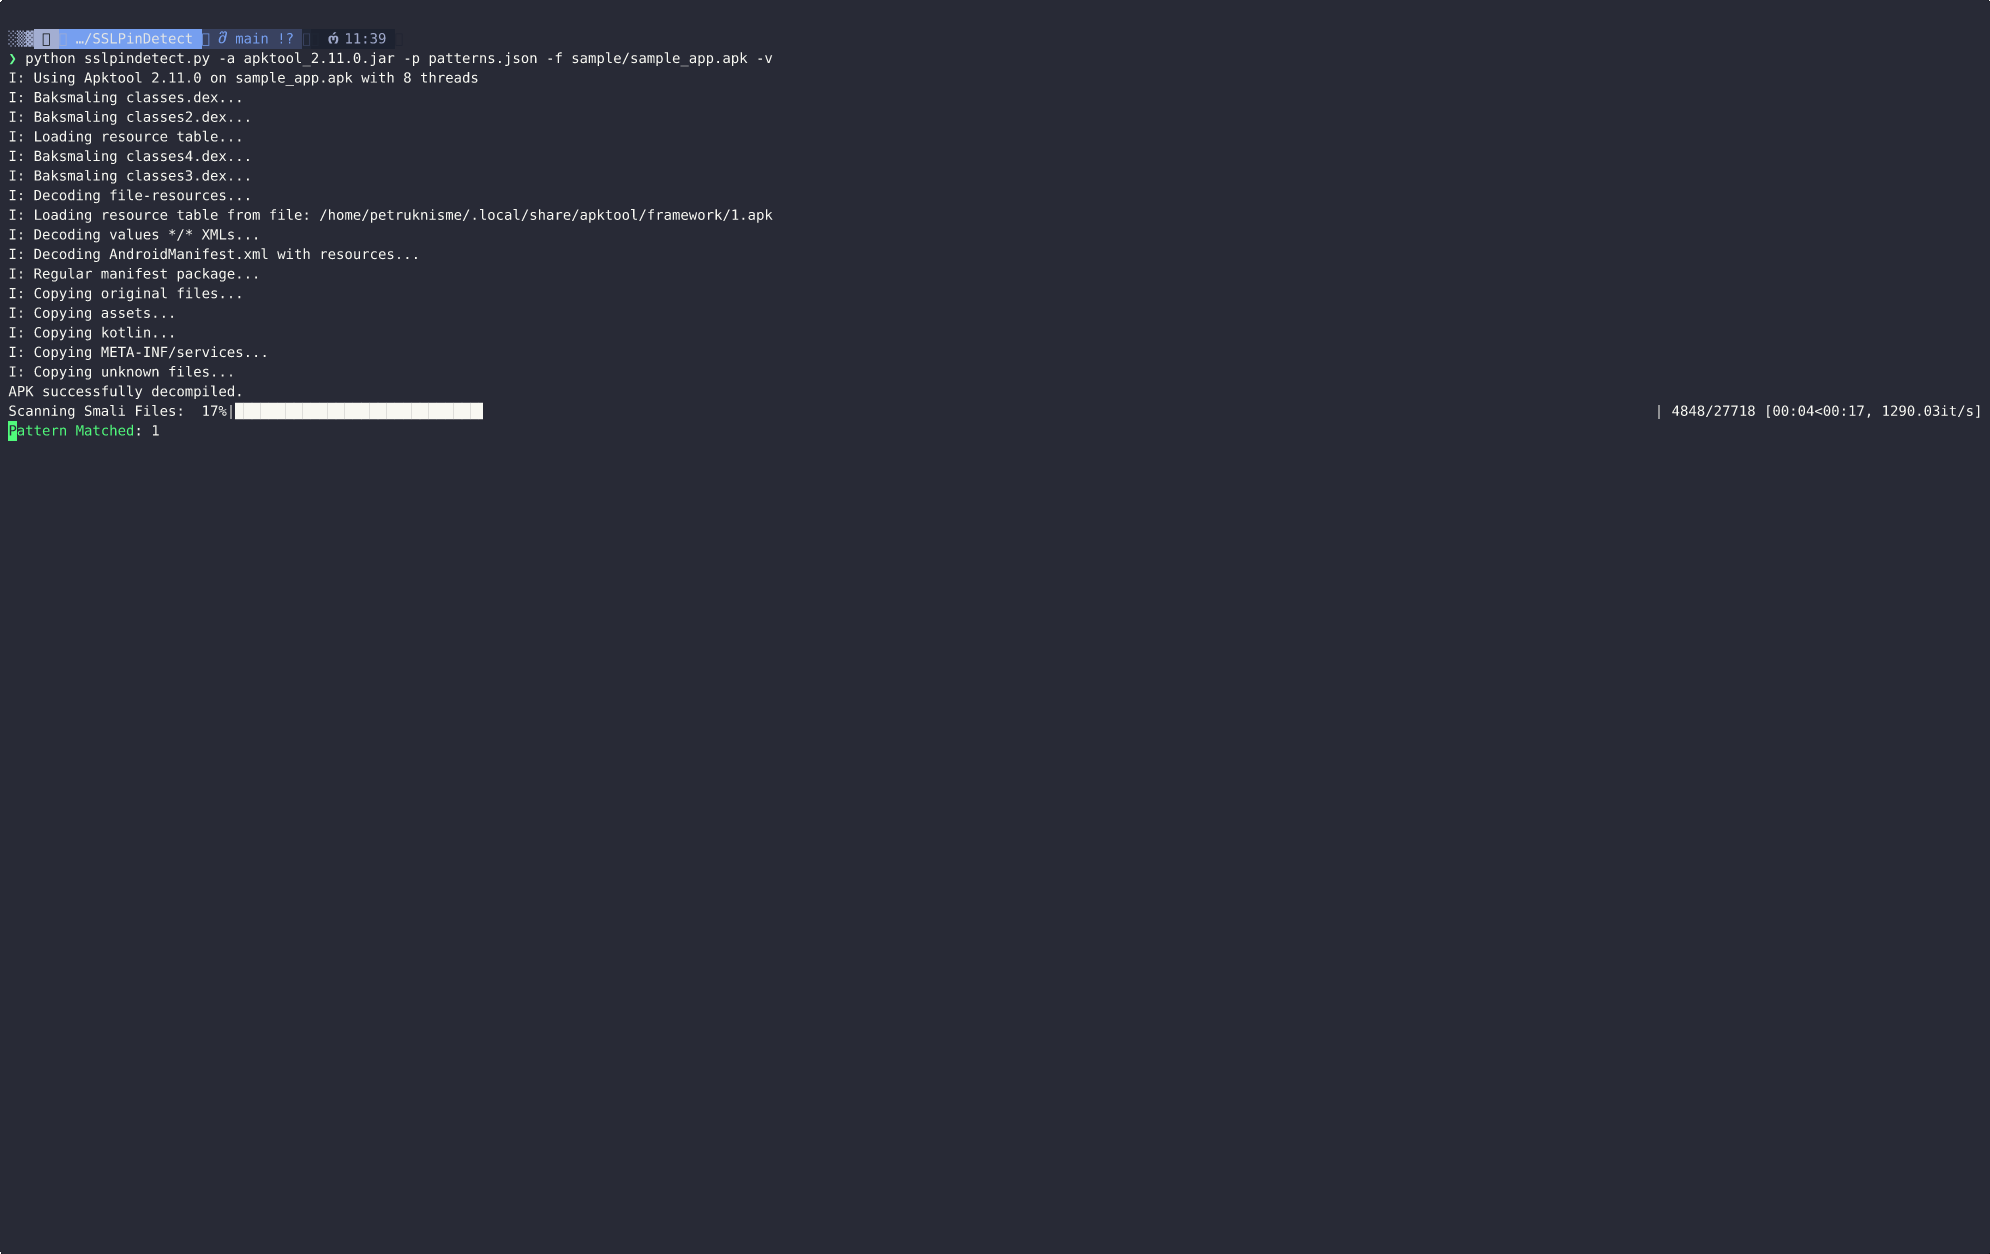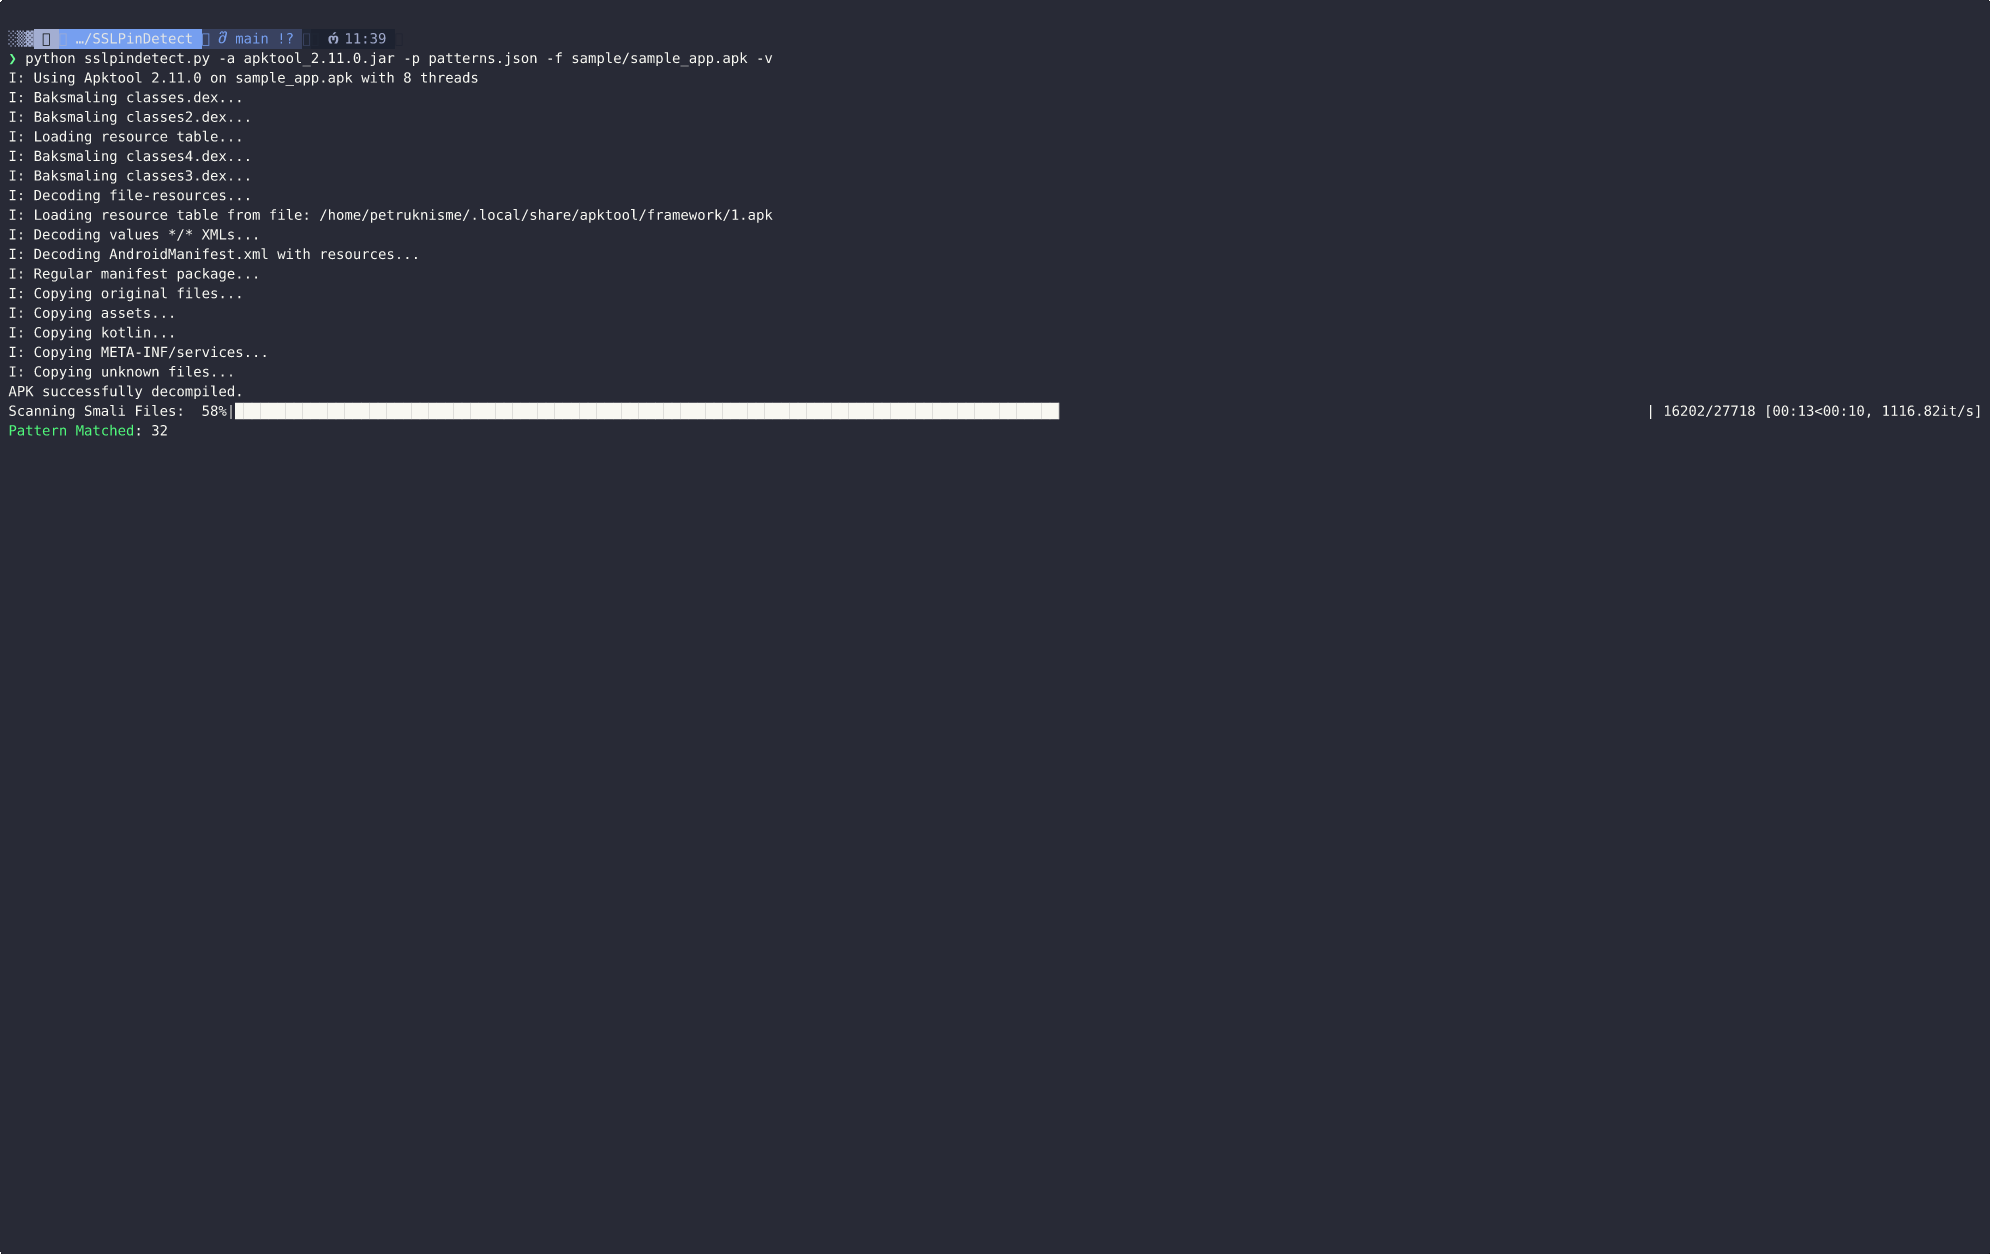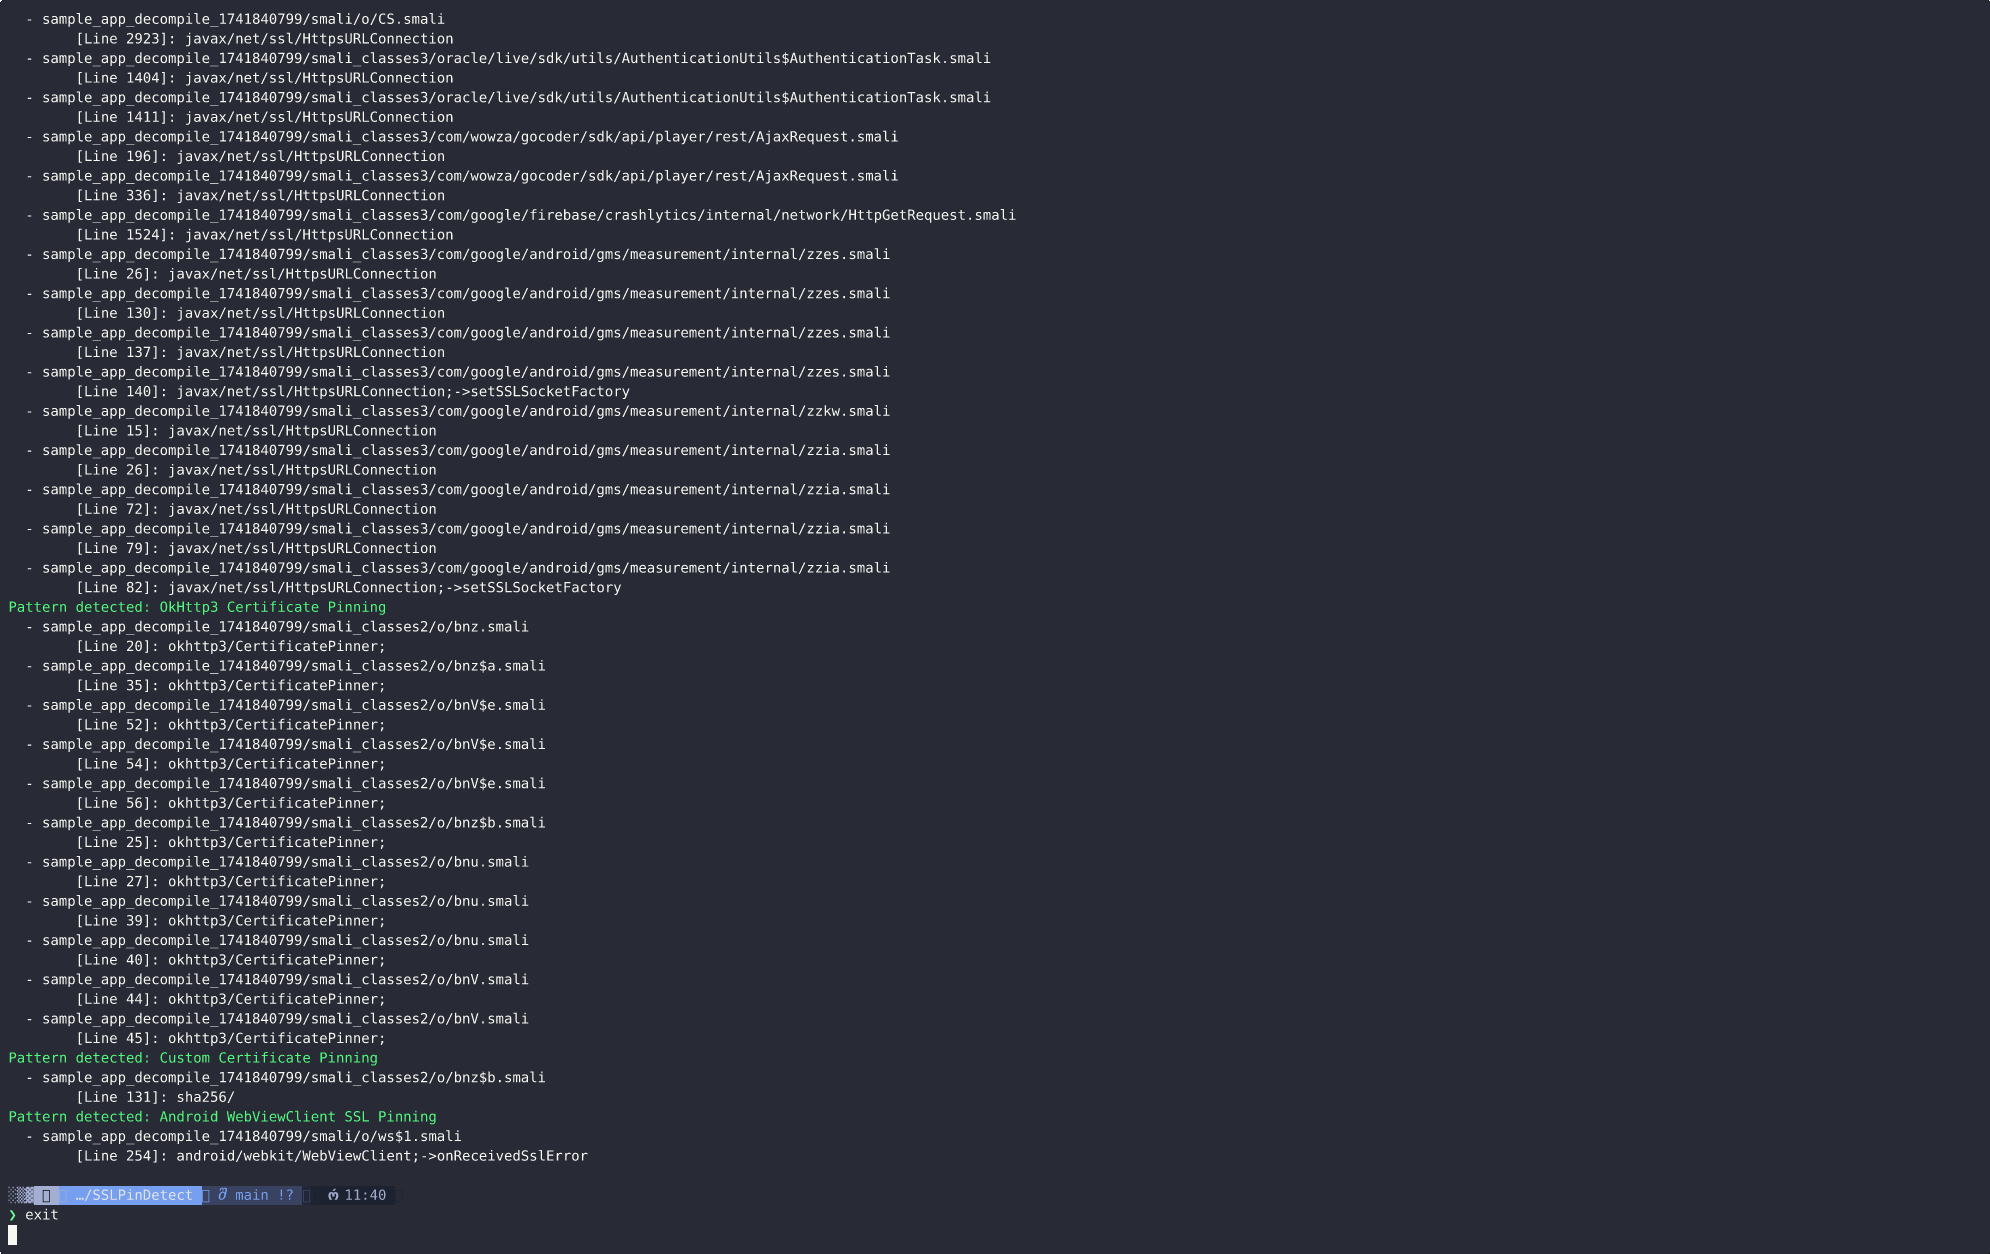 aancw/sslpindetect
SSLPinDetect is a tool for analyzing Android APKs to detect SSL pinning implementations by scanning for known patterns in decompiled code. It helps…
 google/enjarify
Translates Dalvik bytecode (DEX/APK) to equivalent Java bytecode, enabling Java analysis tools to process Android applications with high correctness…
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 webldix/cve-2024-31317-poc-deployer
Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.
 enovella/tee-reversing
A curated list of public TEE resources for learning how to reverse-engineer and achieve trusted code execution on ARM devices
 georgiev-martin/nofrak
Proof Of Concept for Android. NoFrak is designed to prevent fracking attacks, as described in "Breaking and Fixing Origin-Based Access Control in…
 httptoolkit/frida-interception-and-unpinning
Frida scripts to rewrite mobile applications at runtime to directly MitM all HTTPS traffic
 gushmazuko/metasploit_in_termux
Install and run Metasploit Framework 6 on Android via Termux with automated setup, payload generation (msfvenom), and full msfconsole access for…
 darioi/droidcarve
Android Reverse Engineering Framework
 nagendrapittu/cve-2021-521-exploit
Lab Exploit (CVE-2021-521): App uses Java reflection to access Android system components, retrieving a list of all installed apps. Reflection…
 supersonic/cve-2020-0443
Proof of concept app for Android permanent denial-of-service vulnerability CVE-2020-0443
 sarabpal-dev/cheese-cake
A proof-of-concept for CVE-2025-21479, chained with a Dirty Pagetable technique.
 foundryzero/binder-trace
Binder Trace is a tool for intercepting and parsing Android Binder messages. Think of it as "Wireshark for Binder".
 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
 perongh/ghostlock-selinux-disabler
Use CVE-2026-43499 to disable SELinux on Android
 caginkyr/cve-2026-7671
Proof-of-concept for CVE-2026-7671, demonstrating OTP brute-force on Tornet Scooter Android app due to missing rate limiting on /TwoFactor endpoint.