

CVE-2019-11932
 fastmo/cve-2019-11932
Programa para hackear Whatsapp Mediante Gif ,asiendo un exploit con el puerto.
android-securitybinary-exploitationexploitation+4
18
fastmo/cve-2019-11932Programa para hackear Whatsapp Mediante Gif ,asiendo un exploit con el puerto.
 cuteaplane/ghostlock-for-oneplus15t
(CVE-2026-43499)内核漏洞利用程序,适用于未解锁 Bootloader 的一加15T.
 zenyxx-xd/rootmyvivo
One-click root for vivo/iQOO devices on locked bootloader | CVE-2026-43499 + KernelSU
 hiikezoe/diaggetroot
Exploit for CVE-2012-4220 providing root privilege escalation on Android devices via a kernel vulnerability.
 poliva/root-zte-open
exploit for CVE-2012-4220 working on zte-open
 flipphoneguy/root-sonim-xp3800
app that ports CVE-2019-2215 to arm32 and mounts a su binary to /sbin with denylist + root app installer. firehose/Magisk guide included
 wtrwx/smt878u-ionstack-poc
CVE-2026-43499 (IonStack/GhostLock) pure-C re-root POC for Samsung SM-T878U / gts7l (T878USQS8DXE1)
 qm4rs/cve-2026-0075
Probes CVE-2026-0075 Android ContactsProvider side channel with a no-permission PoC, enabling root-cause analysis and patched-vs-vulnerable…
 slapah/ghostlock-h8q
GhostLock CVE-2026-43499 port for Galaxy Z Fold 8 (h8q)
 camsshaft/selinux-permissive-only-cve-2025-21479
This is an SELinux permissive version of the Cheese exploit also known as CVE-2025-21479 which affected the adreno kgsl on many devices including…
 jcalabres/root-exploit-pixel3
Local privilege escalation exploit for Pixel 3 (CVE-2020-0041) that disables SELinux and spawns a root shell via kernel memory corruption and offset…
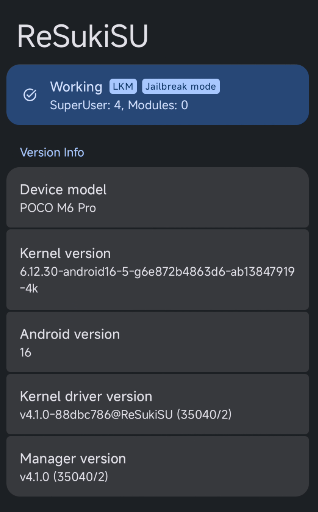 datfooldive/ghostlock-emerald
GhostLock (CVE-2026-43499) kernel exploit for Poco M6 Pro (emerald) with locked bootloader
 mranonymoustz/cve-2019-11932-whatsapp-exploit
Double-free vulnerability in DDGifSlurp in decoding.c in libpl_droidsonroids_gif can read more…
 mmiszczyk/cve-2024-33352
BlueStacks privilege escalation through VM backdooring
 yijiacloud/ghostlock-cve-2026-43499-4.19-k40
CVE-2026-43499 (GhostLock) rtmutex remove_waiter() UAF local-root PoC adapted for Qualcomm Android 4.19 kernels (Redmi K40 / Snapdragon 870 class),…
 mobilehackinglab/cve-2026-0047-poc
CVE-2026-0047: Missing permission check in ActivityManagerService.dumpBitmapsProto() — steal UI bitmaps from every running app with zero permissions…
 nothingfumo/ghostlock-aresin
GhostLock (CVE-2026-43499) exploit for POCO F3 GT (aresin) — MediaTek Dimensity 1200, Linux 4.14.186 ARM64 kernel privilege escalation via futex PI…
 xiaohj233/ghostlock-x200-root
GhostLock-X200 v1.0 - temporary root toolchain for vivo X200 (PD2415 / b57 kernel) based on CVE-2026-43499. For authorized security research only.