
CVE-2026-40000
 skorpion96/cve-2026-40000
A poc for a vulnerability in ZTE File Manager (zte.com.cn.filer) which allows to read arbitrary files from other apps as the privileges of this file…
android-securityexploitationmobile-security+3
1
skorpion96/cve-2026-40000A poc for a vulnerability in ZTE File Manager (zte.com.cn.filer) which allows to read arbitrary files from other apps as the privileges of this file…
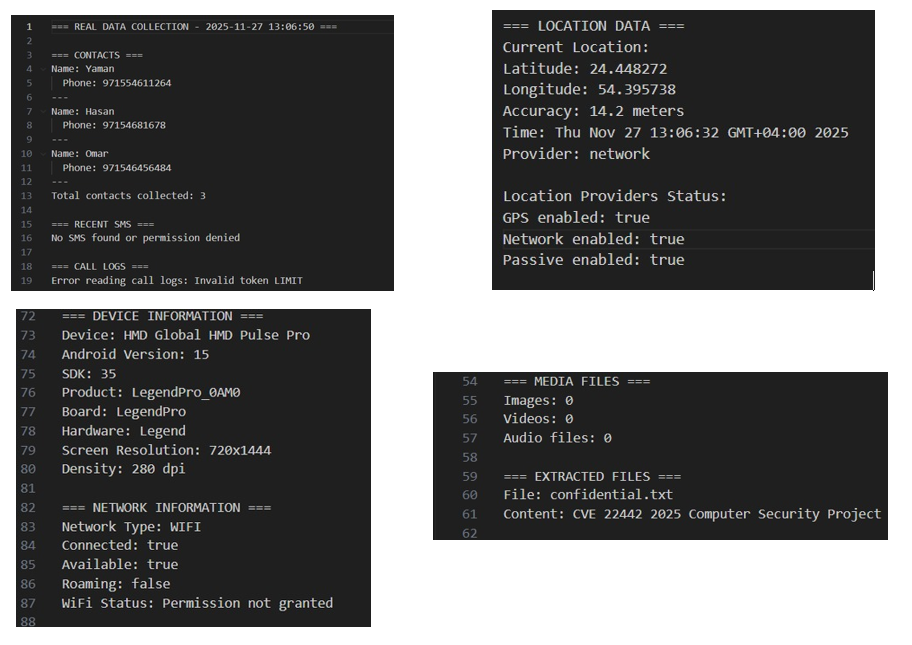 hasan-al-hussein/android-workprofile-exploit
Controlled defensive analysis of CVE-2025-22442 work-profile provisioning, policy timing, and enterprise isolation.
 humoud/hooketh
A set of scripts that ease working with frida
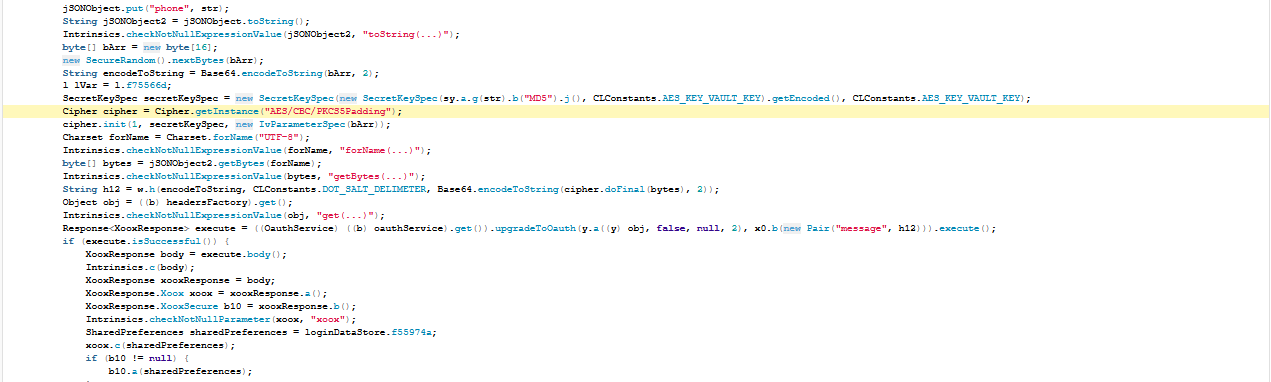 honestcorrupt/meesho-android-improper-encryption-cve-2026-5682
Proof of concept demonstrating insecure AES-CBC encryption with MD5 key derivation in the Meesho Android app, enabling ciphertext tampering and…
 kpatsakis/poc_cve-2017-0807
Proof of concept of CVE-2017-0807
 r3n3r0/cve-2026-0049
PoC and analysis of a zero-click DoS in Android's DNG SDK, with crafted DNG samples, an NDK crash harness, and UBSan/IntSan reproduction of the…
 ravss/bluetooth-crash-cve-2017-0785
Exploit script for CVE-2017-0785 that crashes the Bluetooth module on Android 4.0+ devices by sending crafted SDP search requests, causing…
 honestcorrupt/phonepe-sensitive-data-exposure-cve-2025-5154
CVE-2025-5154: Proof-of-concept for unencrypted local storage of authentication tokens, PII, and KYC data in the PhonePe Android app, enabling…
 snip3r69/cve-2013-4710-webview-rce-vulnerability
Android 3.0 through 4.1.x on Disney Mobile, eAccess, KDDI, NTT DOCOMO, SoftBank, and other devices does not properly implement the WebView class,…
 shaikusaf/system_bt_aosp10_r33_cve-2021-0431
Android Bluetooth stack (Fluoride) with a specific patch for CVE-2021-0431, enabling analysis and testing of Bluetooth vulnerabilities in AOSP 10.
 nanopathi/system_bt_aosp10_r33_cve-2020-0463
Android Bluetooth stack (Fluoride) with a fix for CVE-2020-0463, enabling security analysis and exploitation testing of Bluetooth vulnerabilities on…
 shaikusaf/system_bt_aosp10_r33_cve-2021-0435
AOSP Bluetooth stack repository modified for CVE-2021-0435, providing a patched or vulnerable version for analysis and testing of Bluetooth…
 pazhanivel07/system_bt_a10-r33_cve-2021-0474
Android Fluoride Bluetooth stack source code with a focus on CVE-2021-0474, providing a foundation for vulnerability research and security analysis…
 bingghost/cve-2017-0478
poc of CVE-2017-0478
 shaikusaf/system_bt_aosp10_r33_cve-2022-20224
AOSP Bluetooth stack repository modified to address CVE-2022-20224, providing a patched version of the Fluoride Bluetooth stack for Android 10.
 shaikusaf/system_bt_aosp10_r33_cve-2020-0380
AOSP Bluetooth stack (Fluoride) with a patch for CVE-2020-0380, enabling analysis and testing of Bluetooth vulnerabilities on Android 10.
 sumeetit/cve-2022-20607
In the Pixel cellular firmware, there is a possible out of bounds write due to a missing bounds check. This could lead to remote code execution with…
 shaikusaf/external_wpa_supplicant_8_aosp10_r33cve-2021-0326
Android Wi-Fi vulnerability research repository containing patched wpa_supplicant source for CVE-2021-0326, enabling analysis and testing of the…