
com.phlox.tvwebbrowser
 actuator/com.phlox.tvwebbrowser
CVE-2023-43955
android-securityexploitationmobile-security+2
1
actuator/com.phlox.tvwebbrowserCVE-2023-43955
 actuator/com.enflick.android.textnow
CVE-2024-36437
 nanopathi/system_bt_aosp10_r33_cve-2020-0225
Exploit for CVE-2020-0225 in the Android Fluoride Bluetooth stack, enabling remote code execution via a crafted Bluetooth packet. Includes build…
 satheesh575555/system_bt_aosp10_r33_cve-2021-0589
AOSP Bluetooth stack with a patch for CVE-2021-0589, providing a vulnerable version for security research and exploit development.
 bingghost/cve-2017-0478
poc of CVE-2017-0478
 sloden1977-lang/root-zte-x1001
Magisk root guide for ZTE Blade X1001 (Android 15, Unisoc UMS9230) using CVE-2022-38694 exploit. Contributions and screenshots welcome.
 satheesh575555/system_bt_aosp10_r33-cve-2020-0138
Android Bluetooth stack (Fluoride) with a specific patch for CVE-2020-0138, addressing a critical vulnerability in the Bluetooth component.
 shaikusaf/system_bt_aosp10_r33_cve-2022-20224
AOSP Bluetooth stack repository modified to address CVE-2022-20224, providing a patched version of the Fluoride Bluetooth stack for Android 10.
 nanopathi/system_bt_aosp10_r33_cve-2021-0522
Android Bluetooth stack (system/bt) source code including patch for CVE-2021-0522 privilege escalation vulnerability.
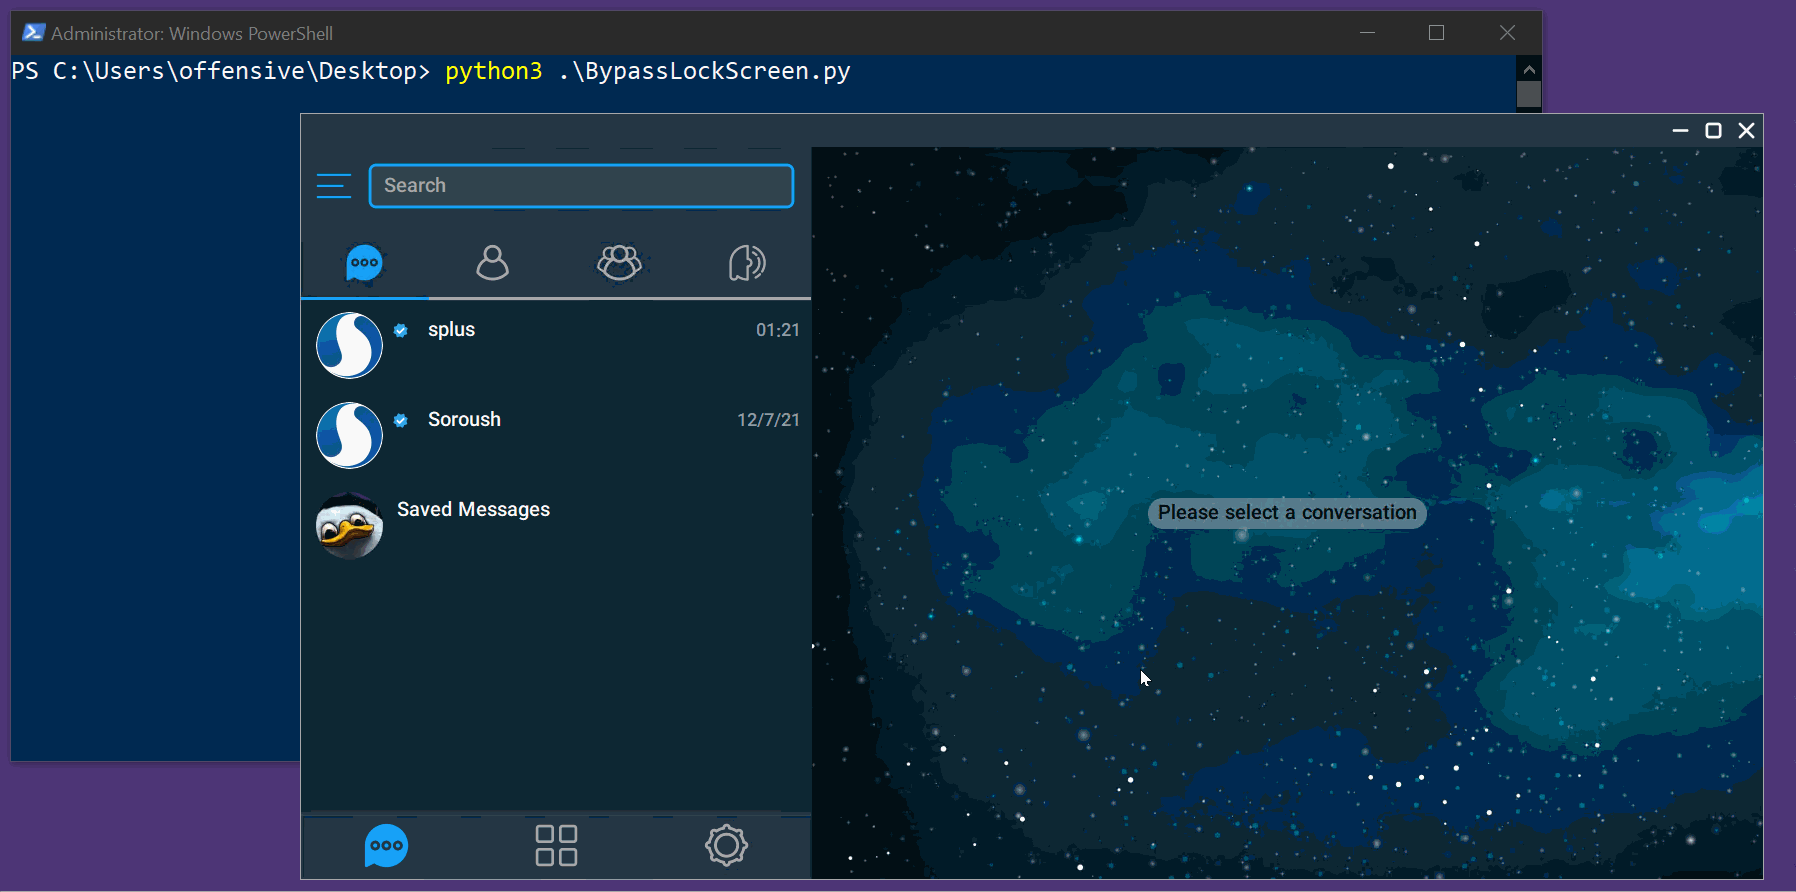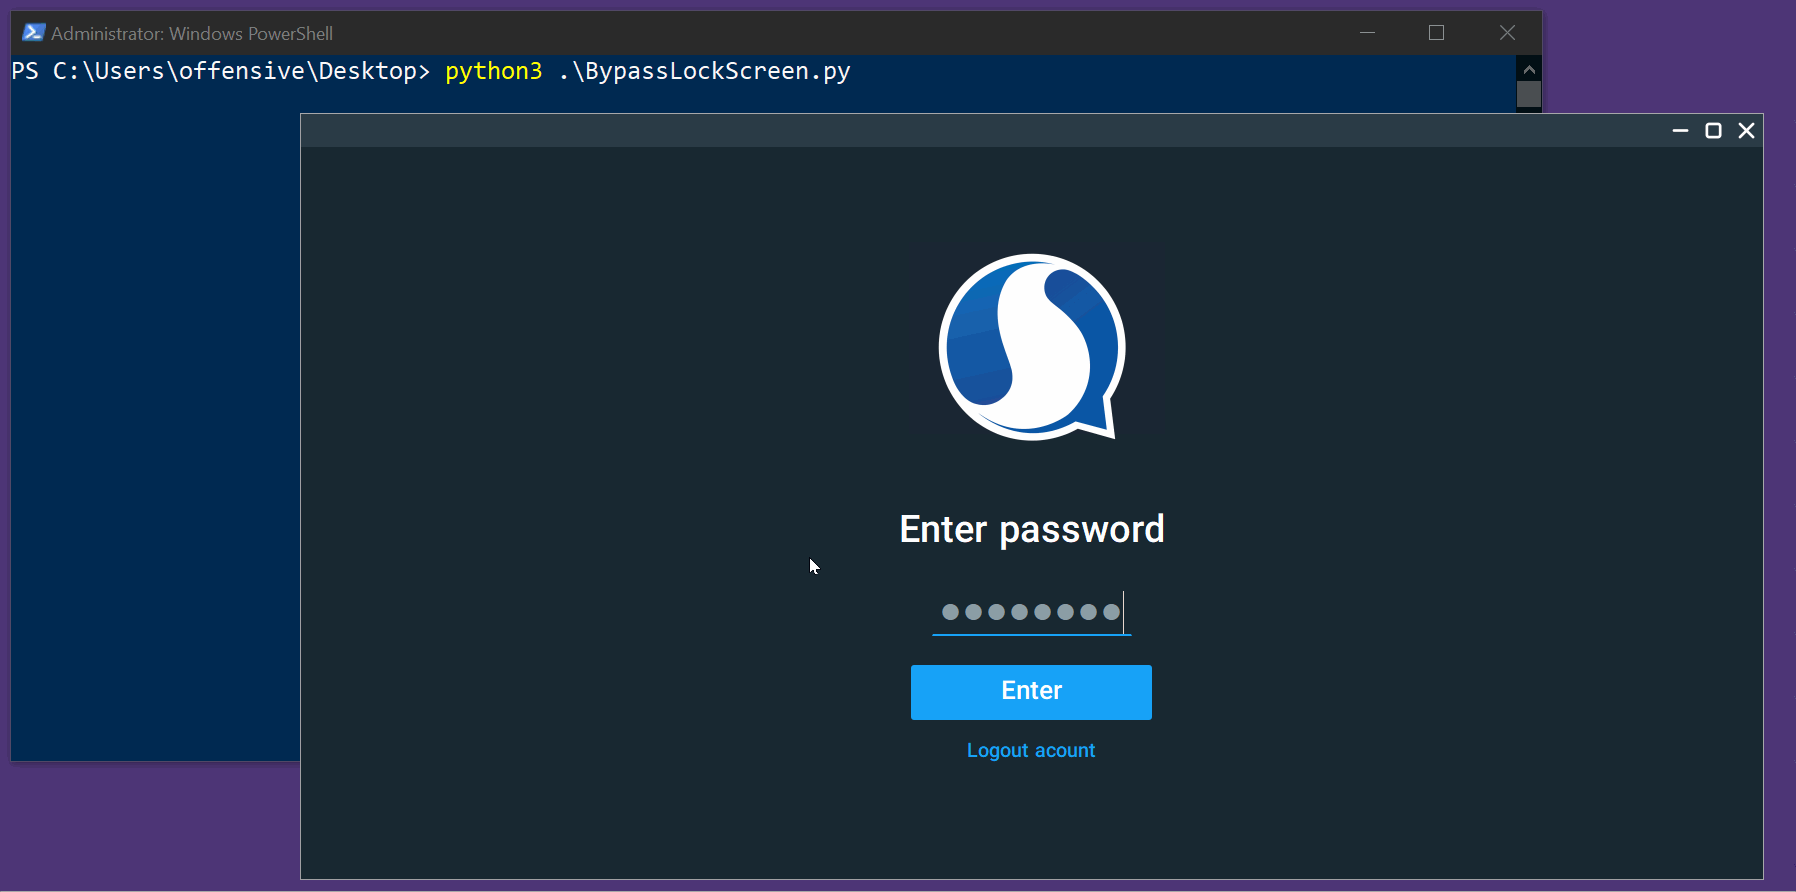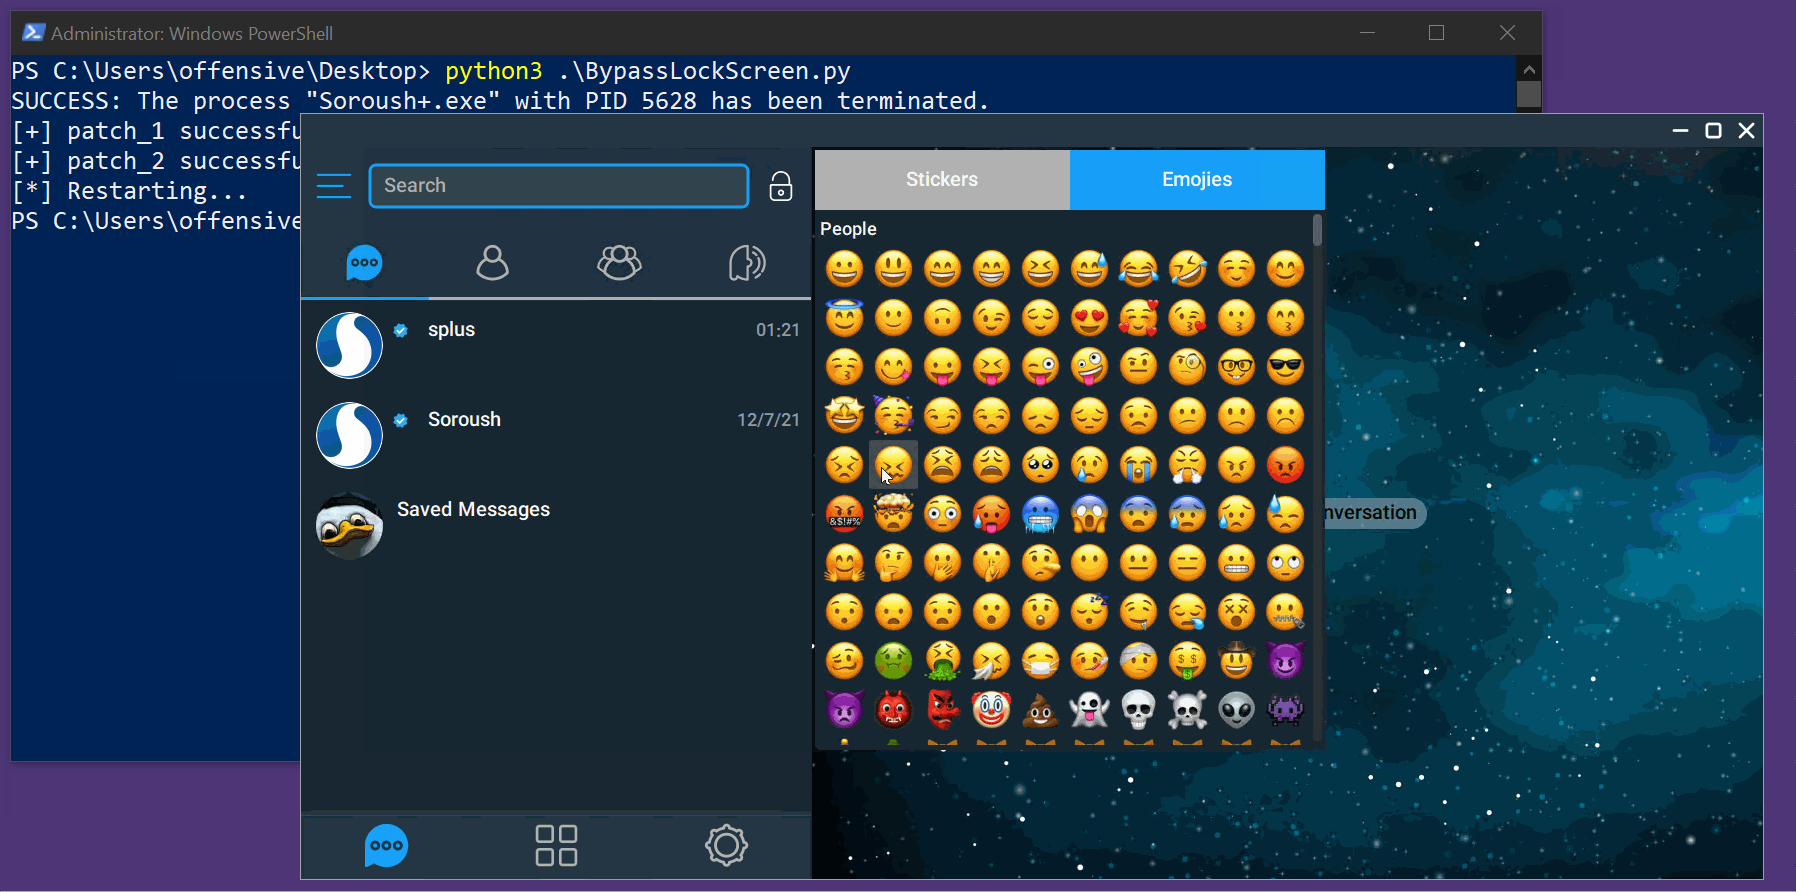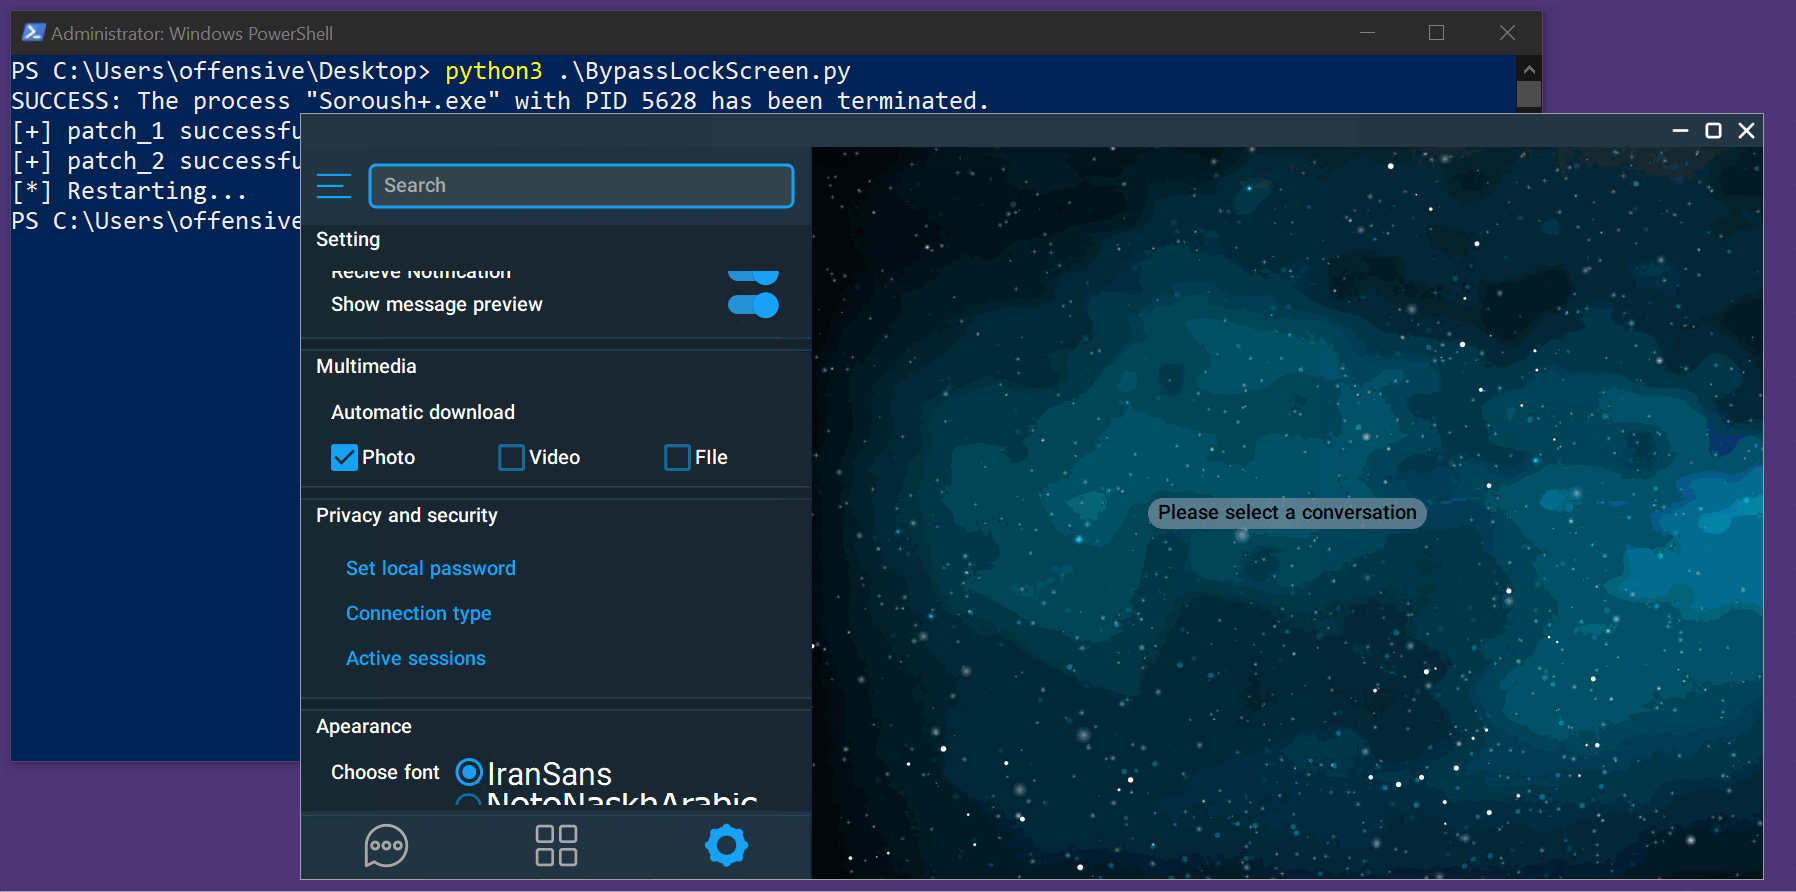 scopion/cve-2022-26629
PoC exploit for CVE-2022-26629: bypasses the lock screen on SoroushPlus+ Messenger 1.0.30 via improper access control. Includes an auto-exploit…
 pazhanivel07/system_bt_a10_r33_cve-2021-0474
Android Bluetooth stack (Fluoride) with a specific patch for CVE-2021-0474, providing source code for building and testing the Bluetooth component on…
 mazx0p/cve-2014-8609-poc
pendingintent vulnerability
 sumeetit/cve-2022-20607
In the Pixel cellular firmware, there is a possible out of bounds write due to a missing bounds check. This could lead to remote code execution with…
 abrarkhan/g3_frameworks_av_cve-2024-0023
Proof-of-concept exploit for CVE-2024-0023 in Android's frameworks/av, implemented in C++ to demonstrate the media framework vulnerability.
 shinycolumn/cve-2025-50944
Improper Certificate Chain Validation in EagleEyes Lite Android Application
 actuator/com.simplemobiletools.dialer
CVE-2023-49003
 trinadh465/frameworks_av_cve-2023-20933
Exploit or patch for Android media framework vulnerability CVE-2023-20933, targeting frameworks_av component.
 likekabin/cve-2017-0478
Proof-of-concept exploit for CVE-2017-0478, a remote code execution vulnerability in Android's mediaserver via crafted WebP images. Includes…