
AOSP-DownloadProviderDbDumperSQLiWhere
 ioactive/aosp-downloadproviderdbdumpersqliwhere
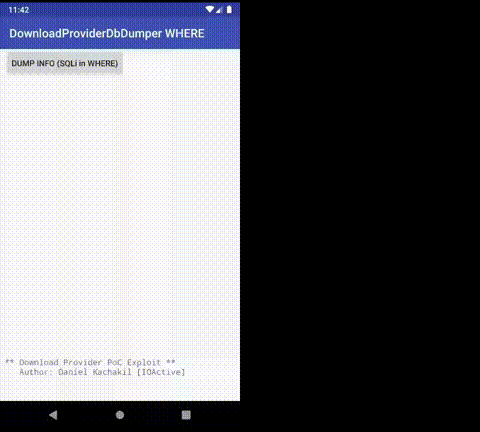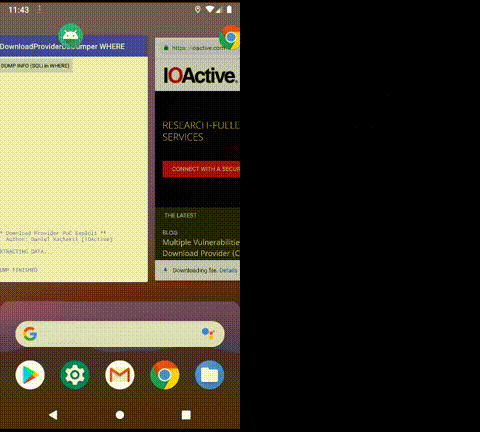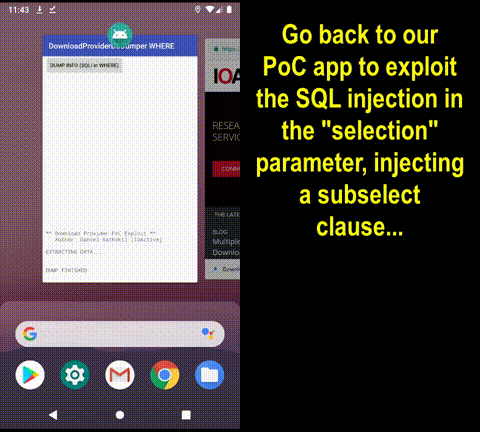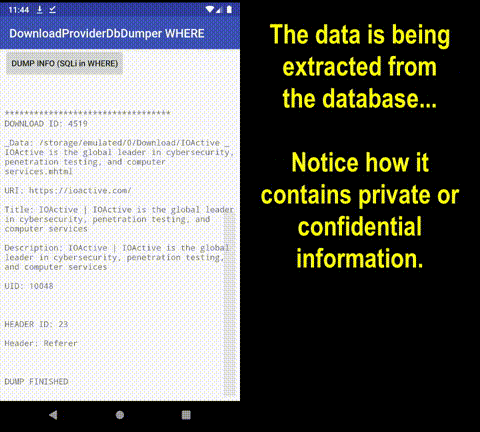
PoC Exploiting SQL Injection in Android's Download Provider in Selection Parameter (CVE-2019-2198)
android-securityexploitationmobile-security+3
35
ioactive/aosp-downloadproviderdbdumpersqliwherePoC Exploiting SQL Injection in Android's Download Provider in Selection Parameter (CVE-2019-2198)
 eudemonics/scaredycat
Python script to generate a malicious MP4 file and start a CherryPy web server hosting a simple HTML page with the embedded file. Exploits another…
 xv4l3x/hermit
Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
 anyone202/cybermeowfia-termux
Termux Privilege Escalation Tool & Root Manager - CVE-2026-43501
 ejfkdev/avdroot
Root an Android Studio emulator by patching its ramdisk with Magisk — in pure Go.
 ioactive/aosp-downloadproviderdbdumper
PoC Exploiting SQL Injection in Android's Download Provider (CVE-2018-9493)
 tinopreter/docviewerexploitapp
This is an Exploit App I made when solving the DocumentViewer challenge (CVE-2021-40724) from MobileHackingLab. It will download a libdocviewe_pro.so…
 nccgroup/android_demystification_toolbox
ADT is a toolset designed to help model application behavior, research and test security vulnerabilities, and facilitate reversing hostile code.
 actuator/com.heytap.browser
CVE-2024-23729
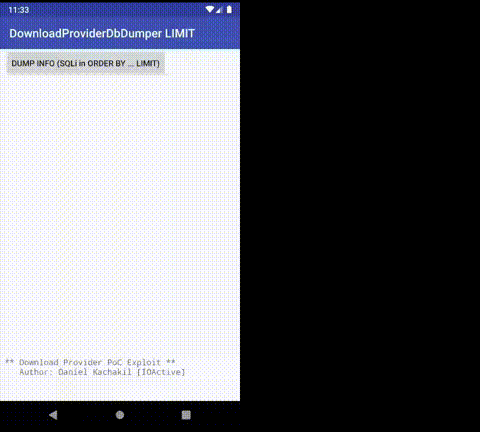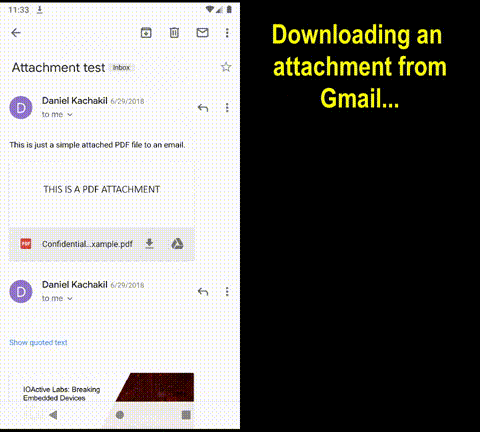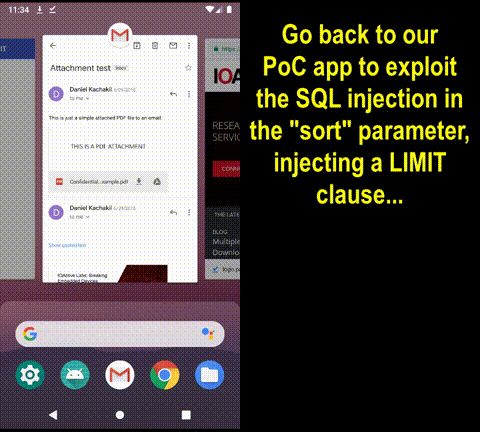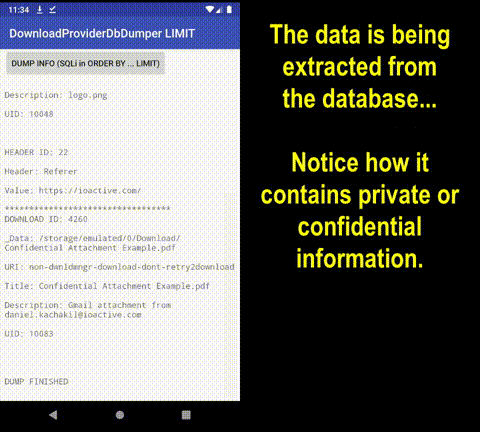 ioactive/aosp-downloadproviderdbdumpersqlilimit
PoC Exploiting SQL Injection in Android's Download Provider in Sort Parameter (CVE-2019-2196)
 minanagehsalalma/zte-smartlife-app-pwned
ZTE SmartLife security findings leading to account takeover: 100K+ Google Play downloads and CVE-2026-86552 through CVE-2026-86555.
 actuator/ekoparty
Ekoparty Miami | Interface Anti-Patterns: Exploiting Insecure Navigation in 3rd Party Android App Lockers
 edwins907/xiaomi-cve-2024-45352
Reporte técnico sobre vulnerabilidad crítica de Xiaomi
 shanika04/nextcloud_android
SQLi CVE-2019-5454