

mvt
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
android-securitydigital-forensicsdisk-forensics+7
15.2k
mvt-project/mvtForensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 firerpa/lamda
Android Full-Stack Device Control Platform: WebRTC/H.264 remote desktop, UI/OCR/image-matching automation, one-click MITM, built-in Frida,…
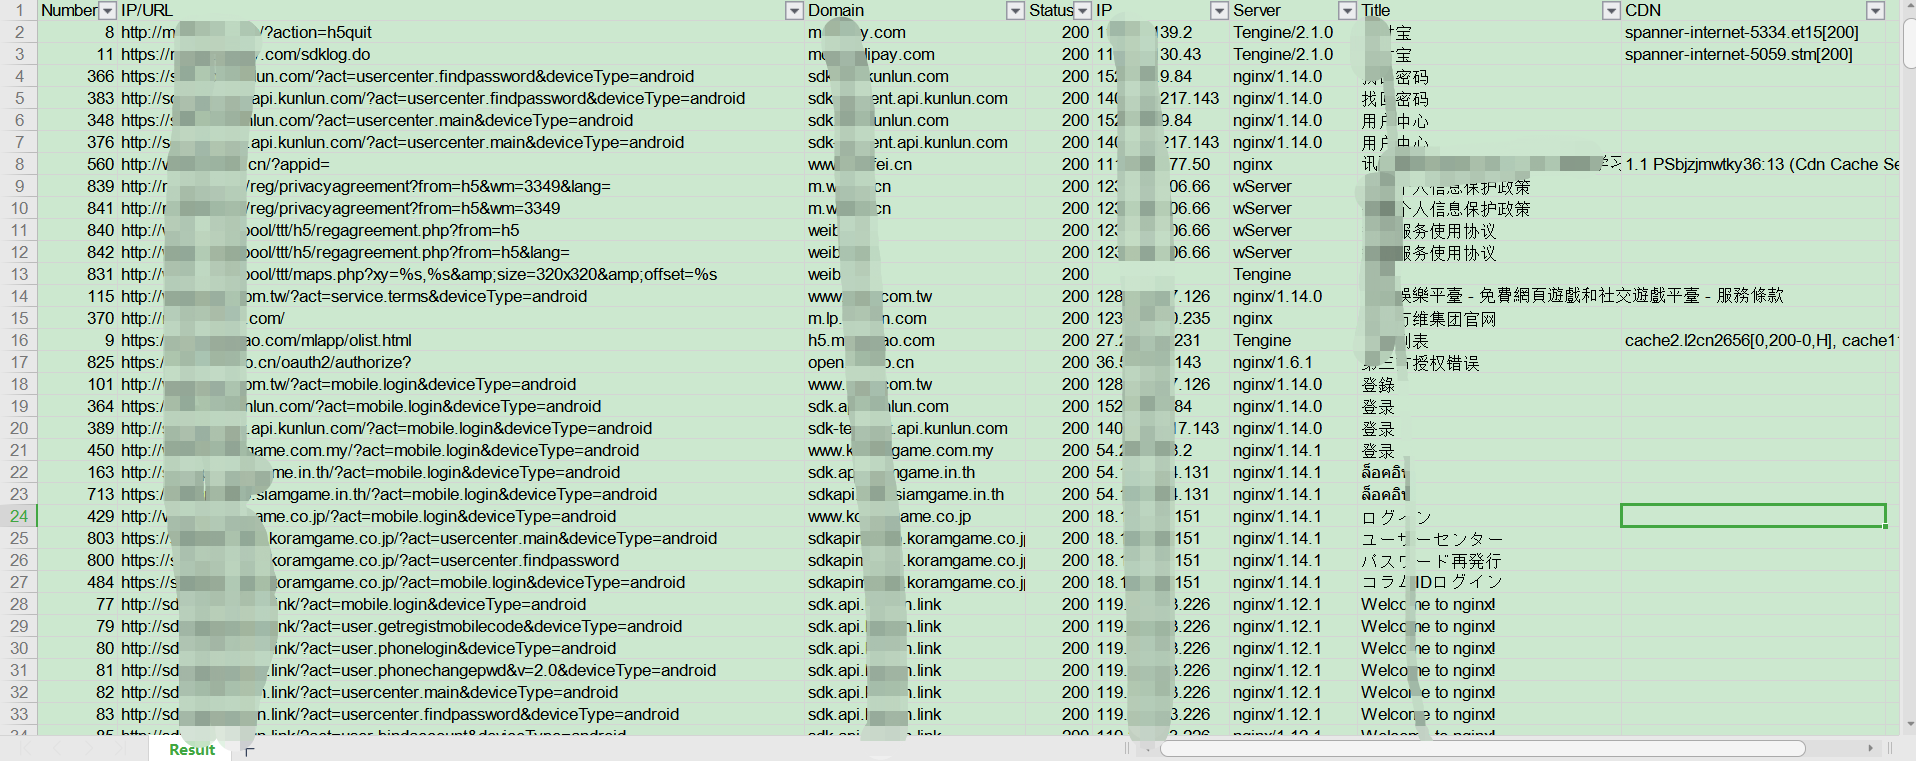 kelvinben/appinfoscanner
一款适用于以HW行动/红队/渗透测试团队为场景的移动端(Android、iOS、WEB、H5、静态网站)信息收集扫描工具,可以帮助渗透测试工程师、攻击队成员、红队成员快速收集到移动端或者静态WEB站点中关键的资产信息并提供基本的信息输出,如:Title、Domain、CDN、指纹信息、状态信息等。
 nfcgate/nfcgate
An NFC research toolkit application for Android
 igio90/dwarf
Full featured multi arch/os debugger built on top of PyQt5 and frida
 dere-ad2001/frida-labs
The repo contains a series of challenges for learning Frida for Android Exploitation.
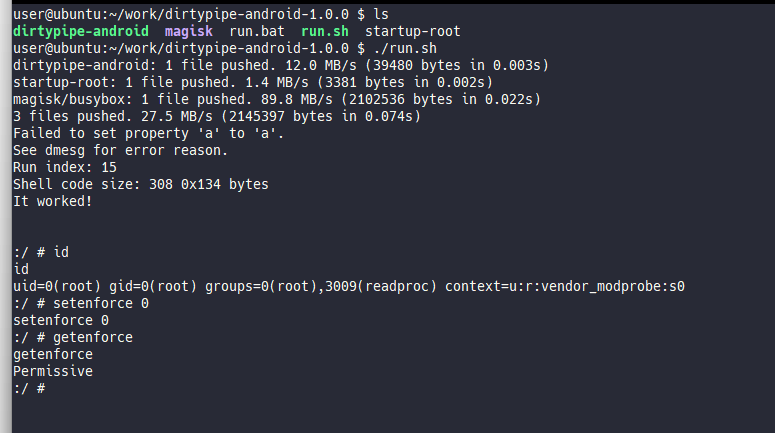 polygraphene/dirtypipe-android
Dirty Pipe root exploit for Android (Pixel 6)
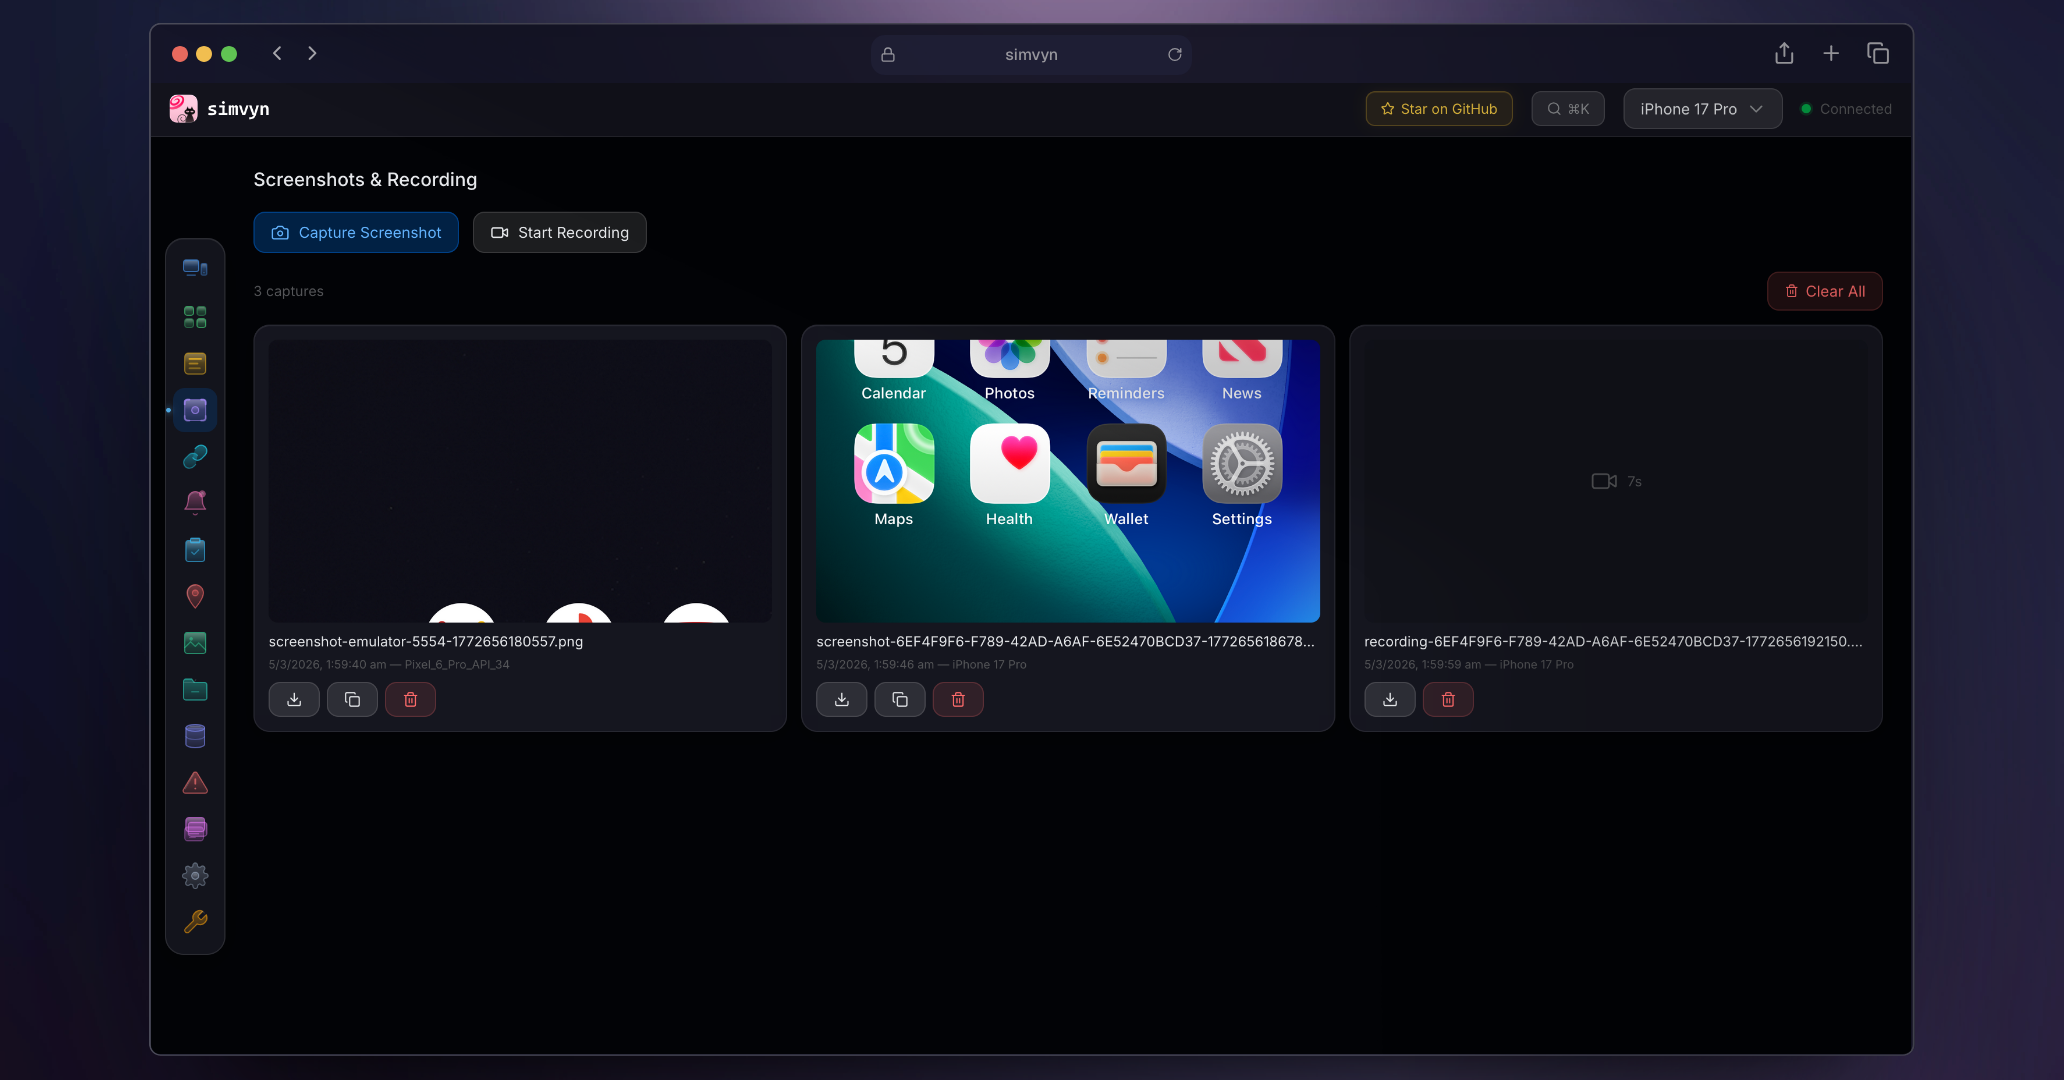 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
 secure-system/insular
Isolate your big brother apps https://secure-system.gitlab.io/Insular/
 bluefrostsecurity/cve-2020-0041
Exploits for Android Binder bug CVE-2020-0041
 sultanahamer/opencontacts
Android contact manager that stores contacts in an isolated database, preventing other apps from accessing them. Provides call log and caller ID…
 mobilehackinglab/cve-2026-28576-poc
Educational proof-of-concept demonstrating a SQL injection vulnerability in Android 17's Contacts Provider, allowing a zero-permission app to…
 brnpl/flutter-reverse-engineering-labs
Hands-on challenges for learning how to reverse engineer Flutter applications.
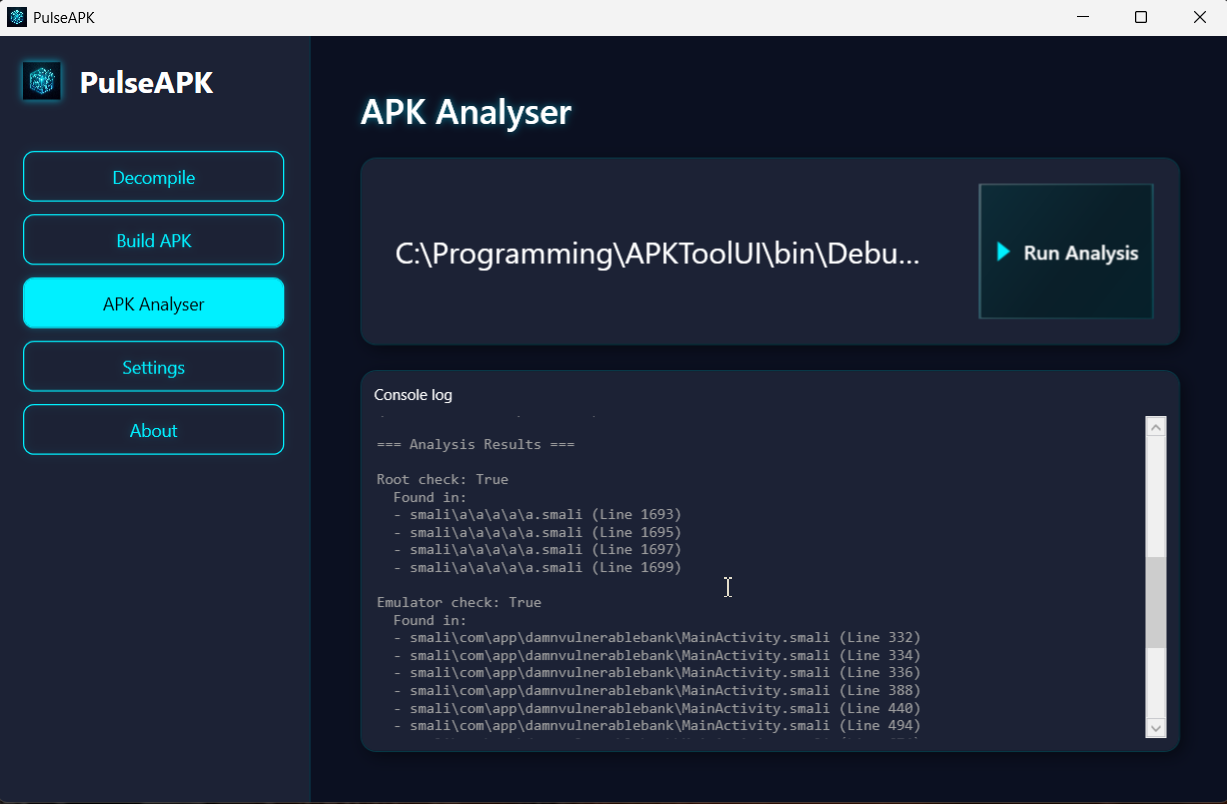 deemoun/pulseapk
PulseAPK is a WPF frontend for apktool and uber-signer with drag-and-drop support, live decompilation output, smali analysis, and integrated APK…
 canyie/transitionplayer
CVE-2026-0091, play with an issue in android window management to perform arbitrary code execution in Launcher process from adb
 theshinigami/mafrida
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
 dangtunguyen/towelroot
Gain root privilege by exploiting CVE-2014-3153 vulnerability