

CVE-2019-6447
 osuni-99/cve-2019-6447
The above investigation of the ES file browser security weakness allows us to see the issue in its entirety
android-securityexploitationinformation-gathering+2
osuni-99/cve-2019-6447The above investigation of the ES file browser security weakness allows us to see the issue in its entirety
 uthrasri/frameworks_base_aosp10_r33_cve-2023-21097
Android AOSP 10 framework base repository containing the fix for CVE-2023-21097, a vulnerability in the Android framework that could lead to local…
 morpheuslord/quadrainspect
Modular Android APK security analysis framework integrating static, dynamic, and reverse engineering tools for comprehensive vulnerability assessment…
 sysnets/atfuzzer
Grammar-guided evolutionary fuzzer for dynamic analysis of AT command interfaces on Android smartphones via Bluetooth and USB, uncovering DoS,…
 maaaaz/androwarn
Yet another static code analyzer for malicious Android applications
 valbrux/cve-2019-11932-supportapp
This native code file aims to be complementary to the published Whatsapp GIF RCE exploit by Awakened , by calculating the system() function address…
 skorpion96/cve-2026-40000
A poc for a vulnerability in ZTE File Manager (zte.com.cn.filer) which allows to read arbitrary files from other apps as the privileges of this file…
 0x1ca3/adbnet
A tool that allows you to search for vulnerable android devices across the world and exploit them.
 perongh/badepoll-selinux-disabler
Use CVE-2026-43074 to disable SELinux on Android (Linux 6.6/6.12)
 accessmodifier364/cve-2026-43499-firetv-sheldonp-writeup
Security research write-up on exploiting CVE-2026-43499 on the Amazon Fire TV Stick 3rd Gen (sheldonp), from temporary root to bootloader unlock.
 dangtunguyen/towelroot
Gain root privilege by exploiting CVE-2014-3153 vulnerability
 seqred-s-a/cve-2019-14326
Privilege escalation in Andy emulator
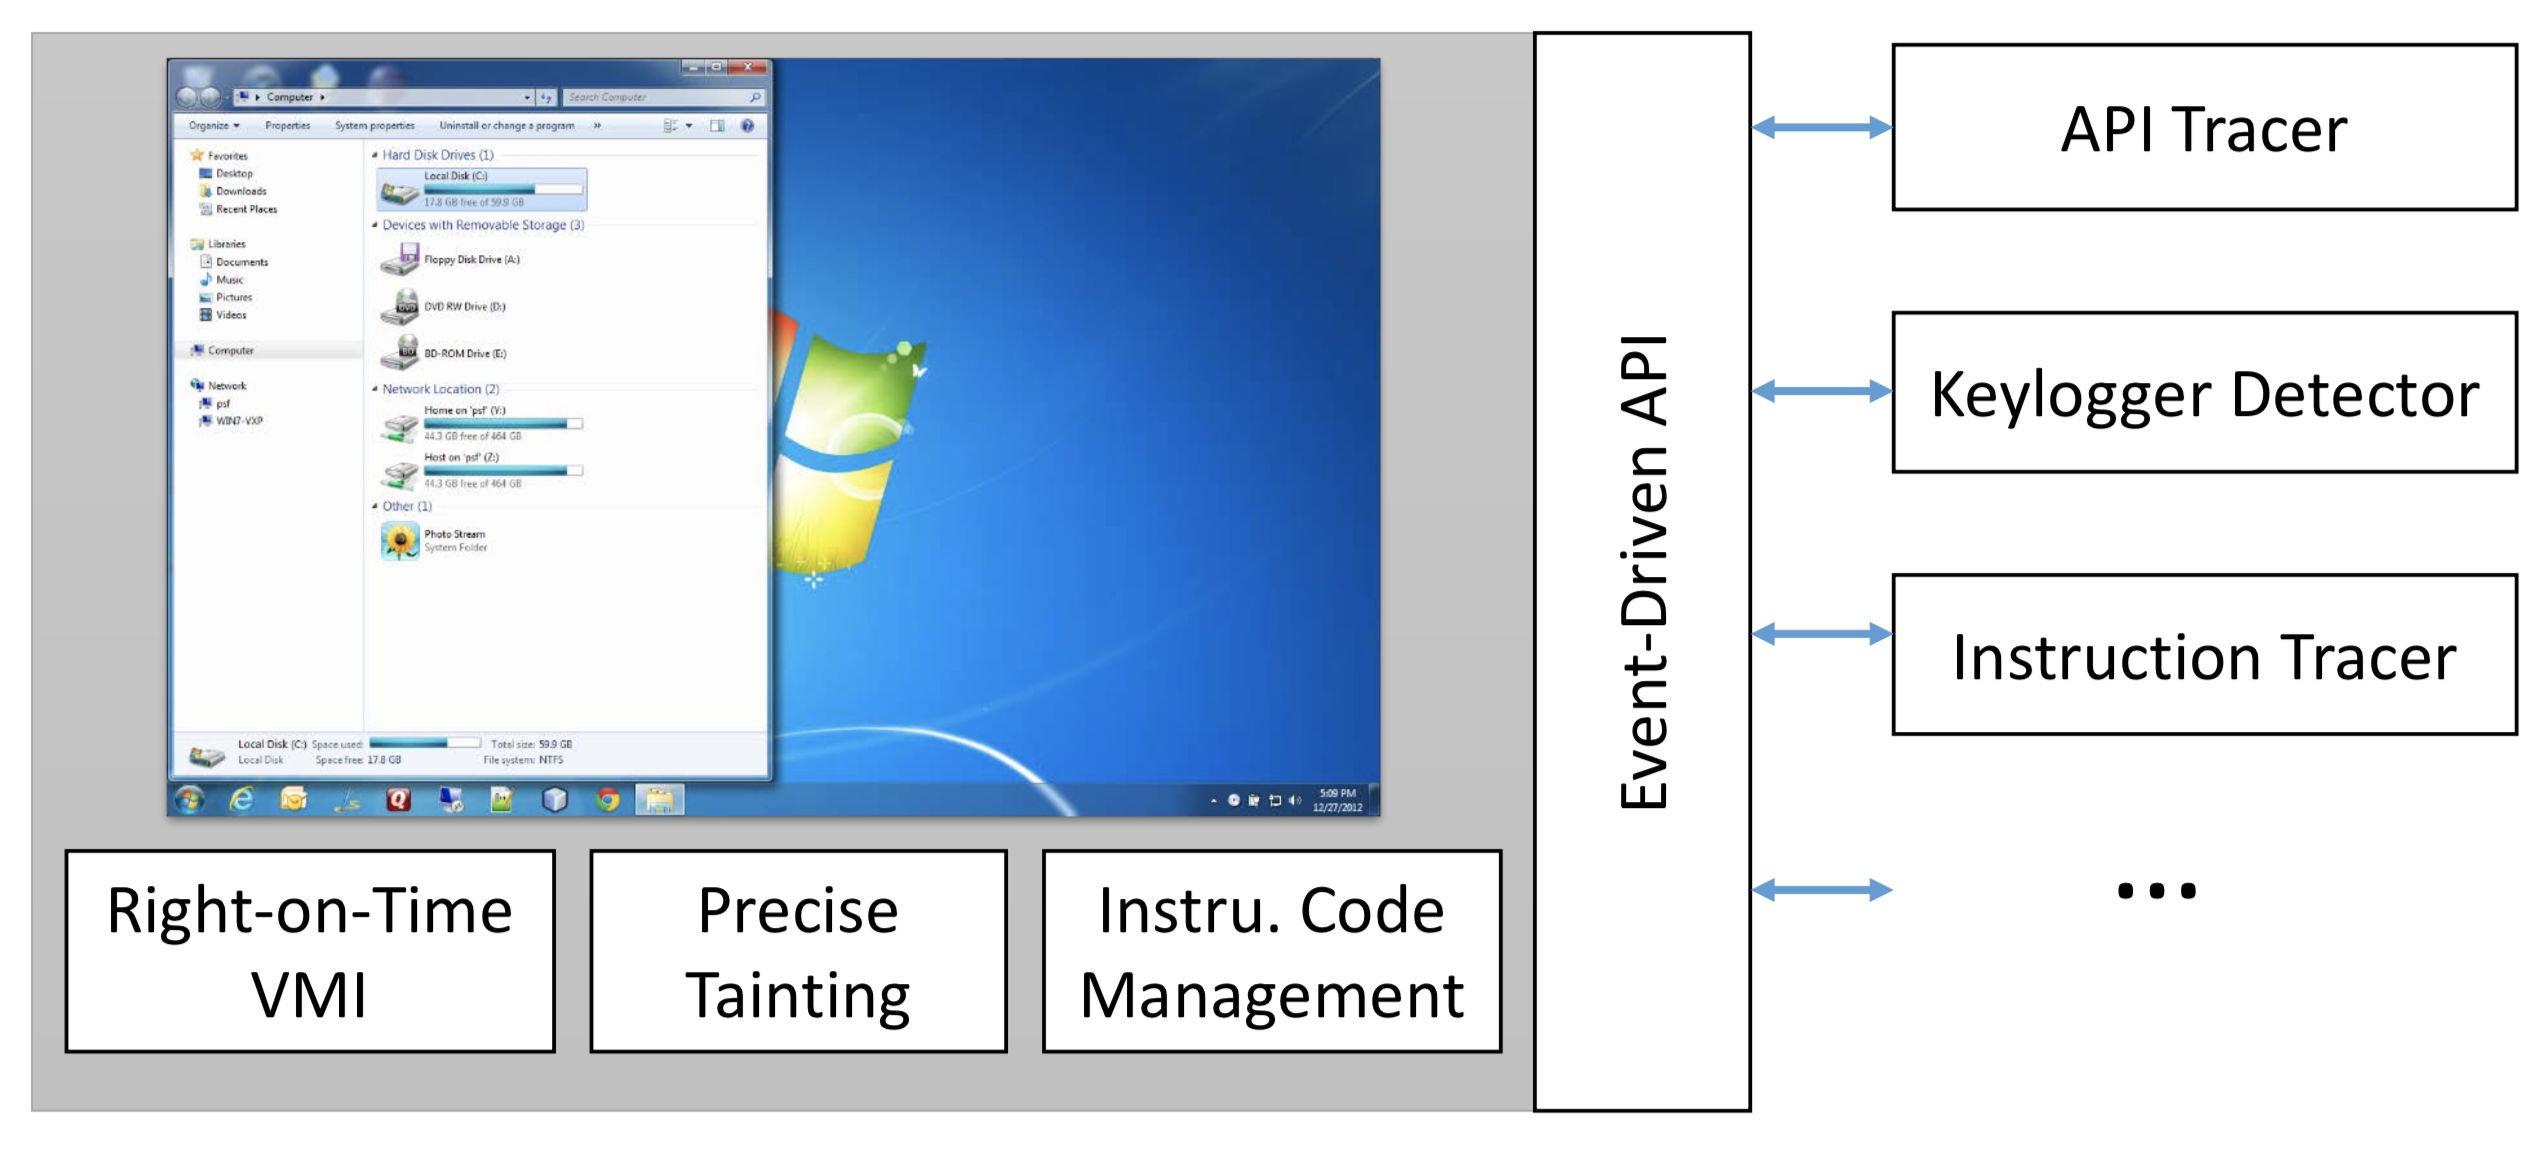 decaf-project/decaf
DECAF (short for Dynamic Executable Code Analysis Framework) is a binary analysis platform based on QEMU. This is also the home of the DroidScope…
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
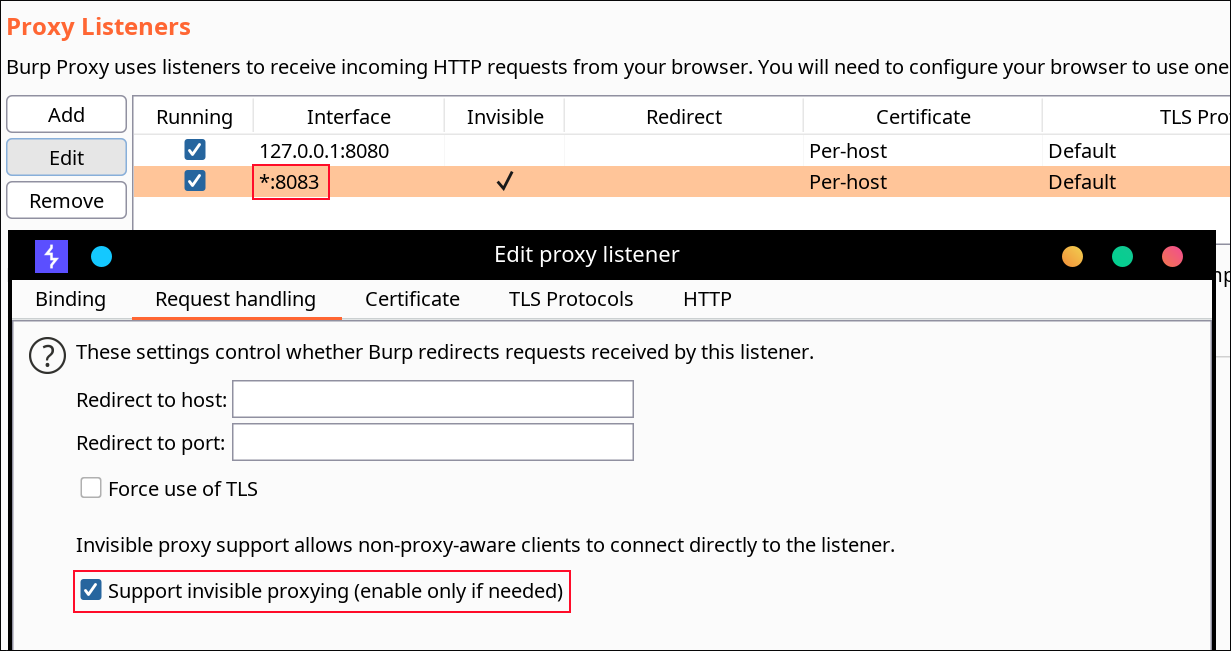 impact-i/reflutter
Patches Flutter engine libraries to enable runtime reverse engineering, traffic interception, and SSL pinning bypass for Android and iOS apps without…
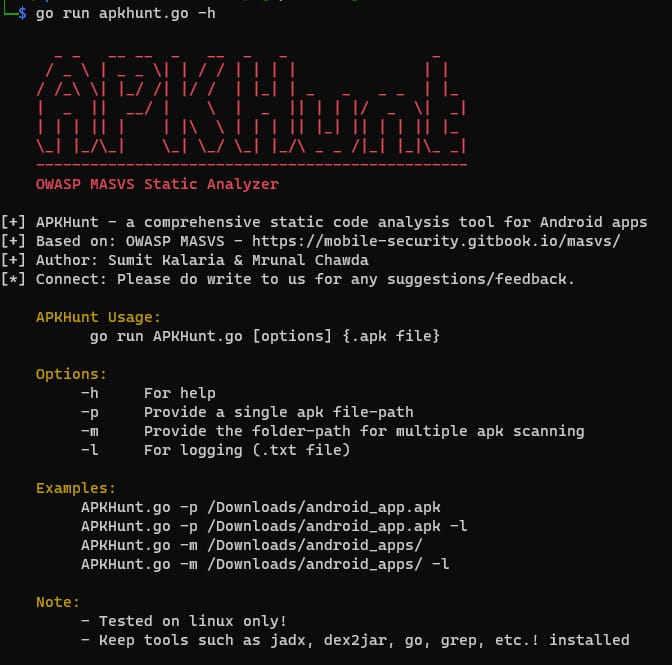 cyber-buddy/apkhunt
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…
 prey/prey-android-client
Android client for Prey: reliable device tracking and security tool
 nccgroup/conscrypttrustusercerts
Magisk module for Android 14 that adds user-installed CA certificates to the system's Conscrypt trust store, enabling HTTPS interception with proxy…