
AndroTickler
 ernw/androtickler
Penetration testing and auditing toolkit for Android apps.
android-securitydynamic-analysis-sandboxinginformation-gathering+4
2541 year ago
ernw/androticklerPenetration testing and auditing toolkit for Android apps.
 ibrahimbalic/androidrat
Android RAT
 hamz-a/frida-android-libbinder
PoC Frida script to view Android libbinder traffic
 nccgroup/lazydroid
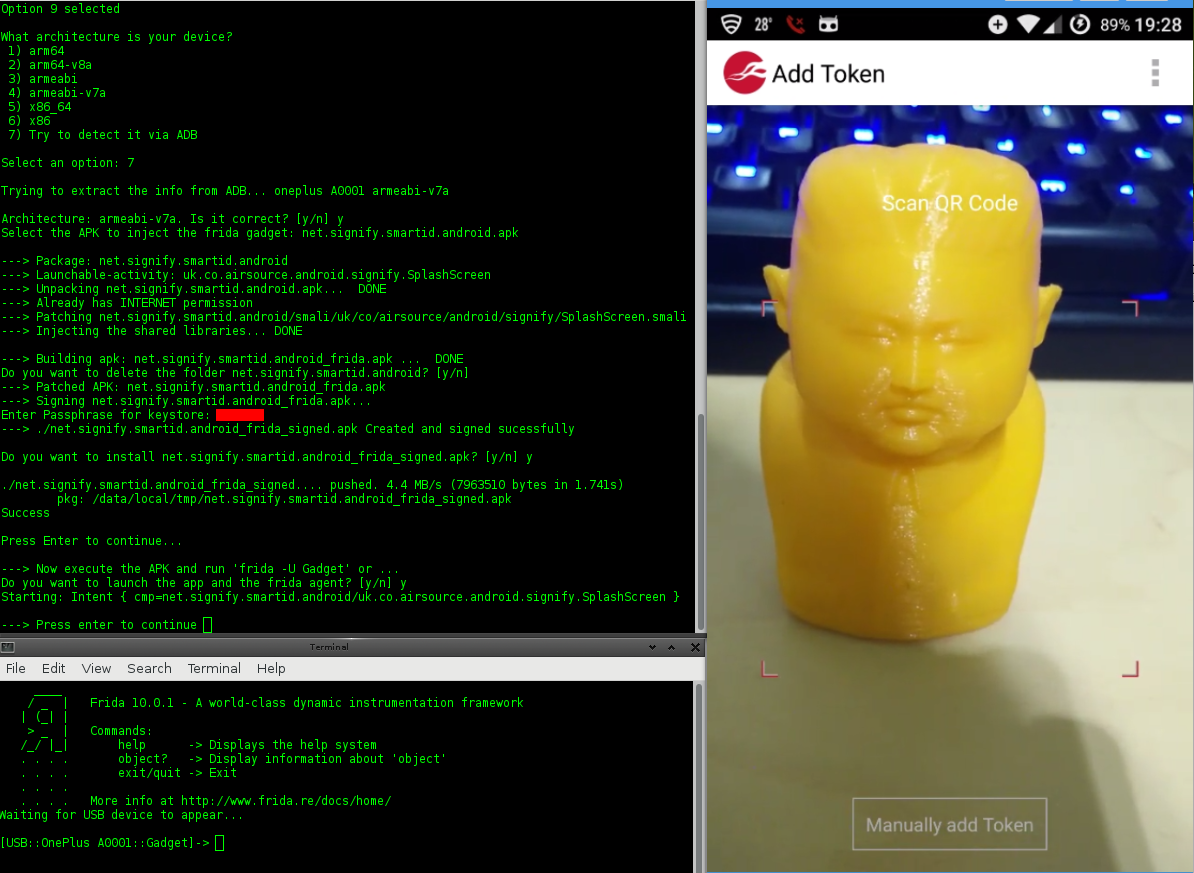
bash script to facilitate some aspects of an Android application assessment
 androguide/dsploit
dSploit - The most complete and advanced IT security professional toolkit on Android.
 viliuskraujutis/androidbroadcastsmonitor
A tool to subscribe to receive all standard Android broadcasts on your Android device.
 packetlss/android-locdump
android location service cache dumper
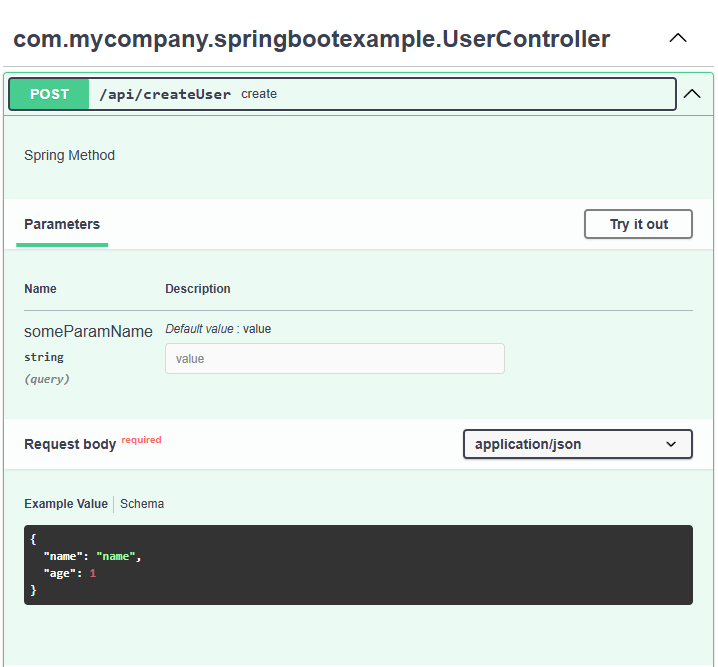 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
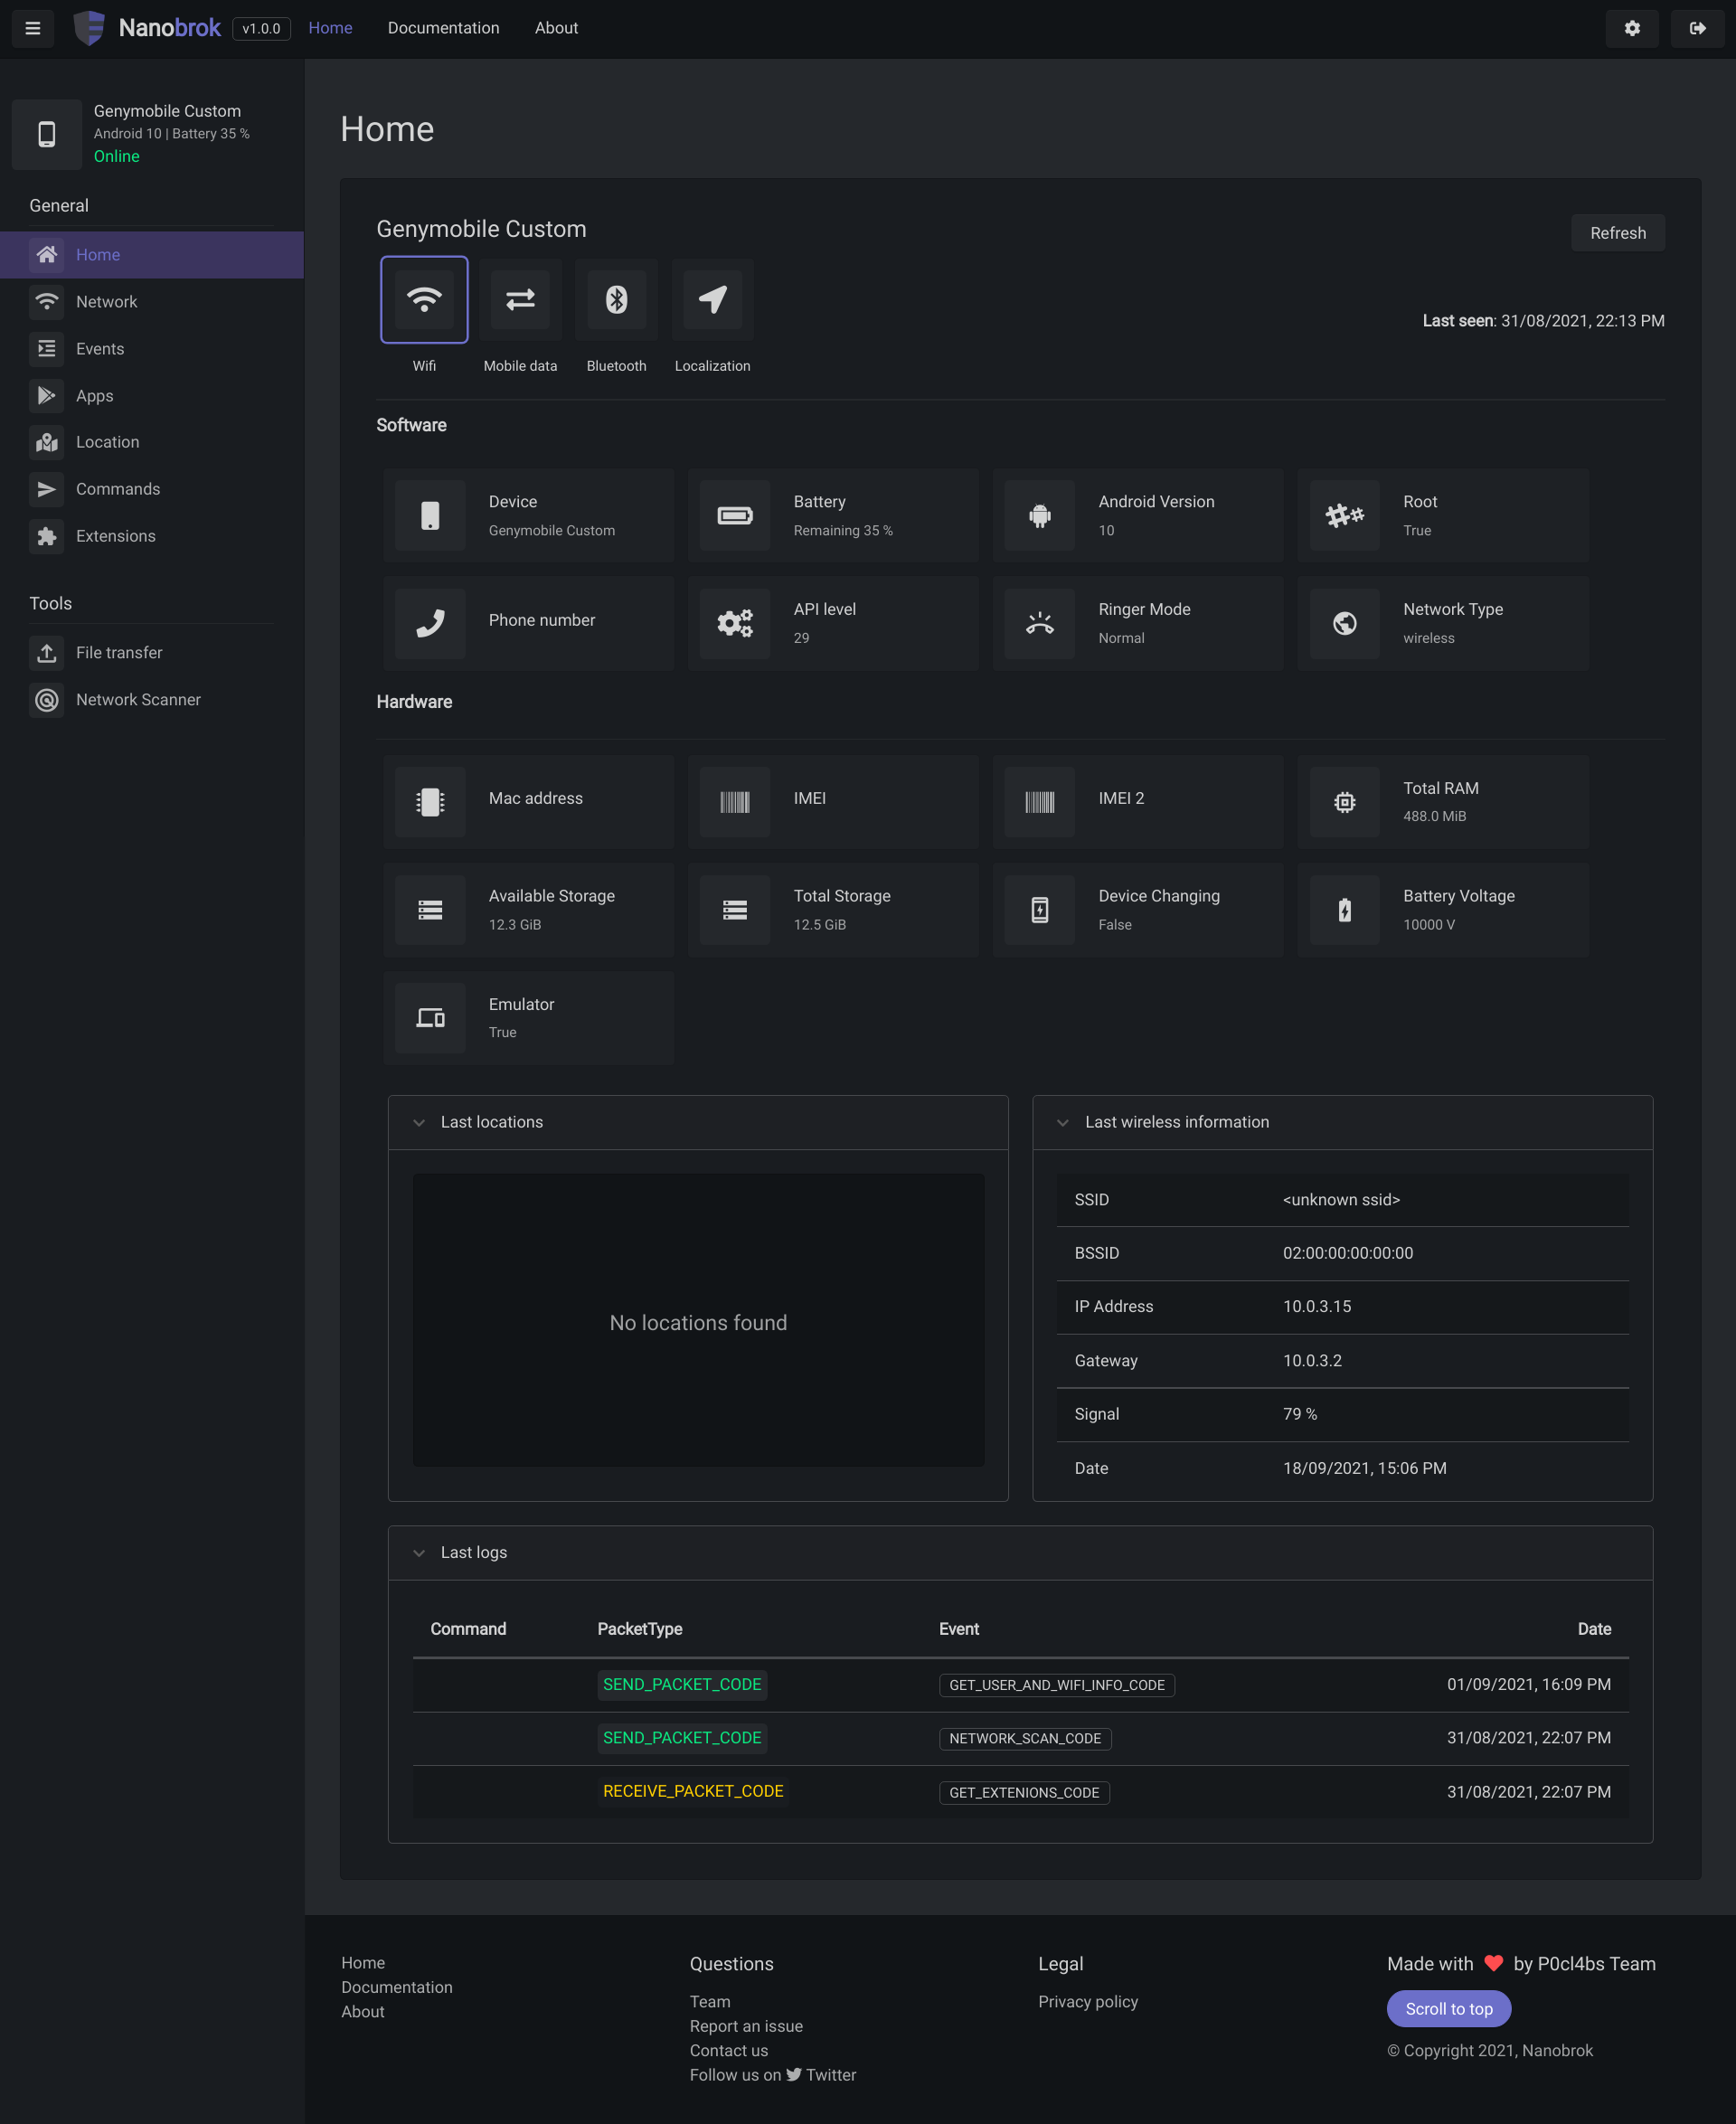 p0cl4bs/nanobrok
Web Service write in Python for control and protect your android device remotely.
 0xdsm/apepe
Extracts app settings, permissions, deeplinks, and SSL pinning bypass suggestions from Android APK files via static analysis of AndroidManifest.xml,…
 maldroid/maldrolyzer
Simple framework to extract "actionable" data from Android malware (C&Cs, phone numbers etc.)
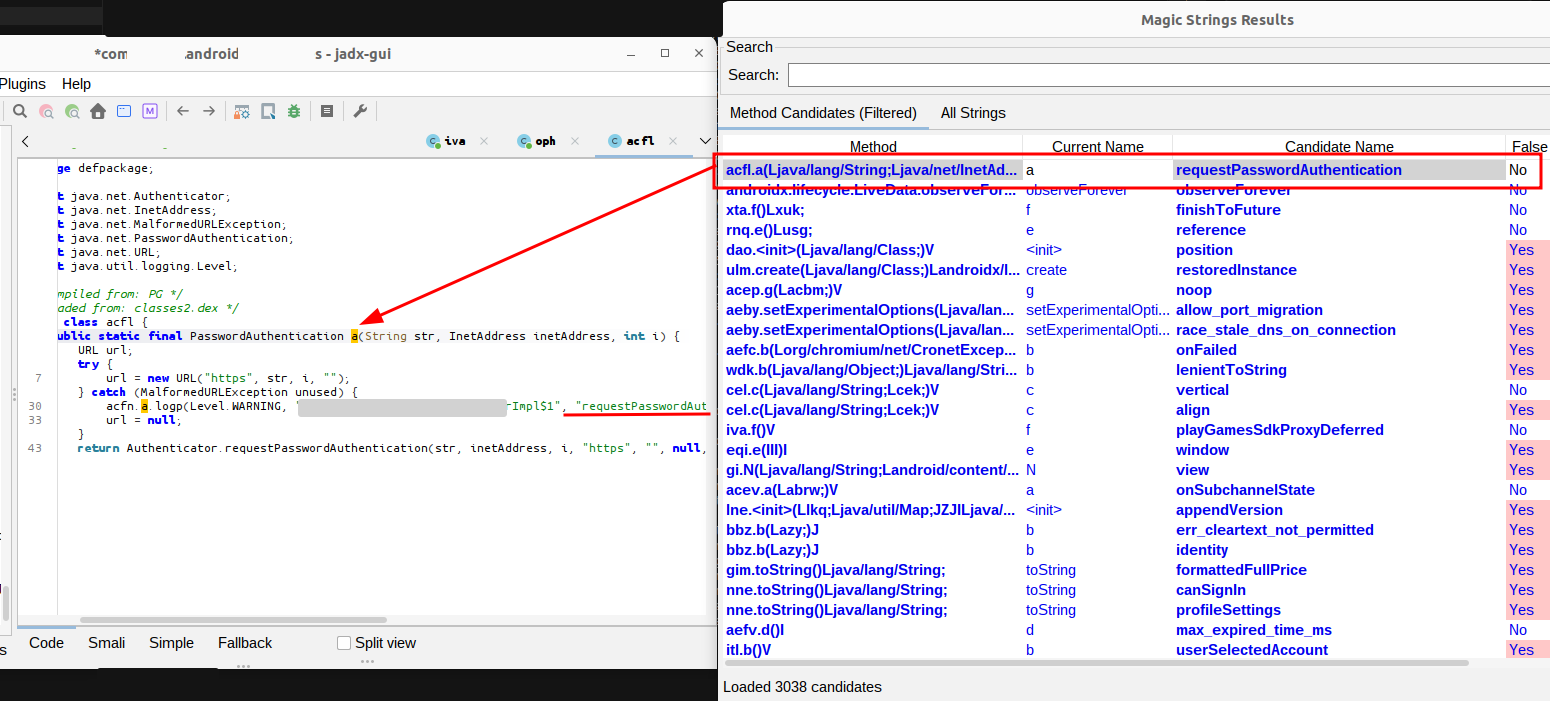 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
 michalbednarski/thisseemswrong
Writeup and exploit for CVE-2024-49746: Android's Parcel::continueWrite closing File Descriptors that are later used
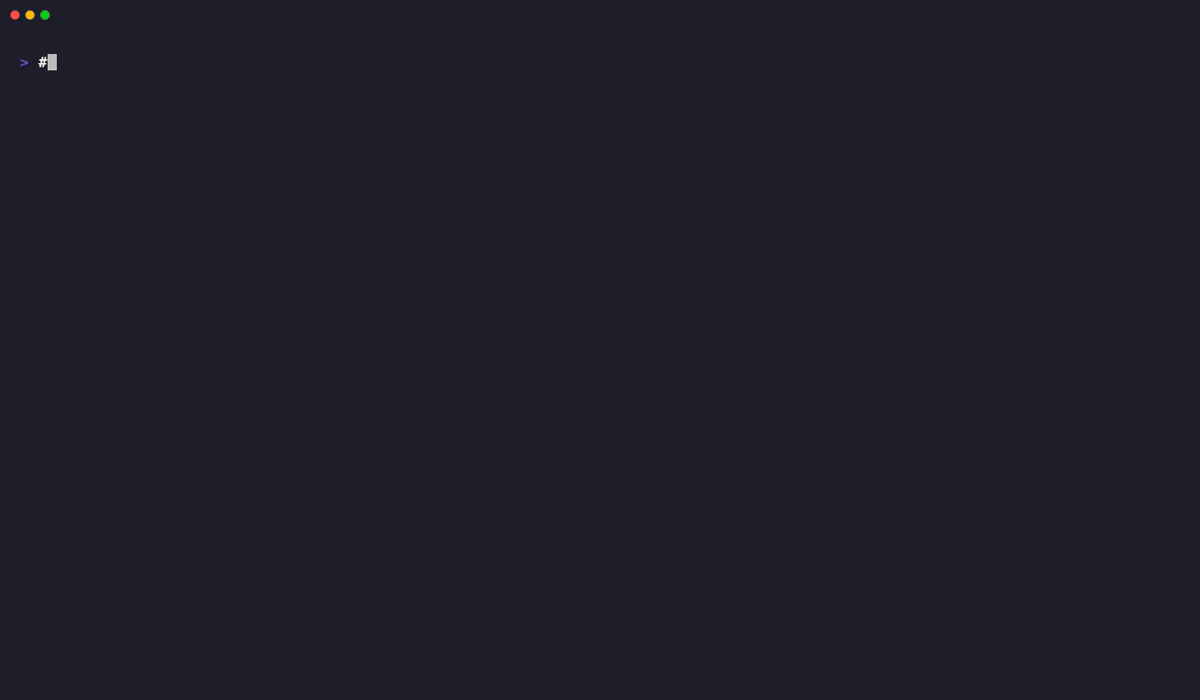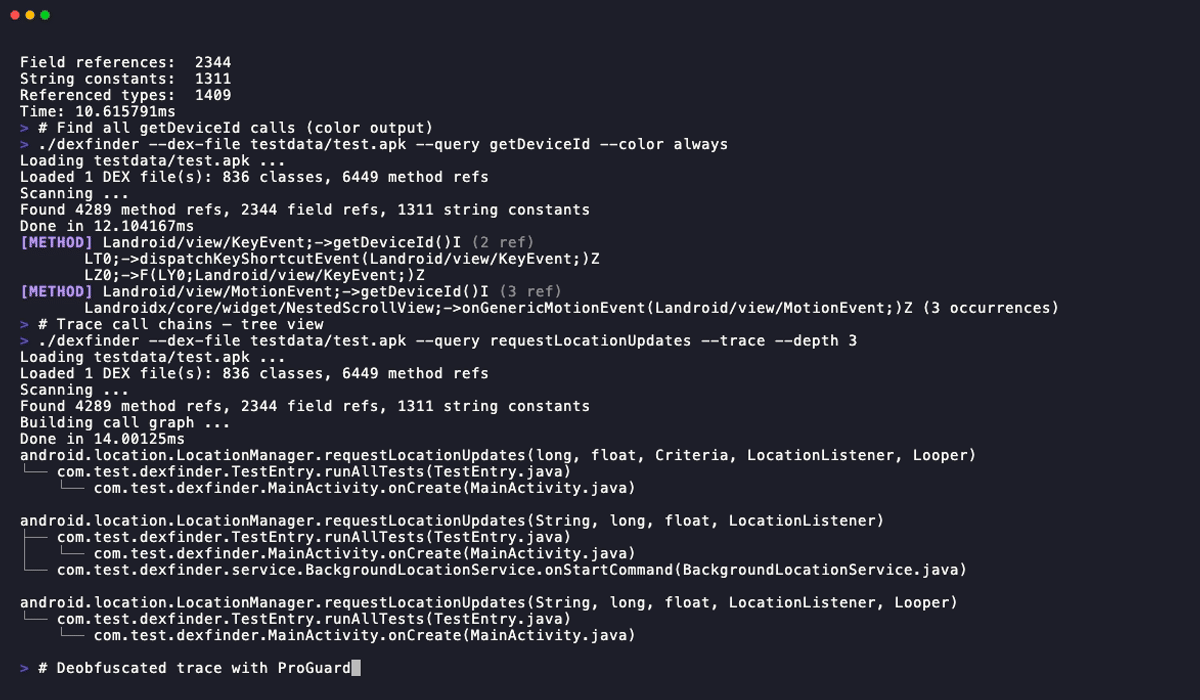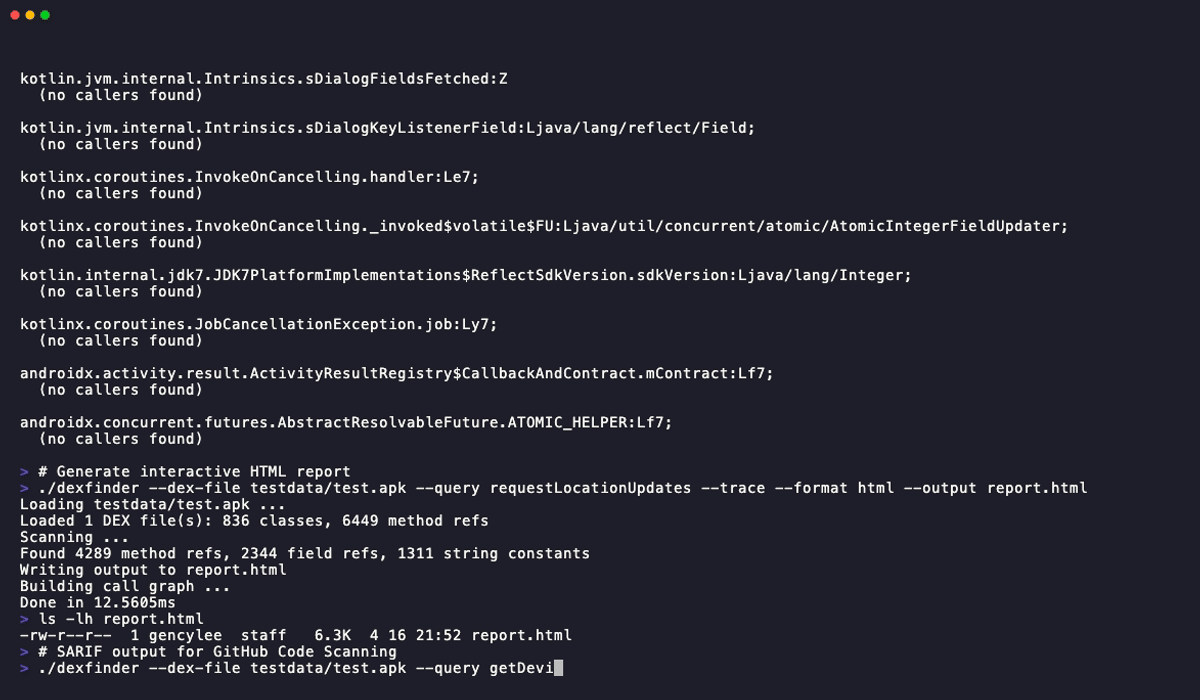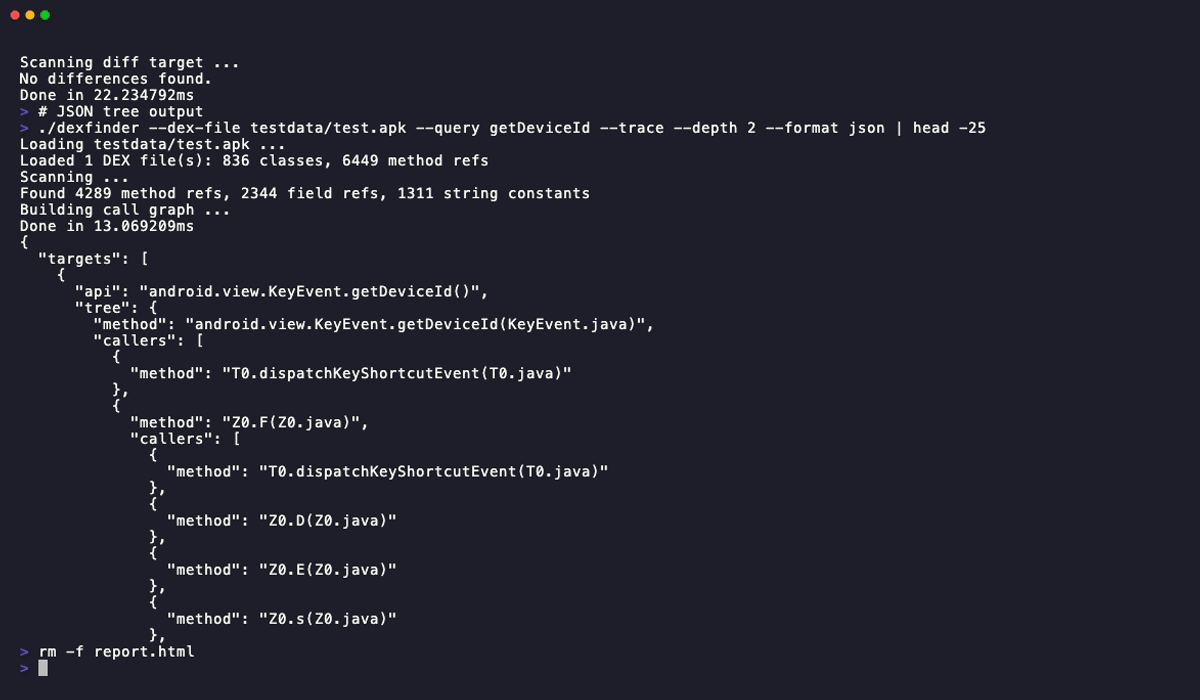 junelegency/dexfinder
Cross-platform APK/DEX method finder with call chain tracing, ProGuard deobfuscation, and hidden API detection
 xtiankisutsa/twiga
A tool that enumerates Android devices for information useful in understanding its internals and for exploit development. It supports android 4.2 to…

 s4vitar/airdroidpwner
Programa ideal para robar toda la información de un dispositivo remotamente a través de la aplicación AirDroid. [CVE-2019-9599]…
 hadesscs/artemis
Extracts and investigates infrastructure (IPs, domains) from APK files, with manifest parsing and WHOIS lookup for mobile application reconnaissance.