
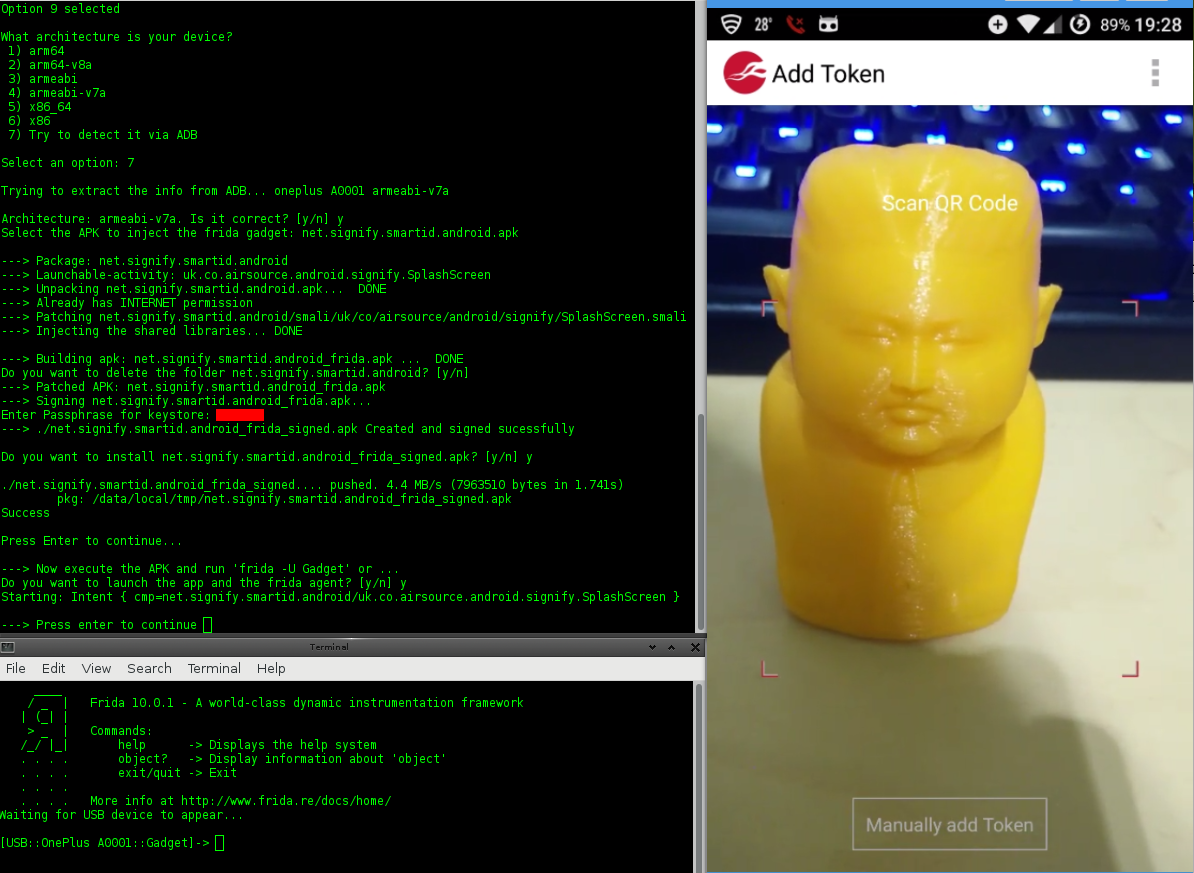
LazyDroid
 nccgroup/lazydroid
bash script to facilitate some aspects of an Android application assessment
android-securitydynamic-analysis-sandboxinginformation-gathering+3
160
nccgroup/lazydroidbash script to facilitate some aspects of an Android application assessment
 cybersecsi/dockerized-android
A container-based framework to enable the integration of mobile components in security training platforms
 owasp/maswe
OWASP enumeration of common security and privacy weaknesses in mobile applications, serving as a reference bridging the MASVS verification standard…
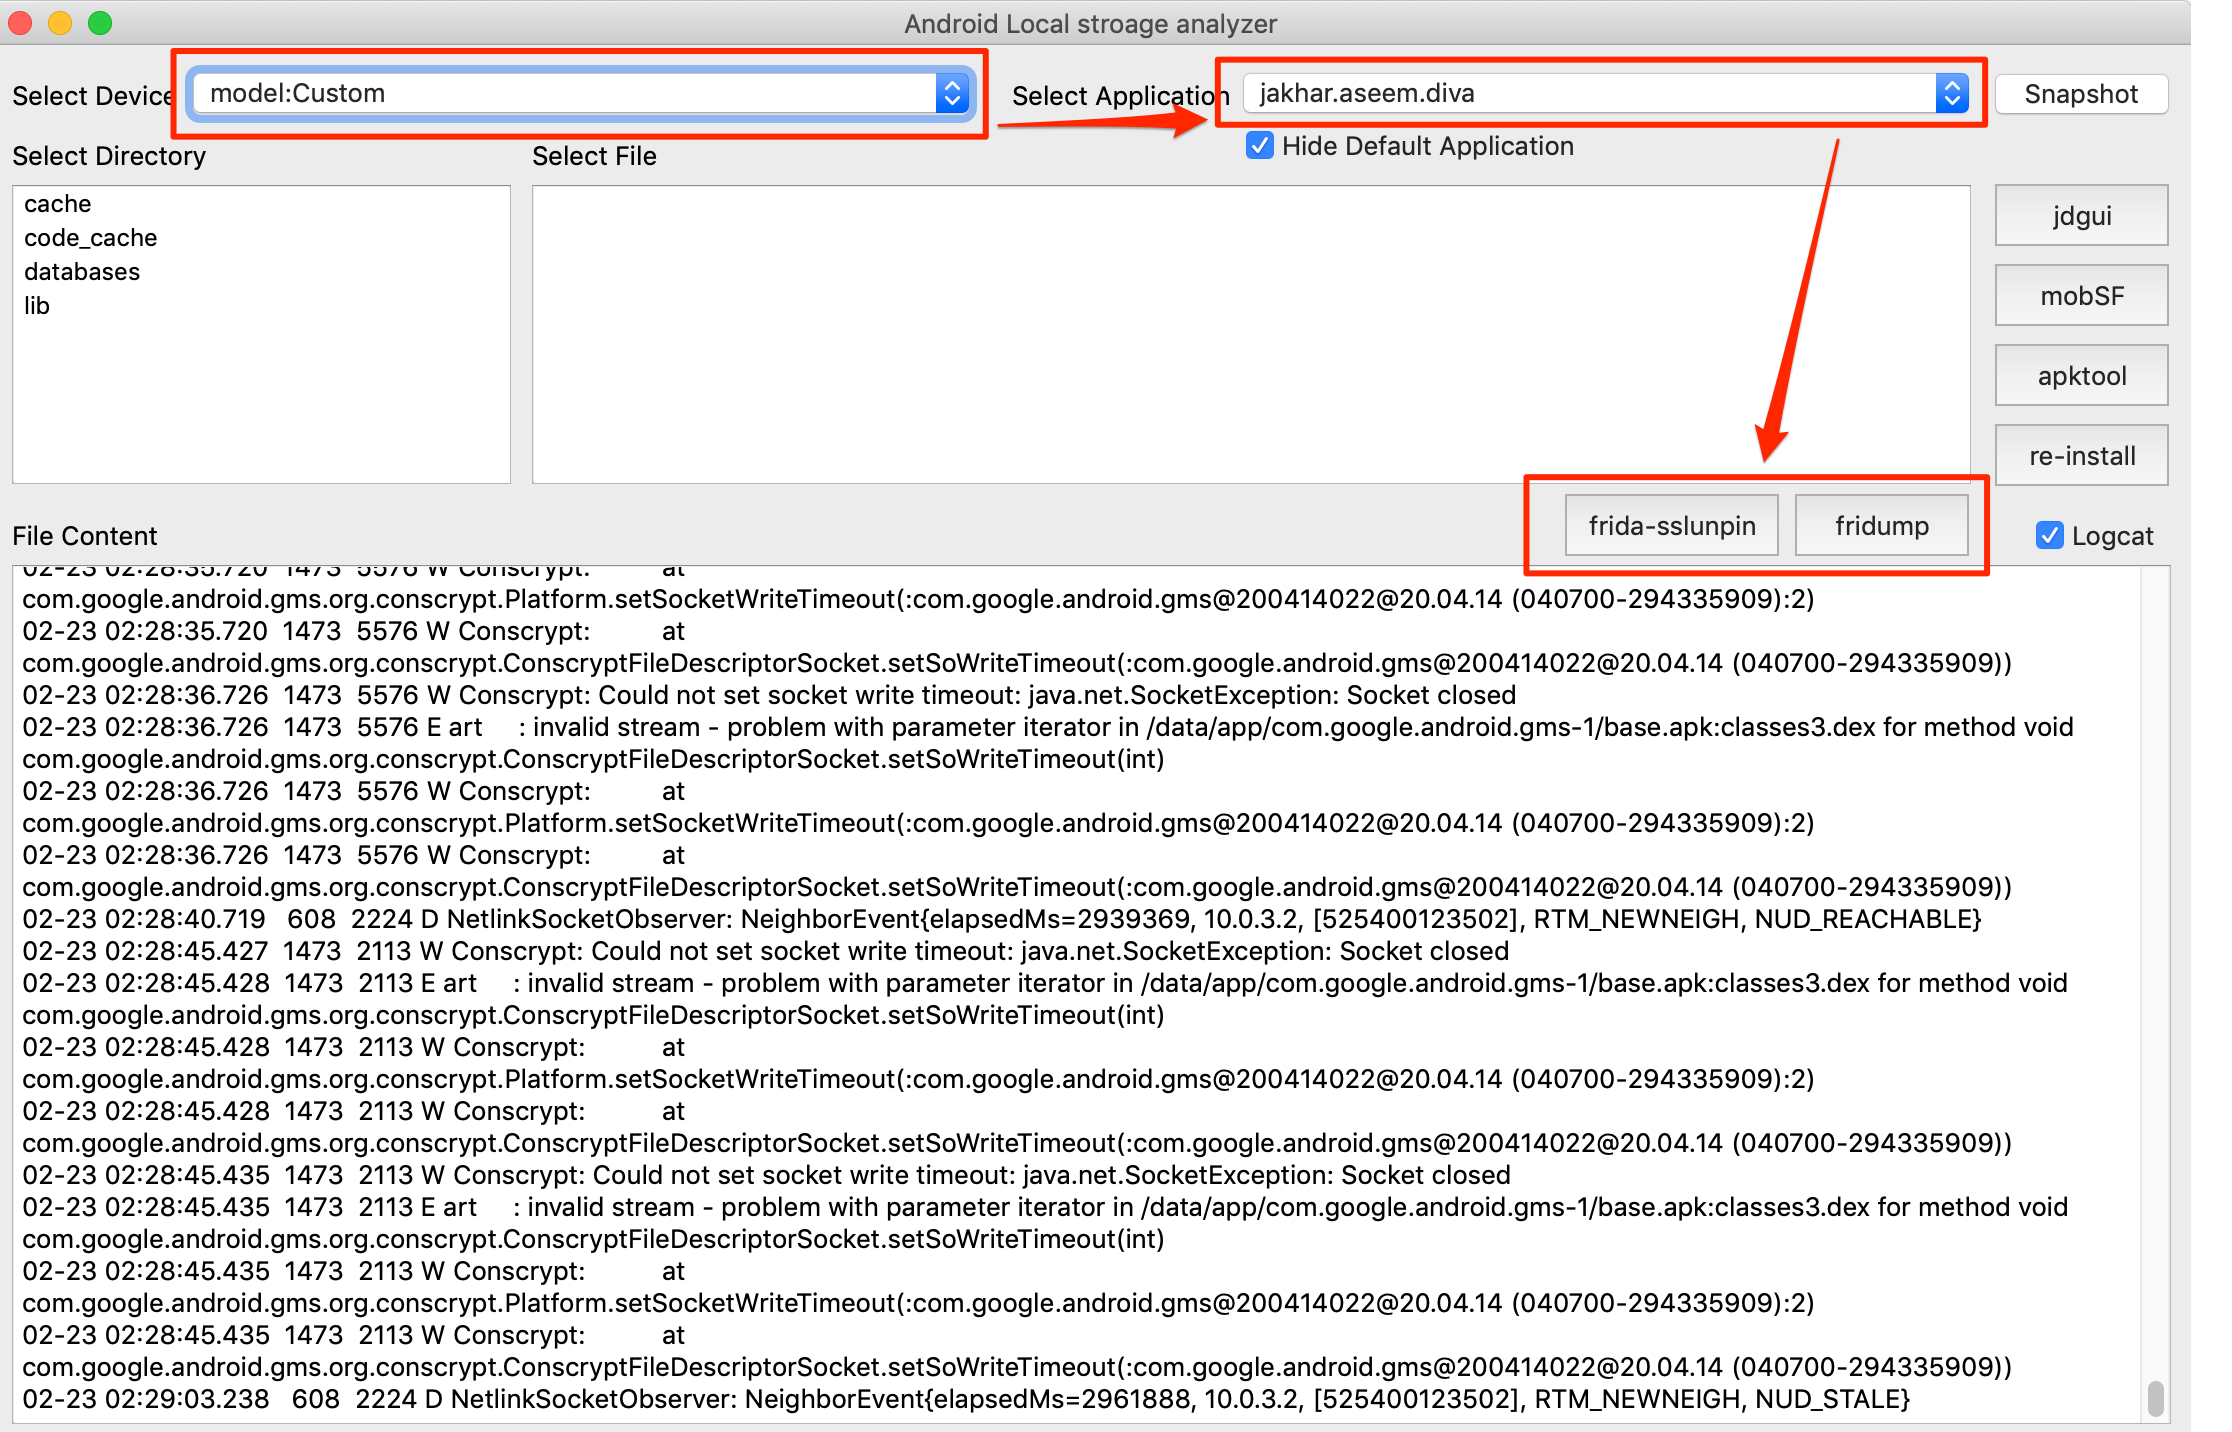 notsosecure/android_application_analyzer
The tool is used to analyze the content of the android application in local storage.
 0xdsm/apepe
Extracts app settings, permissions, deeplinks, and SSL pinning bypass suggestions from Android APK files via static analysis of AndroidManifest.xml,…
 retme7/cve-2014-4322_poc
Gain privileges:system -> root,as a part of https://github.com/retme7/CVE-2014-7911_poc
 viralsecuritygroup/knoxout
A PoC of KNOXout (CVE-2016-6584) - bypassing Samsung KNOX protections and root Samsung Galaxy S6 Android Device.
 michalbednarski/resourcepoison
Writeup and exploit for CVE-2025-22441: Privilege escalation from installed app to SystemUI process on Android due to pass of untrusted…
 amnestytech/inside-pegasus
A curated set of NSO Group internal documents, product materials and sworn testimony that entered the public record in WhatsApp Inc. and Meta…
 leommxj/cve-2020-0022
Proof-of-concept exploit for CVE-2020-0022, targeting Android Bluetooth stack to trigger a buffer overflow via crafted L2CAP packets, causing denial…
 thomasking2014/slides
Curated collection of security conference slide decks covering Android rooting, kernel exploitation, browser memory corruption, JIT mitigations, and…
 reverseclabs/cve-2021-25374_samsung-account-access
This script can be used to gain access to a victim's Samsung Account if they have a specific version of Samsung Members installed on their Samsung…
 donctl/sandy
Release of the sandy framework.
 gmh5225/androiddrivesignity
AndroidDriveSignity is a Python utility designed to bypass driver signature verification in Android kernel(ARMv8.3), facilitating the loading of…
 geekben/towelroot
Research of CVE-2014-3153 and its famous exploit towelroot on x86
 xianwan1314/cve-2026-43499-poc-analysis
Vulnerability analysis and Proof of Concept (PoC) for CVE-2026-43499 affecting Xiaomi devices. For educational and research purposes only.
 valbrux/cve-2019-11932-supportapp
This native code file aims to be complementary to the published Whatsapp GIF RCE exploit by Awakened , by calculating the system() function address…
 spiralbl0ck/remote-buffer-overflow-over-wifi_stack-in-wpa_supplicant-binary-in-android-11-platform-samsung-a20e
Remote buffer overflow over wifi_stack in wpa_supplicant binary in android 11, platform:samsung a20e, stock options so like works out of the box