
android_autorooter
 scs-labrat/android_autorooter
Exfiltrate sensitive user data from apps on Android 12 and 13 using CVE-2024-0044 vulnerability remotely
android-securitydata-exfiltrationexploitation+5
77
scs-labrat/android_autorooterExfiltrate sensitive user data from apps on Android 12 and 13 using CVE-2024-0044 vulnerability remotely
 secmob/cve-2015-6612
Proof-of-concept exploit for Android CVE-2015-6612, demonstrating a privilege escalation vulnerability with a working PoC for security research and…
 dana-at-cp/backdoor-apk
backdoor-apk is a shell script that simplifies the process of adding a backdoor to any Android APK file. Users of this shell script should have…
 0n1con3/fluxer
FluxER - The bash script which installs and runs the Fluxion tool inside Termux. The wireless security auditing tool used to perform WPA/WPA2…
 humoud/apksneeze
A tool that automates the mundane tasks of pentesting Android apps. It uses APKTool and Dex2Jar.
 darkz2012/qualcomm-vulnerability-scanner
A tool to scan Android devices for the recently exploited Qualcomm flaw CVE-2026-21385, providing a simple and efficient way to identify vulnerable…
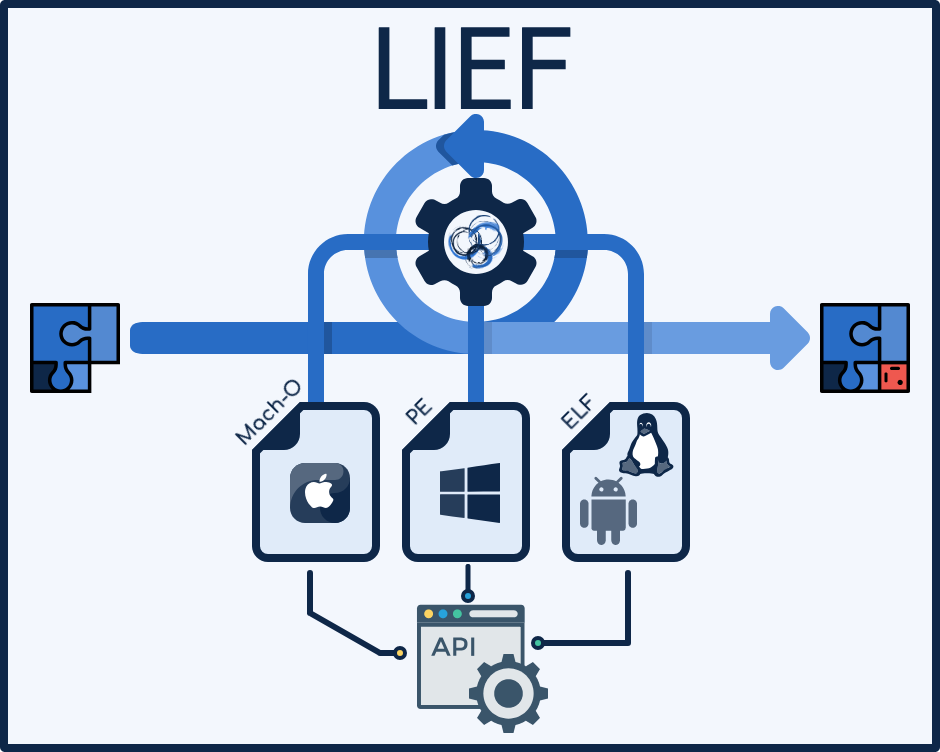 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 sslab-gatech/avpass
Tool for leaking and bypassing Android malware detection system
 cloudfuzz/android-kernel-exploitation
Hands-on workshop for learning Android kernel vulnerability analysis and exploitation, with Docker-based build environment and practical exercises.
 snip3r69/cve-2013-4710-webview-rce-vulnerability
Android 3.0 through 4.1.x on Disney Mobile, eAccess, KDDI, NTT DOCOMO, SoftBank, and other devices does not properly implement the WebView class,…
 gmh5225/awesome-game-security
Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…
 gmh5225/androiddrivesignity
AndroidDriveSignity is a Python utility designed to bypass driver signature verification in Android kernel(ARMv8.3), facilitating the loading of…
 ikoz/certpinningvulnerableokhttp
OkHttp sample app vulnerable to CVE-2016-2402
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 jaf0rk/cve-2026-14382
Proof-of-concept exploit for CVE-2026-14382, a high-severity ANGLE vulnerability in Chromium, with 32-bit and AArch64 PoCs achieving program counter…
 shaikusaf/system_bt_aosp10_r33_cve-2022-20224
AOSP Bluetooth stack repository modified to address CVE-2022-20224, providing a patched version of the Fluoride Bluetooth stack for Android 10.
 hasan-khalil/cve-2020-6514
Exploit for CVE-2020-6514 targeting WebRTC SCTP memory corruption in Android applications. Uses Frida to hook native functions and alter SCTP packets…
 haxatron/cve-2022-0219
Proof-of-concept exploit for CVE-2022-0219, an XXE vulnerability in Jadx that allows local file disclosure when exporting malicious APK files via the…