
Android-Disassembler
 yhs0602/android-disassembler
Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…
android-securitybinary-analysisdebuggers+4
717
yhs0602/android-disassemblerDisassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…
 villager1314/cve-2026-64560-analysis
Linux kernel UAF analysis for CVE-2026-64560 with race-triggering PoC, patch review, affected LTS/Android version matrix, and self-check for patched…
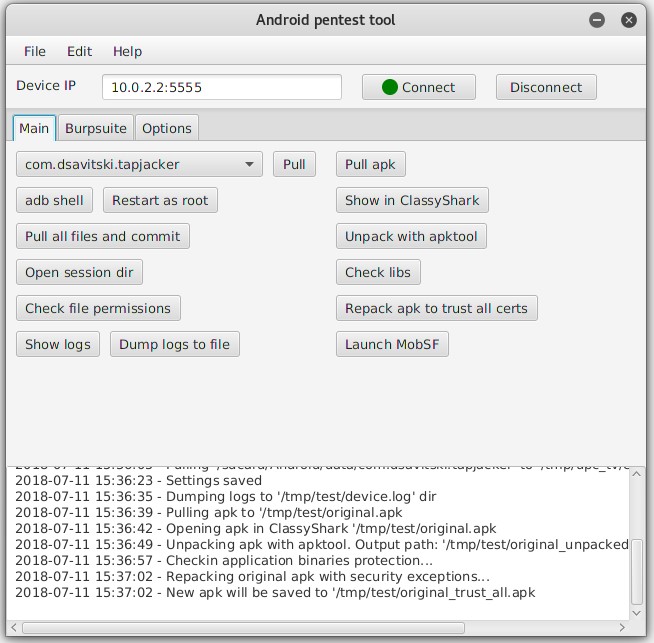 dzmitry-savitski/android-pentest-tool
Android penetration testing tool for Kali linux
 federicodotta/ghidra2frida
Ghidra extension bridging static and dynamic analysis via Frida, enabling scriptable runtime instrumentation for reverse engineering binaries on…
 lyravoid/kernelpatch
Patches and hooks the Linux kernel using only a stripped kernel image, extracting symbols and injecting code for inline and syscall hooking on arm64.
 yijiacloud/ghostlock-oppo-pckm00
CVE-2026-43499 GhostLock futex UAF LPE PoC for OPPO PCKM00 (SM6150) / Linux 4.14.180
 isec-tugraz/file-notification-attacks
Research artifacts for file-notification side-channel attacks on Linux, Windows, and macOS, demonstrating inotify/FSEvents leakage, keystroke timing,…
 oopnv70-lab/ghostlock-aak-apk
GhostLock AAK Launcher - CVE-2026-43499 Linux kernel rtmutex stack UAF local privilege escalation trigger (GPLv3)
 wangs-official/opace6-cve-2026-64560
Temporary root tool for OnePlus Ace 6 that exploits the CVE-2026-64560 Linux kernel POSIX CPU timer use-after-free to gain root until reboot, without…
 dnlid/cve-2026-43499
CVE-2026-43499: Linux kernel futex PI use-after-free research package
 redzrush101/zte-blade-v40-vita-unlock
Unlocking the ZTE Blade V40 Vita (P606F02 / Unisoc UMS9230 / UFS) bootloader via CVE-2022-38694 - Linux scripts, the FBE post-unlock hang fix, and…
 trinadh465/system_bt_aosp10_r33_cve-2021-0589
Patched Android Bluetooth stack (AOSP10) addressing CVE-2021-0589, with build instructions for AOSP and Linux.
 wzhdgithub/ghostlock
CVE-2026-43499 futex PI stack UAF ???????? - Android GKI 6.1~6.12 ??????? pselect() + futex PI ????????????,??? root ??? SELinux??? OPPO Find…
 brucetg/dirtycow-exp
编译好的脏牛漏洞(CVE-2016-5195)EXP
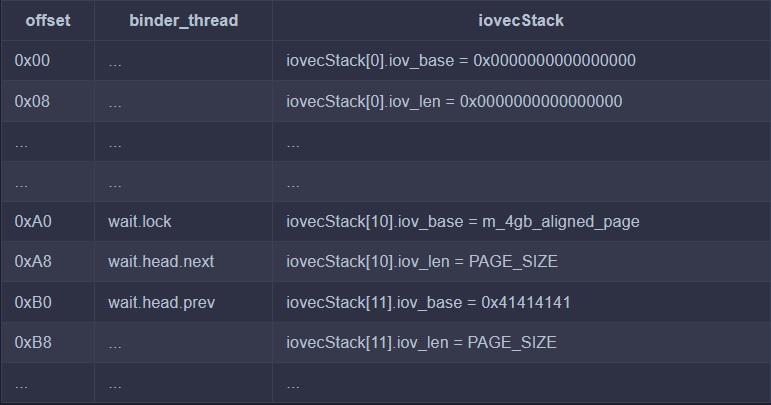 sharif-dev/androidkernelvulnerability
Triggering and Analyzing Android Kernel Vulnerability CVE-2019-2215
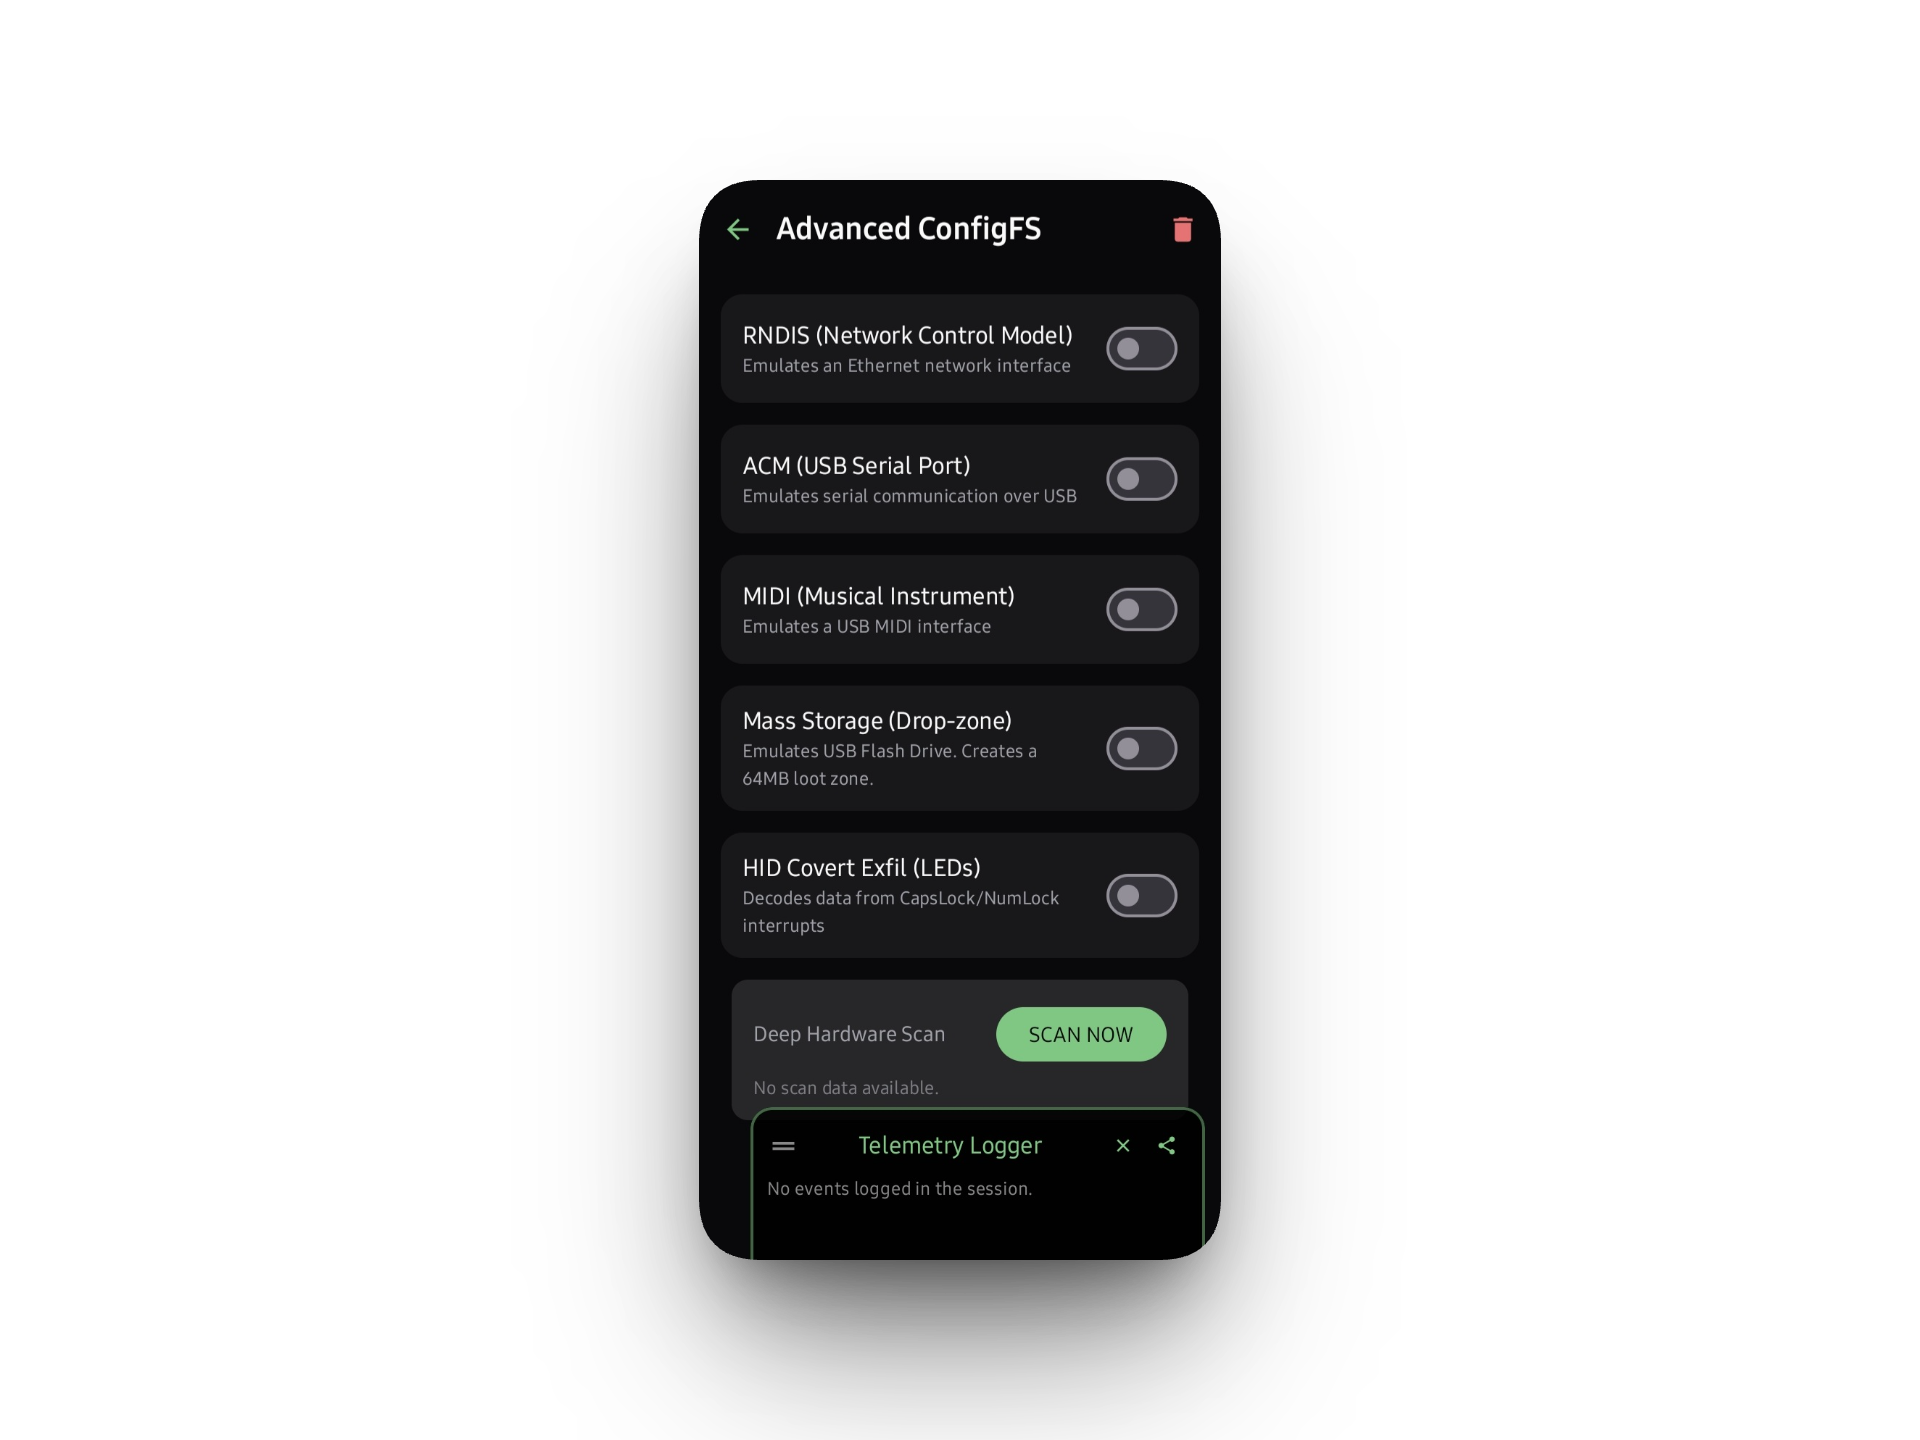 cipher-attack/chimera
Payload injector and HID emulator for Android like Hak5 and rubber ducky
 dangtunguyen/towelroot
Gain root privilege by exploiting CVE-2014-3153 vulnerability