
CVE-2025-48593
 logesh-git001/cve-2025-48593
"A single malicious packet can own your device." — Android Security Team, Nov 2025
android-securitybluetooth-securityeducation+7
7
logesh-git001/cve-2025-48593"A single malicious packet can own your device." — Android Security Team, Nov 2025
 roeeh/conscryptchecker
This app verifies if your device is still vulnerable to CVE-2015-3825 / CVE-2015-3837, aka "One Class to Rule Them All", by checking if it contains…
 pwnaccelerator/stagefright-cve-2015-3864
PoC - Binary patches for CVE-2015-3864 (NOT for production, use at your own risk)
 sunnyjiang/shellshocker-android
This is an Android Application that helps you detect if your machine that run bash is vulnerable by CVE-2014-6271
 tinopreter/docviewerexploitapp
This is an Exploit App I made when solving the DocumentViewer challenge (CVE-2021-40724) from MobileHackingLab. It will download a libdocviewe_pro.so…
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 androguard/androguard
Reverse engineering and pentesting for Android applications
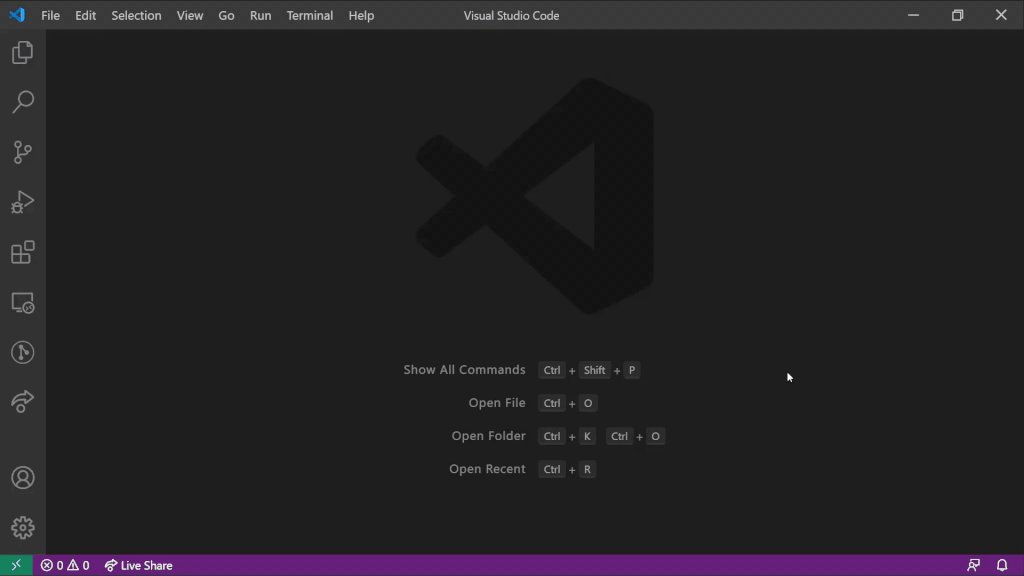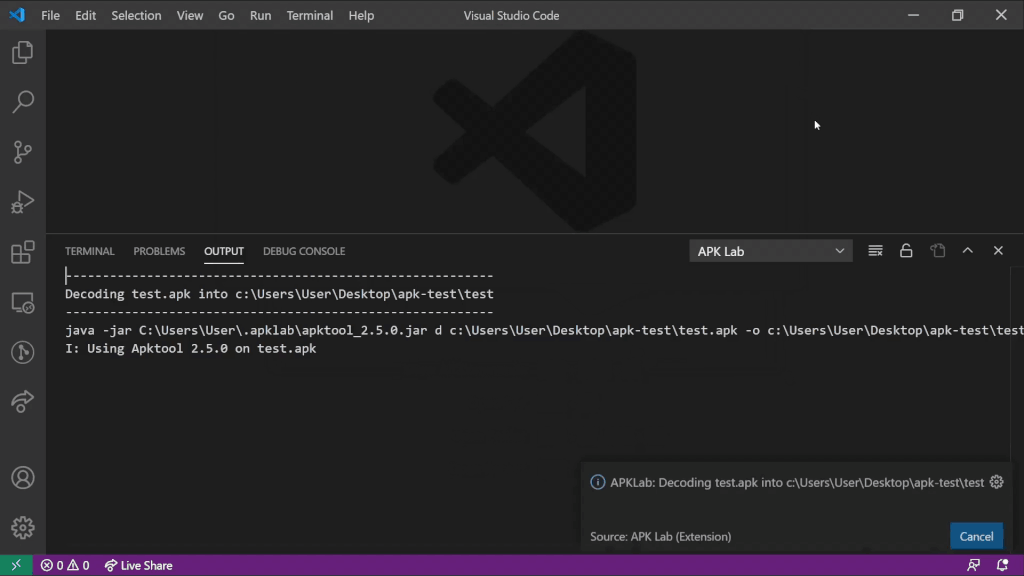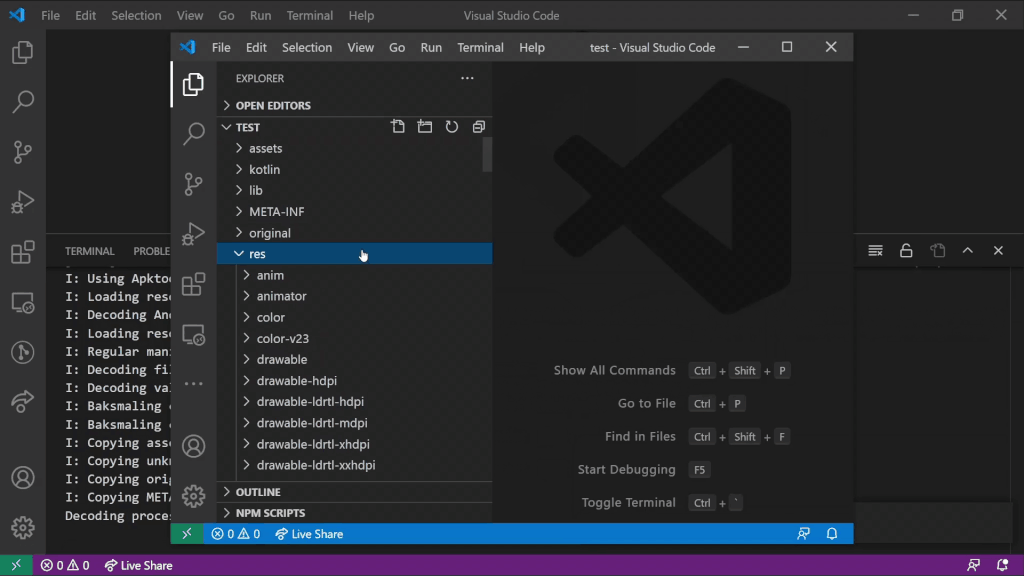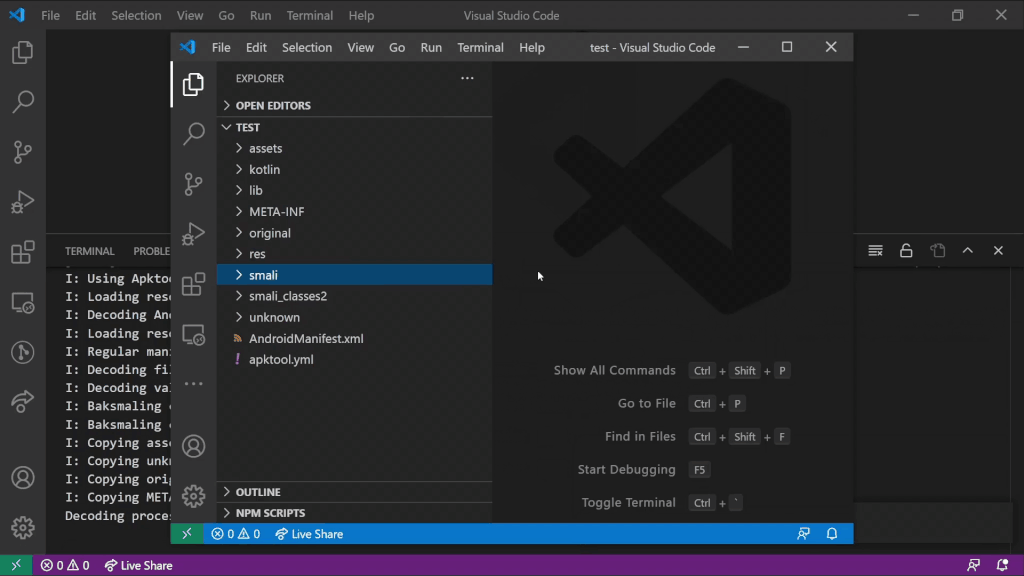 apklab/apklab
Android Reverse-Engineering Workbench for VS Code
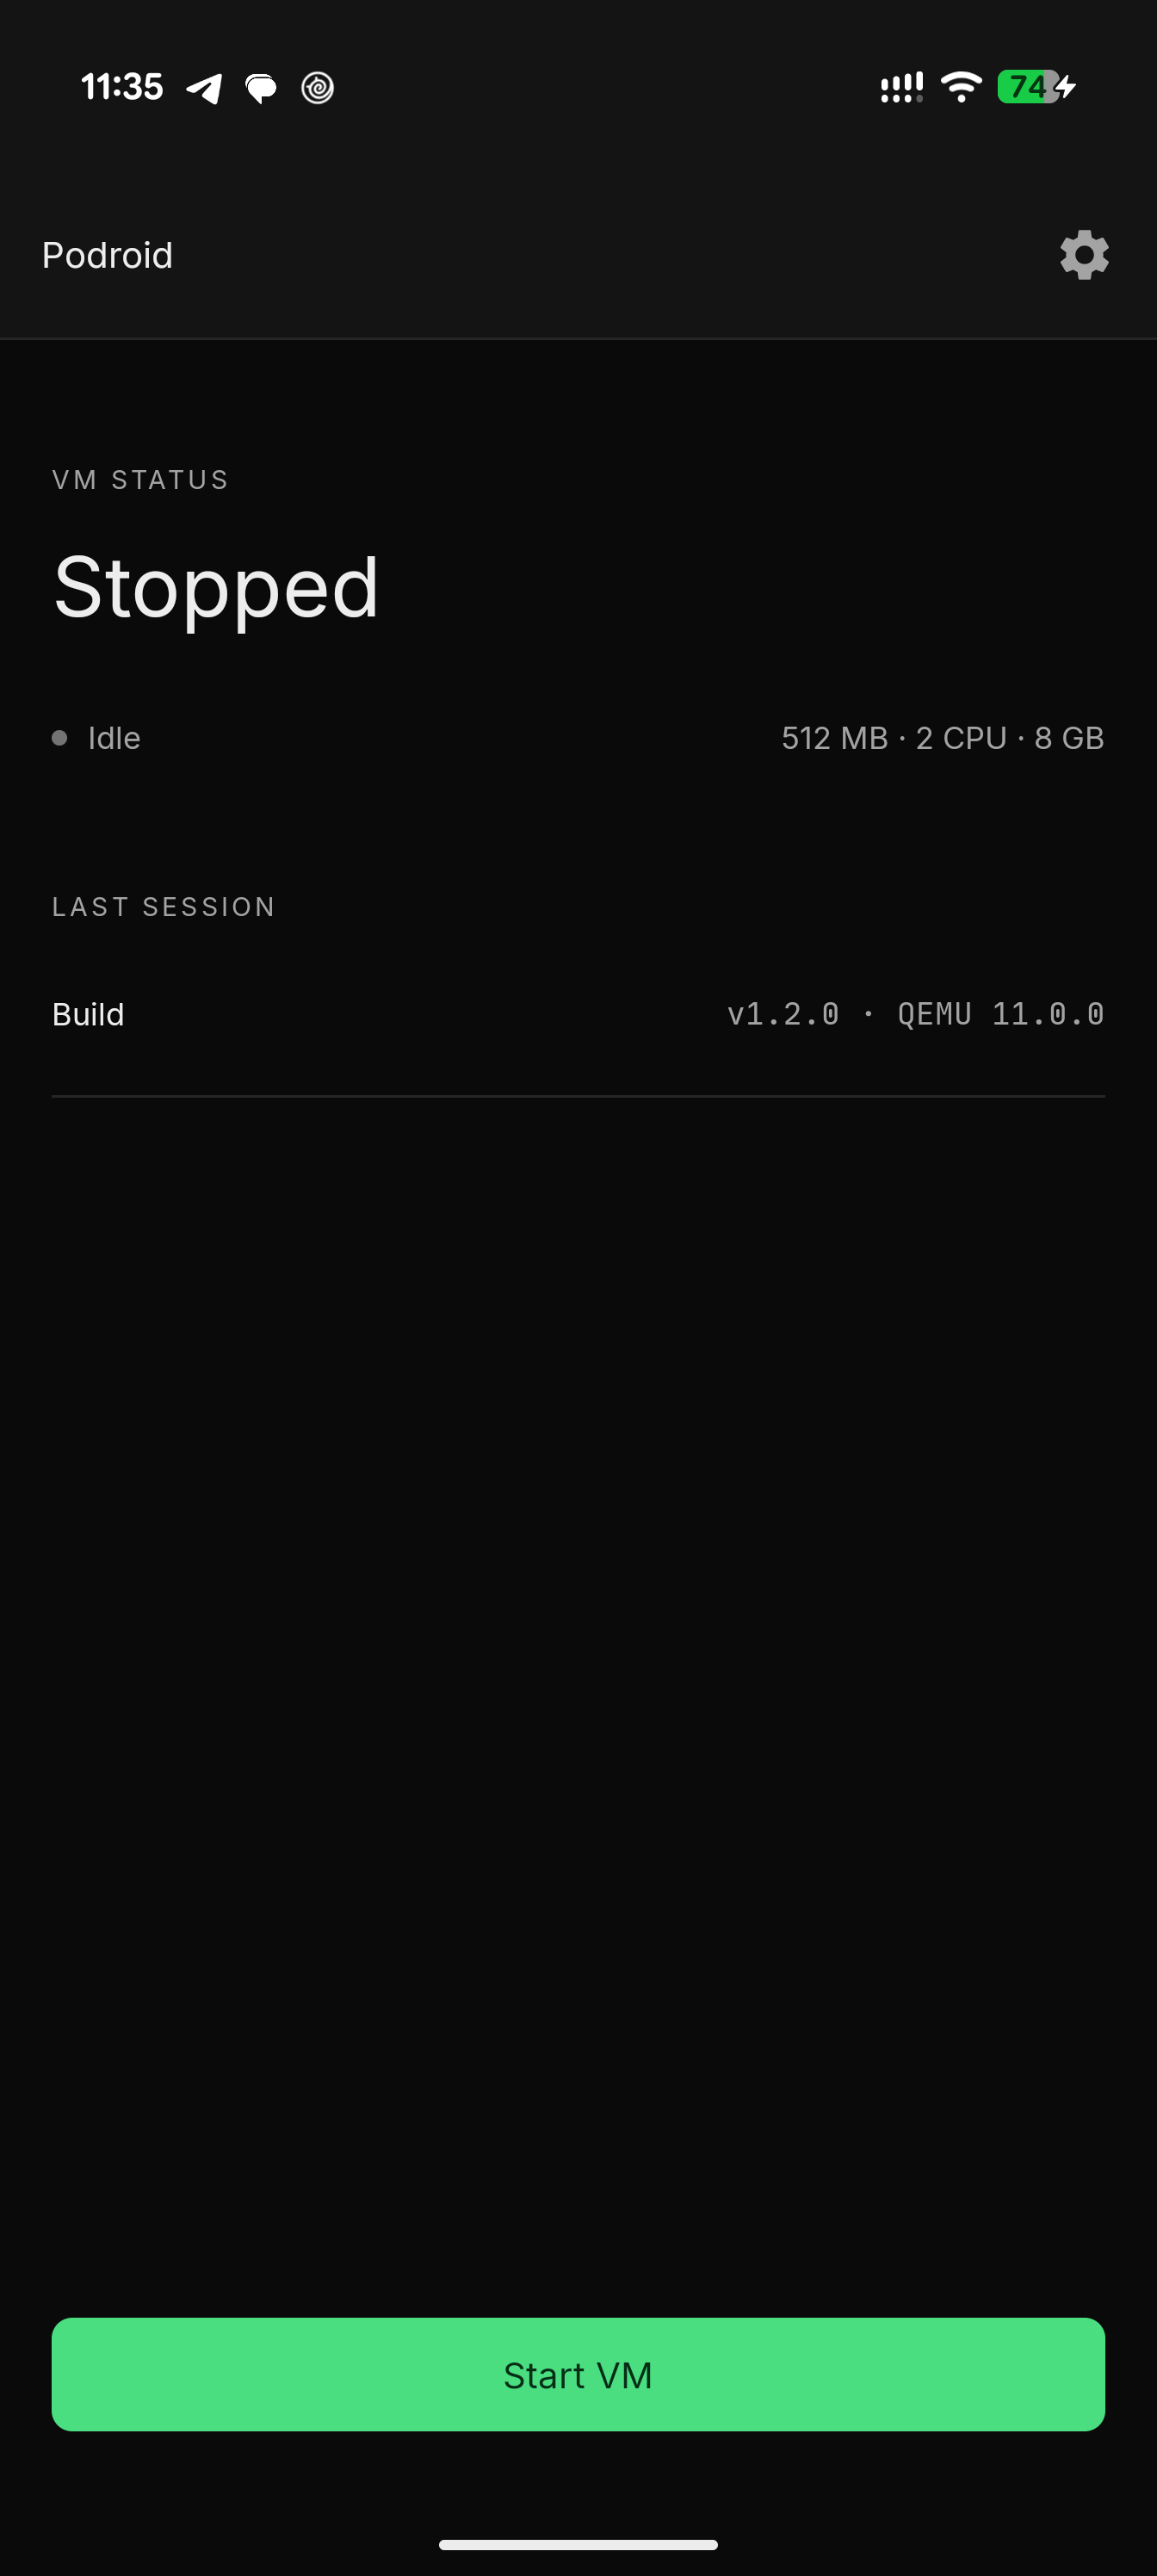 extv/podroid
A rootless Android app that boots Alpine Linux: run containers (Podman/Docker/LXC) and GUI desktop apps.
 dedsec1121fk/dedsec
Educational Android (Termux) toolkit for learning penetration testing, OSINT, social engineering, and network security through hands-on scripts,…
 faizann24/wifi-bruteforcer-fsecurify
Android application to brute force WiFi passwords without requiring a rooted device.
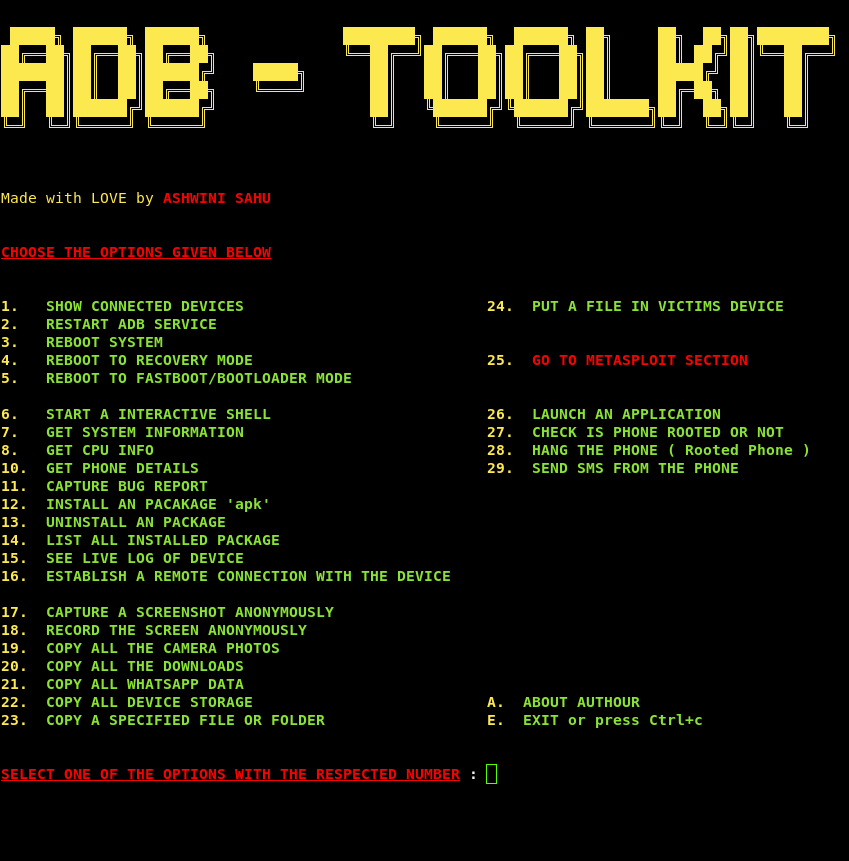 ashwin990/adb-toolkit
ADB-Toolkit V2 for easy ADB tricks with many perks in all one. ENJOY!
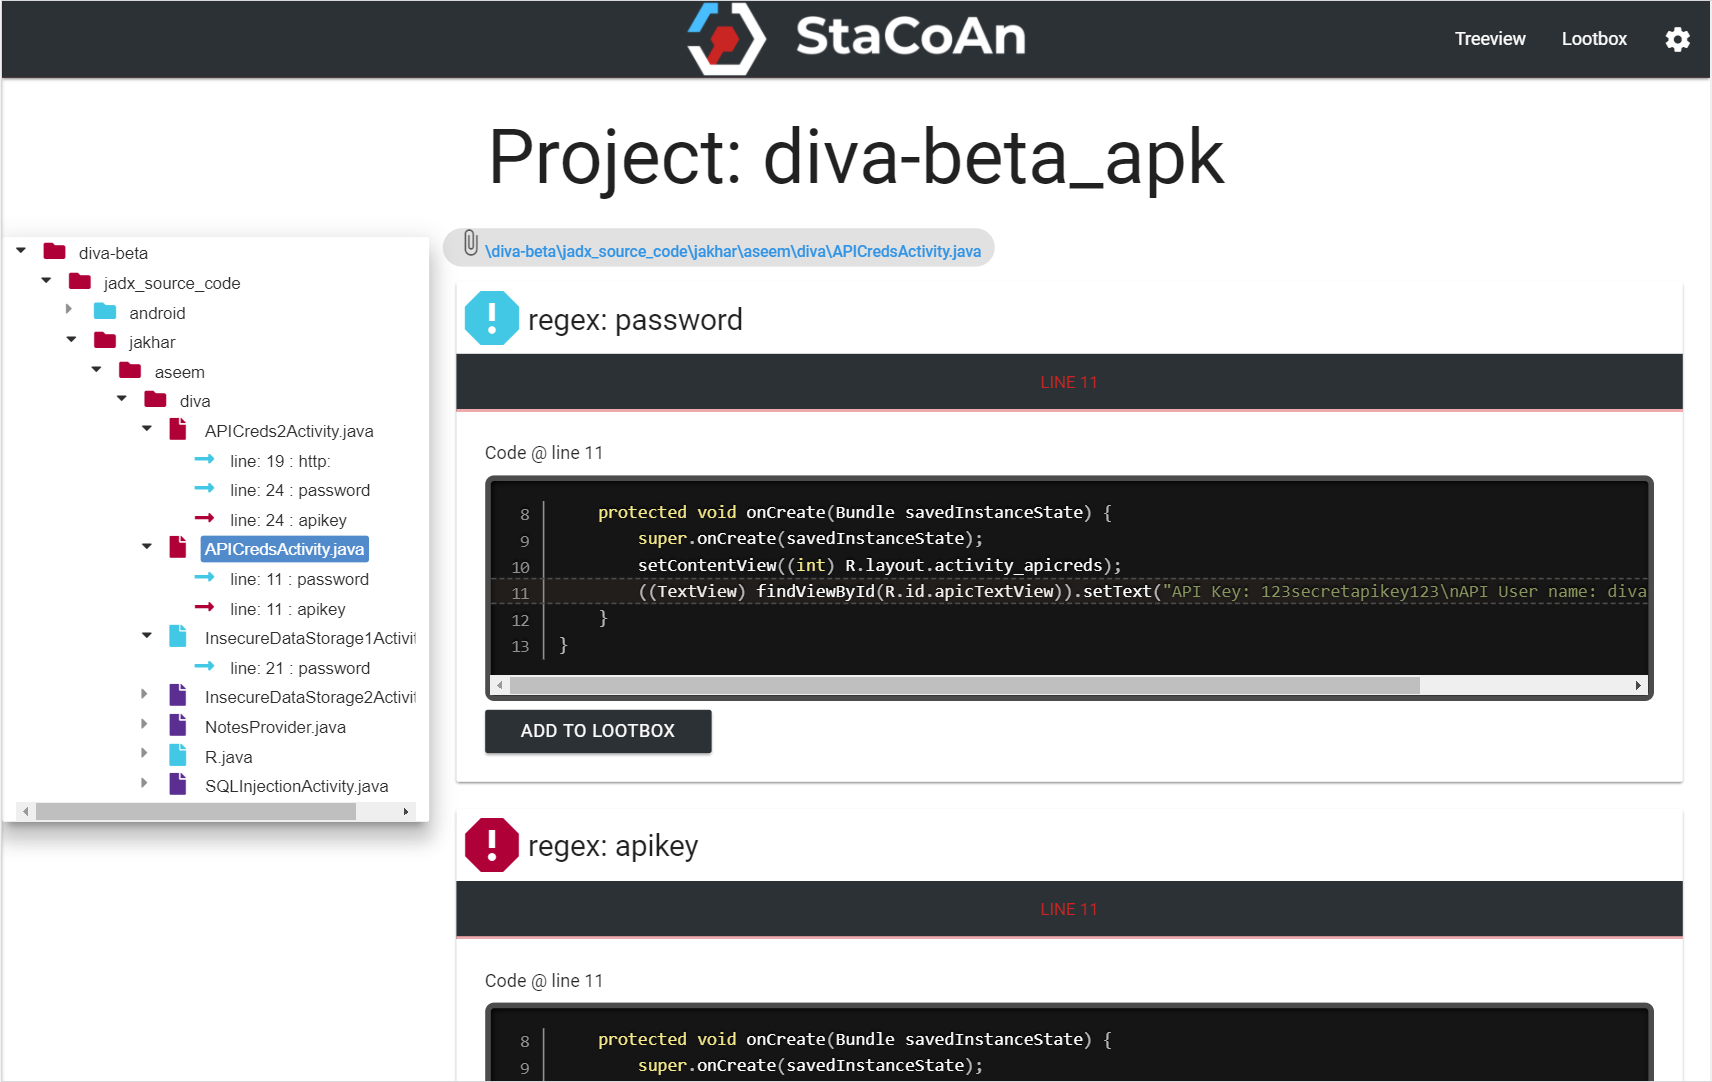 vincentcox/stacoan
StaCoAn is a crossplatform tool which aids developers, bugbounty hunters and ethical hackers performing static code analysis on mobile applications.
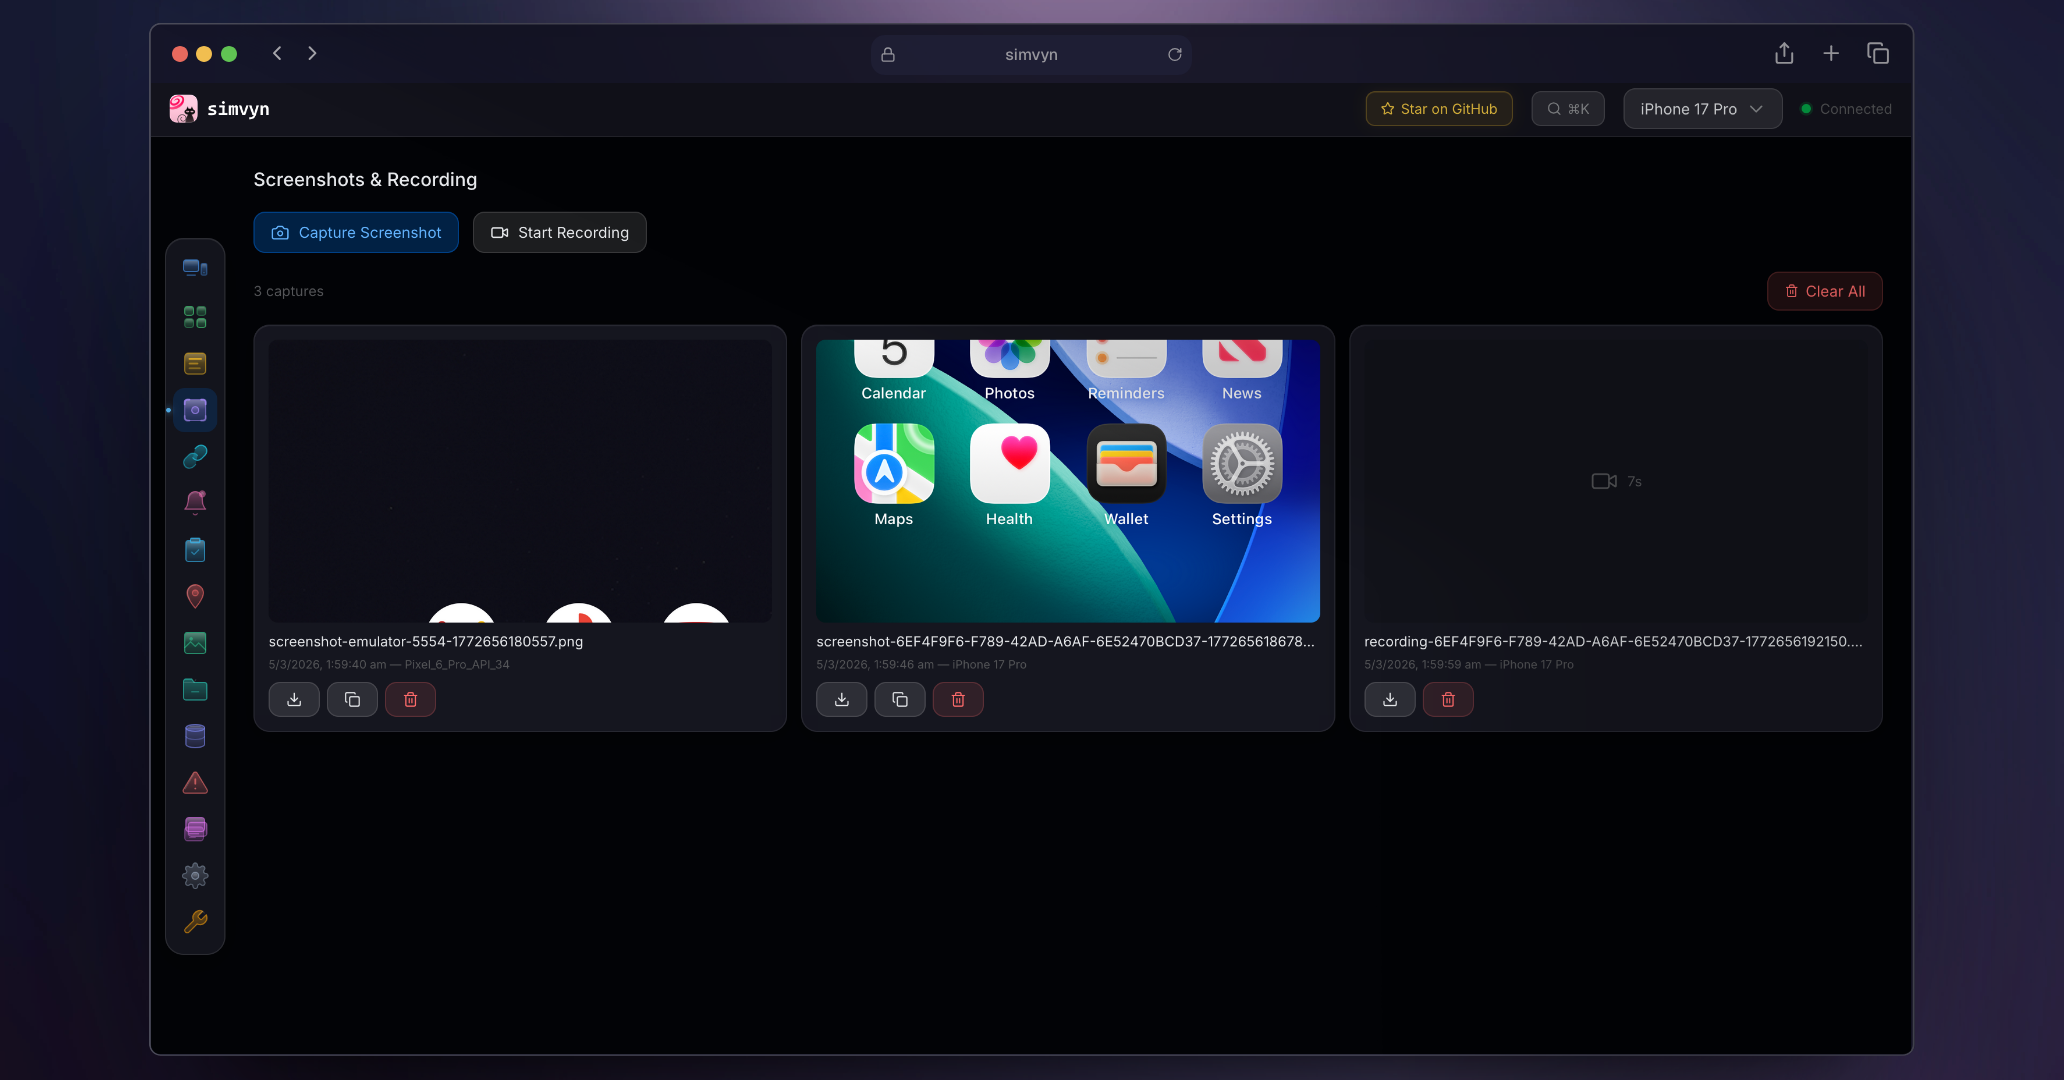 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
 droid-ash/finalrun-agent
AI-driven CLI for testing Android and iOS apps using natural language. Generates, runs, and fixes end-to-end tests on emulators/simulators with…
 jb-selfcompany/tyr
True P2P Email on top of Yggdrasil Network for Android
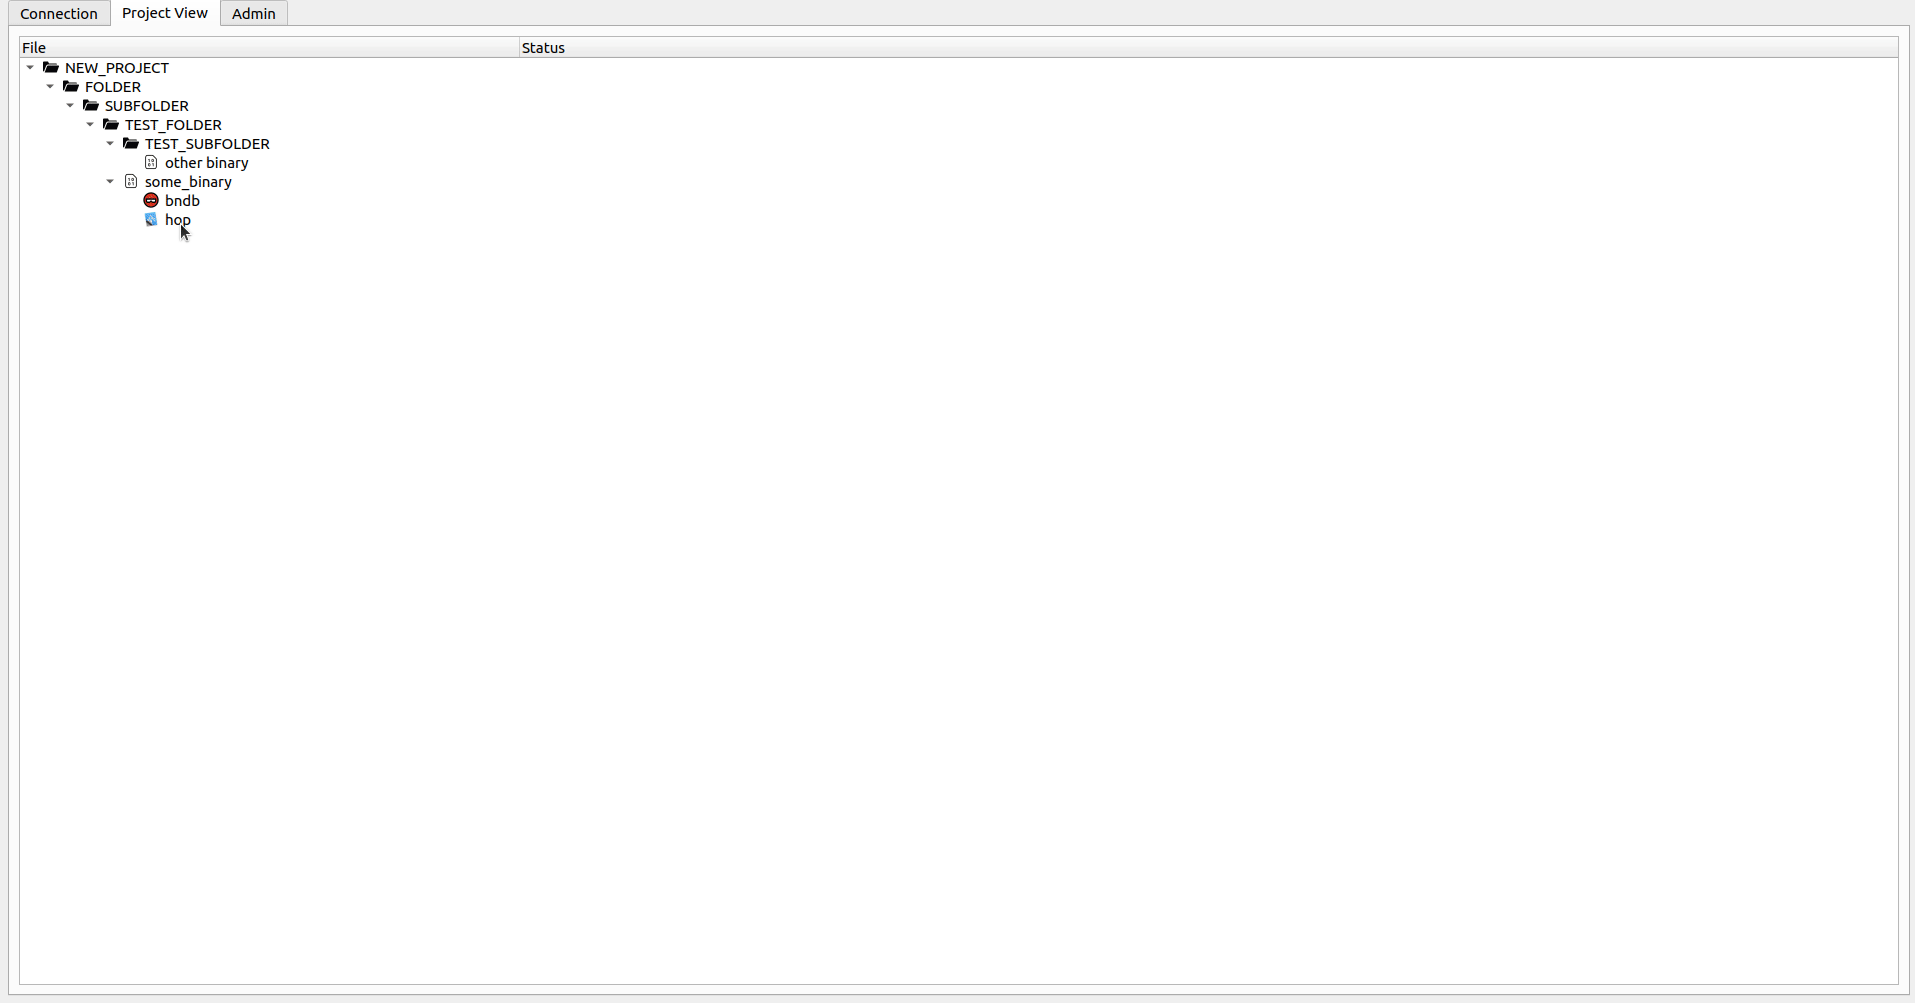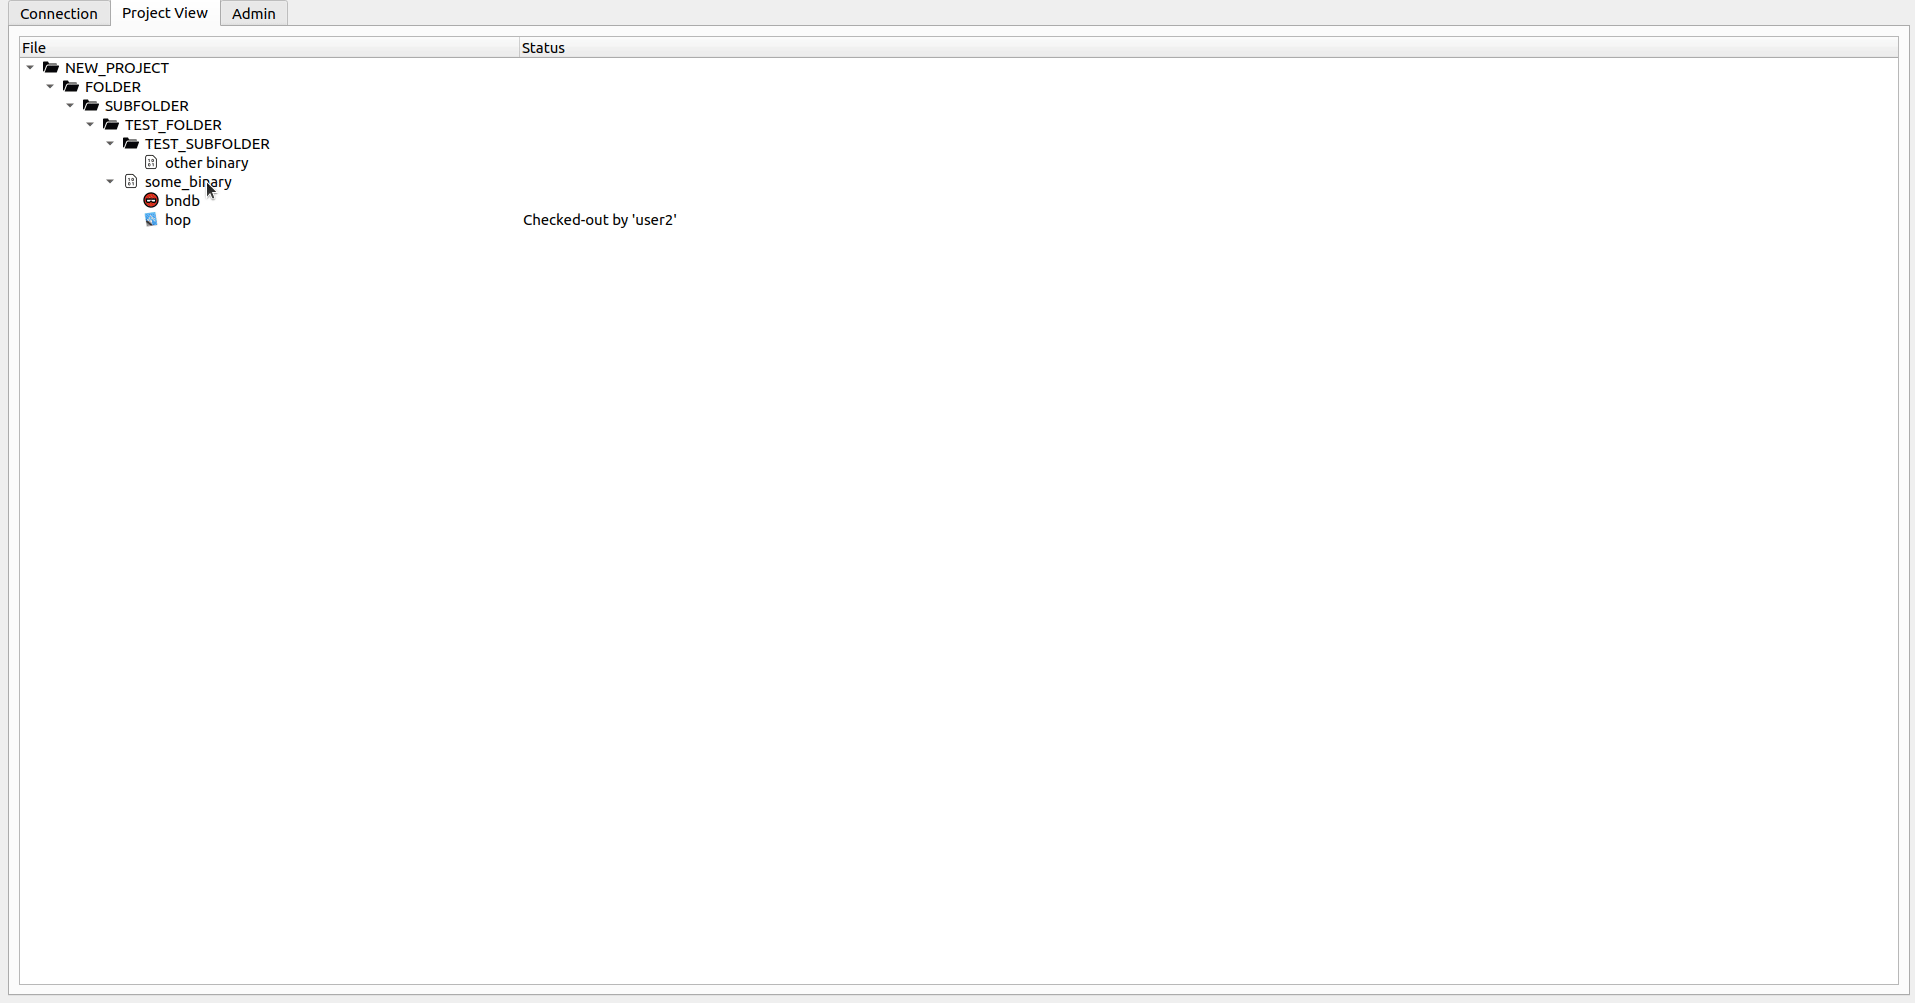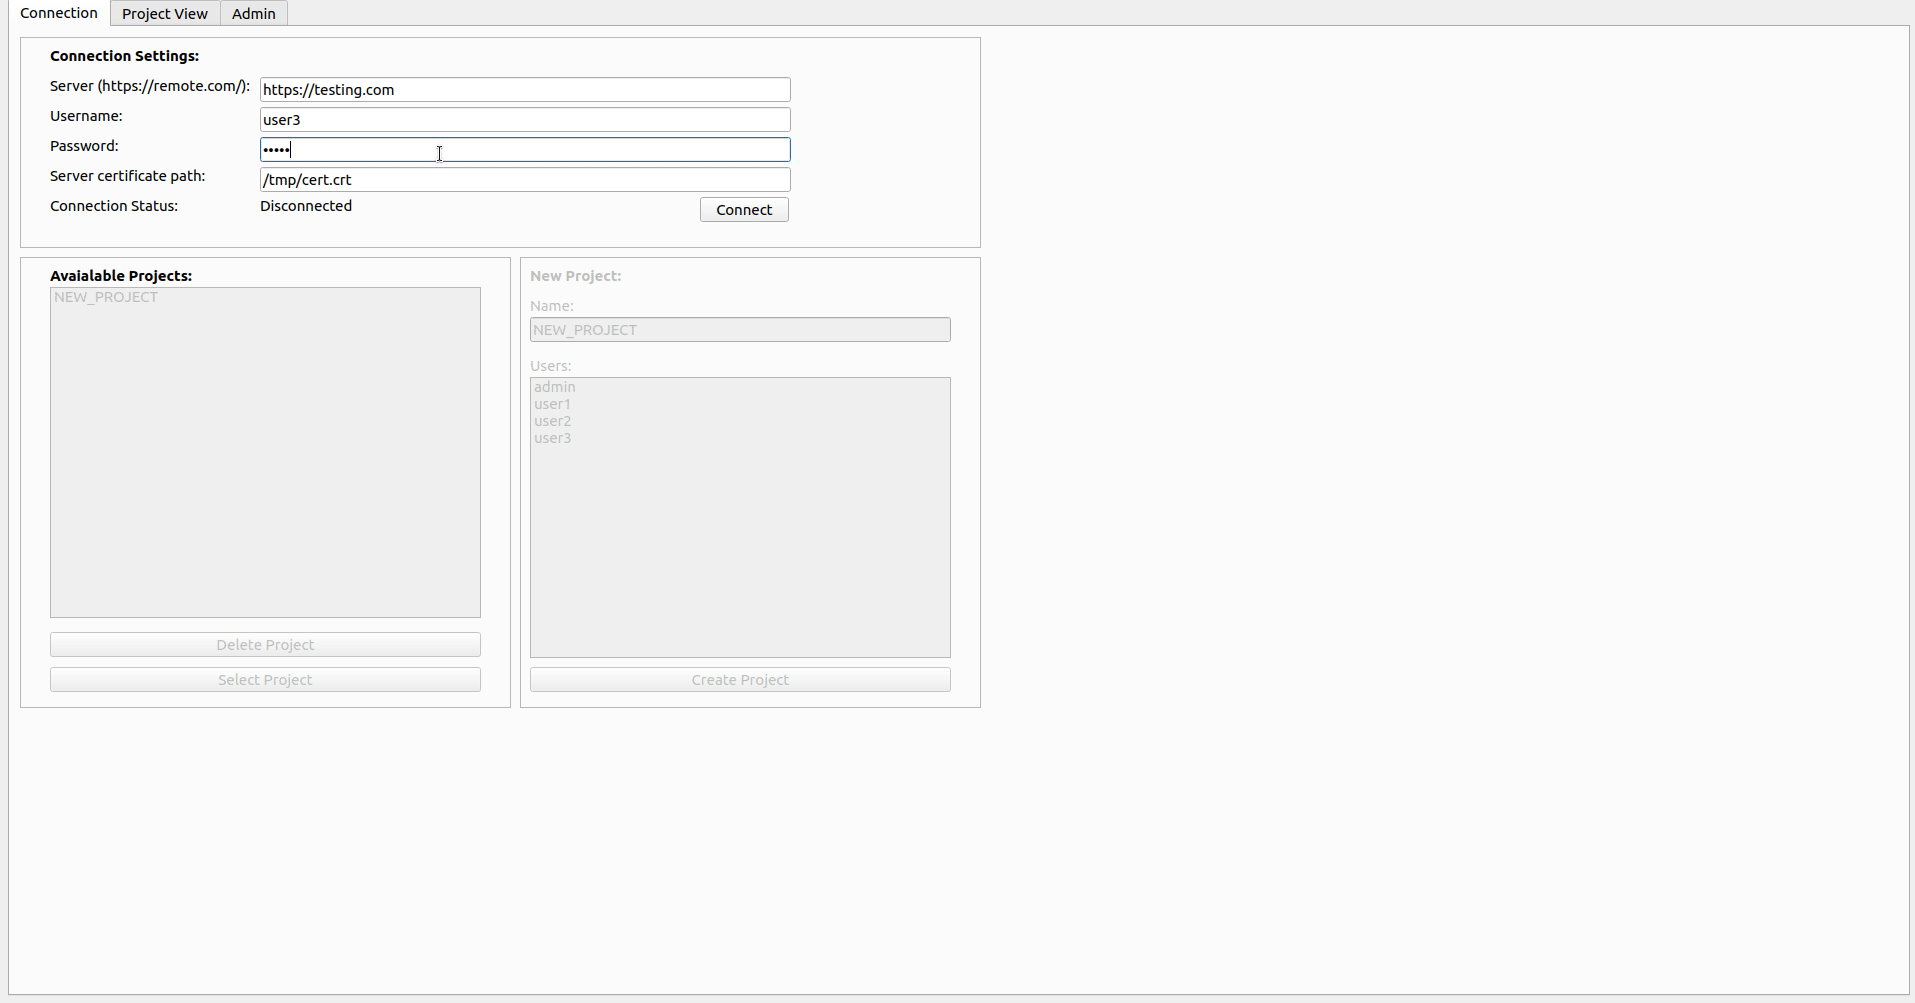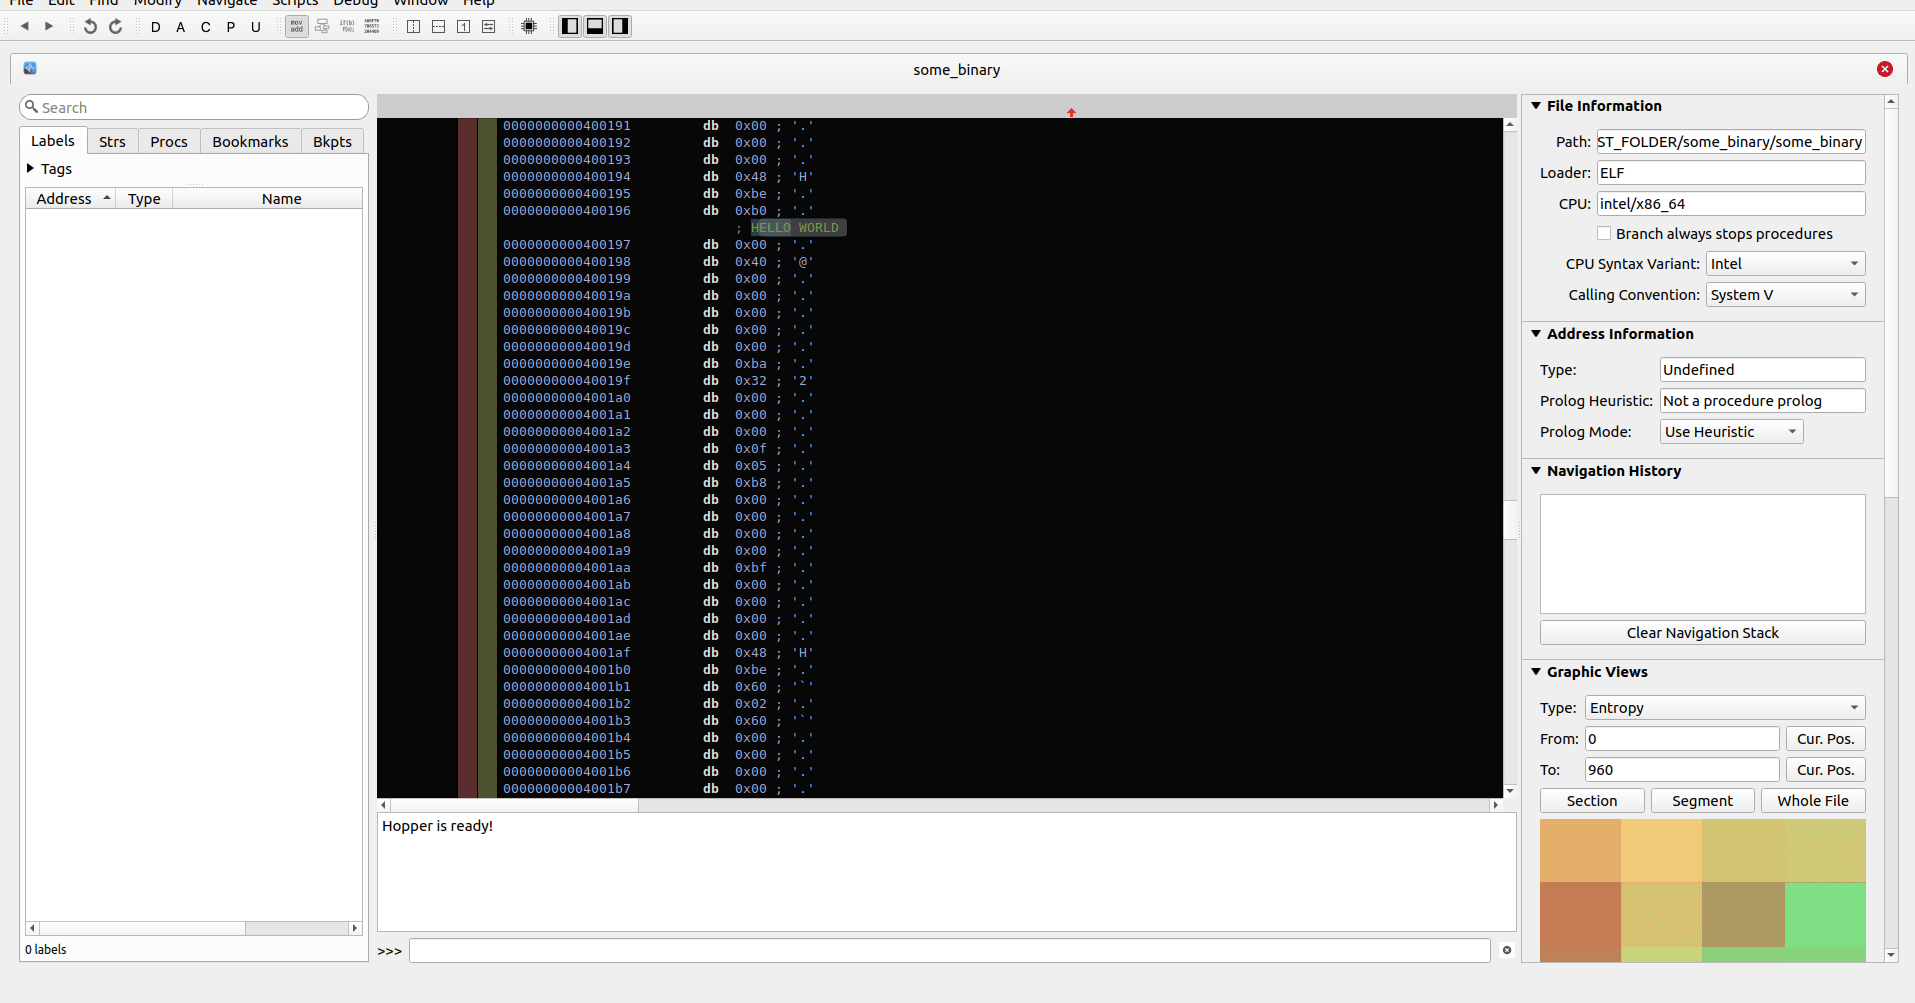 martyx00/collare
Multi-tool reverse engineering collaboration solution.
 timwr/cve-2013-6282
CVE-2013-6282 proof of concept for Android