
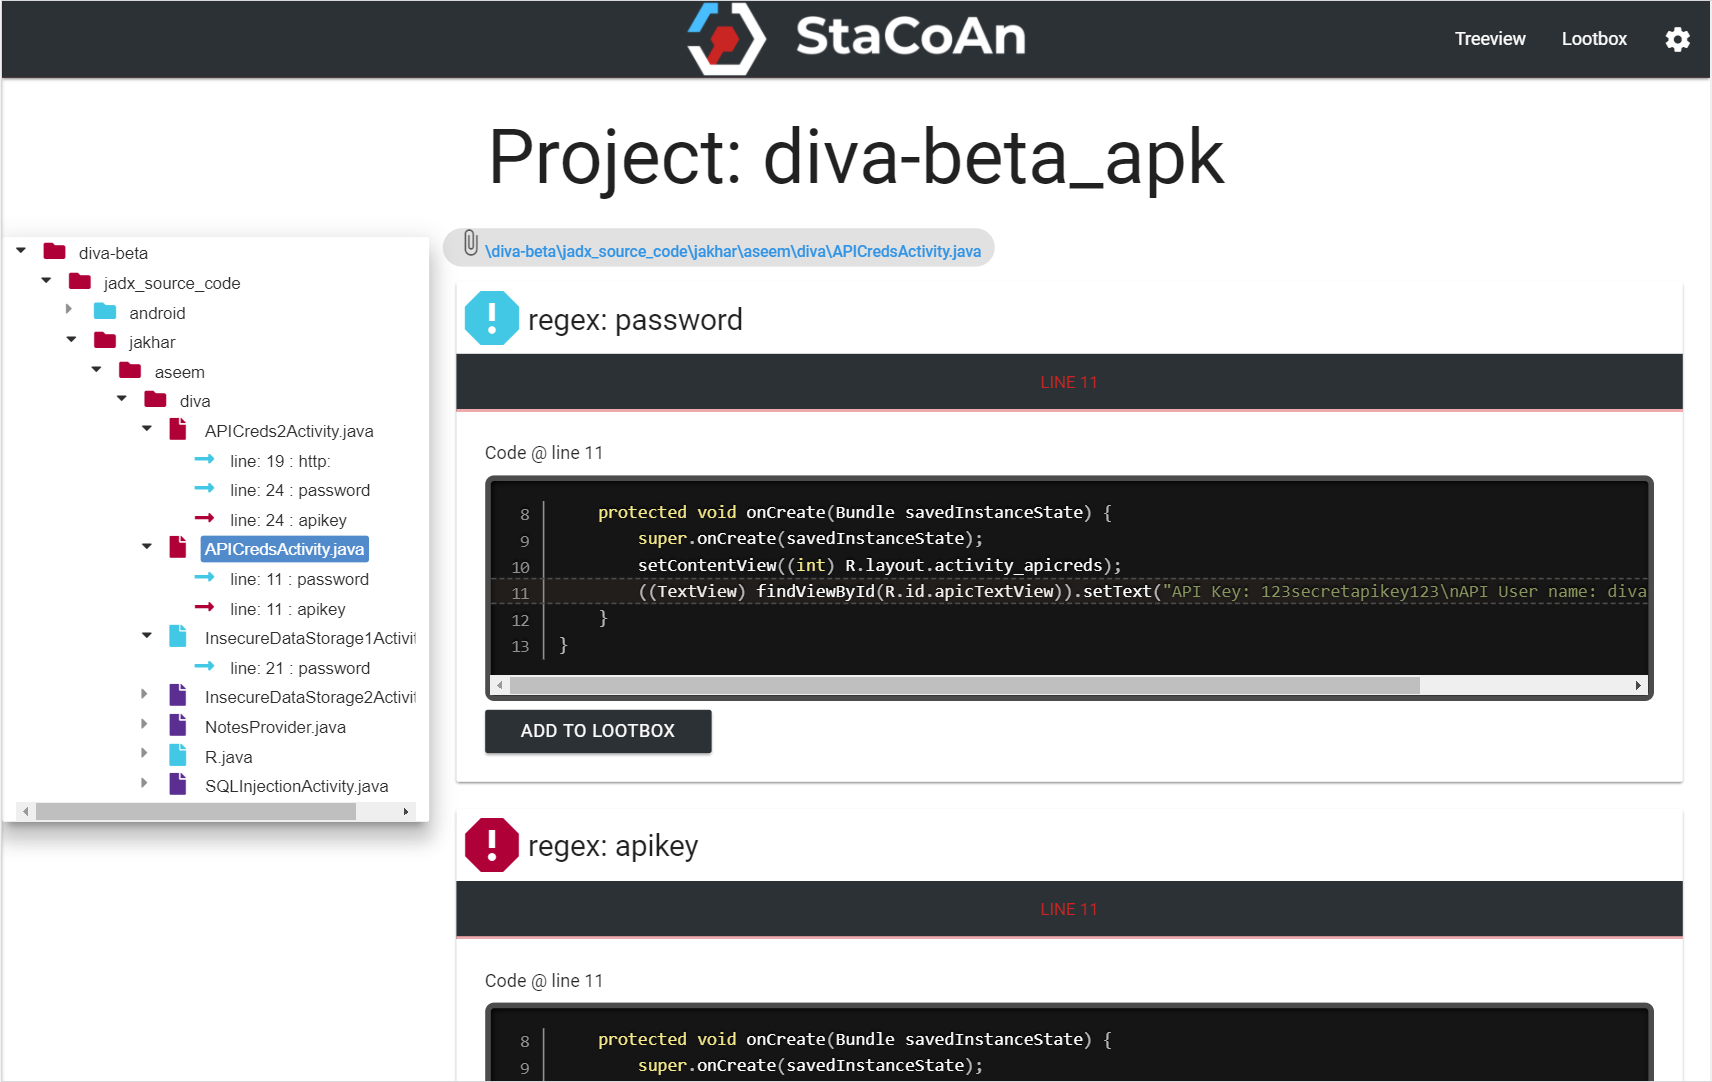
StaCoAn
 vincentcox/stacoan
StaCoAn is a crossplatform tool which aids developers, bugbounty hunters and ethical hackers performing static code analysis on mobile applications.
android-securitymobile-securitystatic-code-analysis+1
vincentcox/stacoanStaCoAn is a crossplatform tool which aids developers, bugbounty hunters and ethical hackers performing static code analysis on mobile applications.
 pjlantz/droidbox
Dynamic analysis sandbox for Android apps that monitors network traffic, file operations, cryptographic API usage, permission circumvention, and…
 nightwatchcybersecurity/truegaze
Static analysis tool for Android/iOS apps focusing on security issues outside the source code
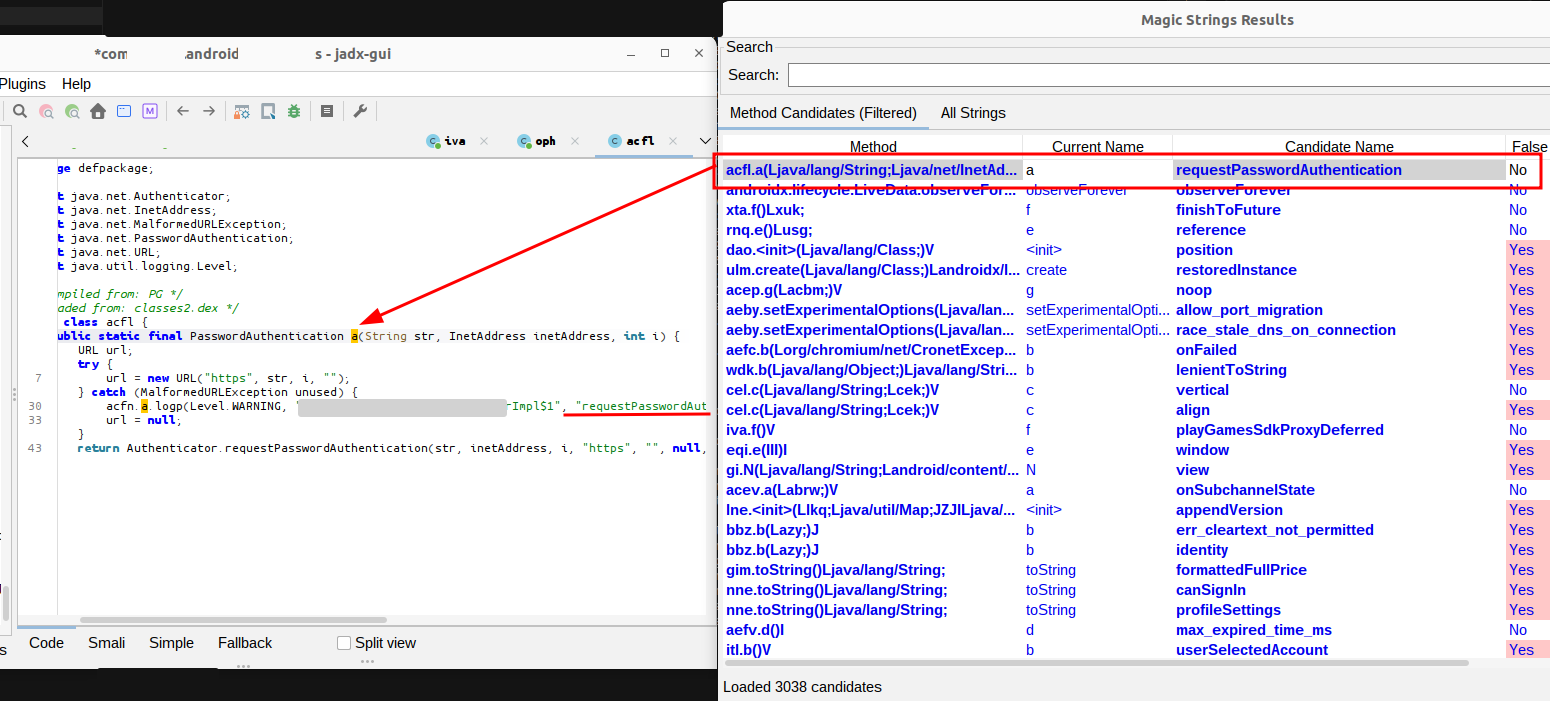 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
 hunt-benito/two-dots-and-a-slash-cve-2026-18907-tecno-hi-browser-download-path-traversal
Python PoC for CVE-2026-18907 path traversal in TECNO Hi Browser's download handler. Includes malicious HTTP server and naive downloader to…
 seqred-s-a/cve-2019-14220
Arbitrary file read in BlueStacks
 haxatron/cve-2022-0219
Proof-of-concept exploit for CVE-2022-0219, an XXE vulnerability in Jadx that allows local file disclosure when exporting malicious APK files via the…
 sonyxperiadev/apkanalyser
Static analysis tool for Android APKs that inspects Dalvik bytecode, decodes XML resources, and detects potential issues. Supports binary…
 ernw/androtickler
Penetration testing and auditing toolkit for Android apps.
 purseclab/cve-2023-33768
DoS against Belkin smart plugs via crafted firmware injection
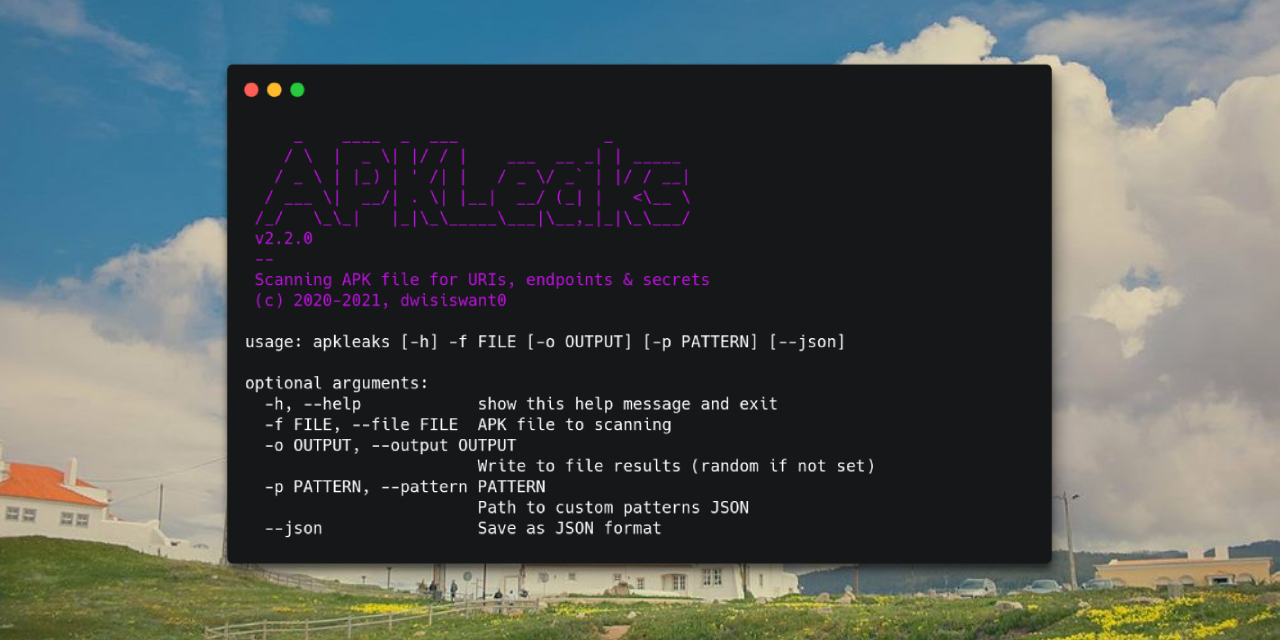 dwisiswant0/apkleaks
Scanning APK file for URIs, endpoints & secrets.
 fs0c131y/esfileexploreropenportvuln
ES File Explorer Open Port Vulnerability - CVE-2019-6447
 jianqiangzhao/cve-2016-2434
Exploit for CVE-2016-2434, a buffer overflow in Android mediaserver enabling arbitrary code execution via crafted media file.
 michalbednarski/thisseemswrong
Writeup and exploit for CVE-2024-49746: Android's Parcel::continueWrite closing File Descriptors that are later used
 chethine/esfileexplorer-cve-2019-6447
Exploiting Android Vulnerability in ES File Explorer
 acloudinthebluesky/cve-2019-6447-es-file-explorer
Technical analysis and safety-conscious research harness for CVE-2019-6447 in ES File Explorer for Android
 h3x0v3rl0rd/cve-2019-6447
Python exploit for CVE-2019-6447 enabling arbitrary file read on ES File Explorer 4.1.9.7.4 for Android. Demonstrates mobile vulnerability…
 febinrev/cve-2019-6447-esfile-explorer-exploit
ES File Explorer v4.1.9.7.4 Open port vulnerability exploit. CVE-2019-6447