

andriller
 den4uk/andriller
📱 Andriller - is software utility with a collection of forensic tools for smartphones. It performs read-only, forensically sound, non-destructive…
android-securitydata-recoverydigital-forensics+4
1.6k
den4uk/andriller📱 Andriller - is software utility with a collection of forensic tools for smartphones. It performs read-only, forensically sound, non-destructive…
 enovella/tee-reversing
A curated list of public TEE resources for learning how to reverse-engineer and achieve trusted code execution on ARM devices
 externalist/exploit_playground
Analysis of public exploits or my 1day exploits
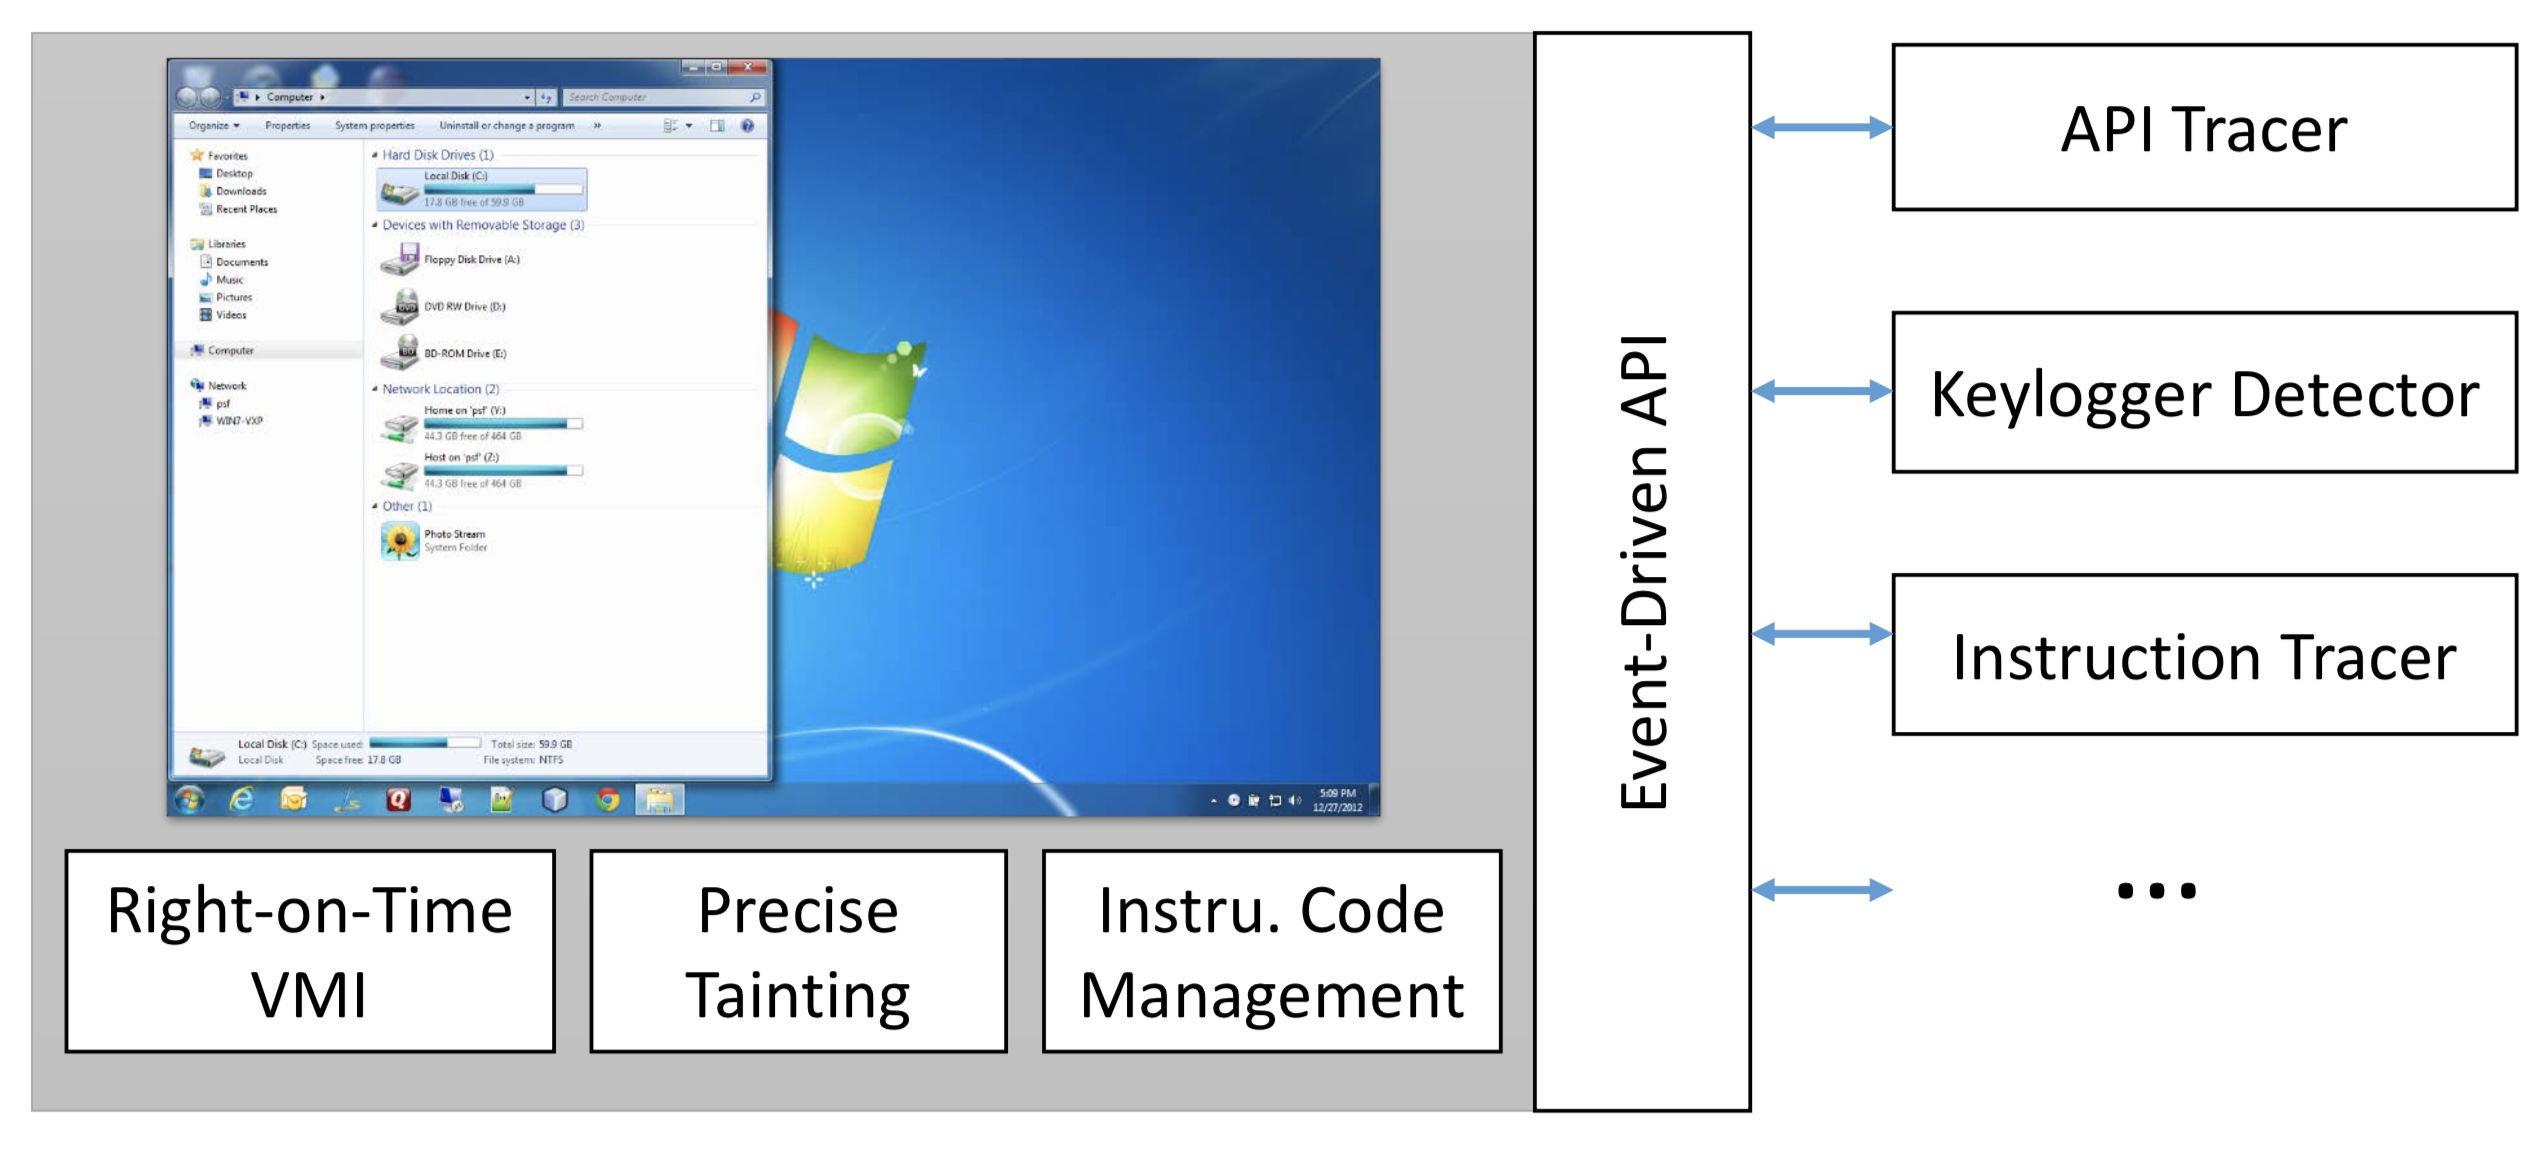 decaf-project/decaf
DECAF (short for Dynamic Executable Code Analysis Framework) is a binary analysis platform based on QEMU. This is also the home of the DroidScope…
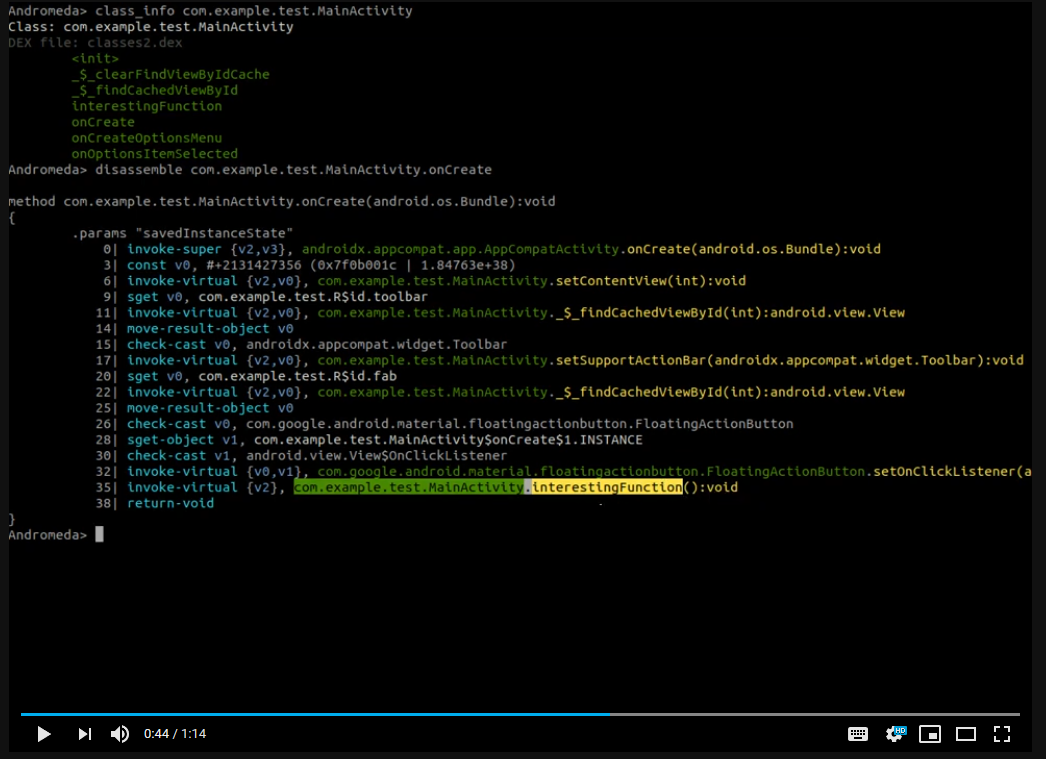 secrary/andromeda
C/C++ interactive reverse engineering tool for Android applications, enabling fast static analysis and binary inspection of APK files.
 zalexdev/wpair-app
WPair is a defensive security research tool that demonstrates the CVE-2025-36911 (eg WhisperPair) vulnerability in Google's Fast Pair protocol. This…
 grant-h/qu1ckr00t
A PoC application demonstrating the power of an Android kernel arbitrary R/W.
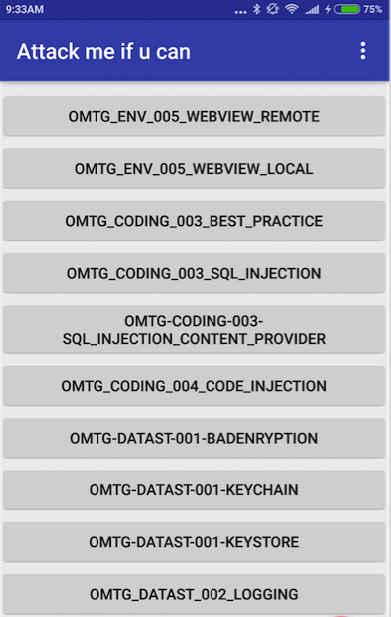 owasp/mastg-hacking-playground
Collection of intentionally insecure iOS and Android apps for learning mobile security testing, reverse engineering, and vulnerability analysis,…
 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
 morpheuslord/quadrainspect
Modular Android APK security analysis framework integrating static, dynamic, and reverse engineering tools for comprehensive vulnerability assessment…
 foundryzero/binder-trace
Binder Trace is a tool for intercepting and parsing Android Binder messages. Think of it as "Wireshark for Binder".
 flankerhqd/vendor-android-cves
Collections of my POCs for android vendor CVEs
 mzfr/slicer
A tool to automate the boring process of APK recon
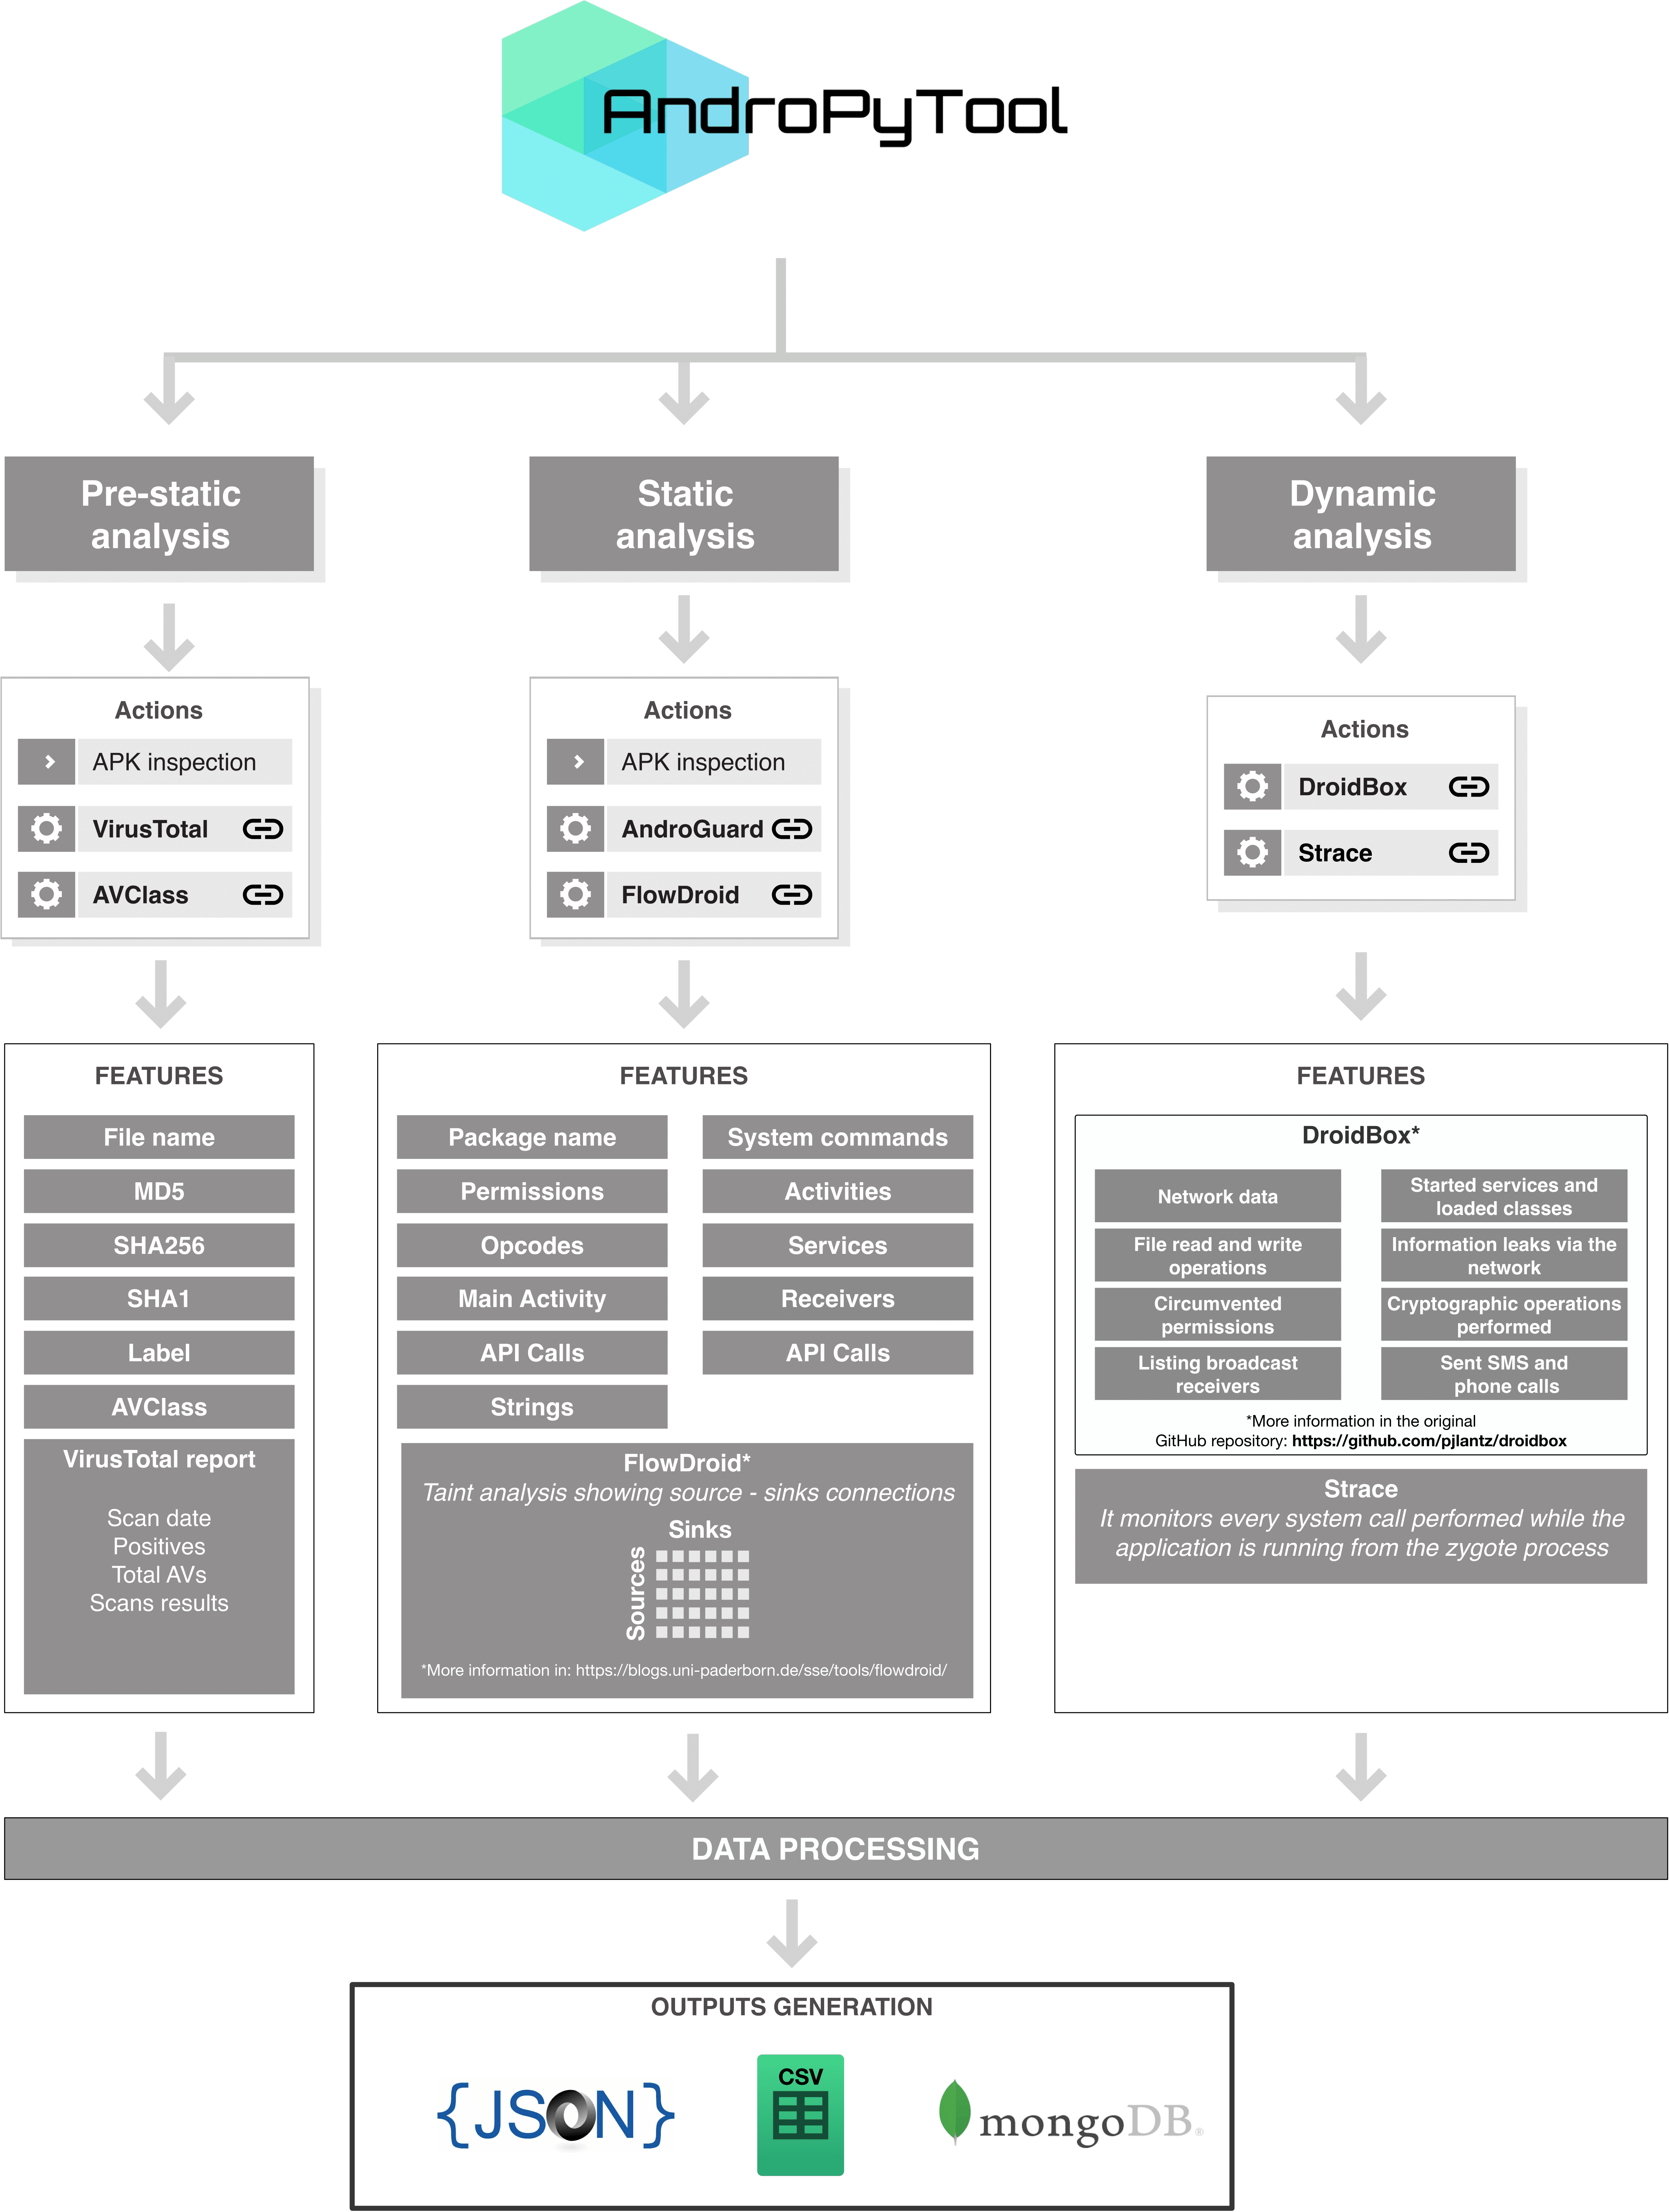 alexmyg/andropytool
A framework for automated extraction of static and dynamic features from Android applications
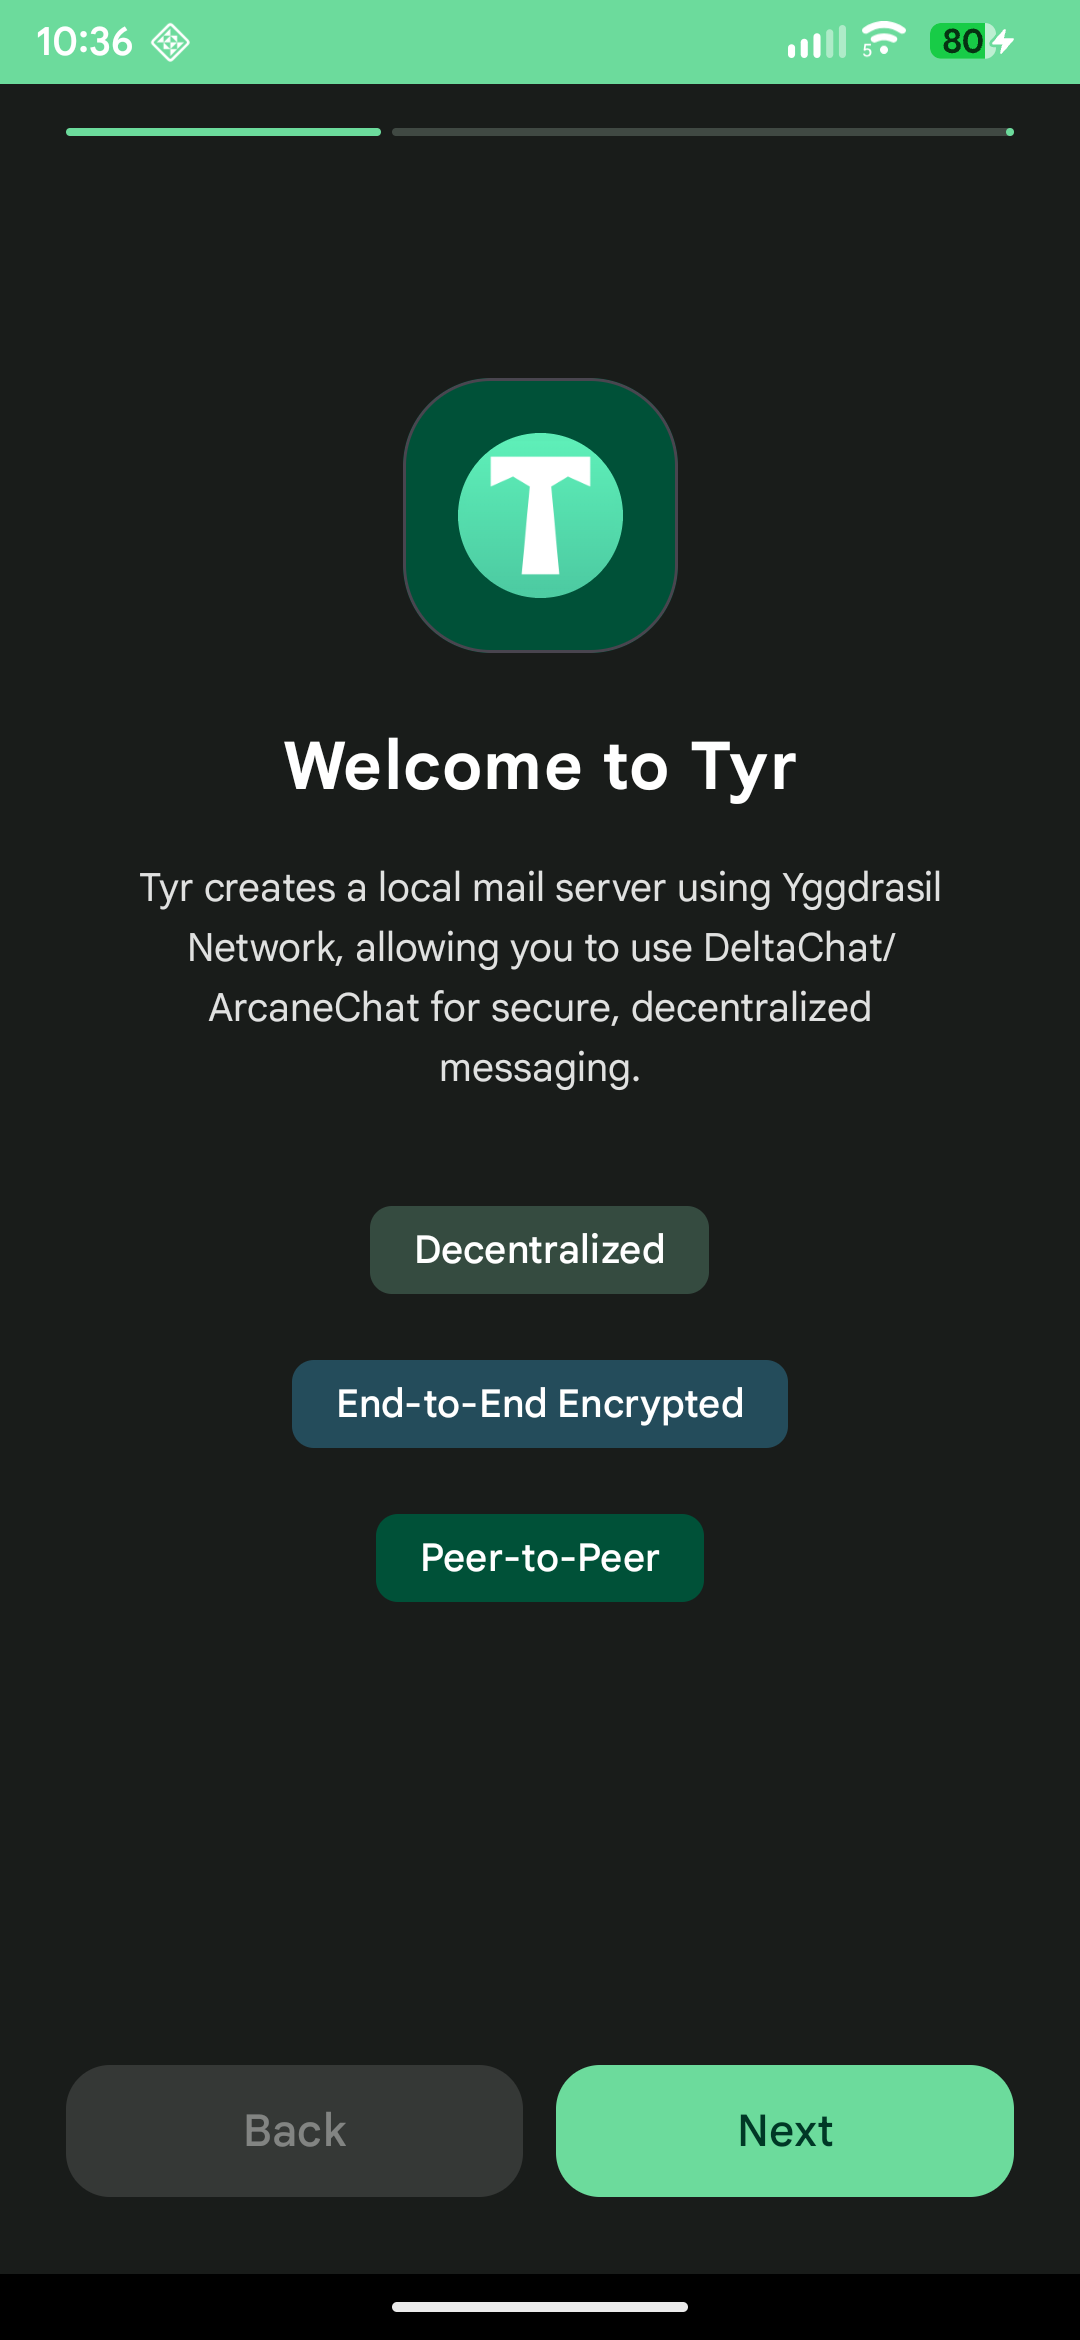 jb-selfcompany/tyr
True P2P Email on top of Yggdrasil Network for Android
 canyie/cve-2024-0044
Proof-of-concept and writeup for bypassing the initial patch of CVE-2024-0044, an Android framework vulnerability enabling privilege escalation from…
 balazsgerlei/androidsecurityevolution
Significant security enchancements of recent major Android versions.
 sysnets/atfuzzer
Grammar-guided evolutionary fuzzer for dynamic analysis of AT command interfaces on Android smartphones via Bluetooth and USB, uncovering DoS,…