Olyx
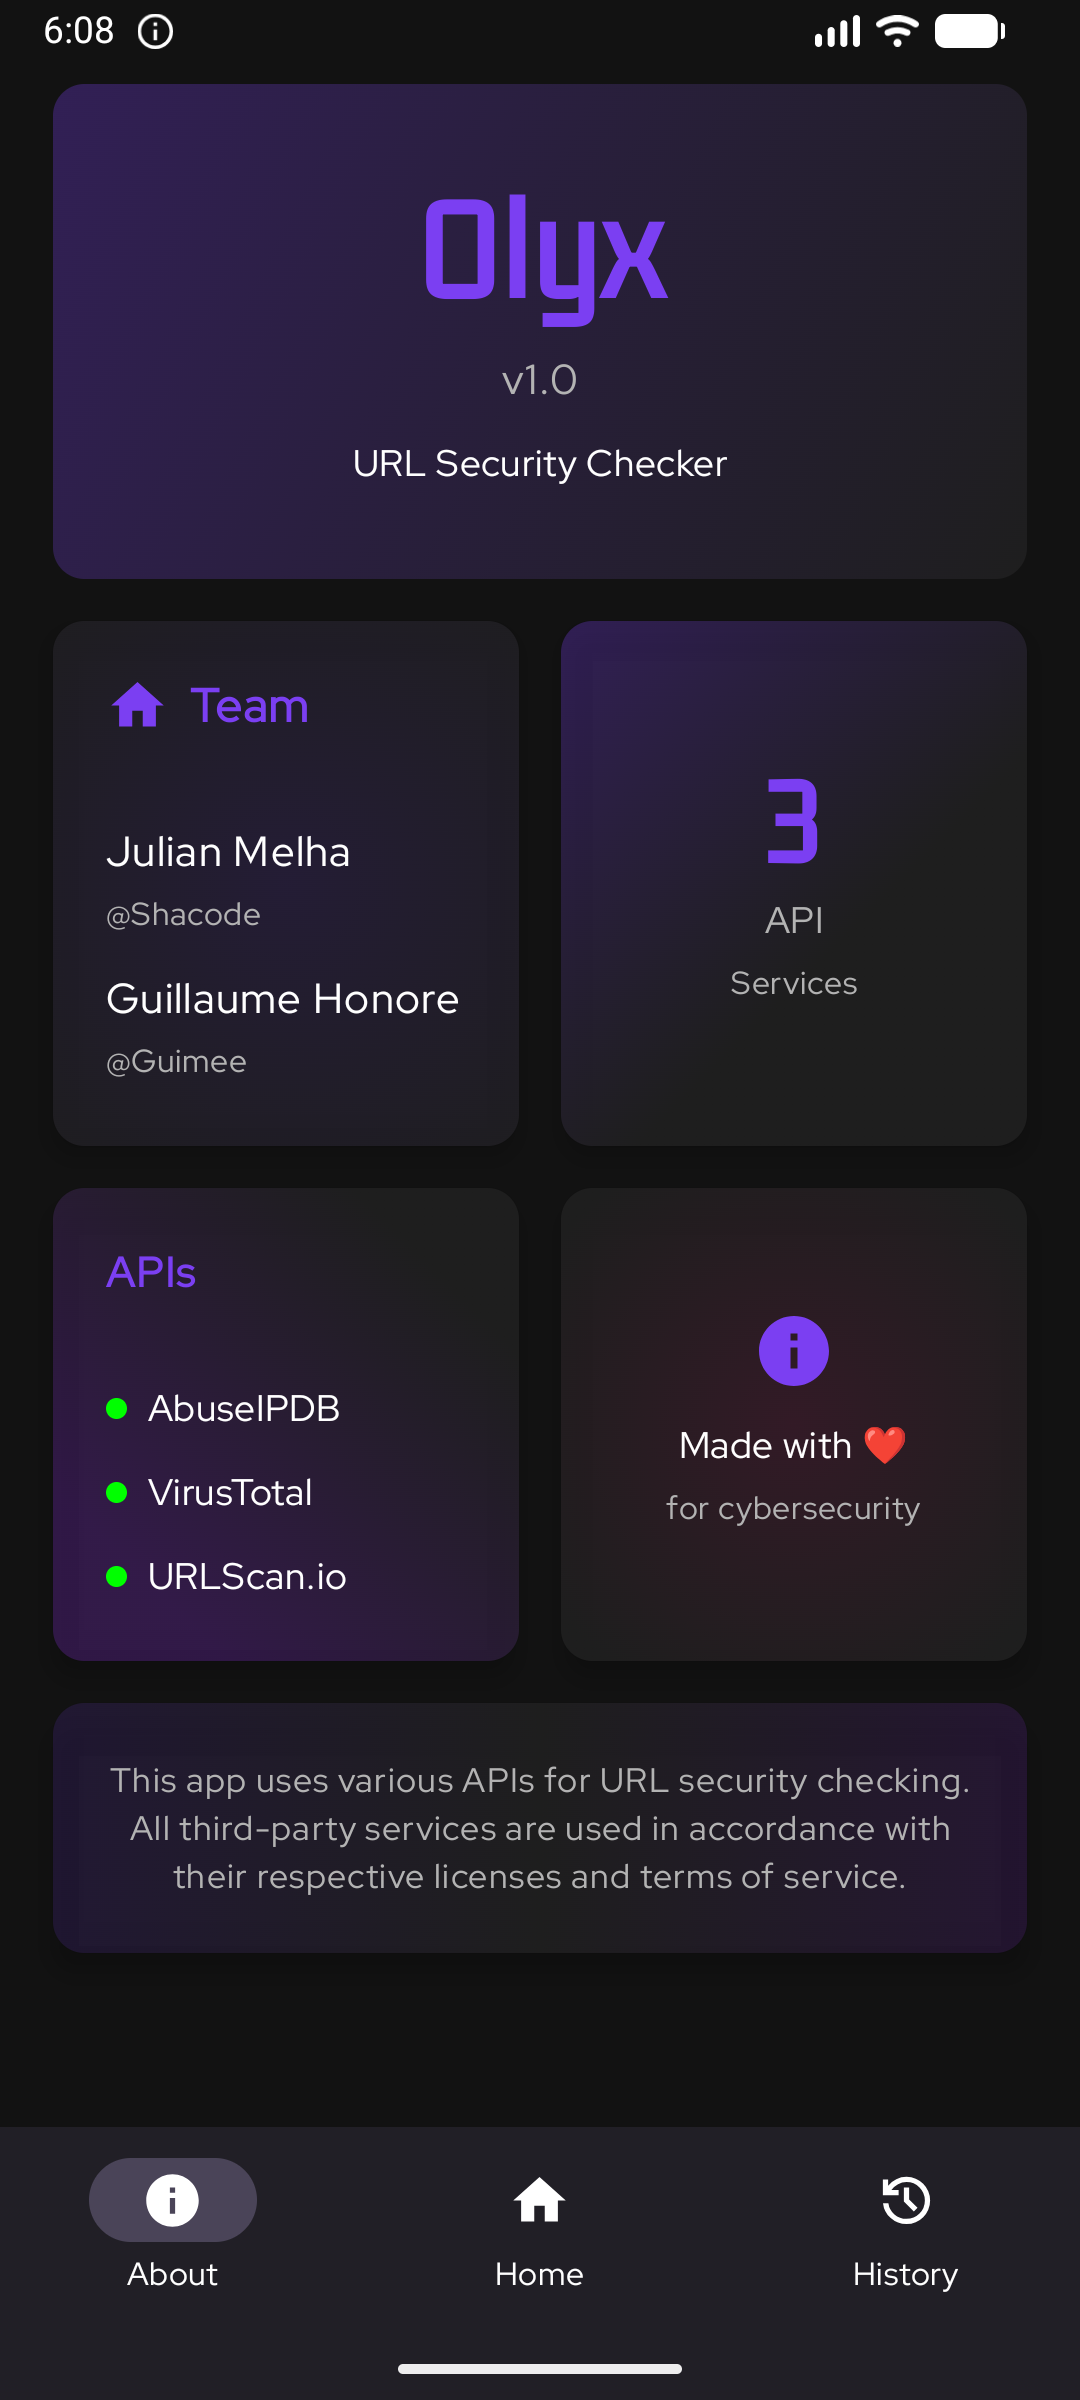
 shacode/olyx
🔗 Lightweight security orchestrator mobile application for URI vetting, providing a unified, multi-engine interface to aggregate and validate link…
android-securityapi-securitydns-analysis+7
shacode/olyx🔗 Lightweight security orchestrator mobile application for URI vetting, providing a unified, multi-engine interface to aggregate and validate link…
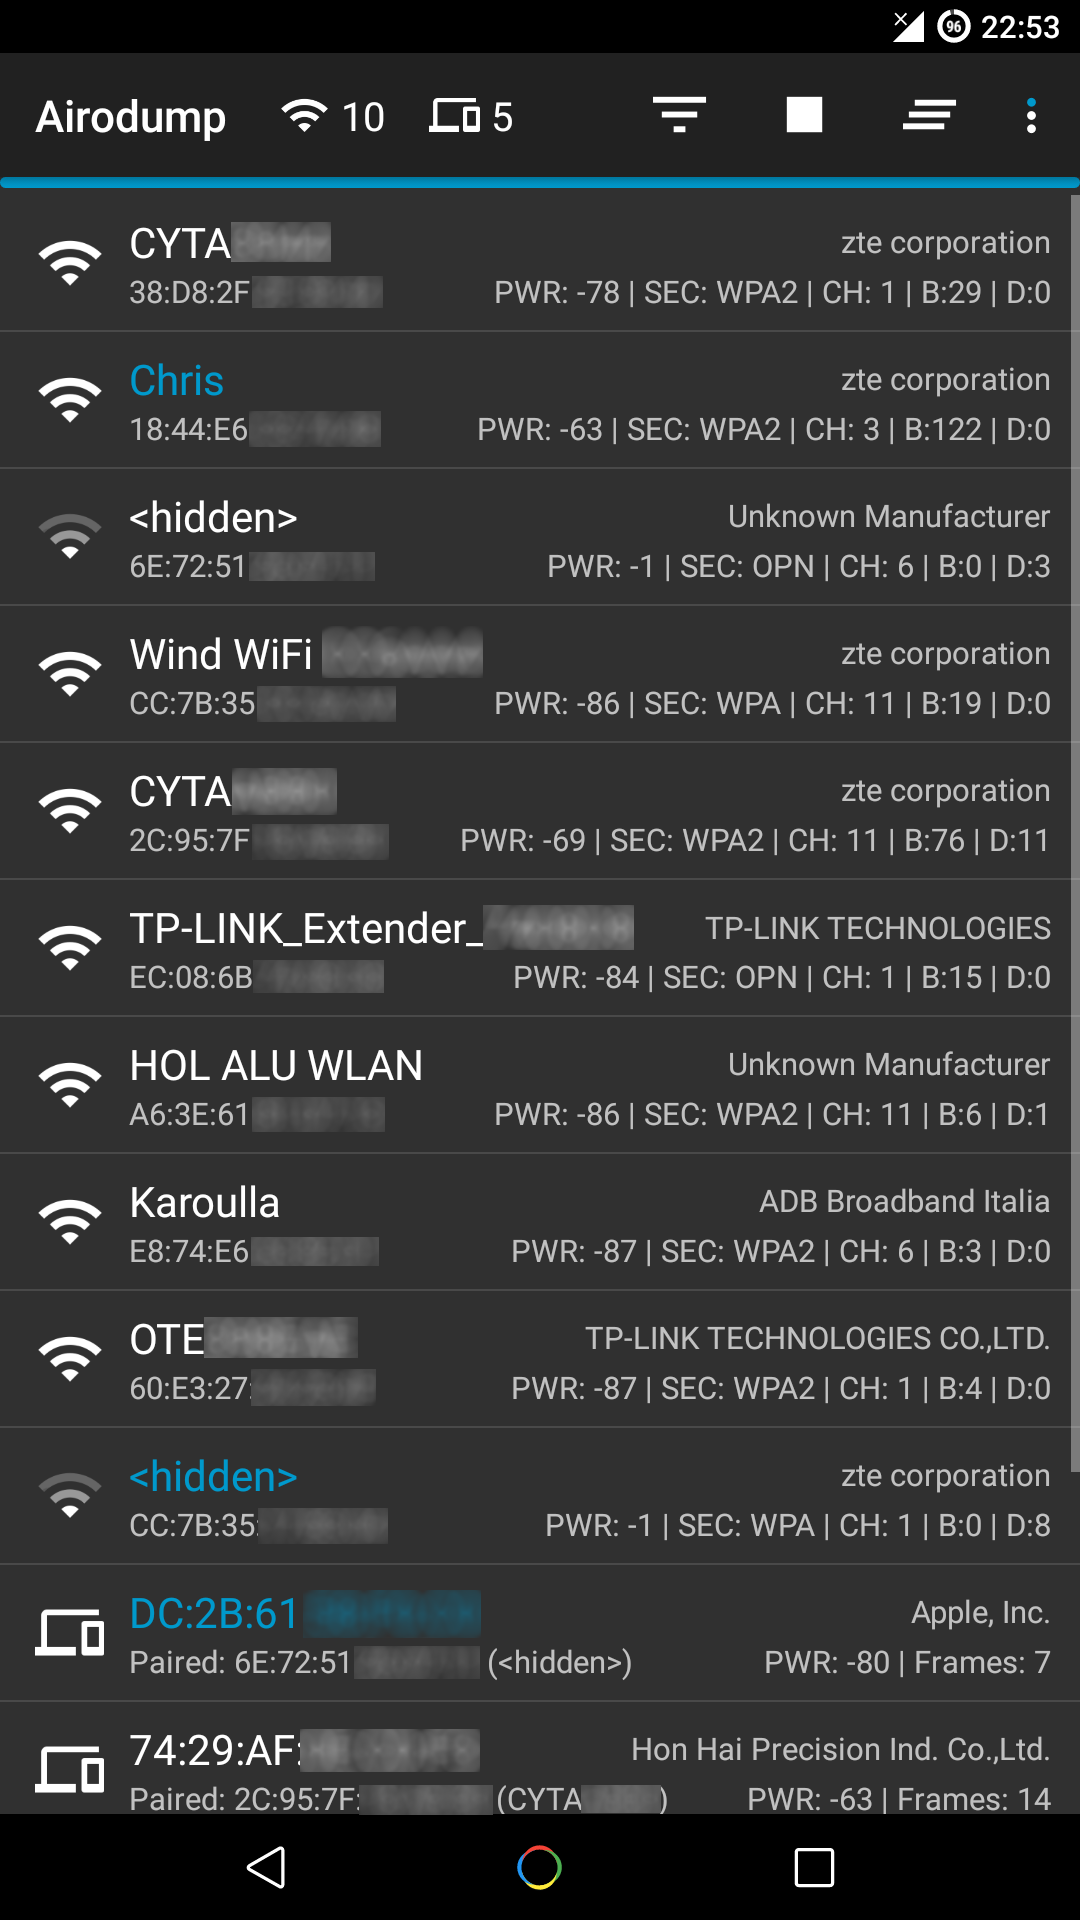
 chrisk44/hijacker
Aircrack, Airodump, Aireplay, MDK3 and Reaver GUI Application for Android
 wheregoes/byd-dolphin-hacking
Reverse engineering the BYD Dolphin head unit — CAN bus, AVAS, NFC keys, OTA, and more. DiLink 3 / Android 10.
 labcif/fama
Forensic Analysis for Mobile Apps (FAMA) -- module for the Autopsy Forensic Browser
 mesquidar/adbsploit
A python based tool for exploiting and managing Android devices via ADB
 frida/frida
Main repo for hosting release binaries
 simoneavogadro/android-reverse-engineering-skill
Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…
 alexandreborges/malwoverview
Malwoverview is a first response tool for threat hunting across VirusTotal, Hybrid Analysis, URLHaus, Polyswarm, Malshare, Alien Vault, Malpedia,…
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 designativedave/androrat
Remote Administration Tool for Android devices
 xploitwizer-community/xploitspy
Cloud-based Android monitoring tool with GPS tracking, microphone recording, SMS/call logging, live notification capture, file explorer, and built-in…
 thakur2309/pagasus-pro
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
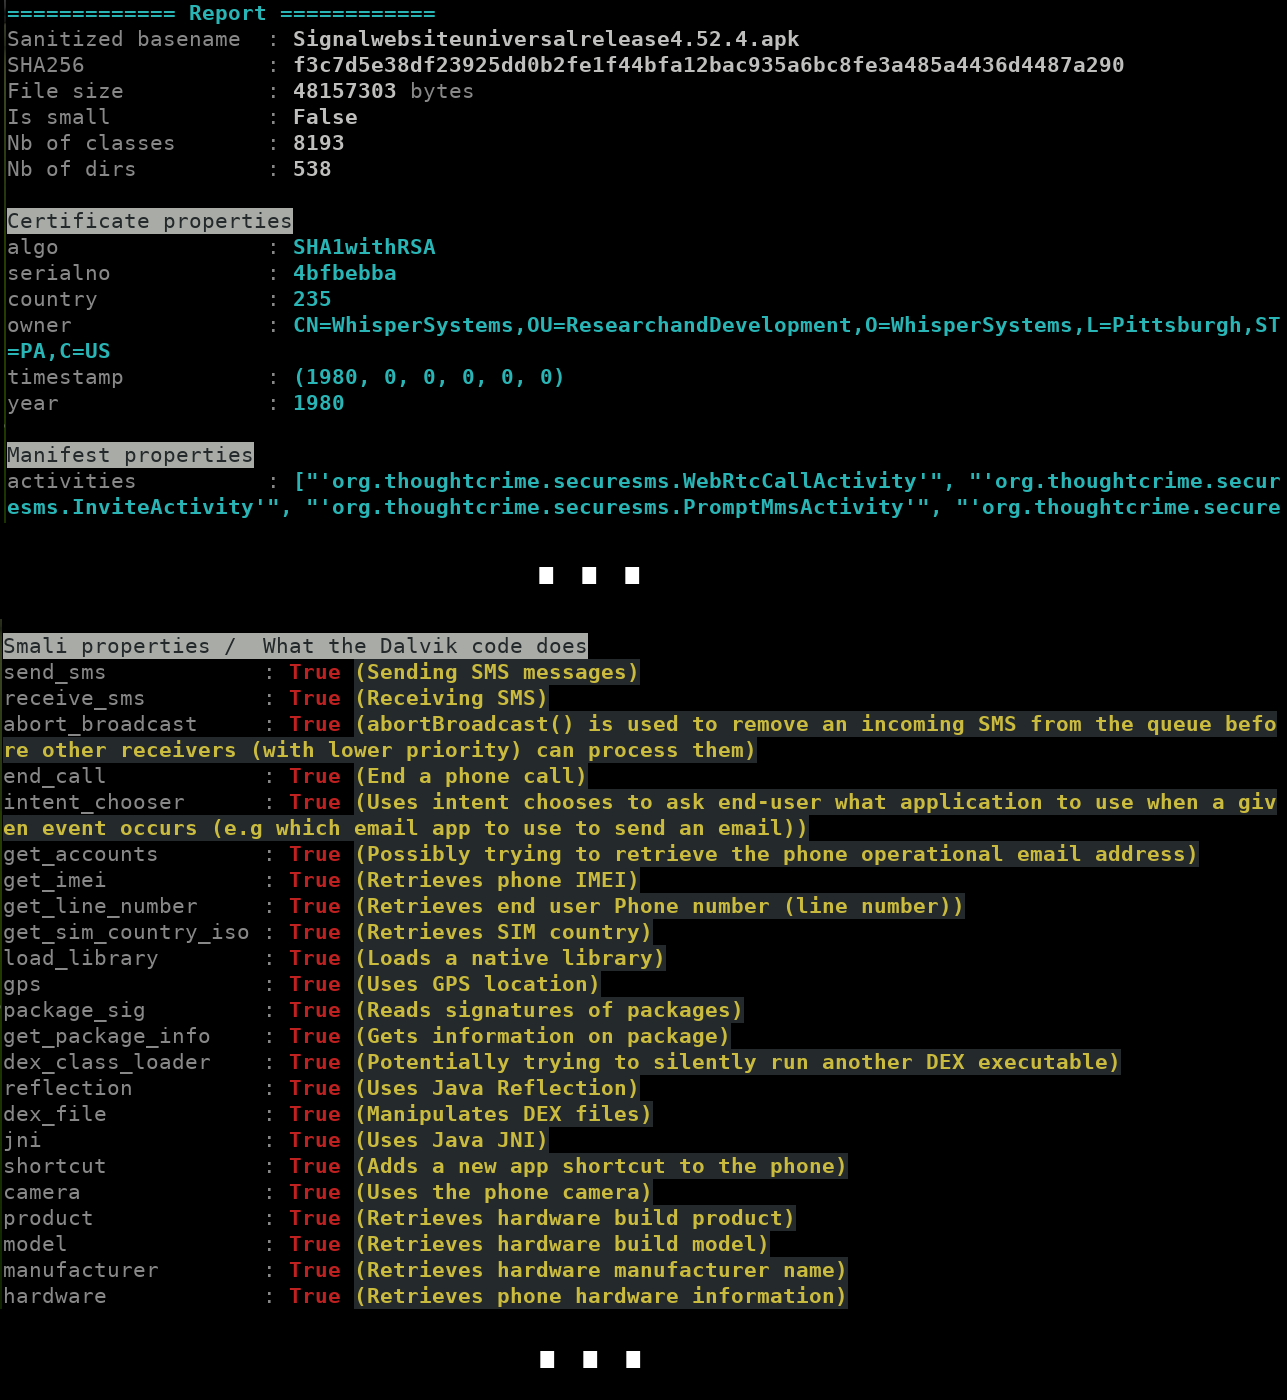 cryptax/droidlysis
Automated pre-analysis tool for Android apps that disassembles samples, extracts properties via configurable pattern matching, and organizes output…
 mozilla/firefox-devtools-mcp
Model Context Protocol server for Firefox DevTools - enables AI assistants to inspect and control Firefox browser through WebDriver BiDi
 0xpwny/apkatshu
Apkatshu is a Tool for extracting urls , emails , ip address , and interesting data from APK files
 packetlss/android-locdump
android location service cache dumper
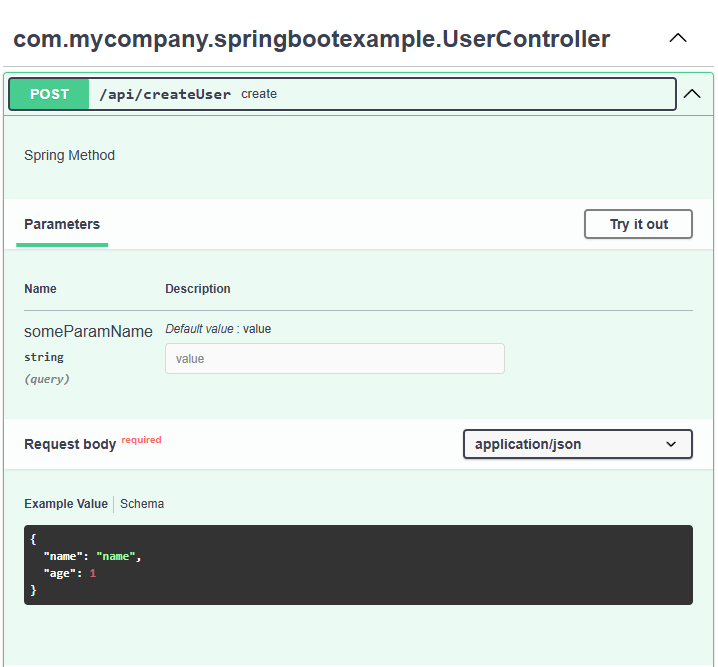 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
 michalbednarski/thisseemswrong
Writeup and exploit for CVE-2024-49746: Android's Parcel::continueWrite closing File Descriptors that are later used