

PoCForCVE-2015-1528
 kanpol/pocforcve-2015-1528
Proof-of-concept exploit for CVE-2015-1528 demonstrating privilege escalation on Android 5.0 via binder call fuzzing, with staged code injection into…
android-securitybinary-exploitationexploitation+3
1
kanpol/pocforcve-2015-1528Proof-of-concept exploit for CVE-2015-1528 demonstrating privilege escalation on Android 5.0 via binder call fuzzing, with staged code injection into…
 actuator/ekoparty
Ekoparty Miami | Interface Anti-Patterns: Exploiting Insecure Navigation in 3rd Party Android App Lockers
 ravss/bluetooth-crash-cve-2017-0785
Exploit script for CVE-2017-0785 that crashes the Bluetooth module on Android 4.0+ devices by sending crafted SDP search requests, causing…
 idkwim/cve-2020-0022
Research repository documenting BlueFrag (CVE-2020-0022) Android Bluetooth heap overflow experiments, including GDB crash analysis and memcpy…
 aureliusivaninvenioptl/ubl-itel-s23
Unlock Bootloader for Itel S23 (S665L) / Unisoc T606 using CVE-2022-38694
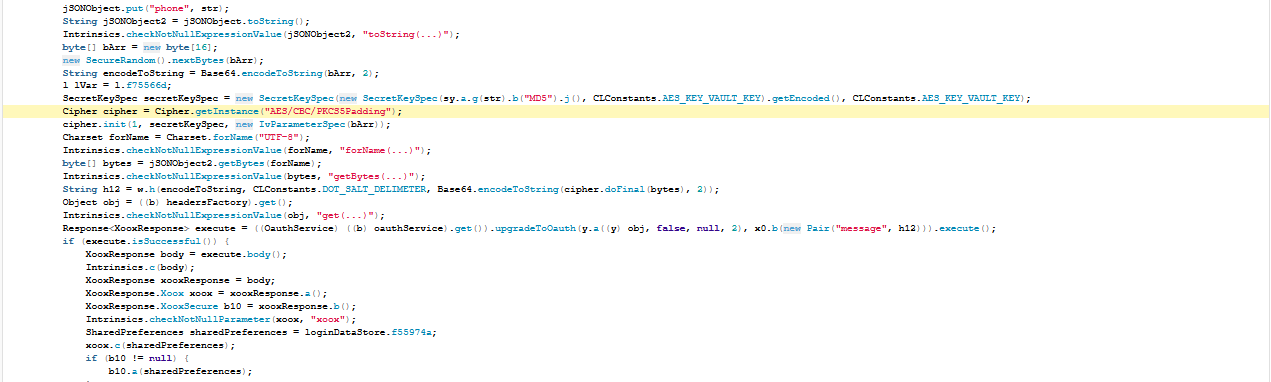 honestcorrupt/meesho-android-improper-encryption-cve-2026-5682
Proof of concept demonstrating insecure AES-CBC encryption with MD5 key derivation in the Meesho Android app, enabling ciphertext tampering and…
 actuator/com.phlox.tvwebbrowser
CVE-2023-43955
 tinopreter/docviewerexploitapp
This is an Exploit App I made when solving the DocumentViewer challenge (CVE-2021-40724) from MobileHackingLab. It will download a libdocviewe_pro.so…

 mazx0p/cve-2014-8609-poc
pendingintent vulnerability
 edwins907/xiaomi-cve-2024-45352
Reporte técnico sobre vulnerabilidad crítica de Xiaomi
 shinycolumn/cve-2025-50944
Improper Certificate Chain Validation in EagleEyes Lite Android Application
 sribaba/android-cve-2016-5195
Proof-of-concept exploit for CVE-2016-5195 (Dirty COW) on Android devices. Compiles native binaries via NDK and deploys via ADB to escalate…
 mobilelinux/iovy_root_research
A root tool based on the [CVE-2015-1805 vulnerability](https://access.redhat.com/security/cve/cve-2015-1805) It supports 32 and 64bit, get sys call…
 aymankhalfatni/cve-2017-0785
CVE-2017-0785: BlueBorne PoC
 pazhanivelmani/external_libcap-android10_r33_cve-2023-2603
POSIX.1e capability library for Android 10, addressing CVE-2023-2603 with tools for setting and getting process capabilities to manage privilege…
 kai2er/cve-2024-0044-exp
利用CVE-2024-0044 在Android12、13 没有root'下进行数据备份 用法./CVE-2024-0044-EXP.sh <package_name>
 edllt/cve-2016-5195-master
Proof-of-concept exploit for CVE-2016-5195 (Dirty COW) targeting Android devices via ADB, demonstrating local privilege escalation through race…