
CVE-2024-50657
 sahalll/cve-2024-50657
Provides a proof-of-concept exploit for CVE-2024-50657, an incorrect access control vulnerability in Owncloud Android app, demonstrating passcode…
android-securityexploitationmobile-security+2
sahalll/cve-2024-50657Provides a proof-of-concept exploit for CVE-2024-50657, an incorrect access control vulnerability in Owncloud Android app, demonstrating passcode…
 seriousattempts/bootloader_unlock_retroid_pocket_3plus
Bootloader unlock using CVE-2022-38694 for Retroid Pocket 3+
 dere-ad2001/frida-labs
The repo contains a series of challenges for learning Frida for Android Exploitation.
 l0lsec/cve-2026-12960
CVE-2026-12960 - Improper Export of Android Application Components in the ASUS Router app (com.asus.aihome). PoC, exploit APK, video, and vendor…
 flipphoneguy/root-sonim-xp3800
app that ports CVE-2019-2215 to arm32 and mounts a su binary to /sbin with denylist + root app installer. firehose/Magisk guide included
 caveeroo/gv_decryptor
Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.
 cleov2/debuggable-app-exploit
CVE-2024-31317 Debuggable App Exploit
 fusiondrive/cve-2026-43499-s24u
CVE-2026-43499 research port for Galaxy S24 Ultra SM-S928U1 DZF2 (COMPLETED)
 newazbenalam/root-my-galaxy-payloads
Device-specific CVE-2026-43499 root payloads and KernelSU artifacts for Samsung Galaxy models, with firmware profiles, exploit source, and a support…
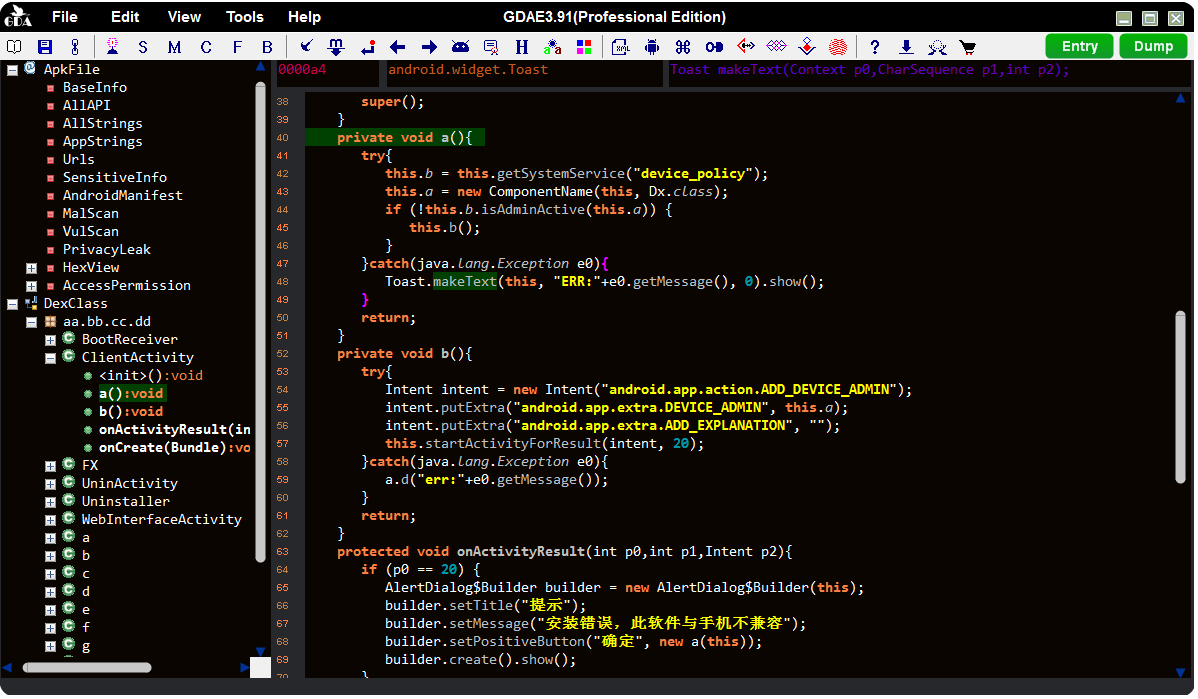 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
 advancedhacker101/android-c-sharp-rat-server
This is a plugin for the c# R.A.T server providing extension to android based phone systems
 ireshchaminda1/android-privilege-escalation-remote-access-vulnerability-cve-2015-1805
AndroRAT is a capability that can be used to inject a root exploit as a silent installation to perform a malicious task on the device. This AndroRAT…
 nestle19/cve-2019-2215
Android kernel exploit for CVE-2019-2215, a use-after-free in the Binder driver, enabling privilege escalation to root via memory corruption and cred…
 trinadh465/frameworks_base_aosp-4.2.2_r1_cve-2023-21272
Android framework base repository for AOSP 4.2.2_r1, modified to address CVE-2023-21272, a vulnerability in the Android framework.
 viralsecuritygroup/knoxout
A PoC of KNOXout (CVE-2016-6584) - bypassing Samsung KNOX protections and root Samsung Galaxy S6 Android Device.
 eudemonics/scaredycat
Python script to generate a malicious MP4 file and start a CherryPy web server hosting a simple HTML page with the embedded file. Exploits another…
 timwr/cve-2013-6282
CVE-2013-6282 proof of concept for Android
 dorlow/hazel-cve-2026-43499
Firmware-specific temporary root exploit for Toshiba/Amazon Fire TV (hazel) using CVE-2026-43499. Implements ARM32 futex-PI UAF, kernel address leak,…